Container Registry and Software Supply Chain Platform
One trusted path from a source commit to a running workload, and machine-checkable evidence that the path was followed. The requirement named AWS as its target; this set answers it with an open-source stack the team runs on its own hardware — Harbor and MinIO for artifacts, Sigstore (Fulcio, Rekor, Cosign) for signing and transparency, Tekton Chains for provenance, Syft for SBOMs, Trivy and Grype for scanning, OSV and distro feeds reconciled into one advisory record, OPA for policy, Kafka for evidence distribution, ClickHouse for the component index, PostgreSQL for registry metadata, Vault with a PKCS#11 HSM for key custody, SPIRE and Keycloak for identity.
33 views, each in three formats.
Open a view to read it in full. Every SVG carries its diagram source inside it, so it opens in diagrams.net fully editable with no import step; the draw.io files are the same diagrams as plain source.
-
01
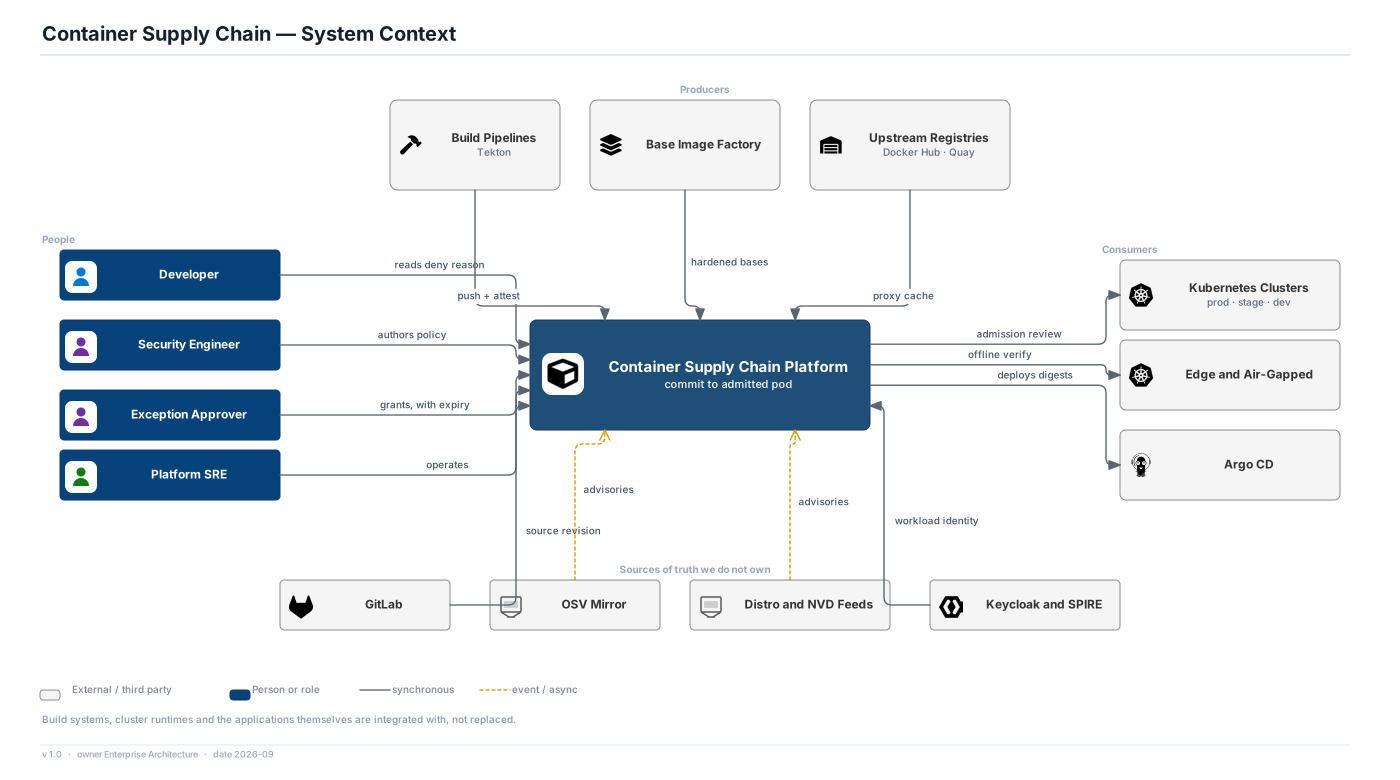
System Context
Who produces artifacts, who consumes them, and what the platform deliberately does not own.
-
02
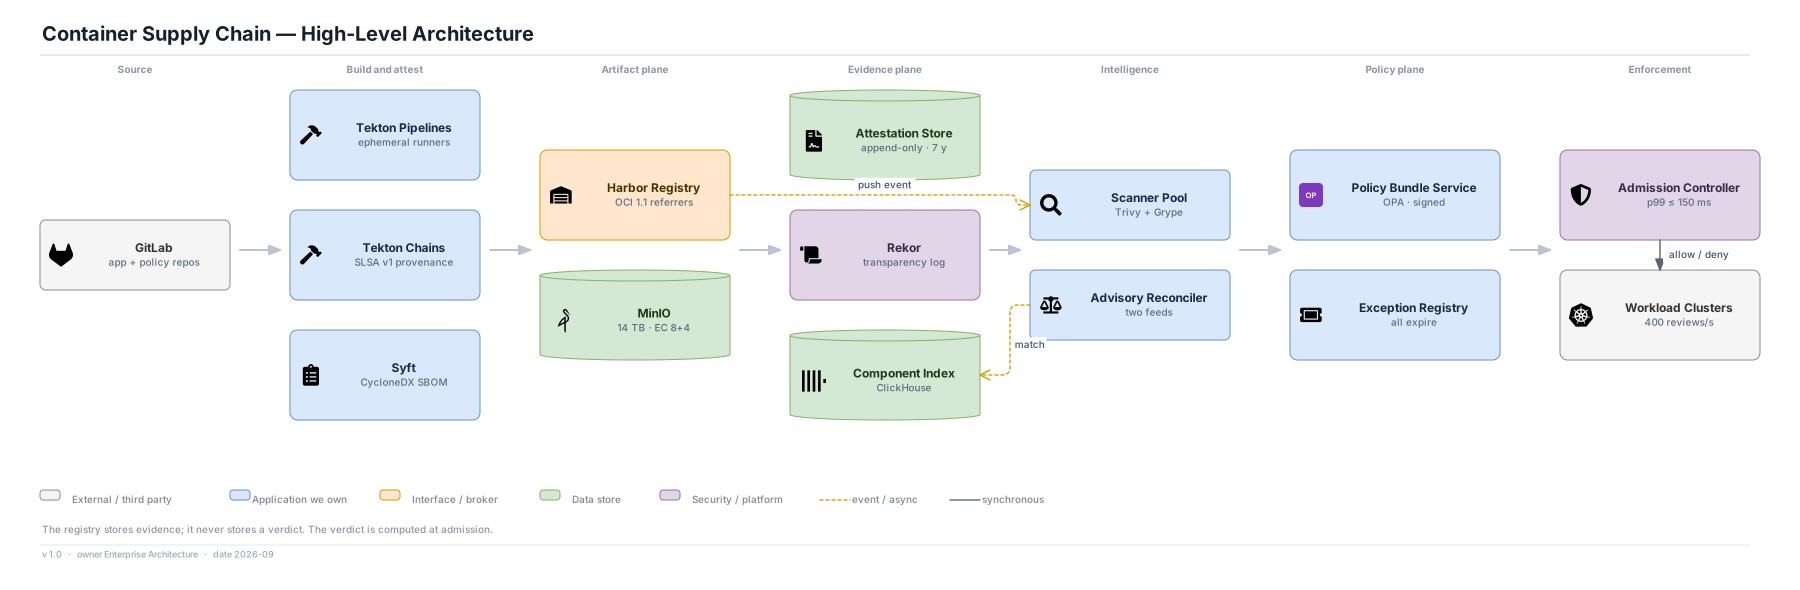
High-Level Architecture
The shape of the platform in one picture, for the reader who will see only one.
-
03
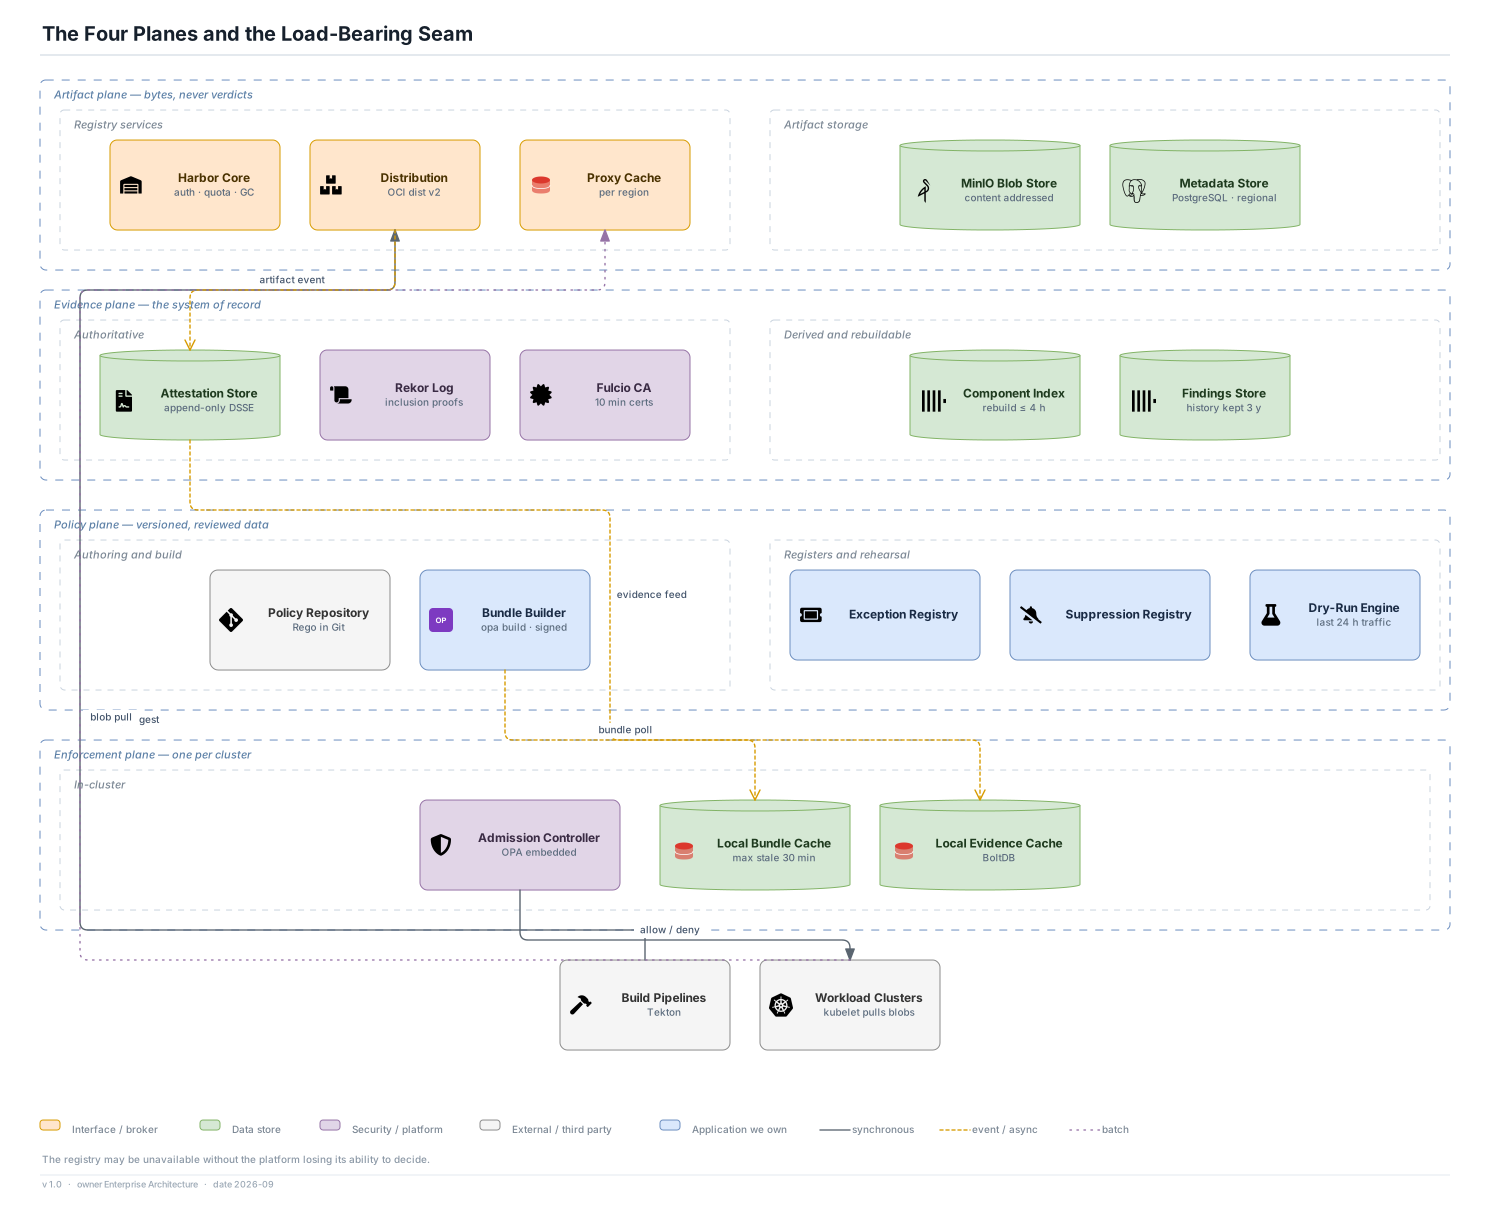
The Four Planes
Why the boundary between the artifact plane and the evidence plane is the load-bearing seam of the whole system.
-
04
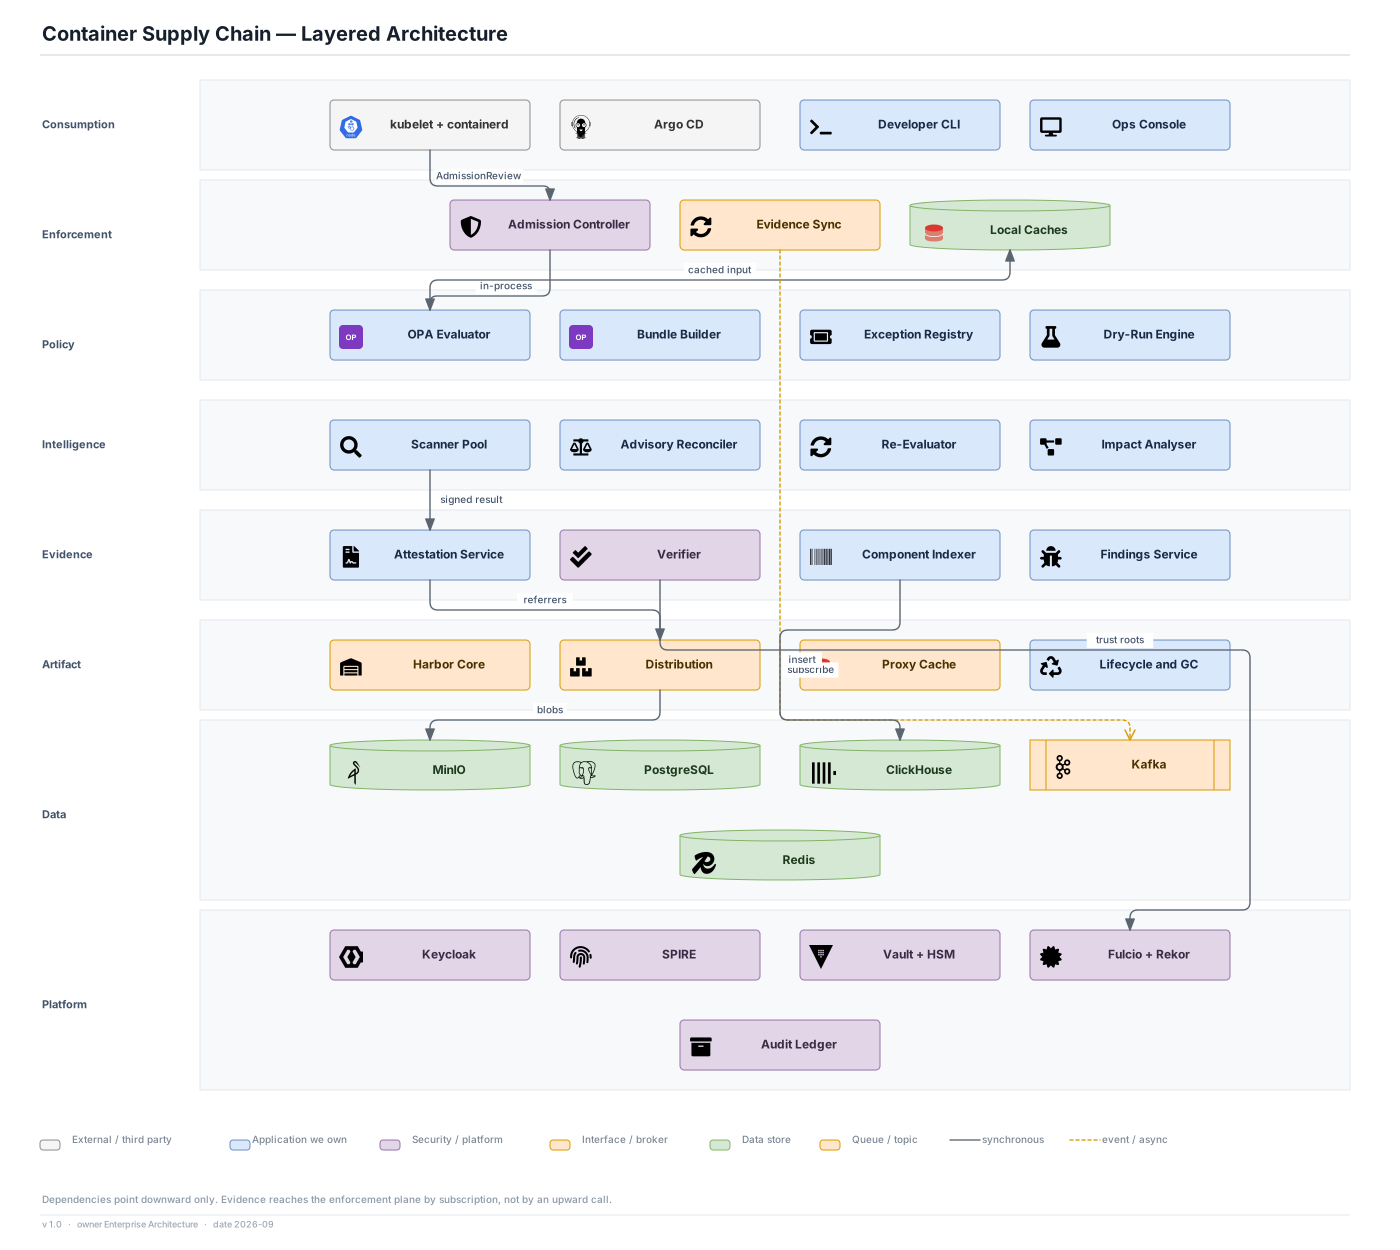
Layered Architecture
What depends on what, and why no layer calls upward.
-
05
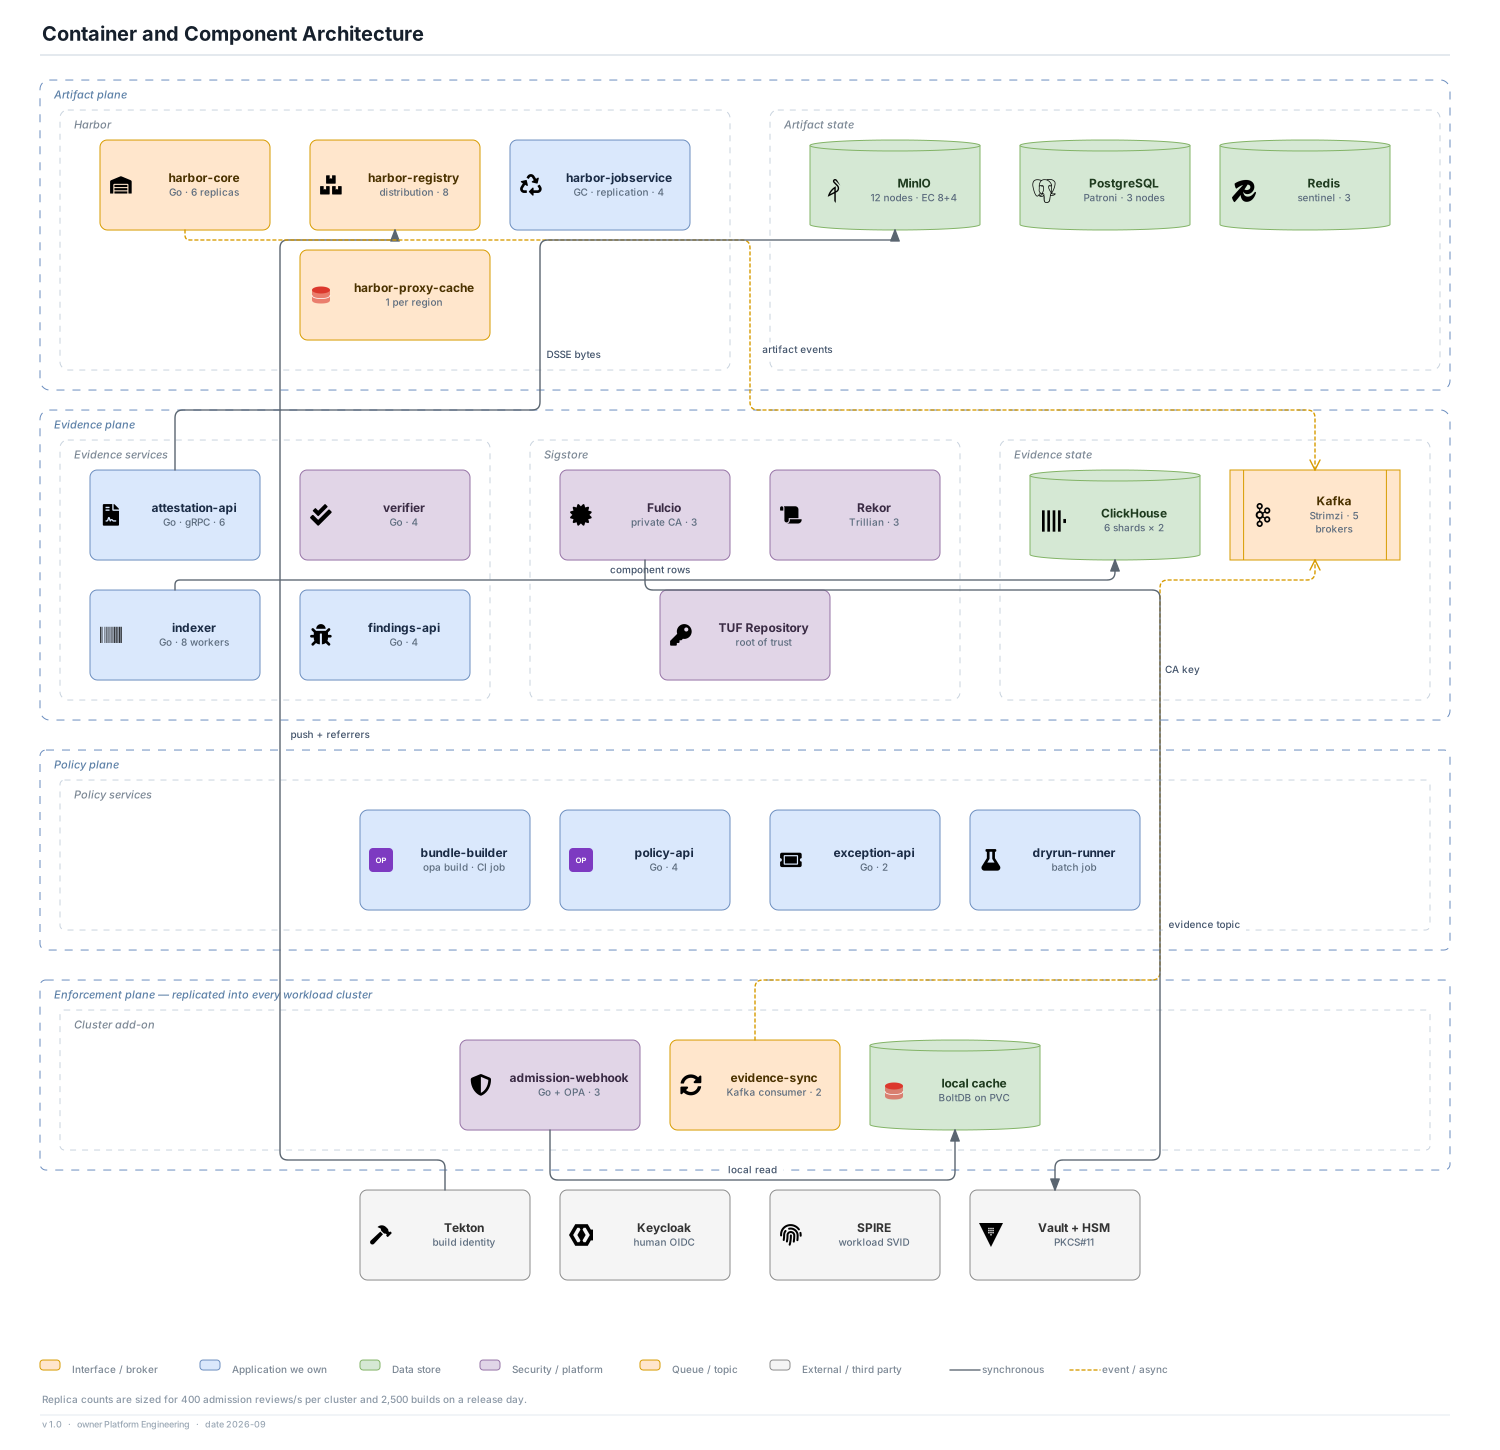
Container and Component Architecture
Every deployable unit, its technology, and how many of it there are.
-
06
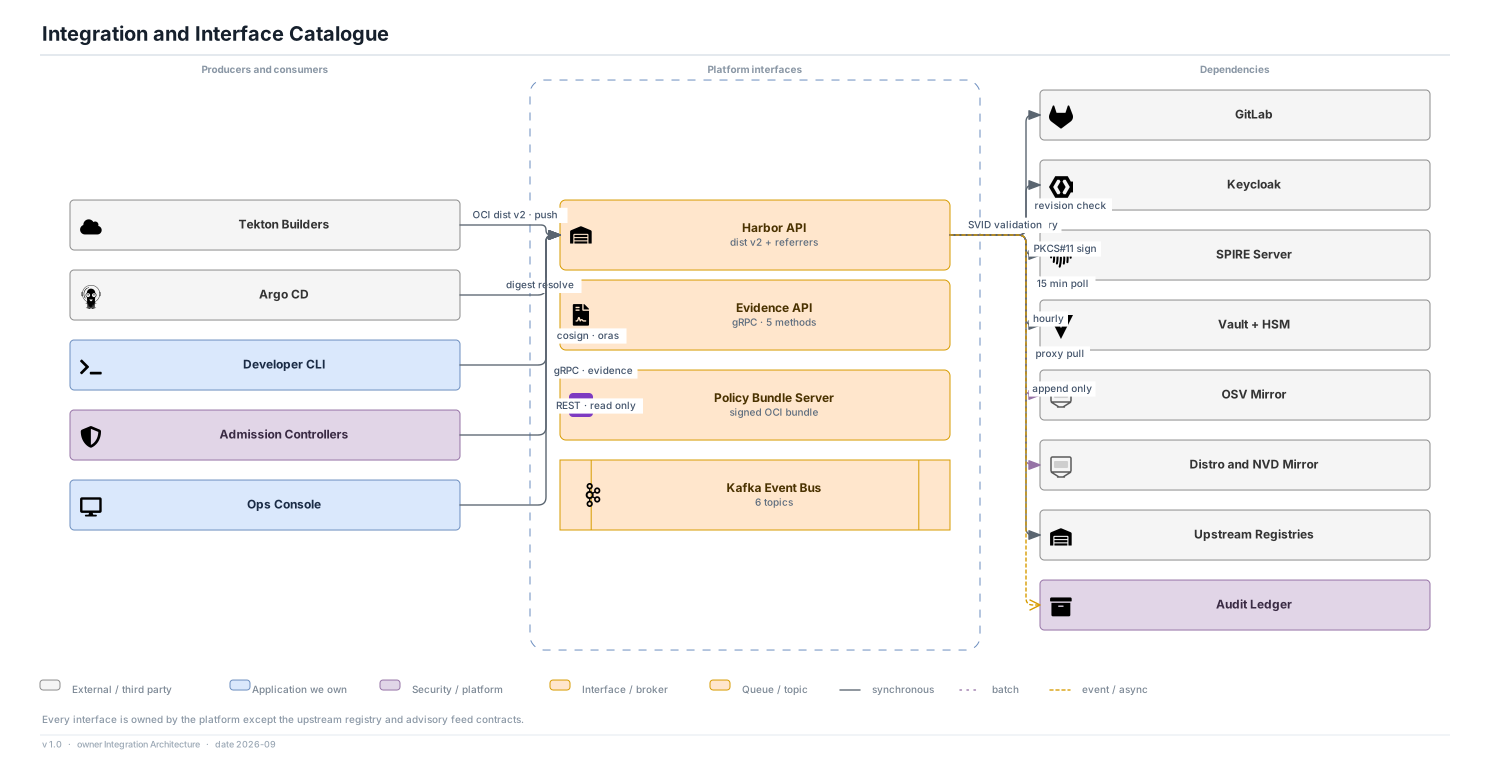
Integration and Interface Catalogue
Every way something enters or leaves the platform, with protocol and cadence.
-
07
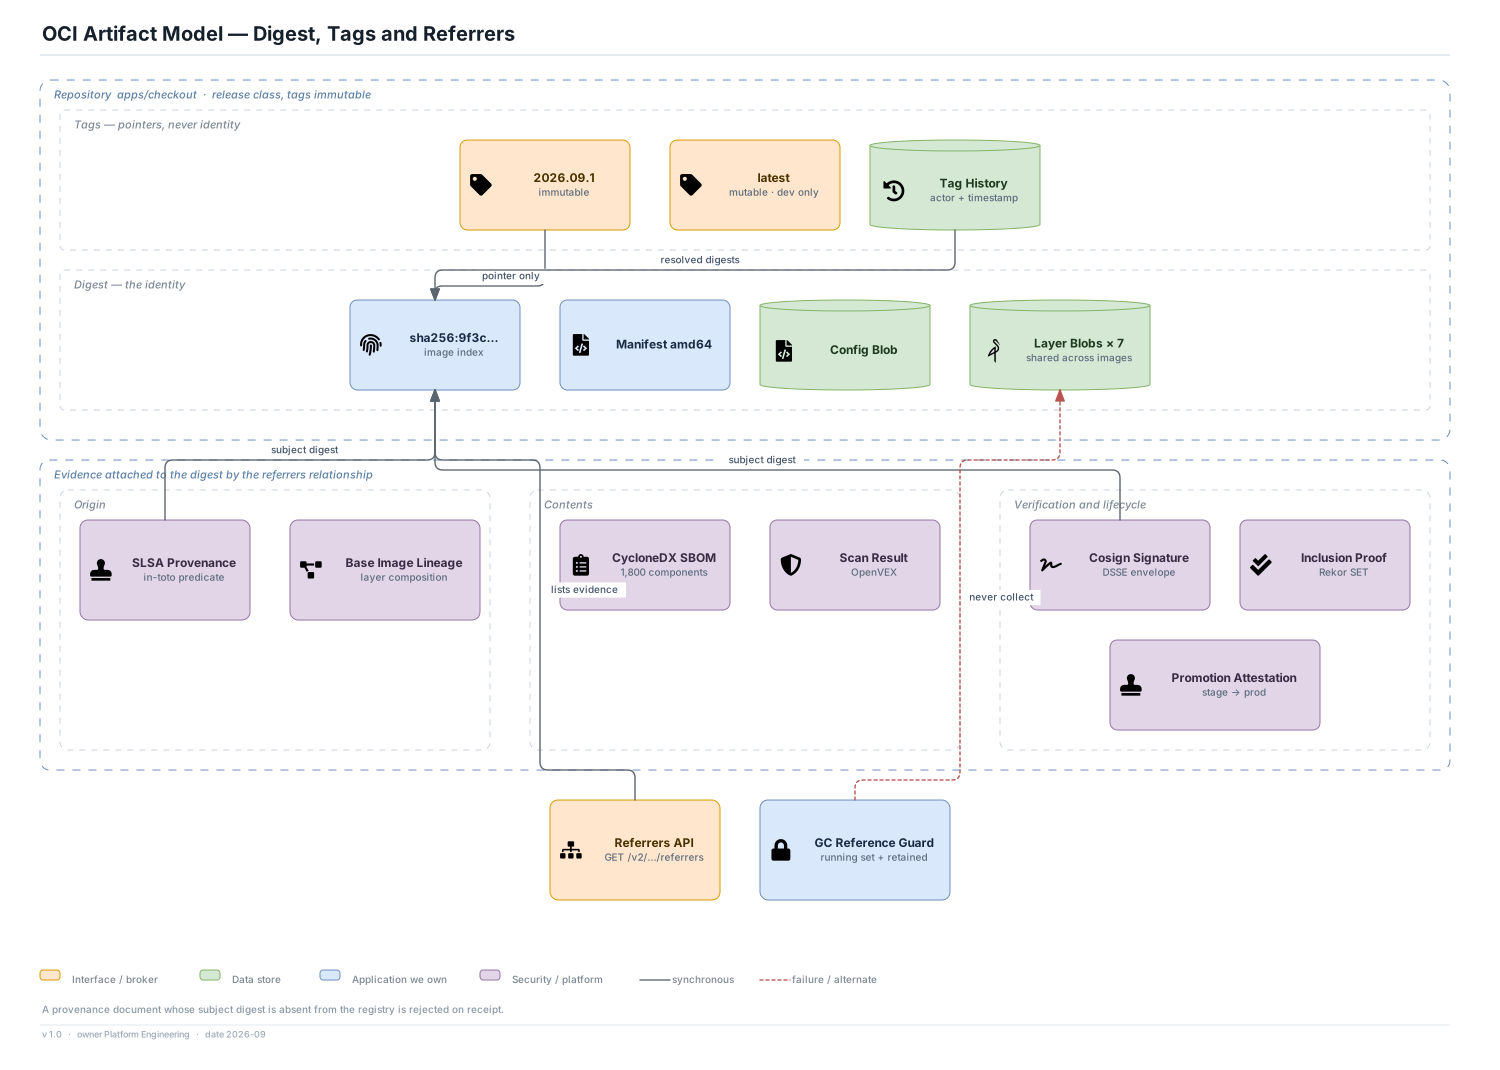
OCI Artifact Model
How a tag, a digest and its evidence relate, and why only one of the three is an identity.
-
08
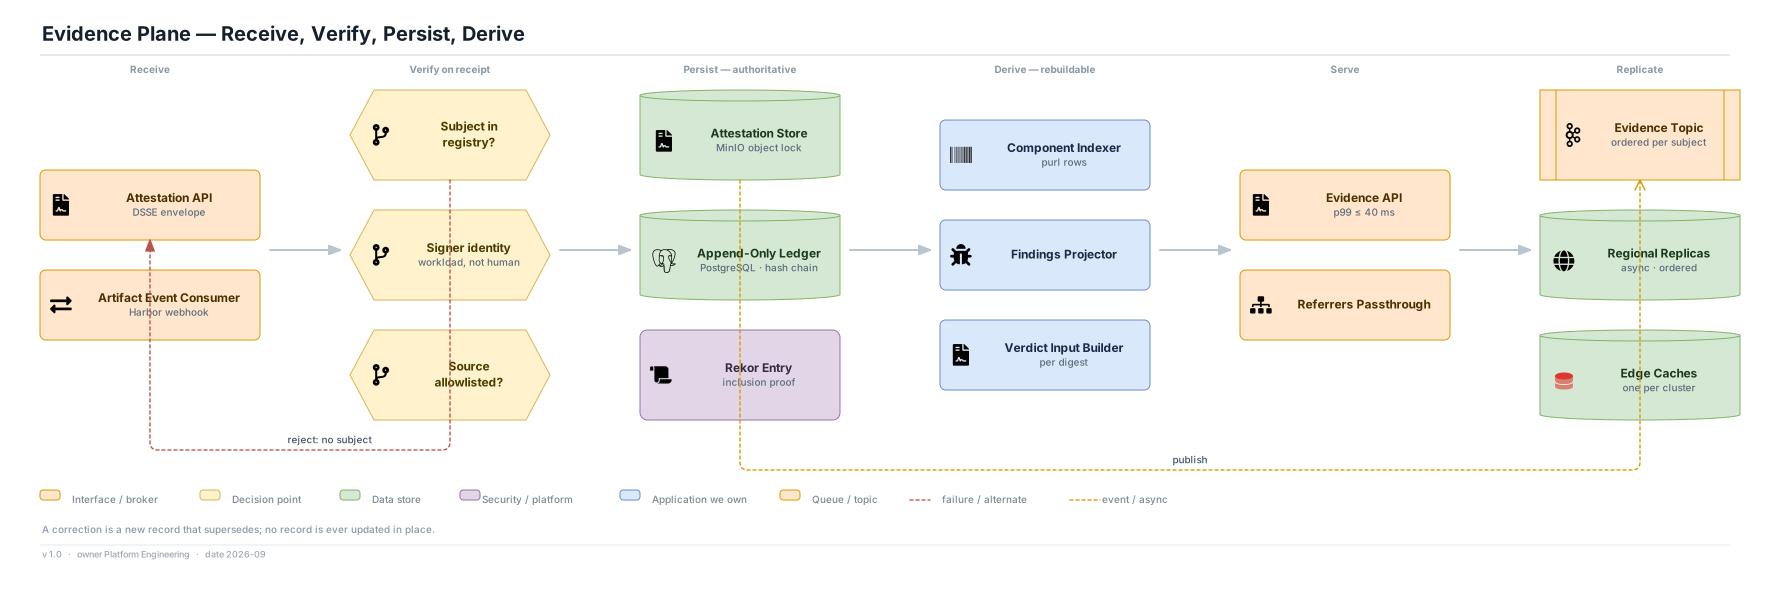
Evidence Plane Pipeline
What happens to a piece of evidence between arriving and being usable at an enforcement point.
-
09
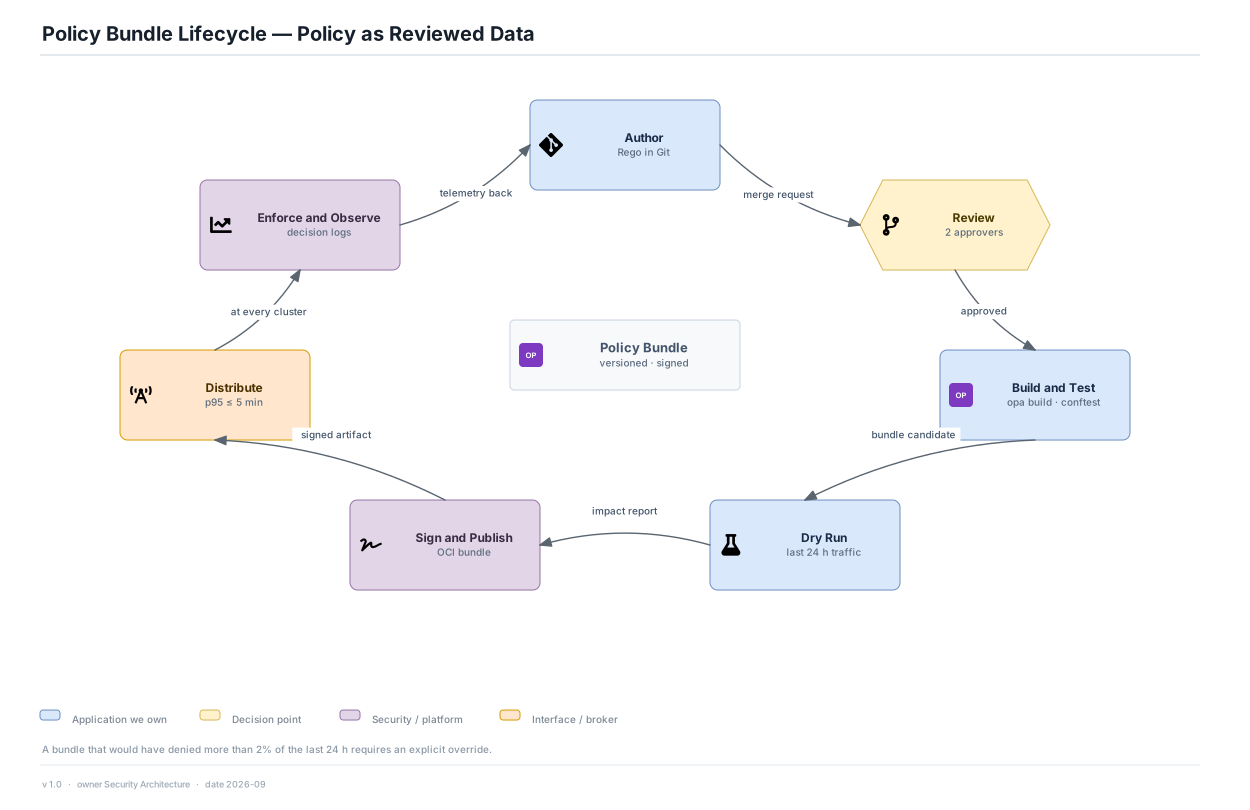
Policy Bundle Lifecycle
How a rule change reaches every enforcement point without becoming an outage.
-
10
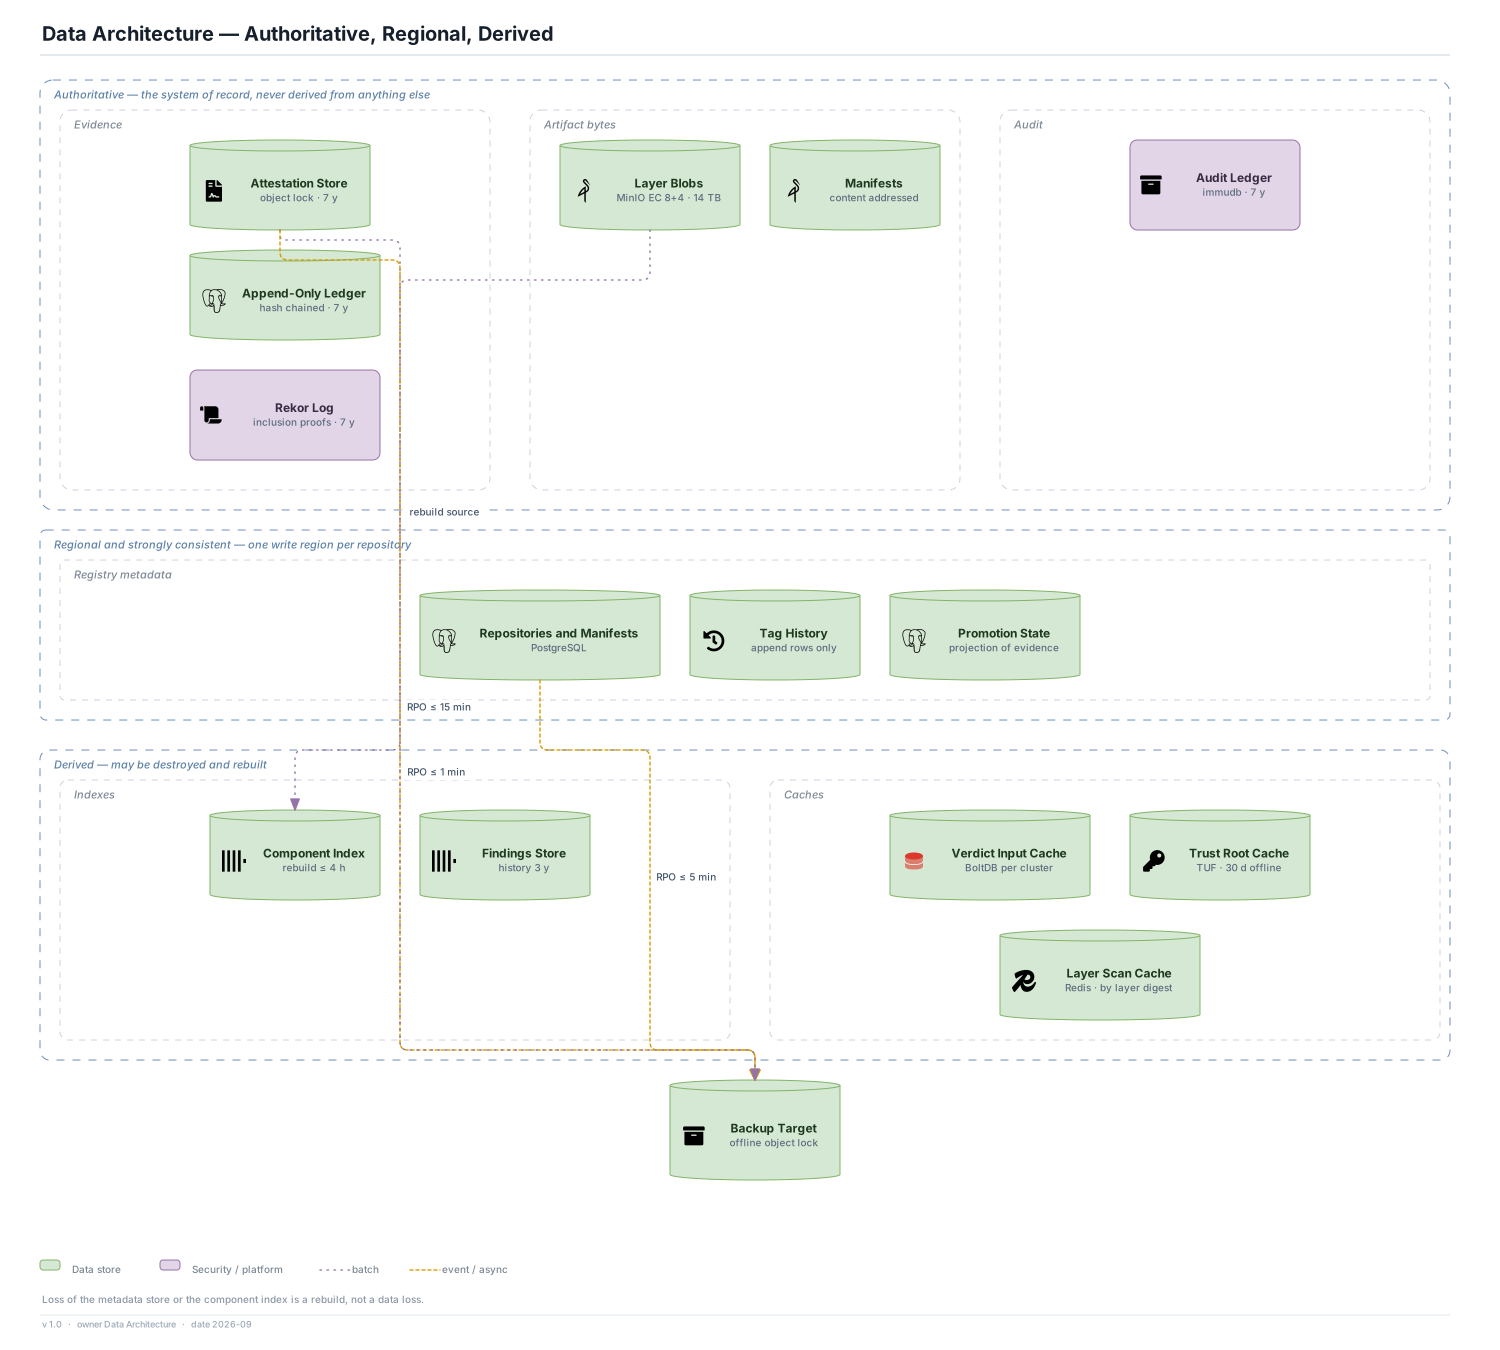
Data Architecture and Storage Zones
Which store is the system of record, which are derived, and what backup actually has to cover.
-
11
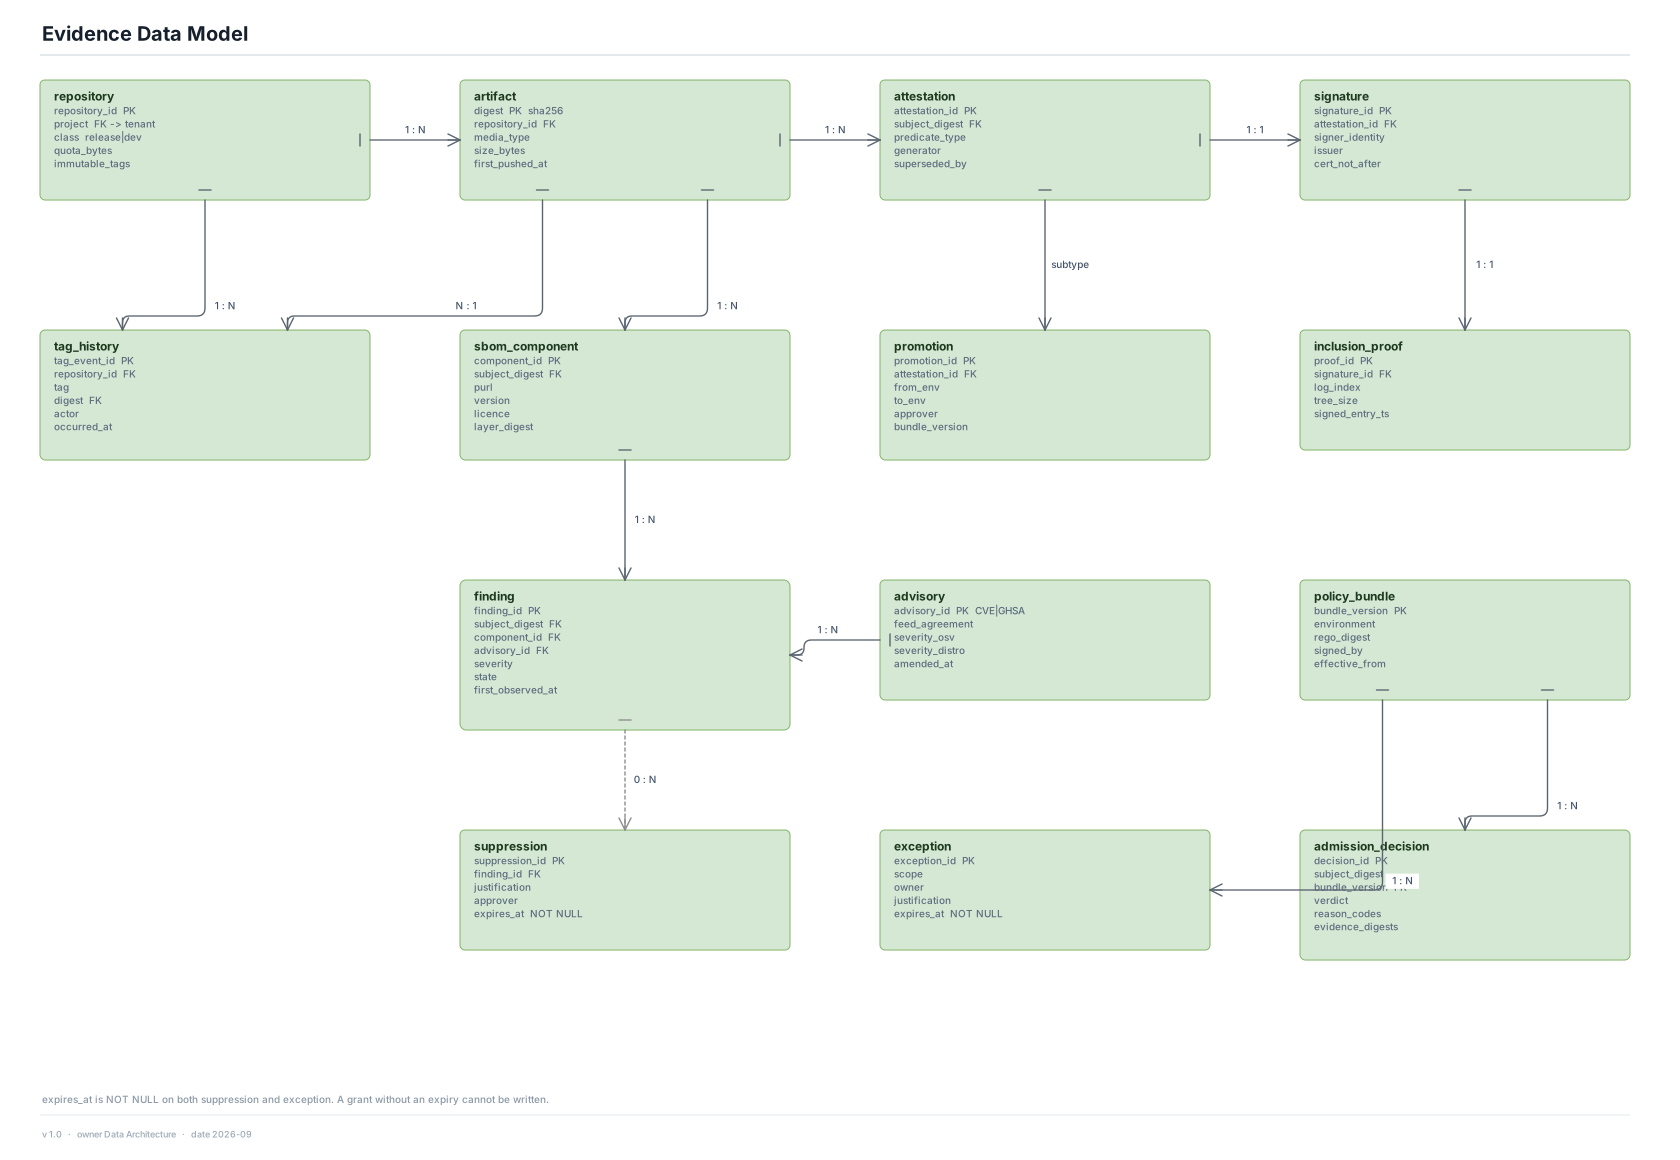
Evidence Data Model
The entities a decision reads, and the two columns that cannot be null.
-
12
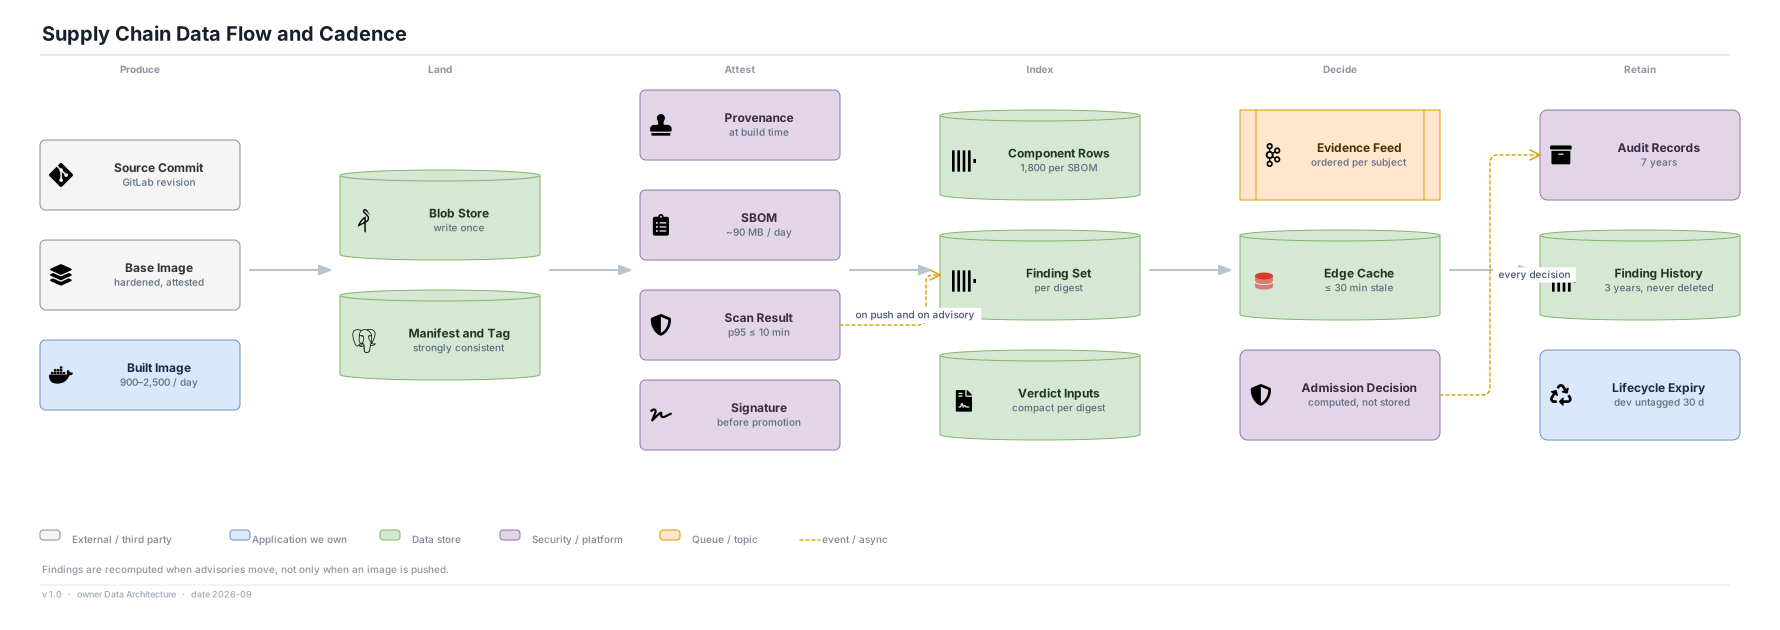
Supply Chain Data Flow
Where each kind of data comes from, what it becomes, and how long it is kept.
-
13
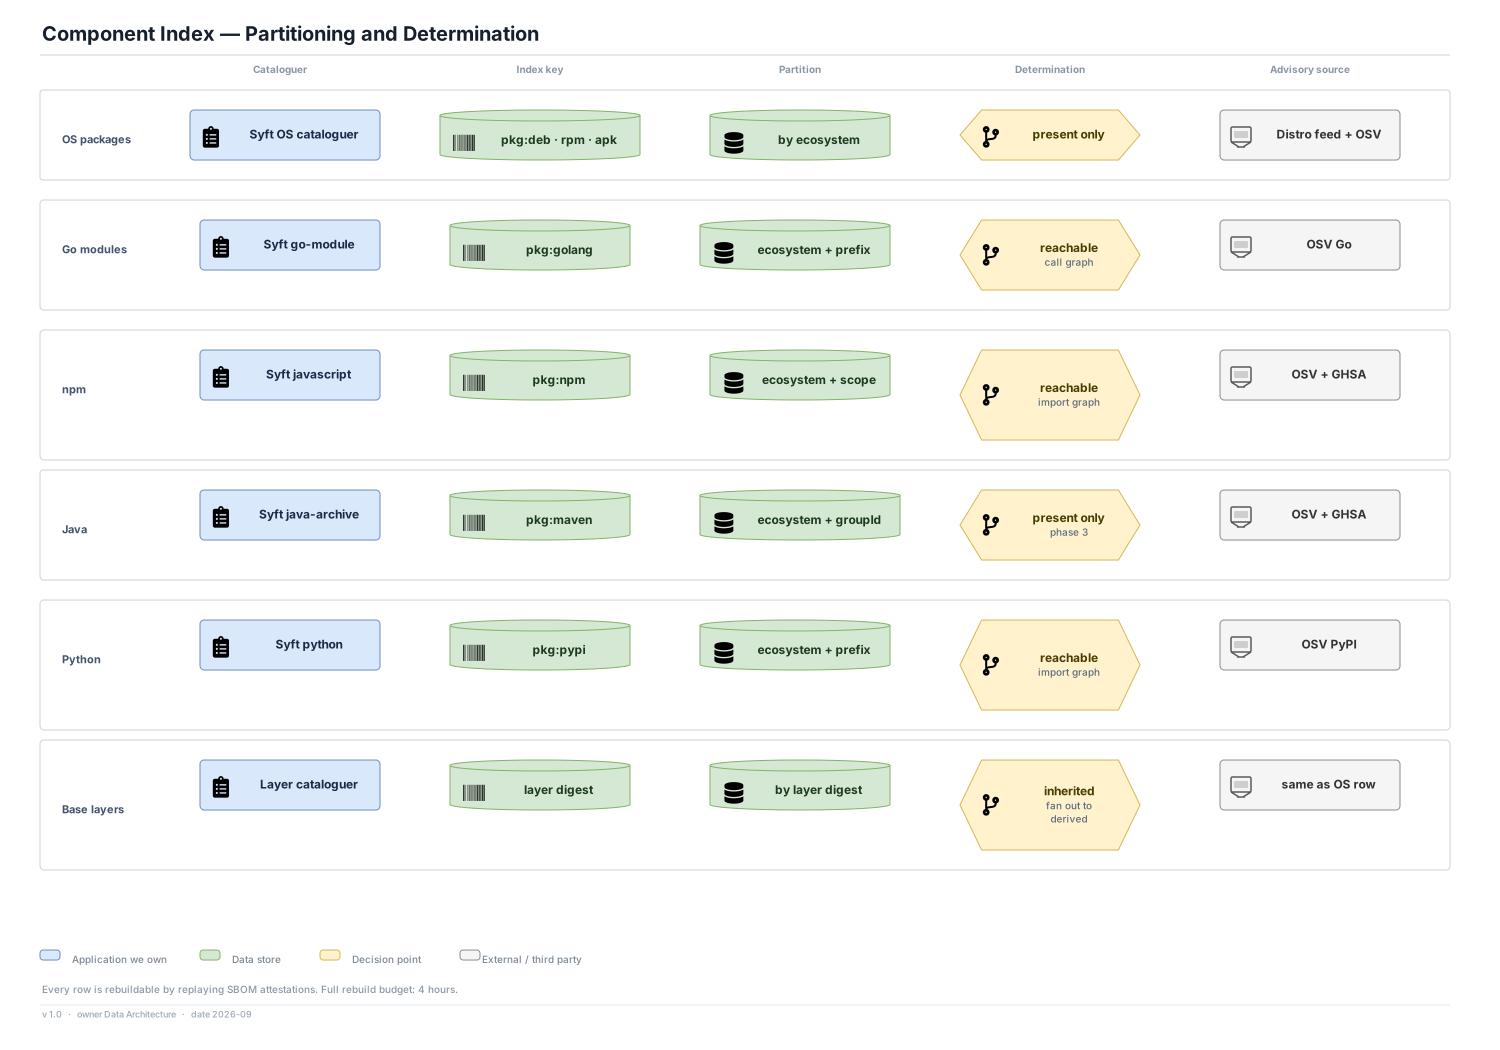
Component Index
How 'which images contain package X at version Y' stays a bounded query as the corpus grows.
-
14
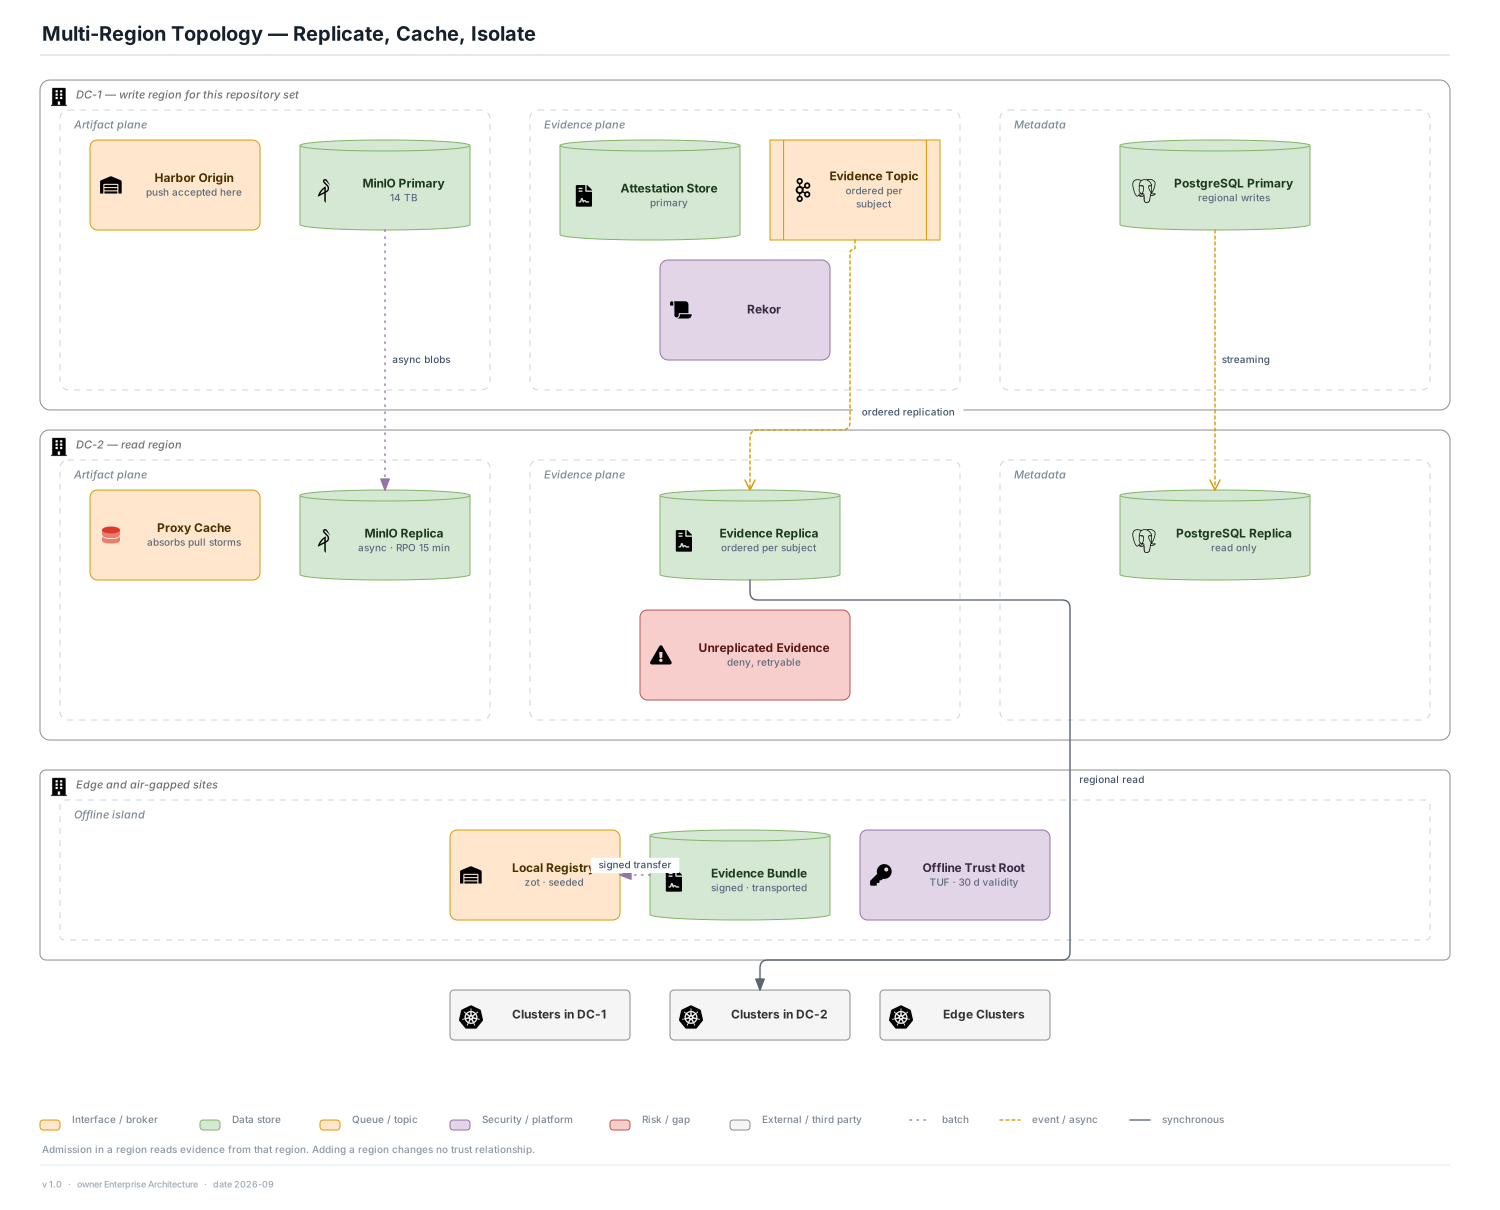
Multi-Region Topology
What replicates, what caches, and what an artifact does when its evidence has not arrived yet.
-
15
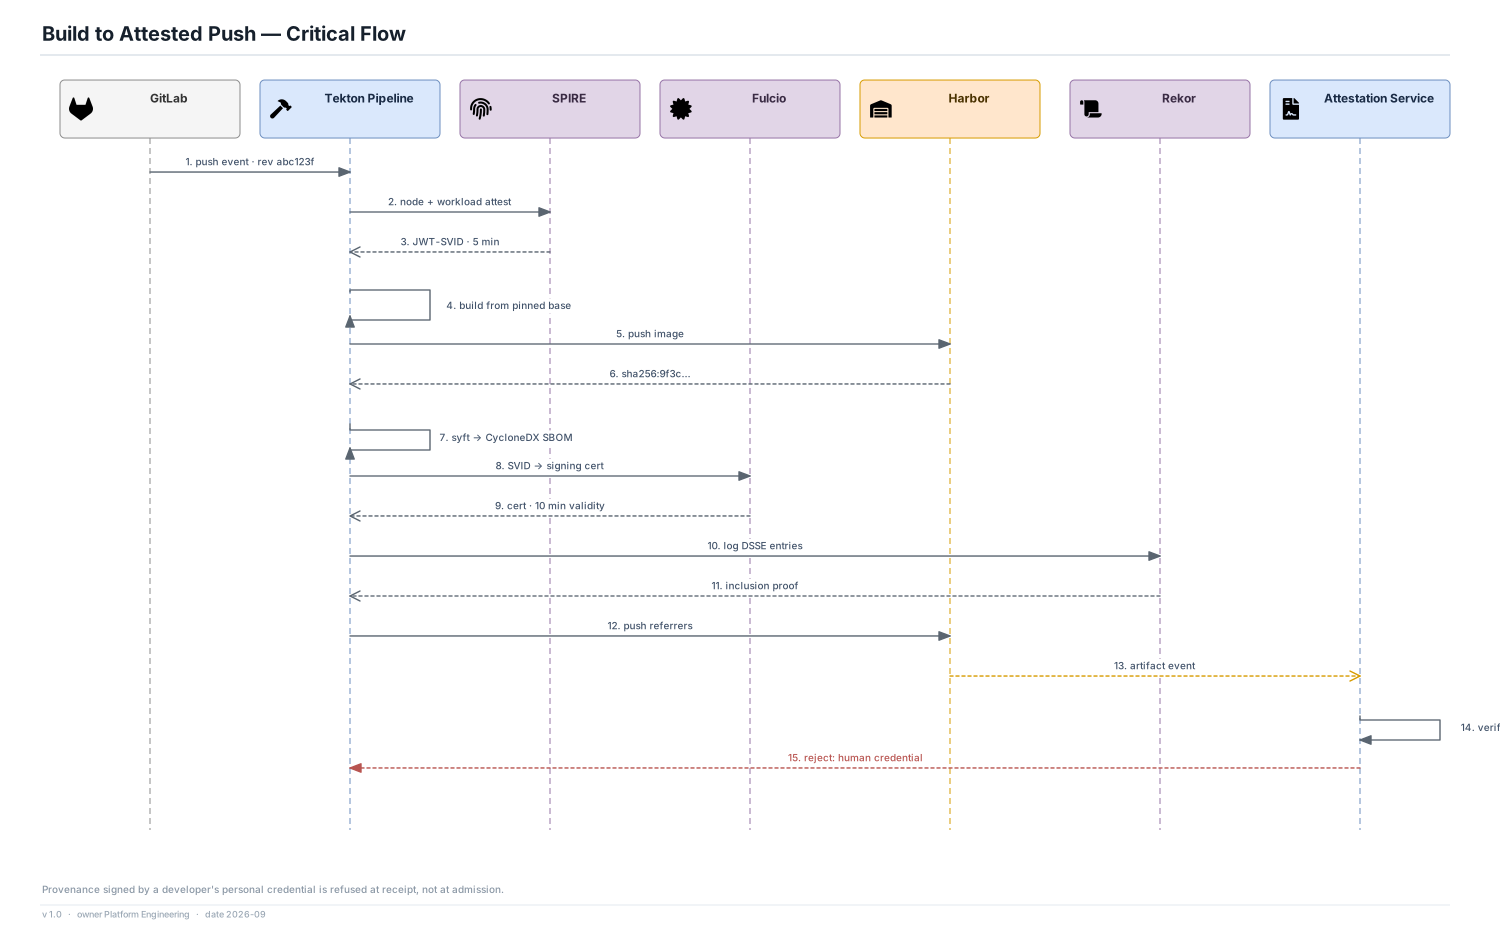
Build to Attested Push
How an image acquires provenance, an SBOM, a signature and an inclusion proof before anyone can deploy it.
-
16
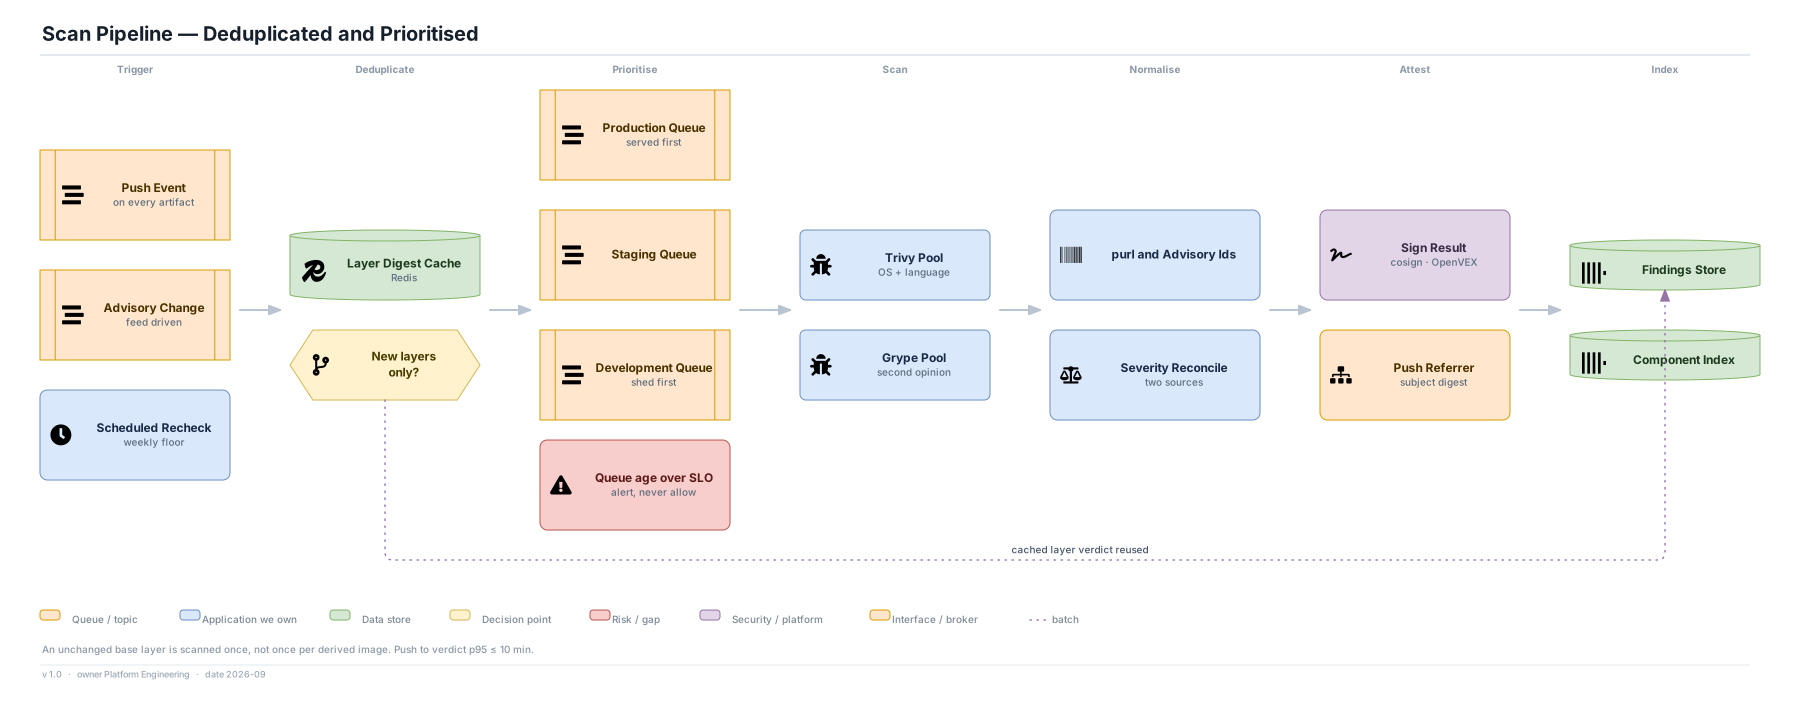
Scan Pipeline
How a scan stays inside ten minutes at 2,500 builds a day without scanning the same base layer 2,500 times.
-
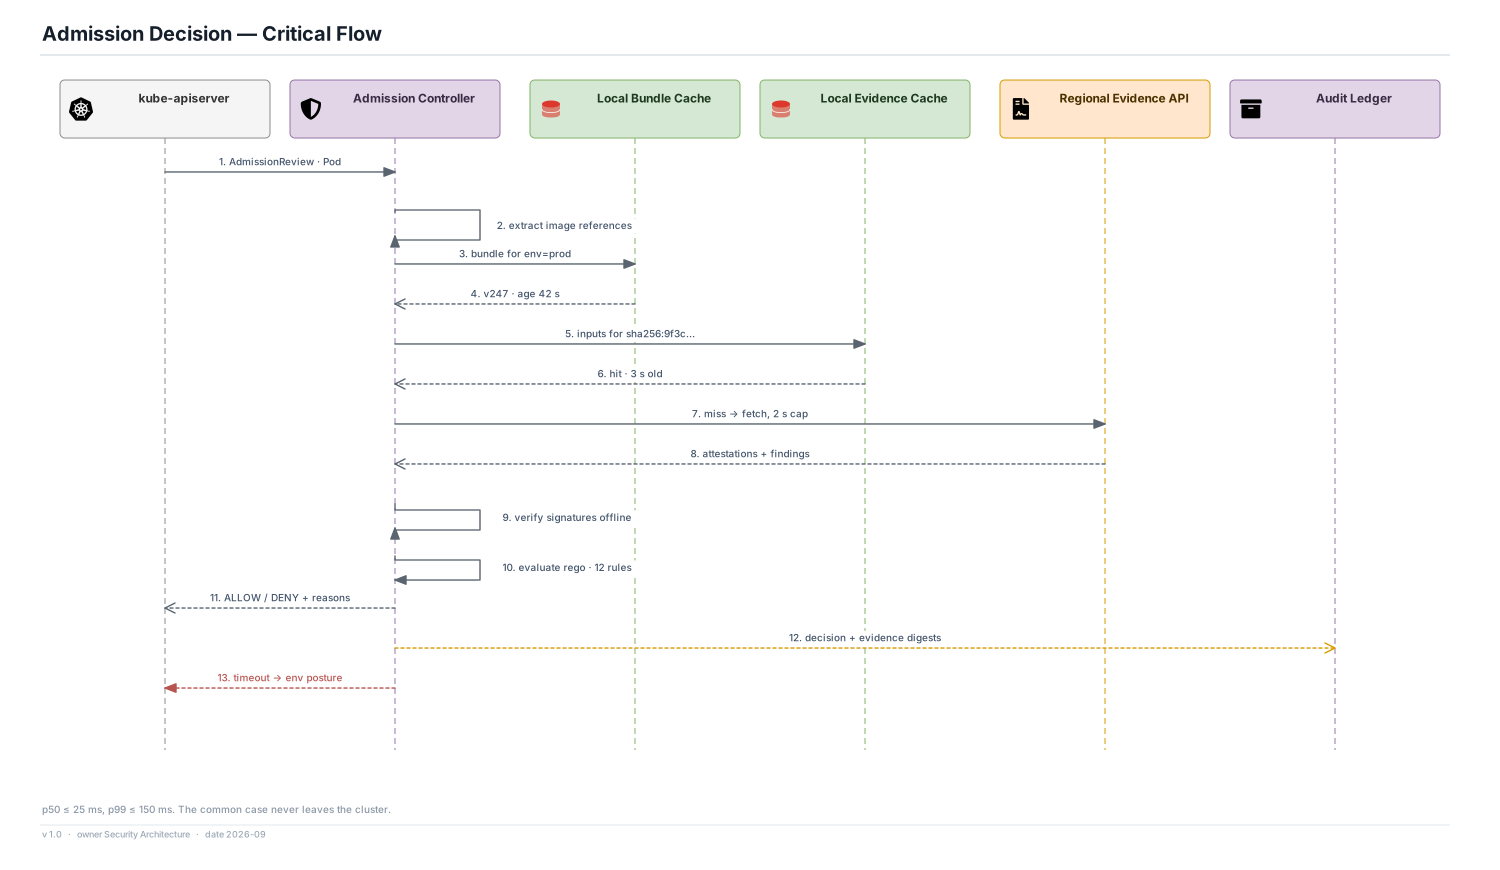
17
Admission Decision
The one flow that must be fast, correct and available, and what it does when it cannot be all three.
-
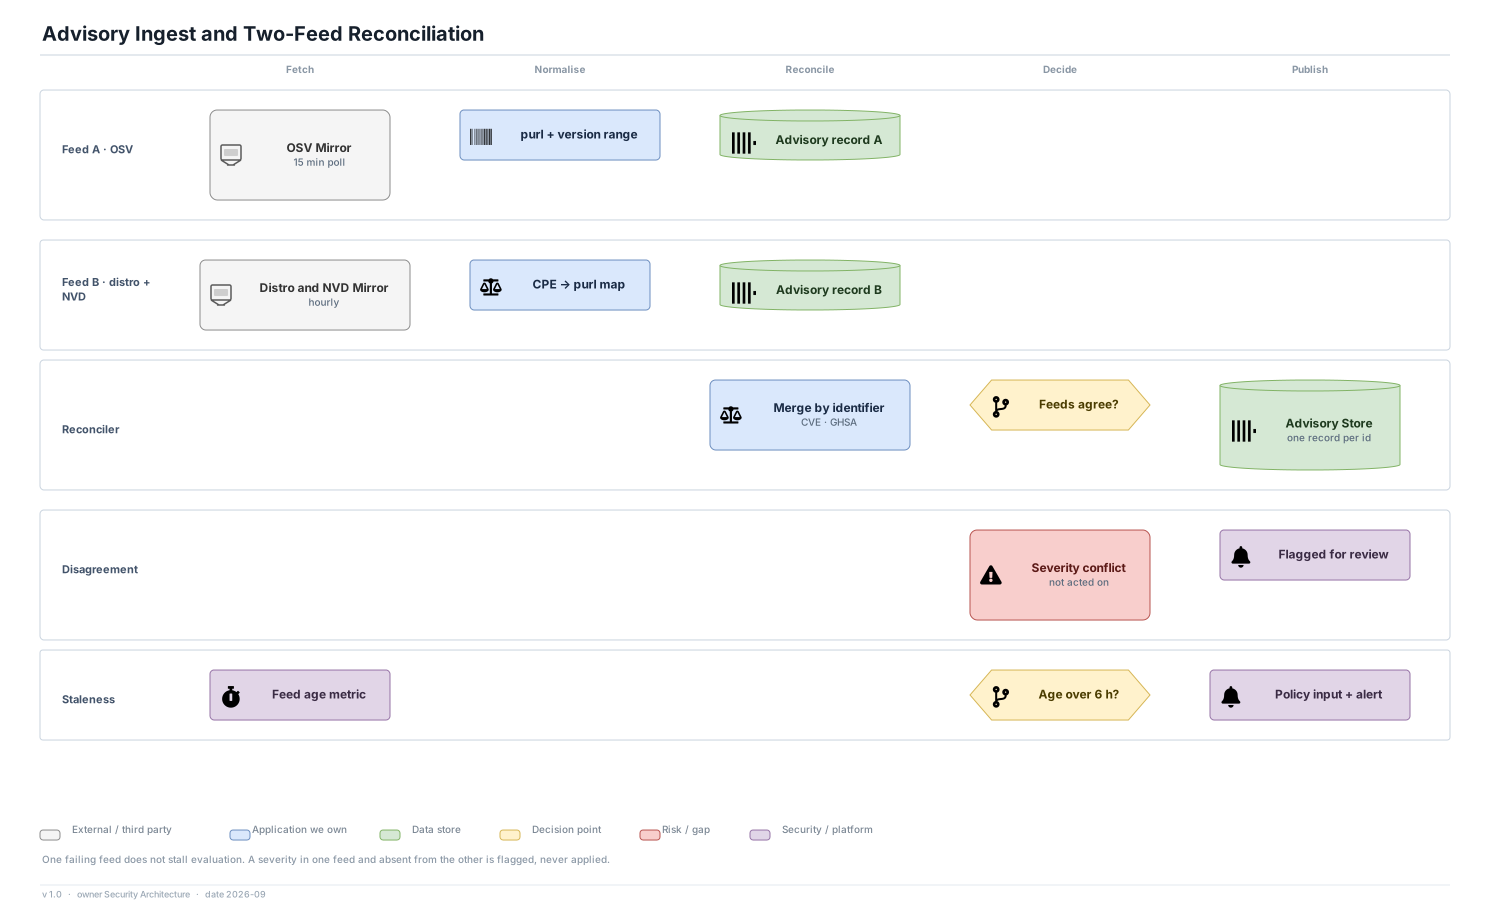
18
Advisory Ingest and Reconciliation
Two feeds, one advisory record, and what happens when the two disagree.
-
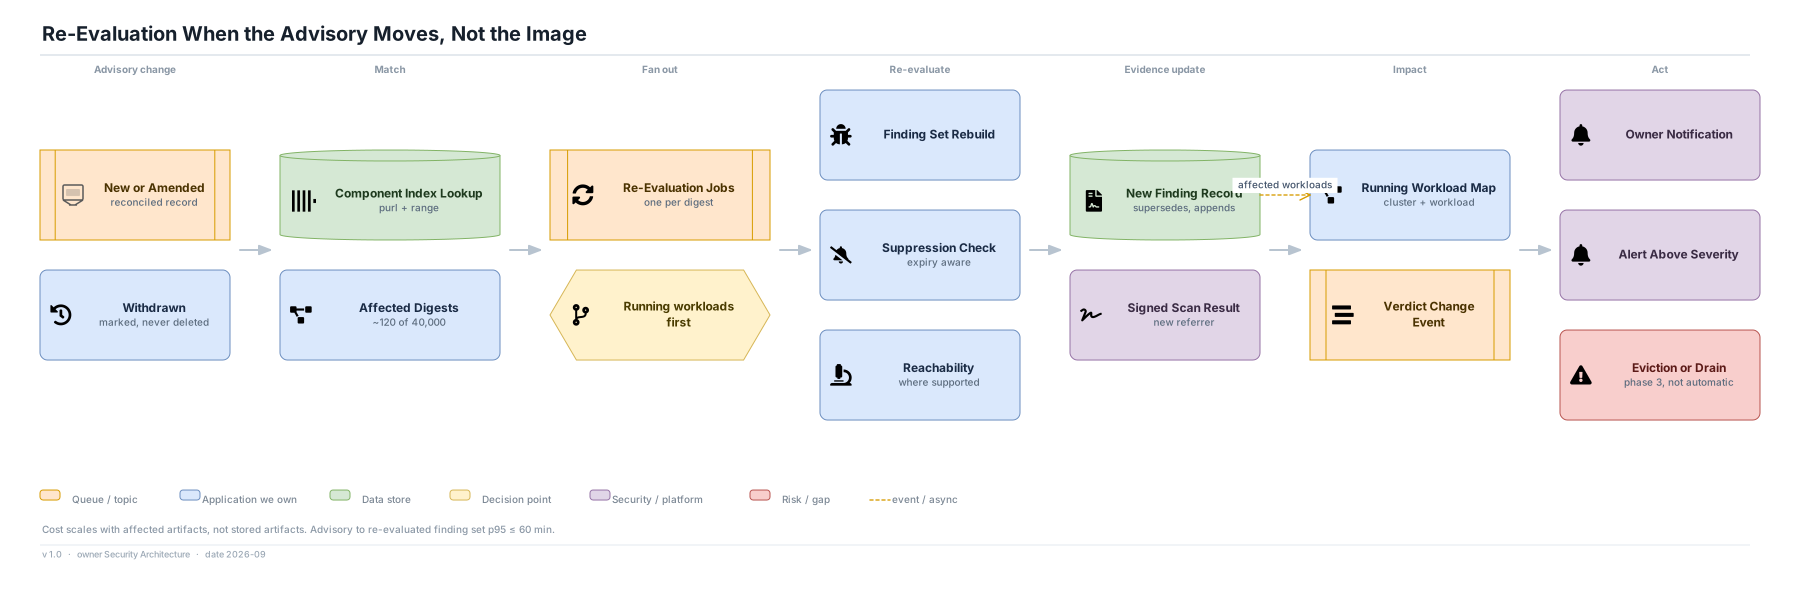
19
Advisory-Driven Re-Evaluation
What happens when the world's knowledge changes and the image does not.
-
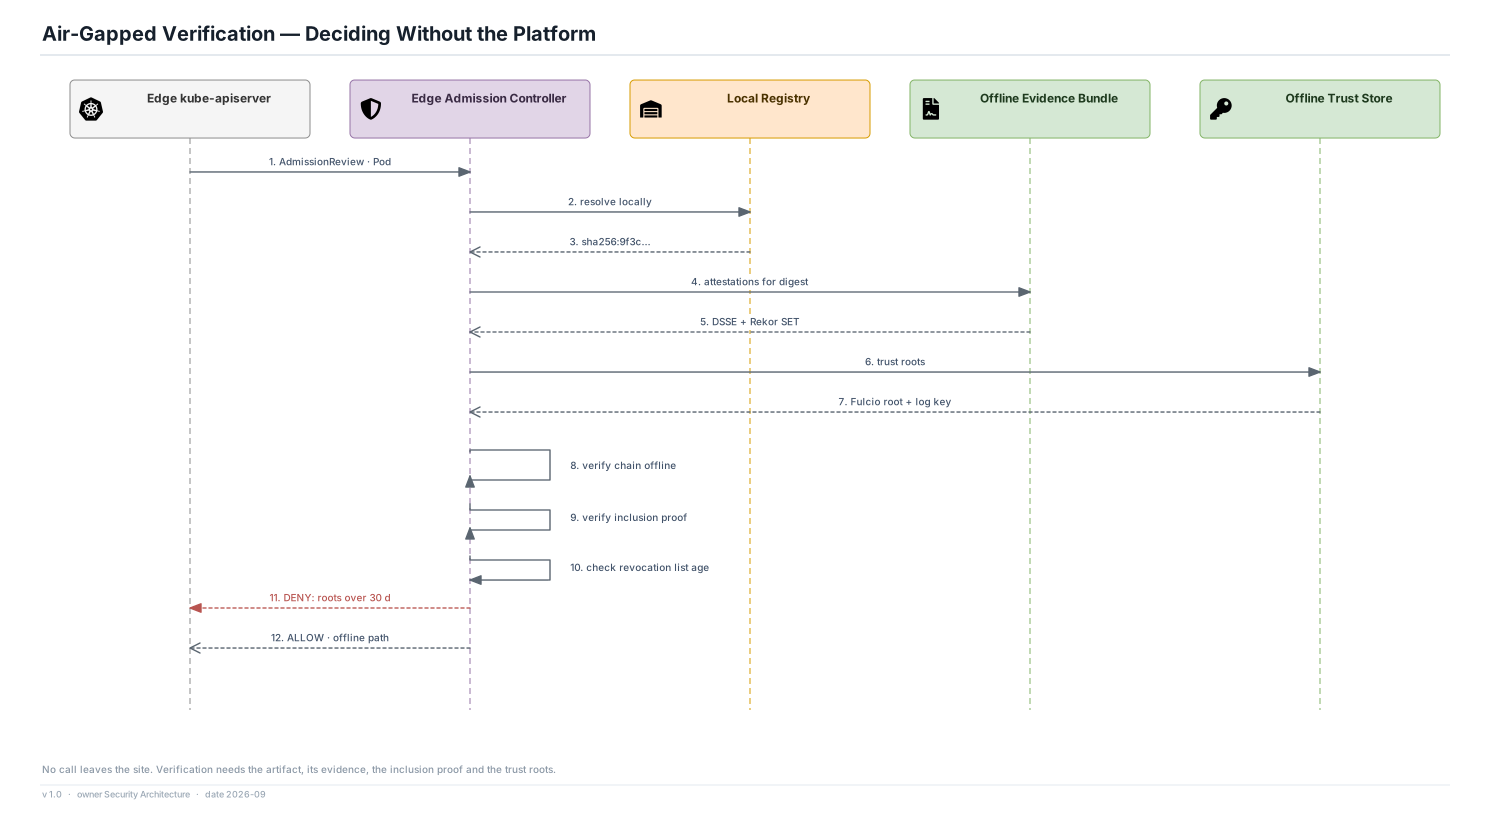
20
Air-Gapped Verification
An enforcement point with the artifact, its evidence and the trust roots decides without calling the platform.
-
21
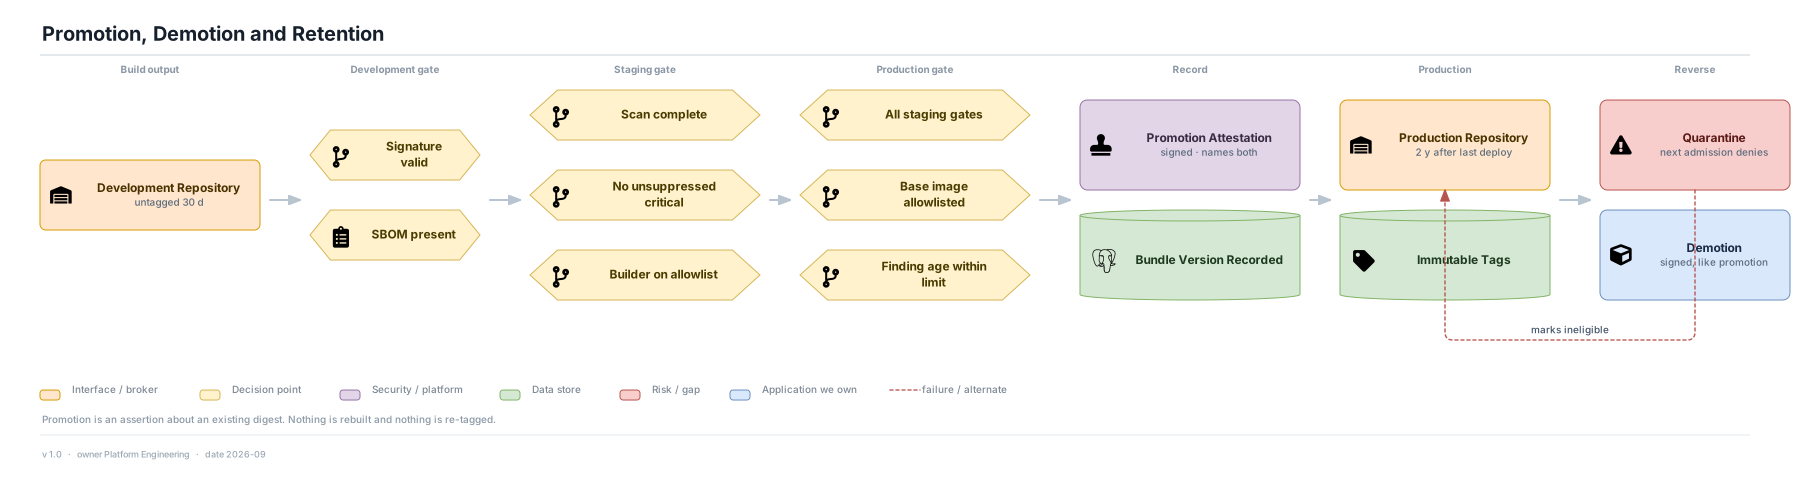
Promotion, Demotion and Retention
How an artifact moves between environments without being rebuilt, re-tagged or trusted twice.
-
22
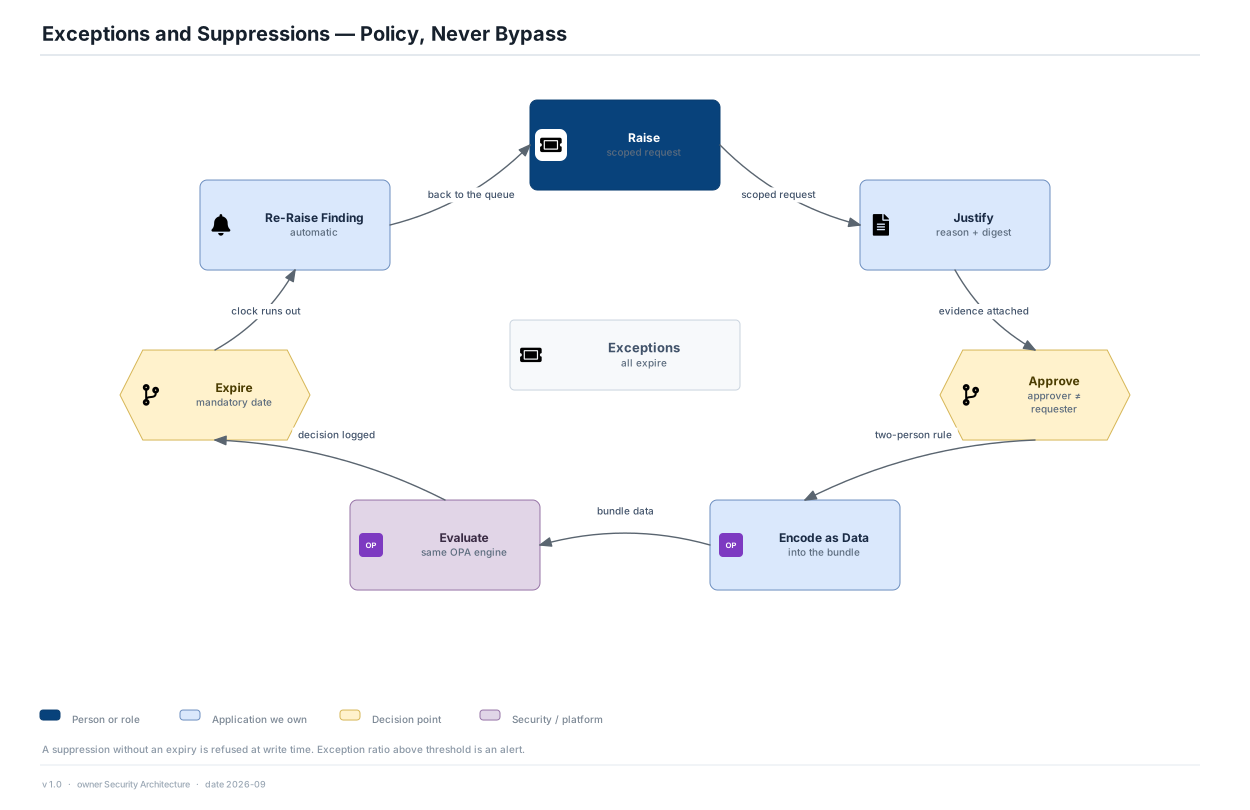
Exceptions and Suppressions
How the platform says yes to something it would otherwise refuse, without creating a permanent hole.
-
23
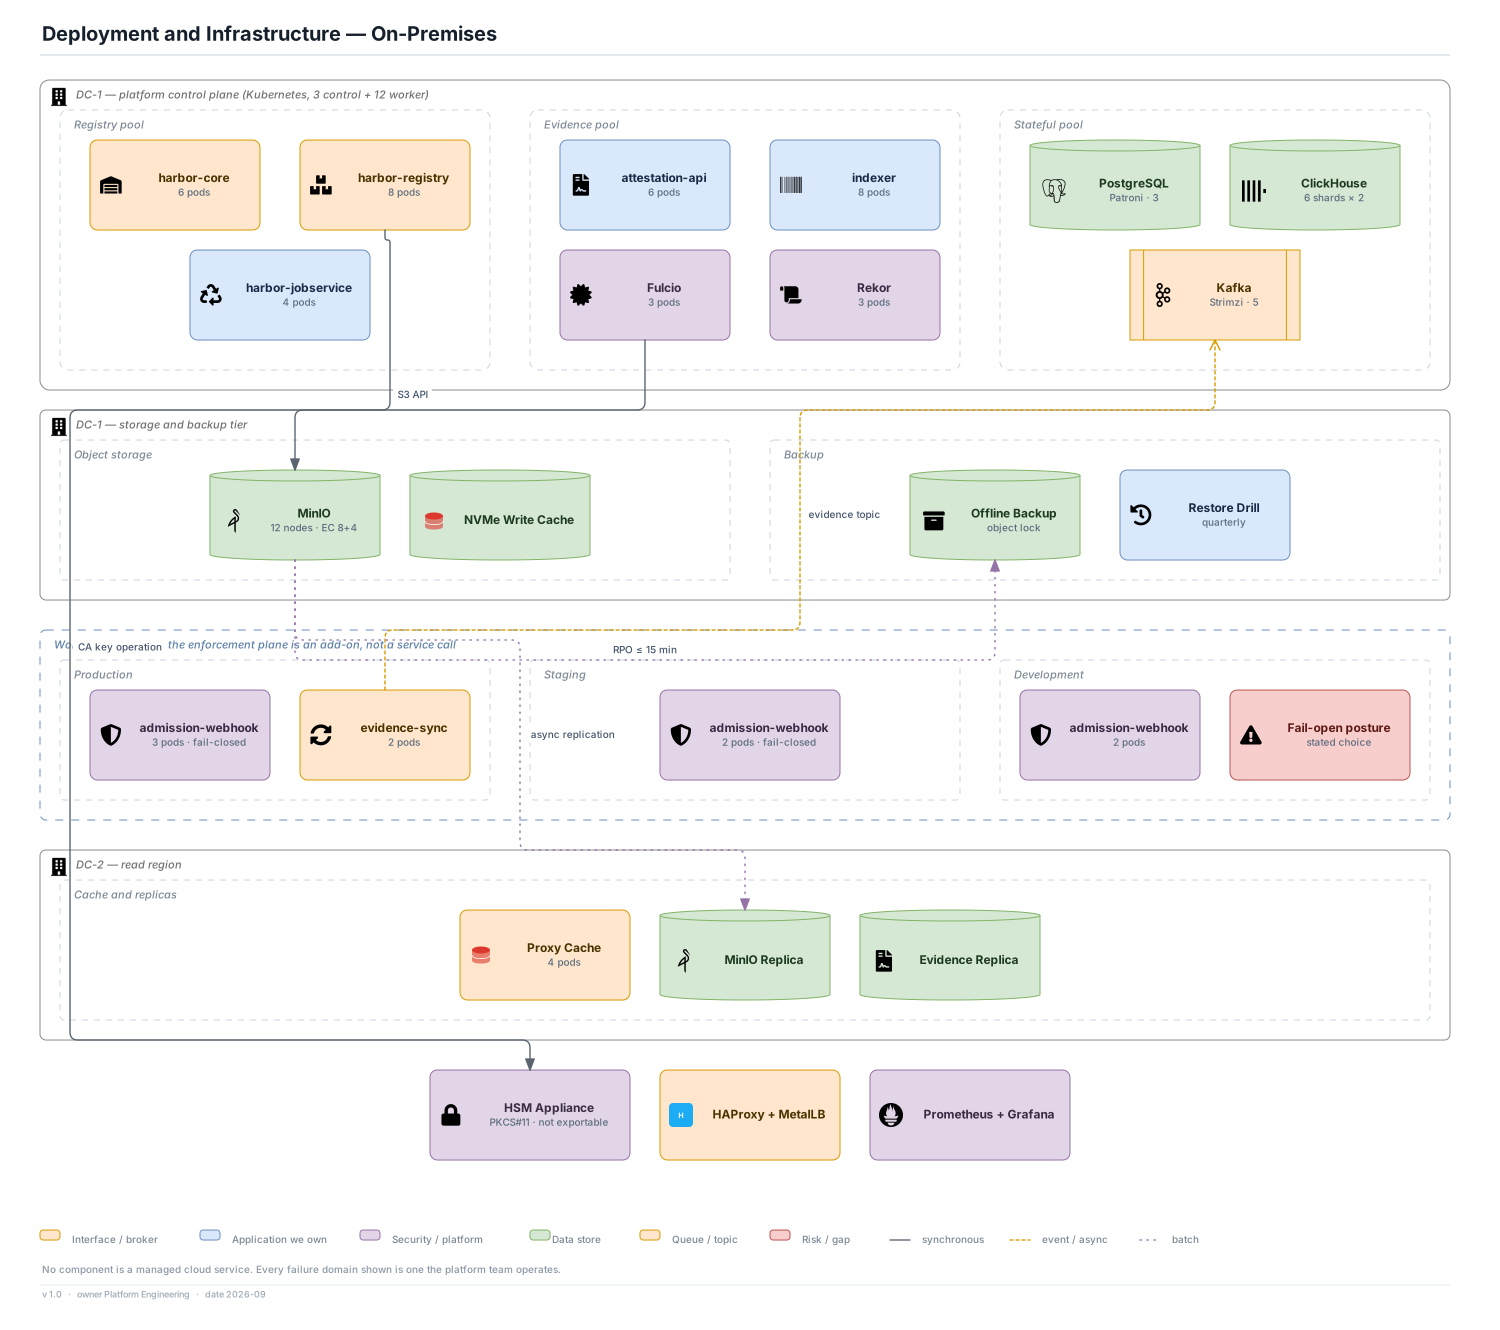
Deployment and Infrastructure
What runs where, on hardware the team owns, and which failure domains that creates.
-
24
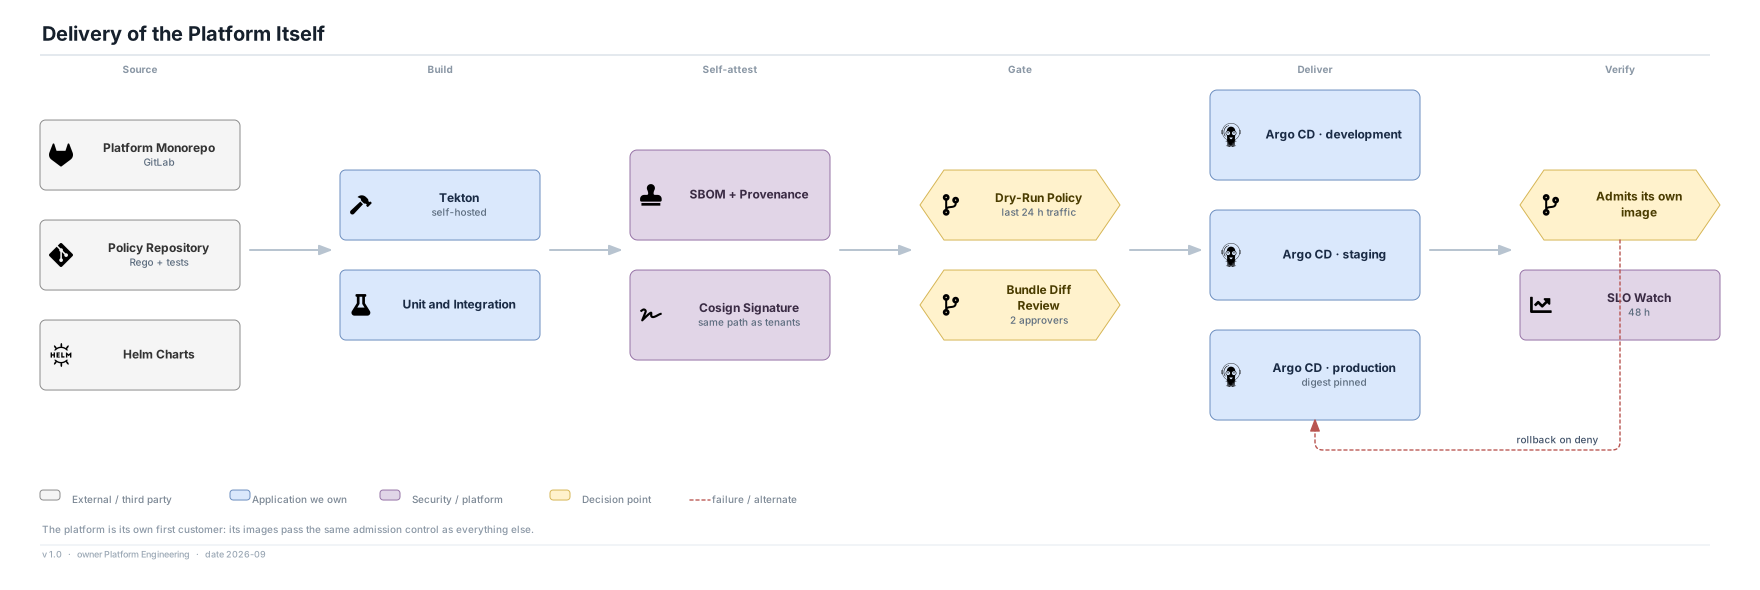
Delivery of the Platform Itself
How a change to the platform reaches production, through the platform's own gates.
-
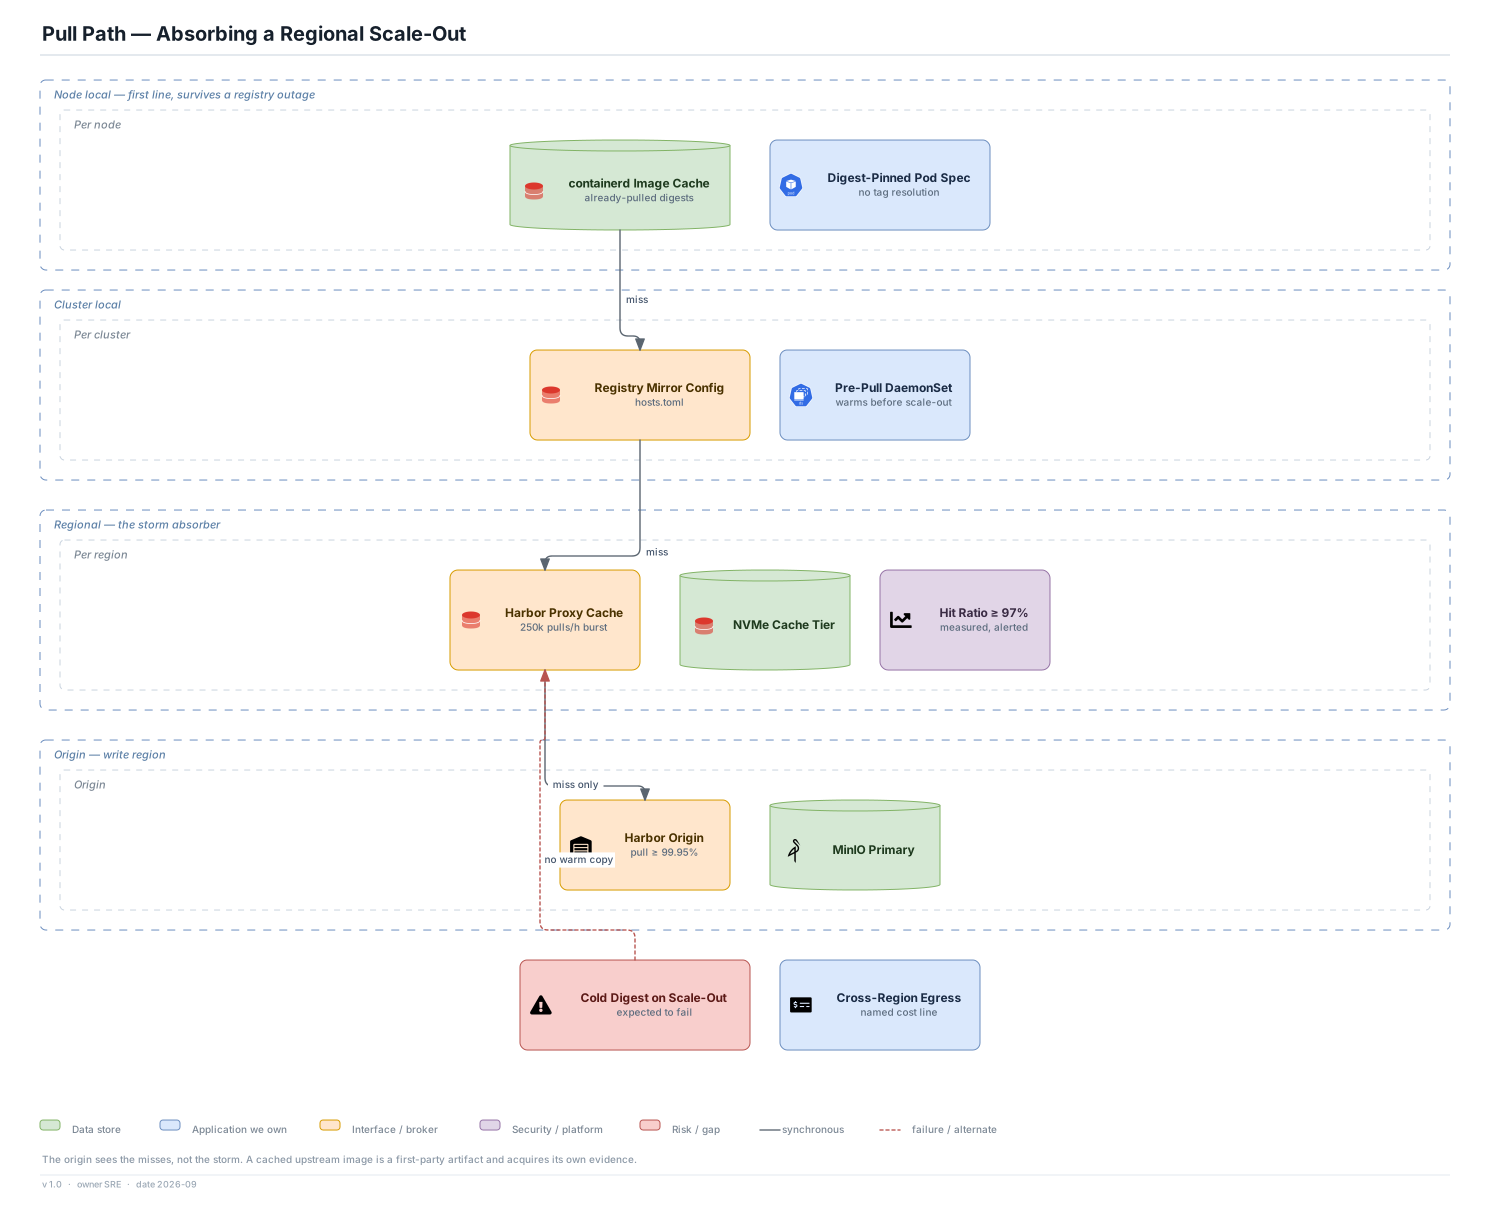
25
Pull Path and Storm Absorption
What happens when a regional cluster scales out and 250,000 pulls an hour arrive for the same digest.
-
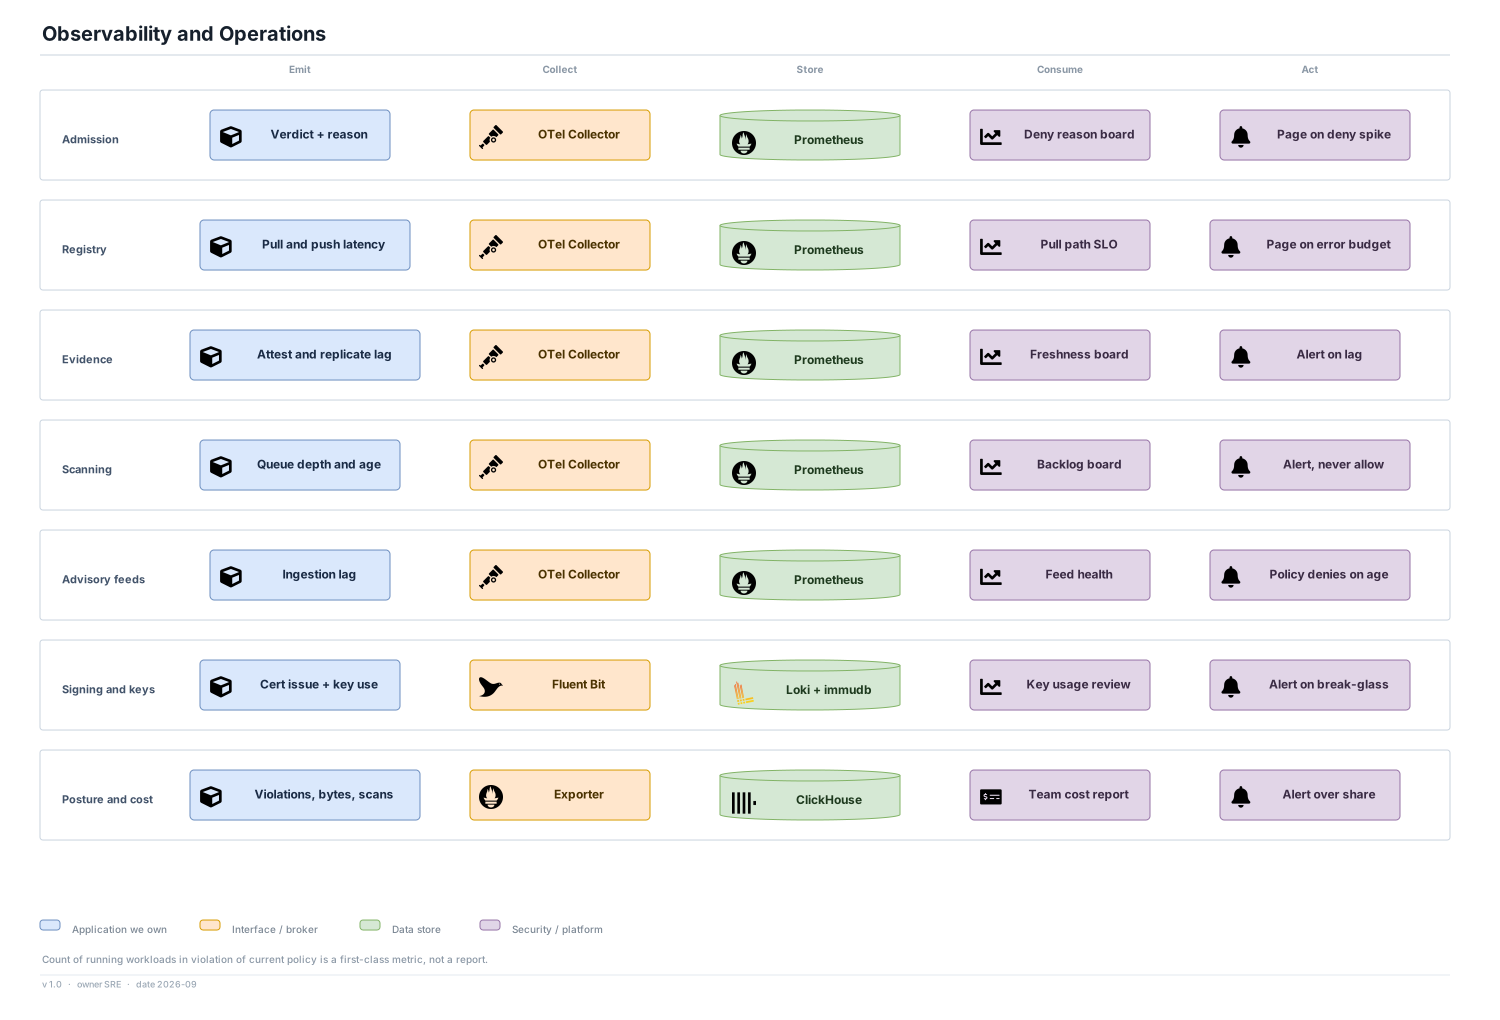
26
Observability and Operations
Which signals exist, where they go, and which of them wake somebody up.
-
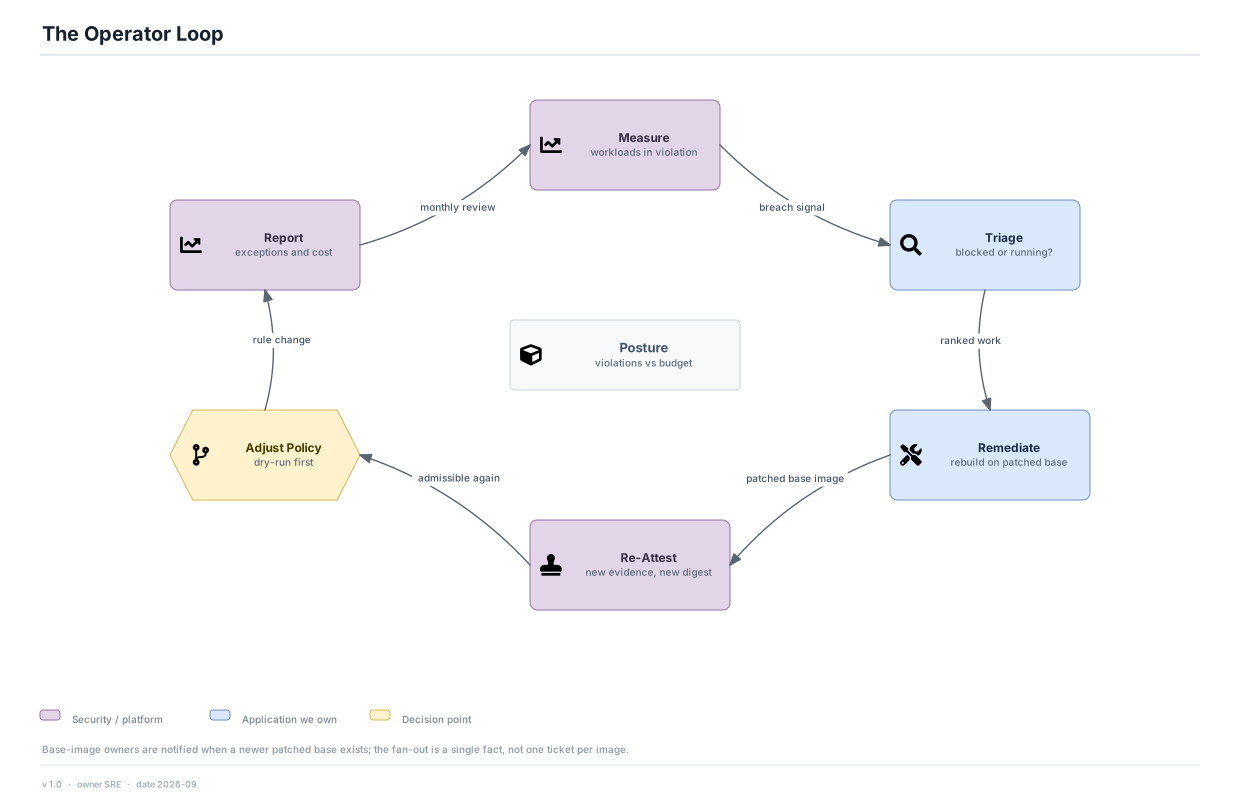
27
The Operator Loop
The weekly cycle that turns a violation count into a fixed image, and closes.
-
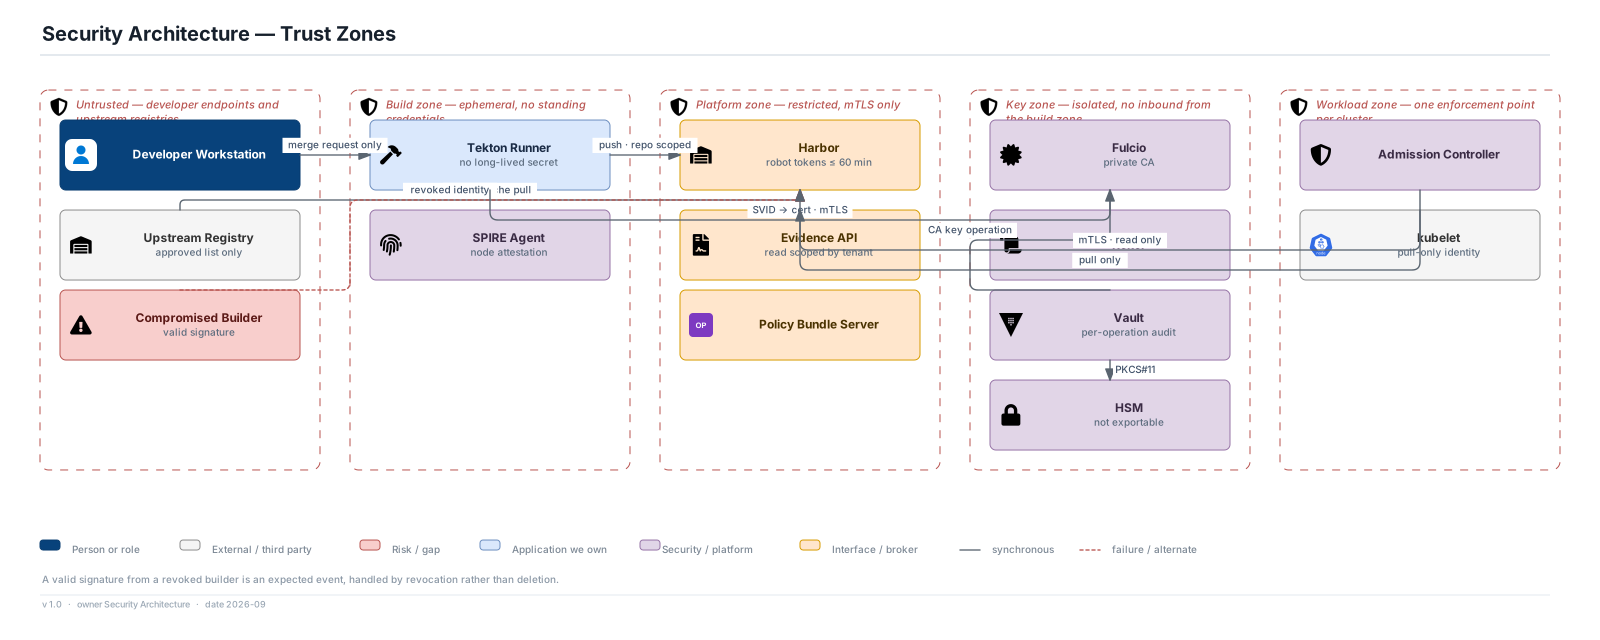
28
Security Trust Zones
Where the boundaries are, what crosses them, and where an attacker actually arrives.
-
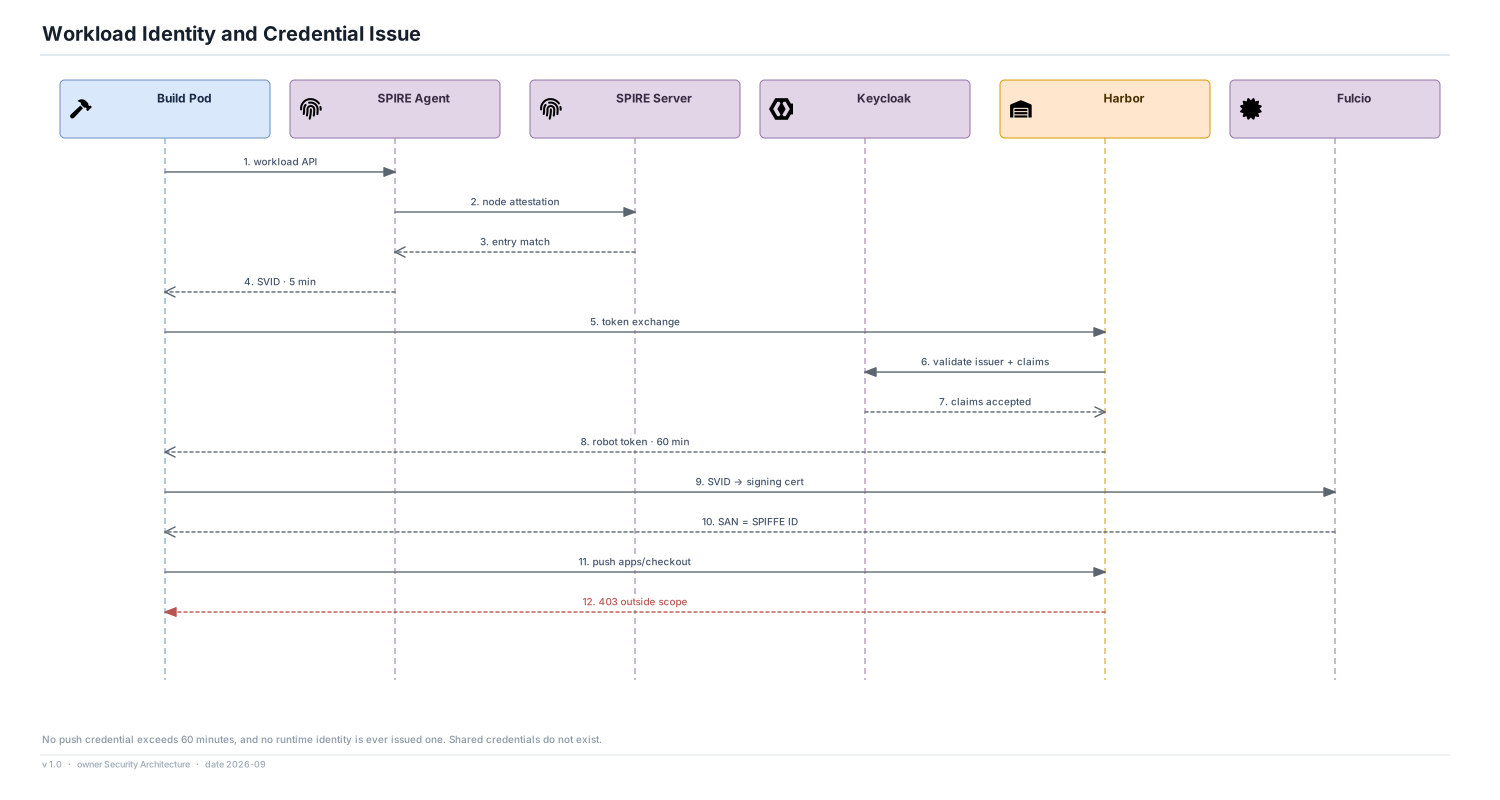
29
Workload Identity and Credentials
How a build proves what it is, and how short-lived every credential it receives actually is.
-
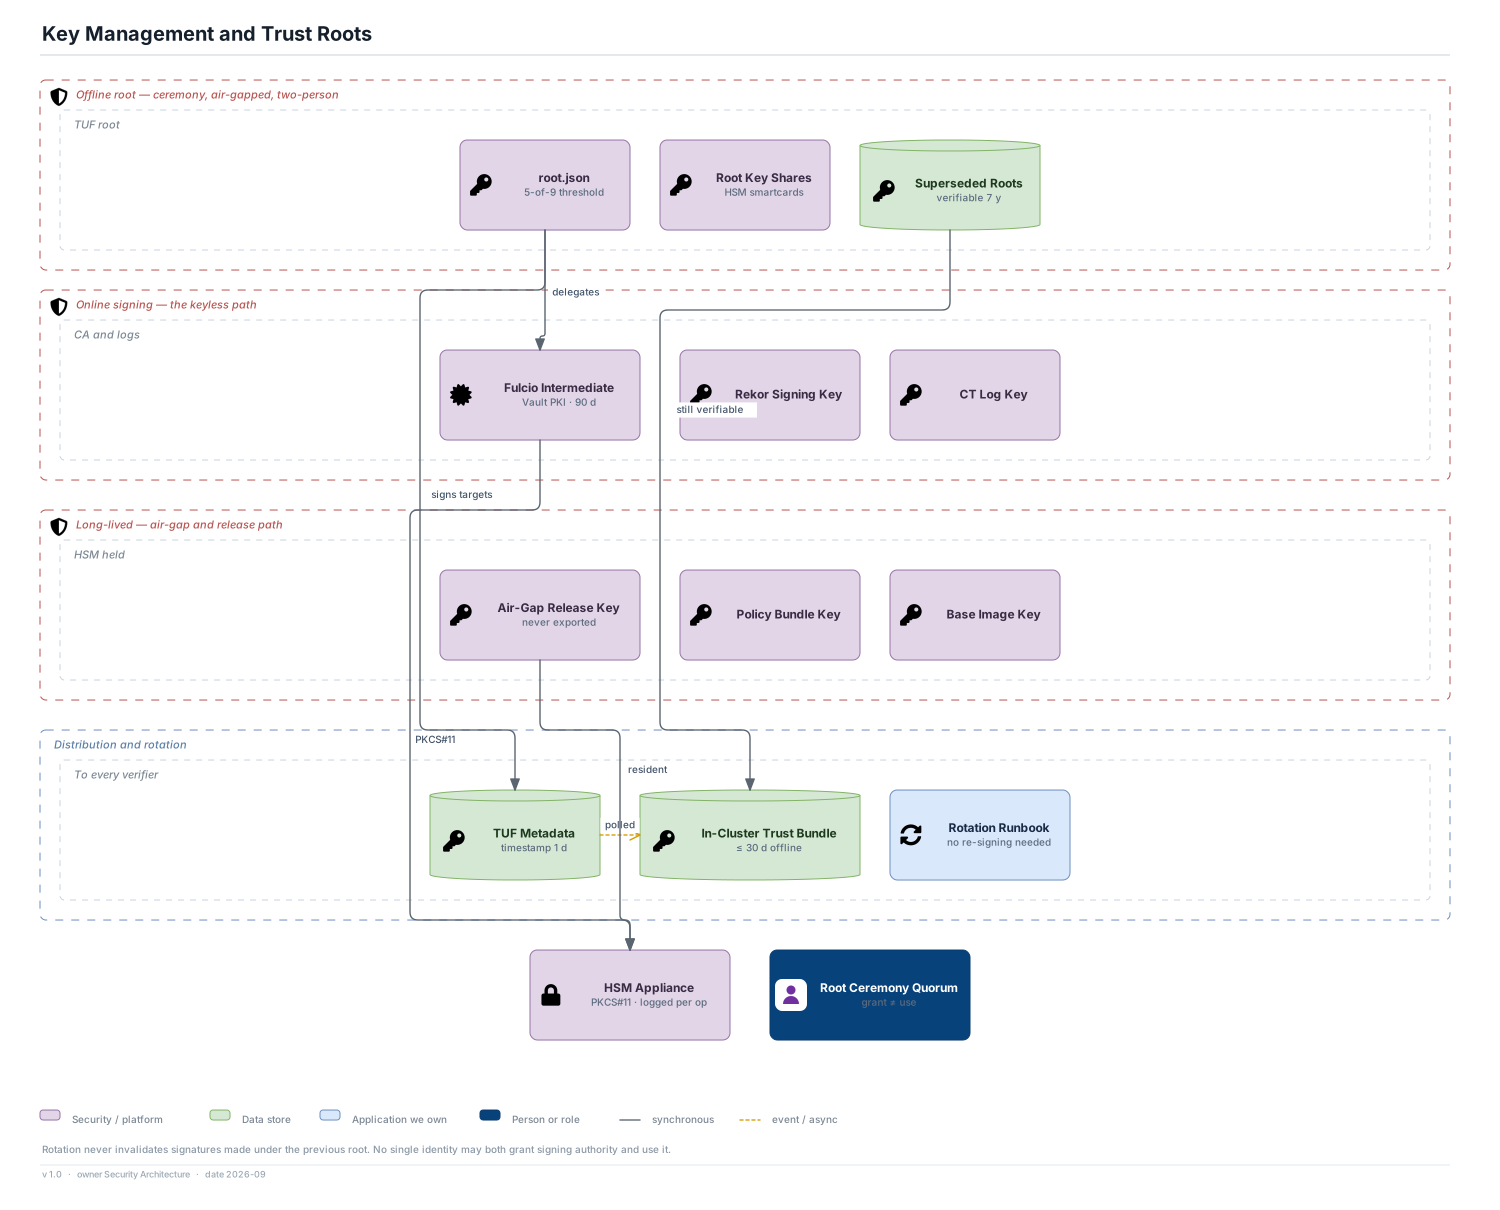
30
Key Management and Trust Roots
Which keys exist, who holds them, and what rotation does to signatures already made.
-
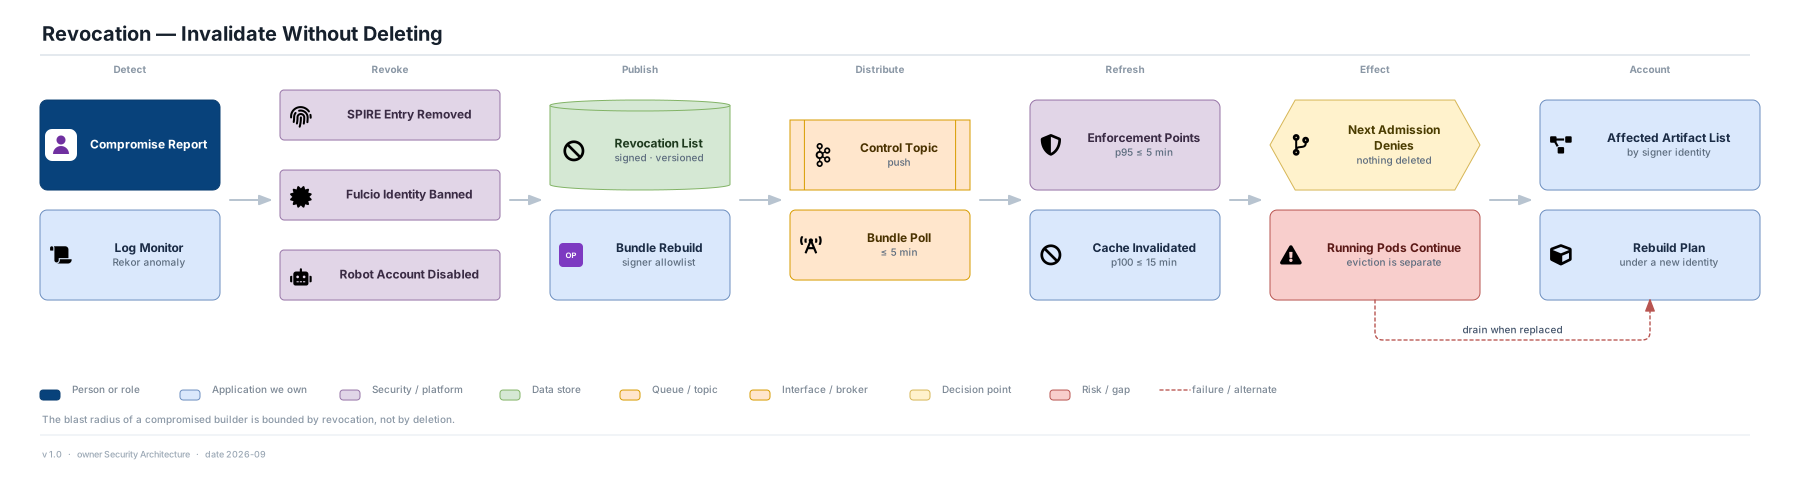
31
Revocation Propagation
How a compromised builder stops being trusted, in minutes, without deleting anything.
-
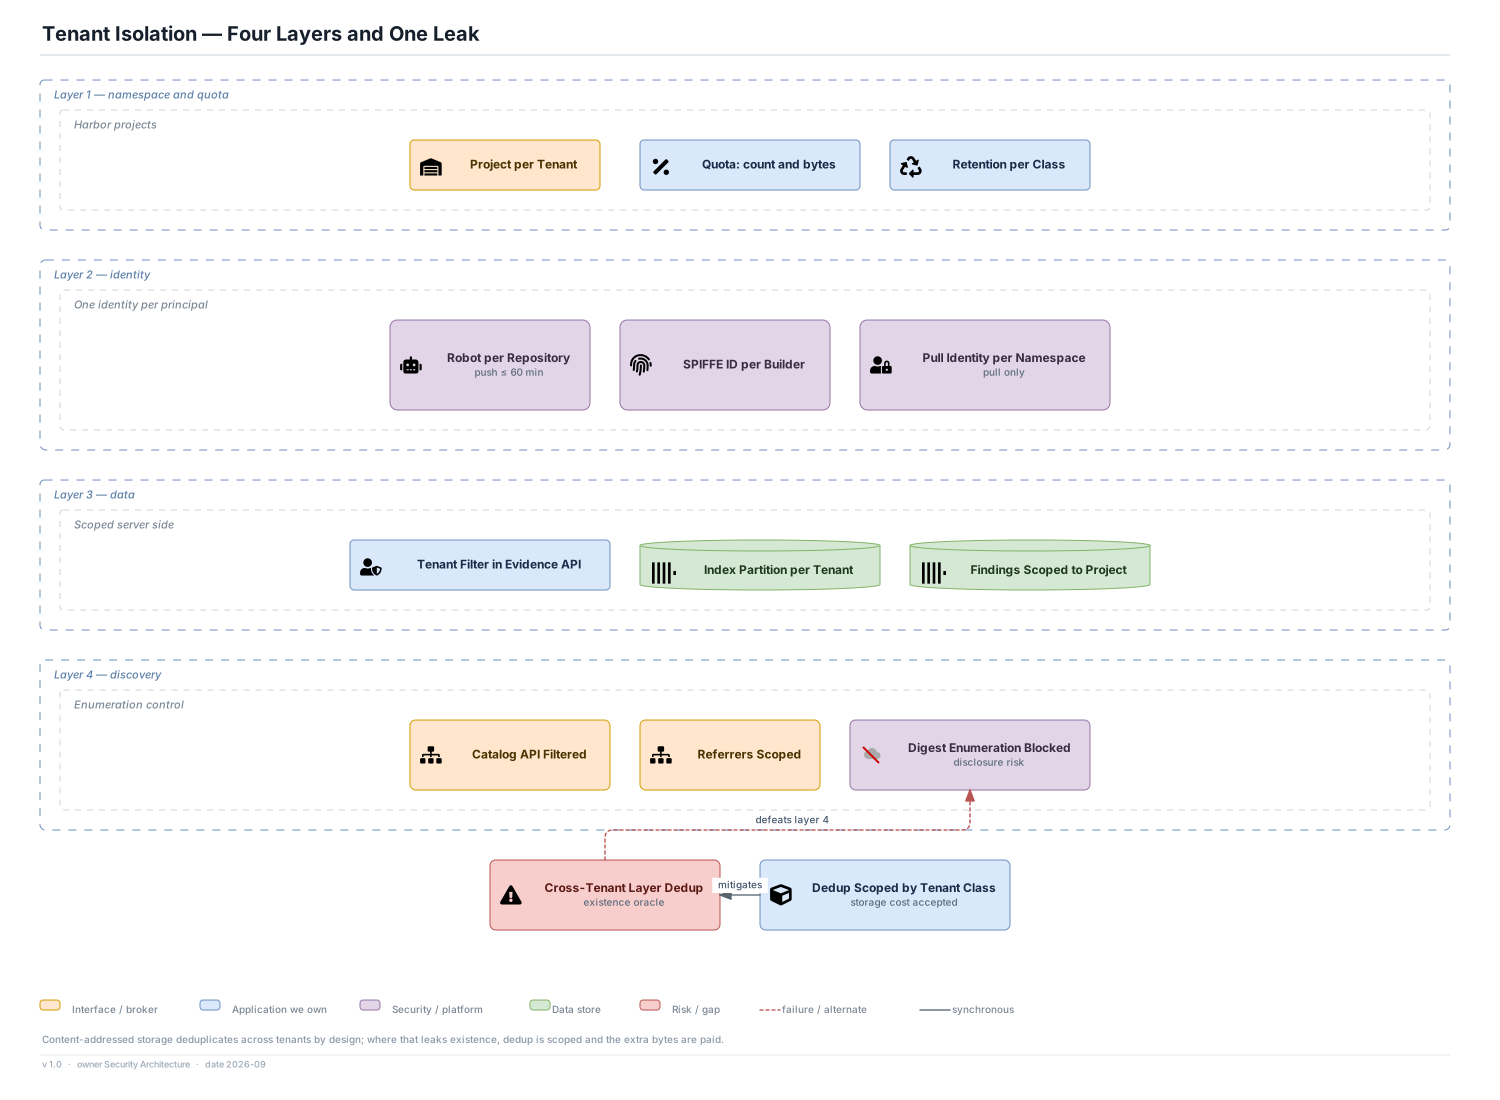
32
Tenant Isolation
Four layers that stop one tenant learning about another, and the one place content addressing leaks.
-
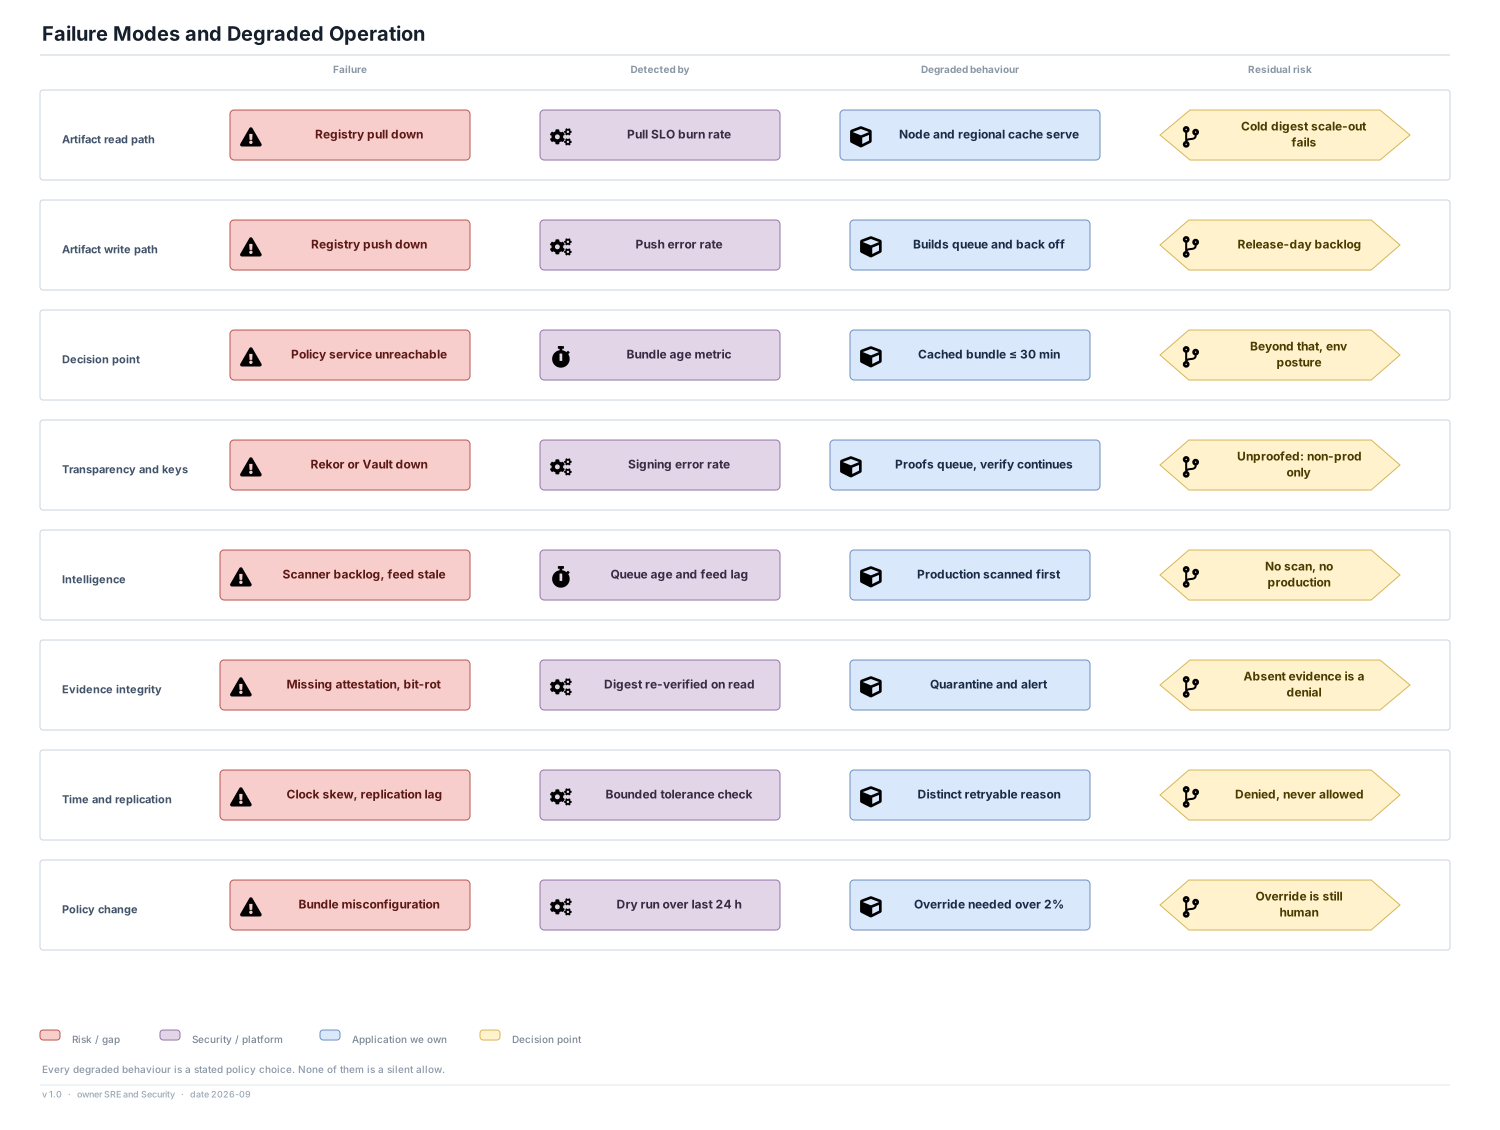
33
Failure Modes and Degraded Operation
Every named failure class, how it is detected, what the platform does, and what risk is left over.
Everything as it was delivered.
These files are served exactly as they were produced — the diagram pages keep their own house style because that is the artifact, not a rendering of it.