Container Registry and Software Supply Chain Platform  ·  View 28 of 33  ·  6 · Assurance

Security Trust Zones

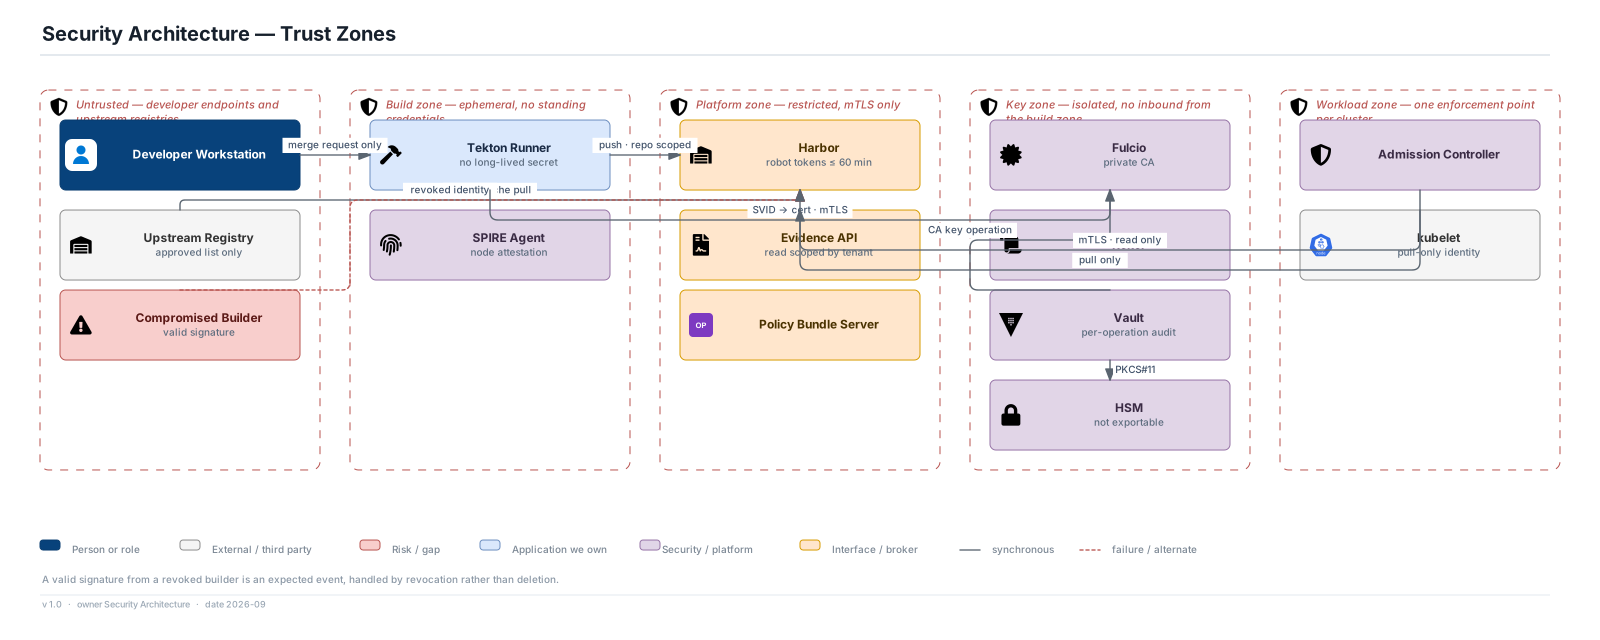
Where the boundaries are, what crosses them, and where an attacker actually arrives.

Editable source SVG draw.io All views
Untrusted — developer endpoints and upstream registries Developer Workstation Upstream Registry approved list only Compromised Builder valid signature Build zone — ephemeral, no standing credentials Tekton Runner no long-lived secret SPIRE Agent node attestation Platform zone — restricted, mTLS only Harbor robot tokens ≤ 60 min Evidence API read scoped by tenant Policy Bundle Server Key zone — isolated, no inbound from the build zone Fulcio private CA Rekor Vault per-operation audit HSM not exportable Workload zone — one enforcement point per cluster Admission Controller kubelet pull-only identity merge request only proxy cache pull revoked identity push · repo scoped SVID → cert · mTLS CA key operation PKCS#11 mTLS · read only pull only Security Architecture — Trust Zones Person or role External / third party Risk / gap Application we own Security / platform Interface / broker synchronous failure / alternate A valid signature from a revoked builder is an expected event, handled by revocation rather than deletion. v 1.0 · owner Security Architecture · date 2026-09

Decisions

  • Every principal — human, build system, cluster node, controller — has a distinct identity; shared registry credentials do not exist
  • The key zone accepts no inbound connection from the build zone except certificate issue, and that call is mTLS with a SPIFFE identity
  • Artifacts and evidence are encrypted at rest with customer-managed keys and all traffic in transit

The assumed compromise

  • A valid signature from a compromised build identity is an expected event, not a surprise
  • Revocation of a builder identity invalidates its artifacts at admission without requiring their deletion
  • Break-glass access to the control plane requires two-person authorisation, has a maximum session length, and alerts on use

Deliberately omitted

  • Network segmentation below the zone level — VLANs and firewall rules are an infrastructure deliverable
  • Threat model in full — this view shows the boundaries, not the attack tree