Container Registry and Software Supply Chain Platform · View 30 of 33 · 6 · Assurance
Decisions
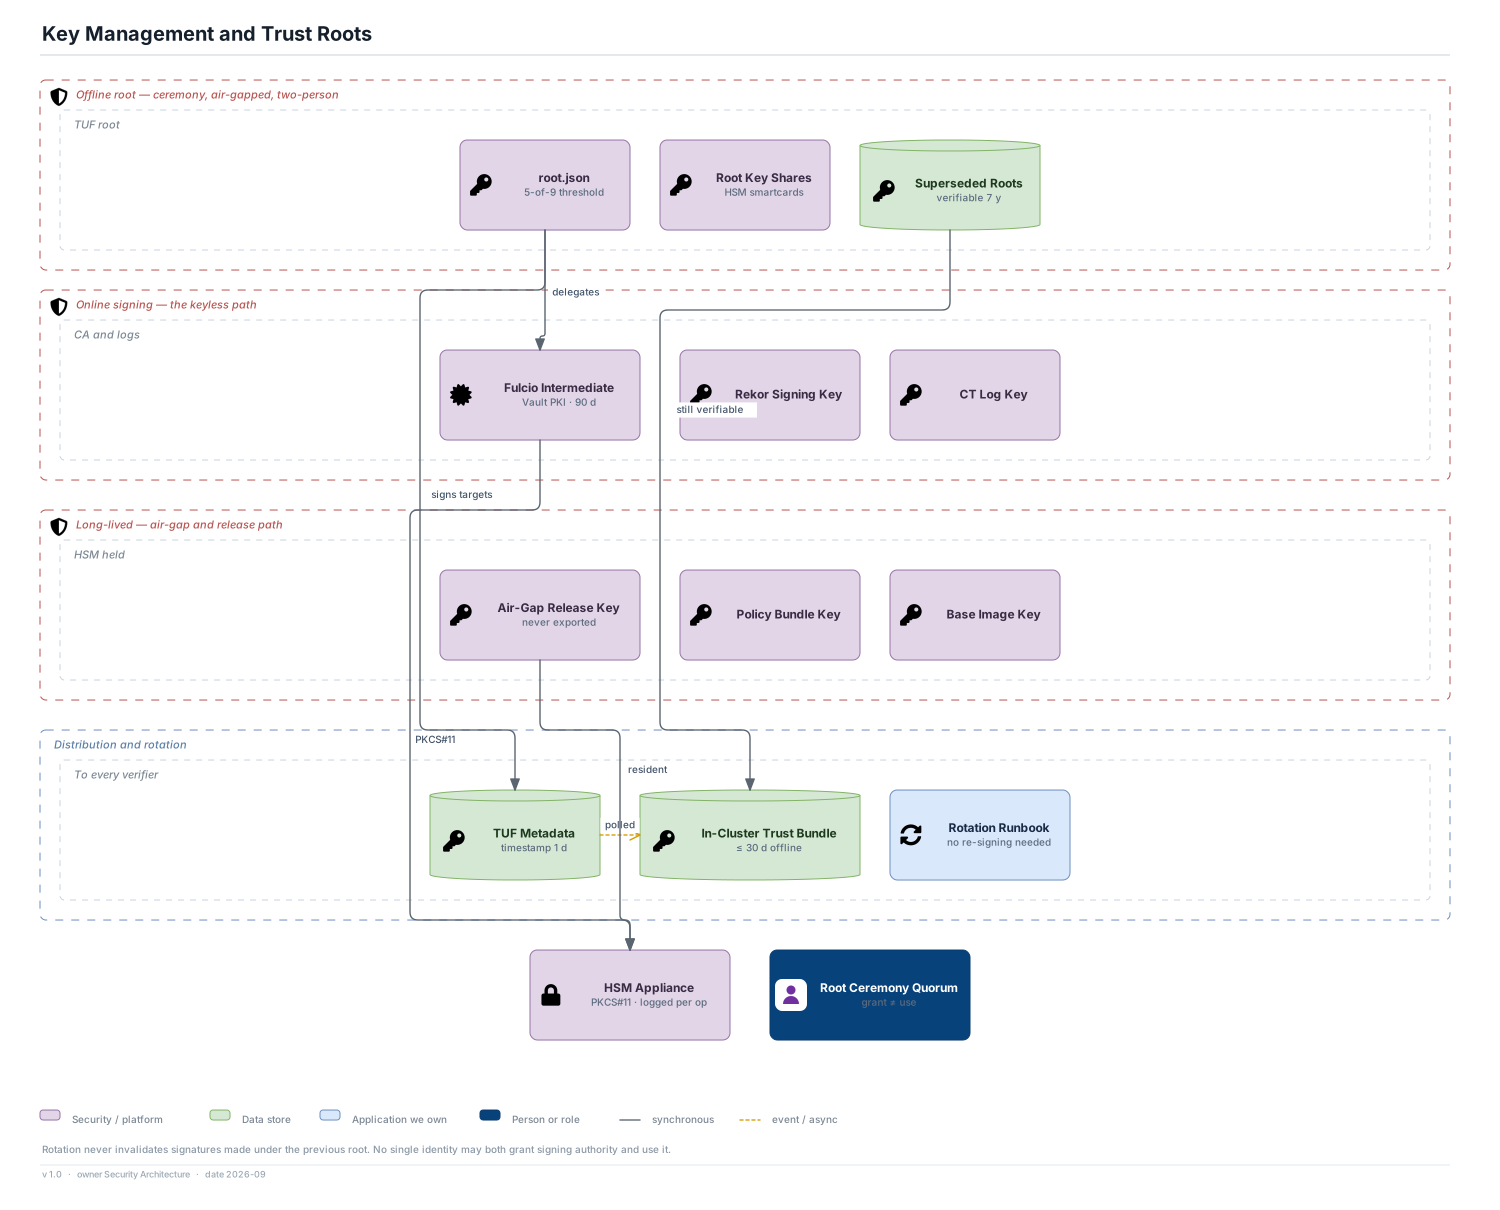
- TUF root with a 5-of-9 threshold, held on HSM smartcards, exercised in an air-gapped ceremony
- Online signing uses a Fulcio intermediate whose key lives in Vault backed by the HSM, rotated every 90 days
- Long-lived keys exist only for the air-gapped release path, base-image releases and policy bundle signing
Rotation
- Trust-root rotation does not invalidate signatures produced under the previous root
- Superseded roots stay verifiable for the 7-year attestation retention period
- Verifiers poll TUF metadata; a cluster trust bundle is valid for 30 days offline
Risks
- The root ceremony is an organisational commitment, not a technical one; if the quorum cannot be assembled, rotation does not happen
- Key service unavailability halts signing but not verification — that asymmetry is deliberate and is what keeps deployments running