Container Registry and Software Supply Chain Platform

Architecture Views

33 views, in reading order. Every view ships three ways: an HTML page, an SVG that re-opens in diagrams.net fully editable, and draw.io source.

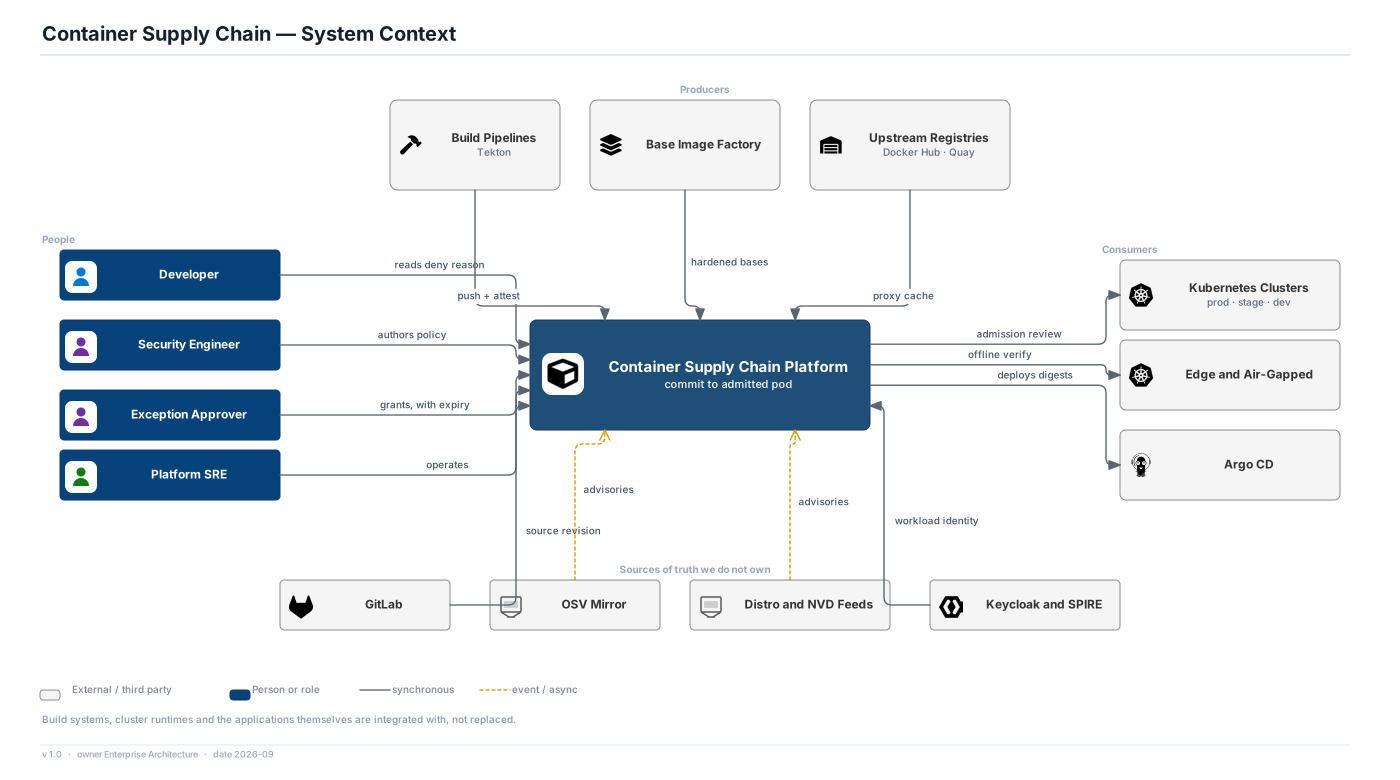
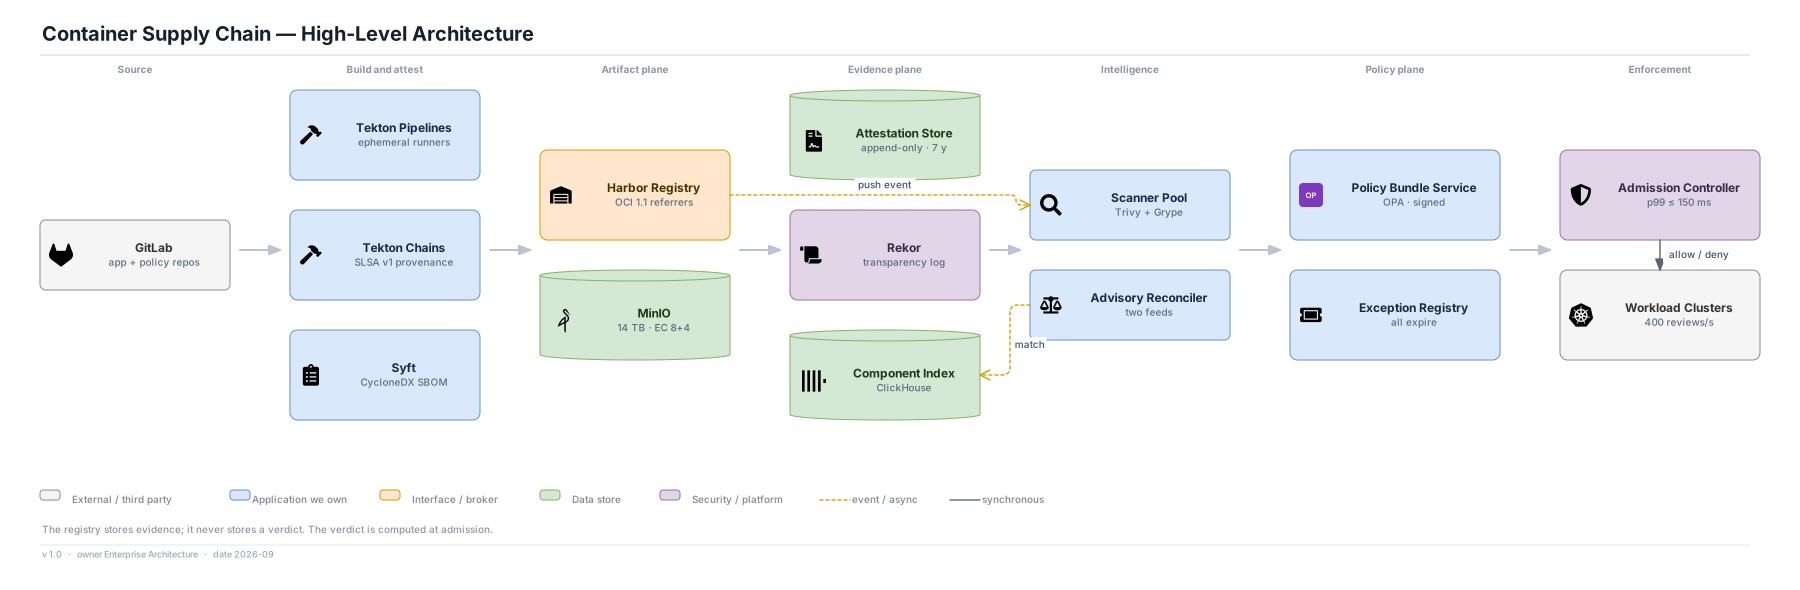
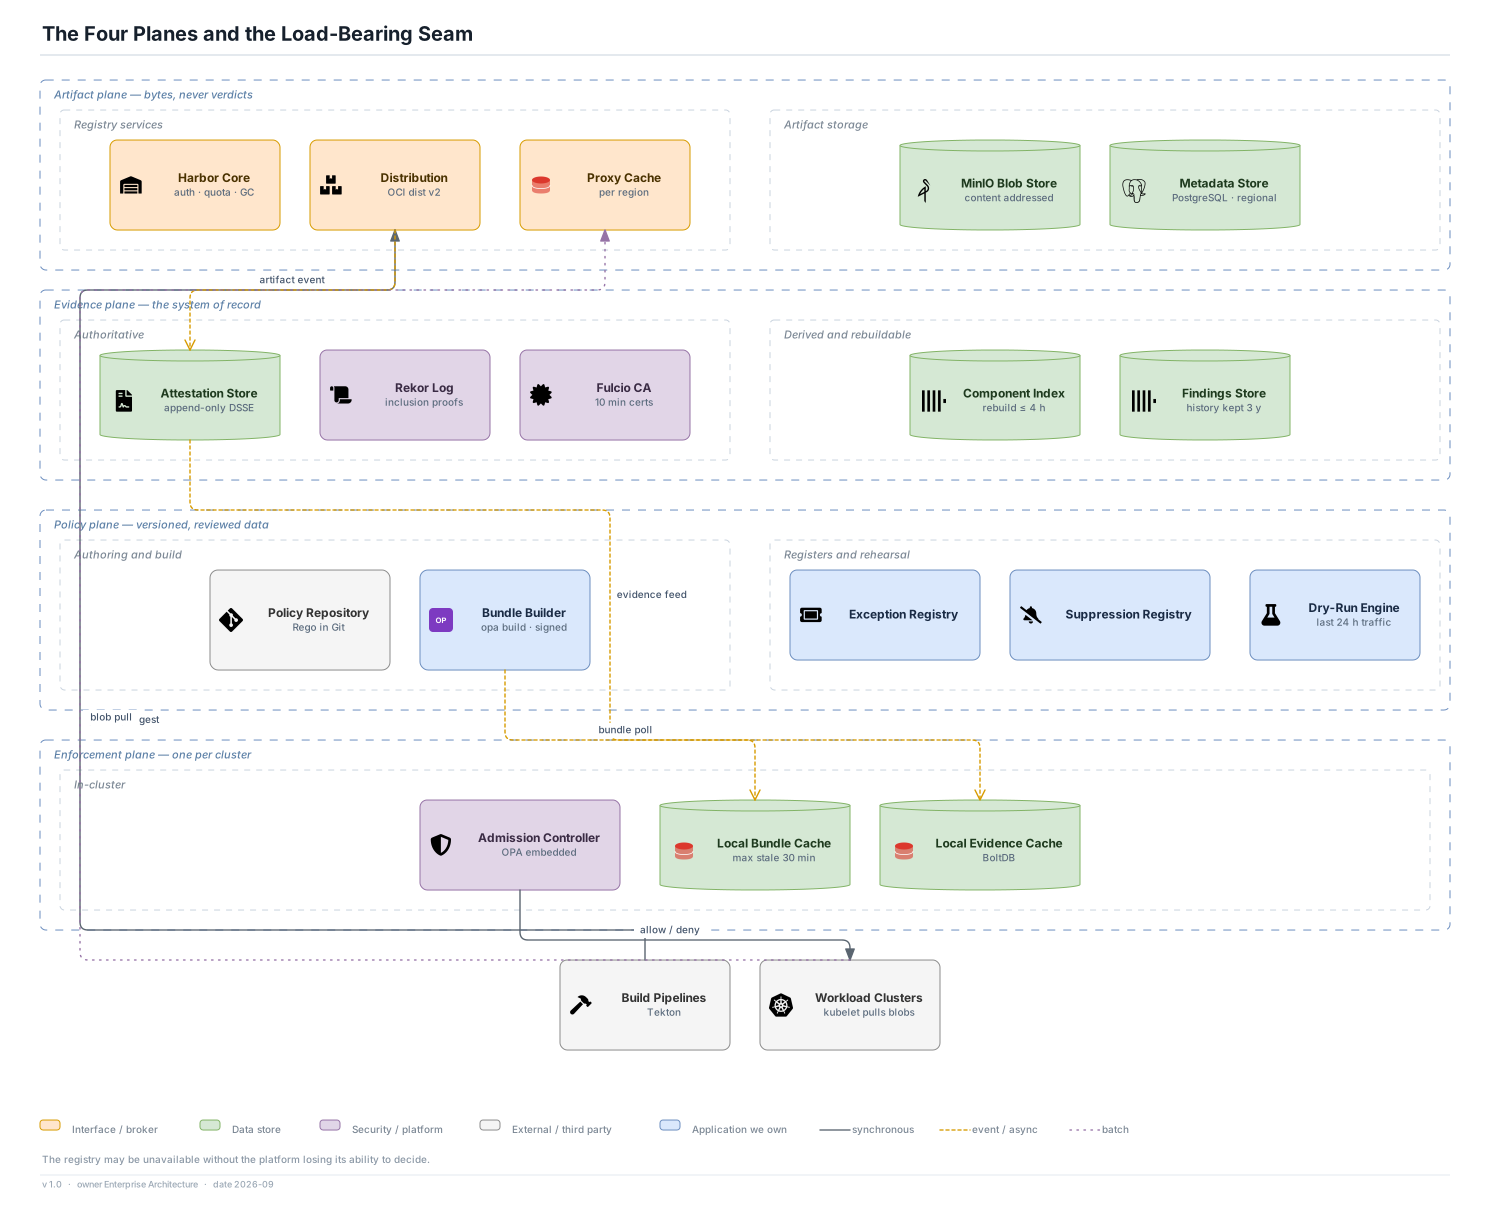
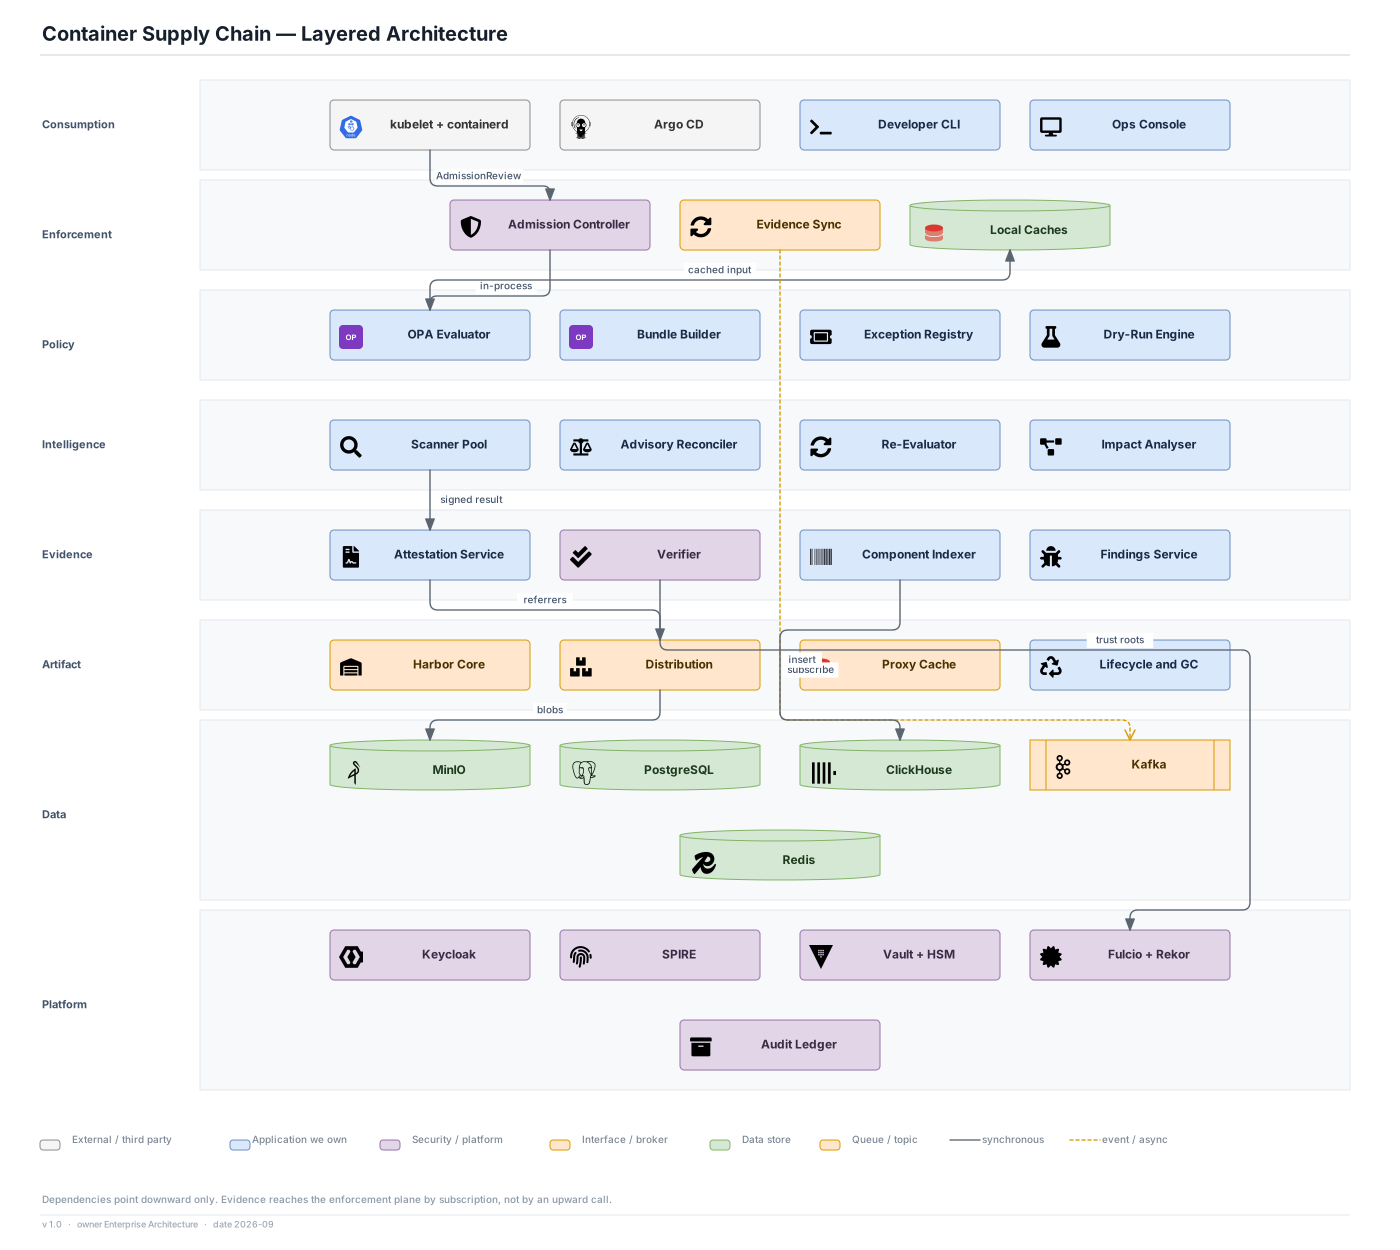
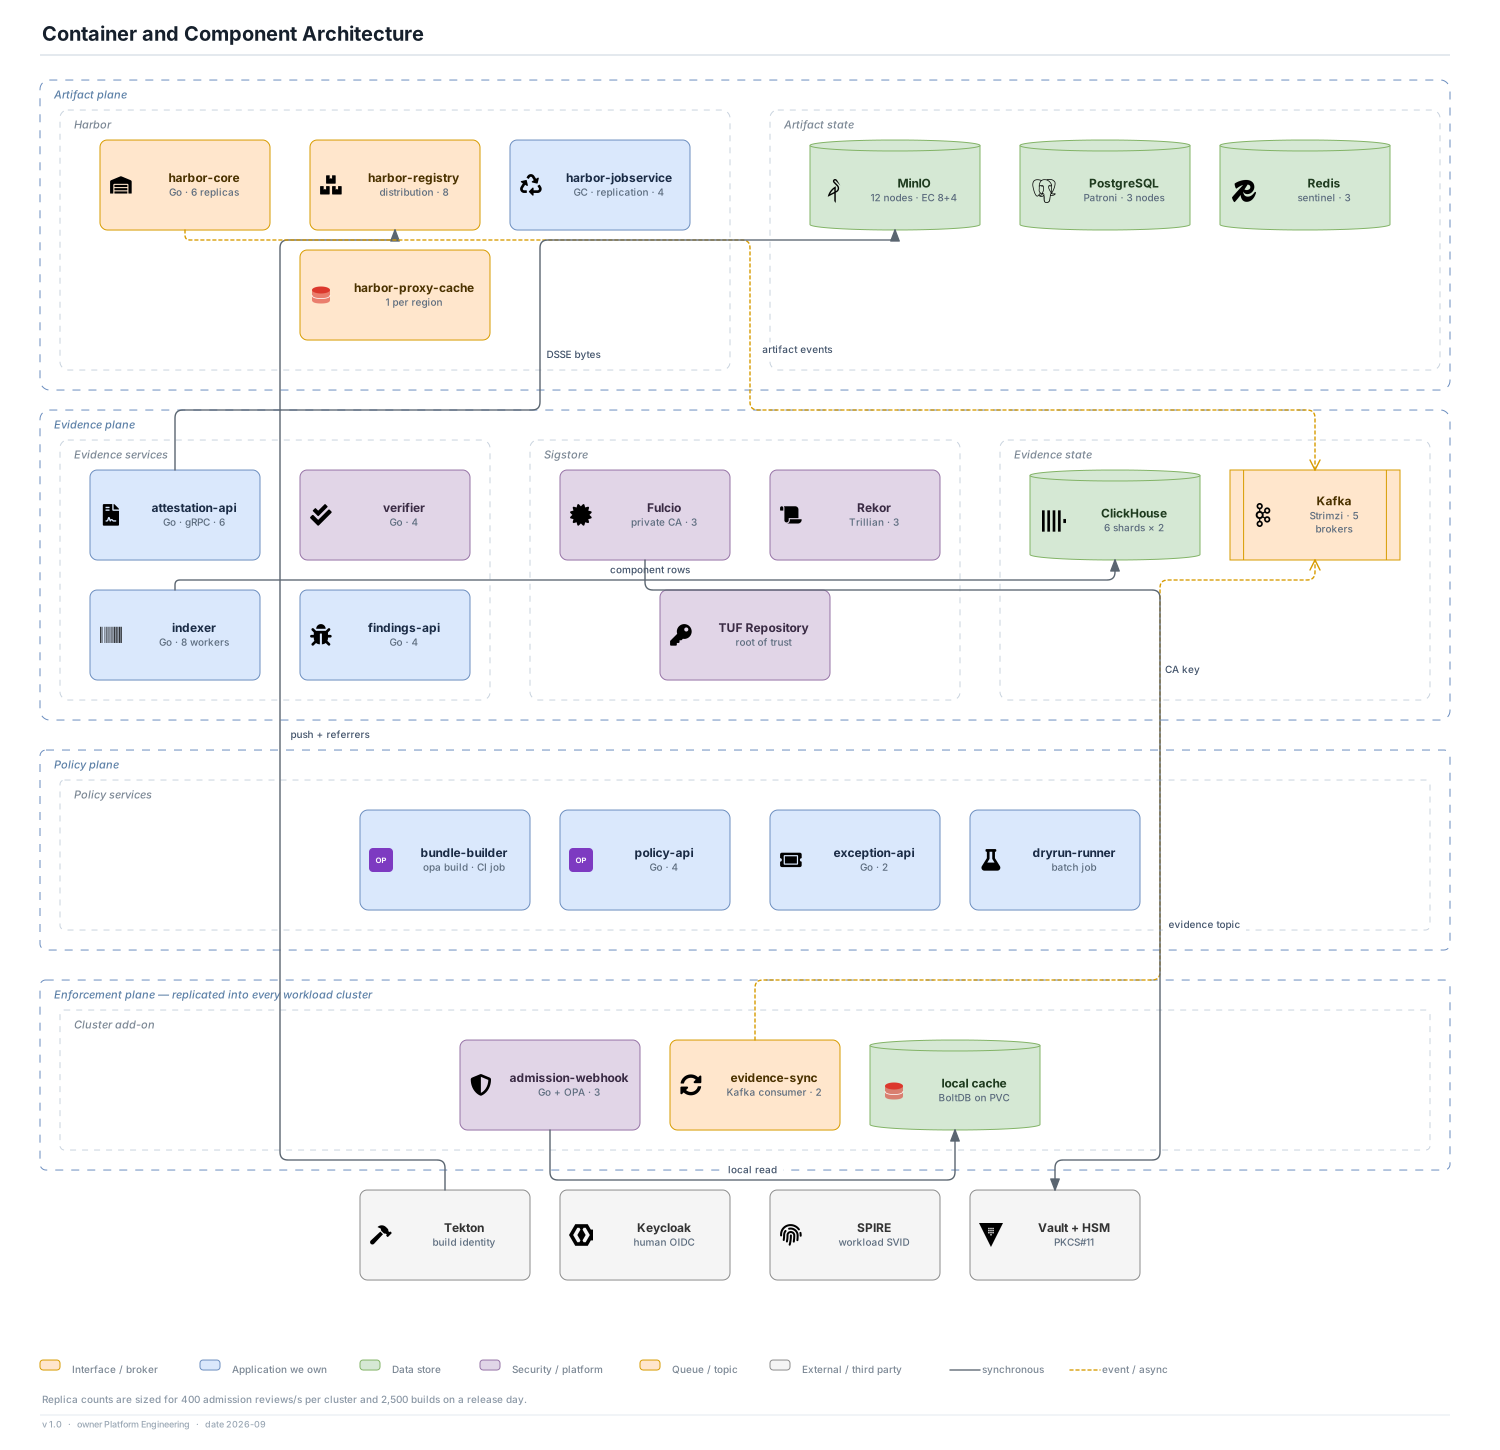
One trusted path from a source commit to a running workload, and machine-checkable evidence that the path was followed. Read the set in order: acts 1 and 2 fix the boundary and the four planes; act 3 says which store is authoritative and which is rebuildable; act 4 shows what happens when an image is built, scanned, admitted and re-evaluated; act 5 covers running it; act 6 covers why it is safe and how it degrades. One decision governs all of them — the registry stores evidence, never a verdict.

1 · Context and scope

The boundary, the producers and consumers, and the plane separation that governs everything after it.

2 · Structure

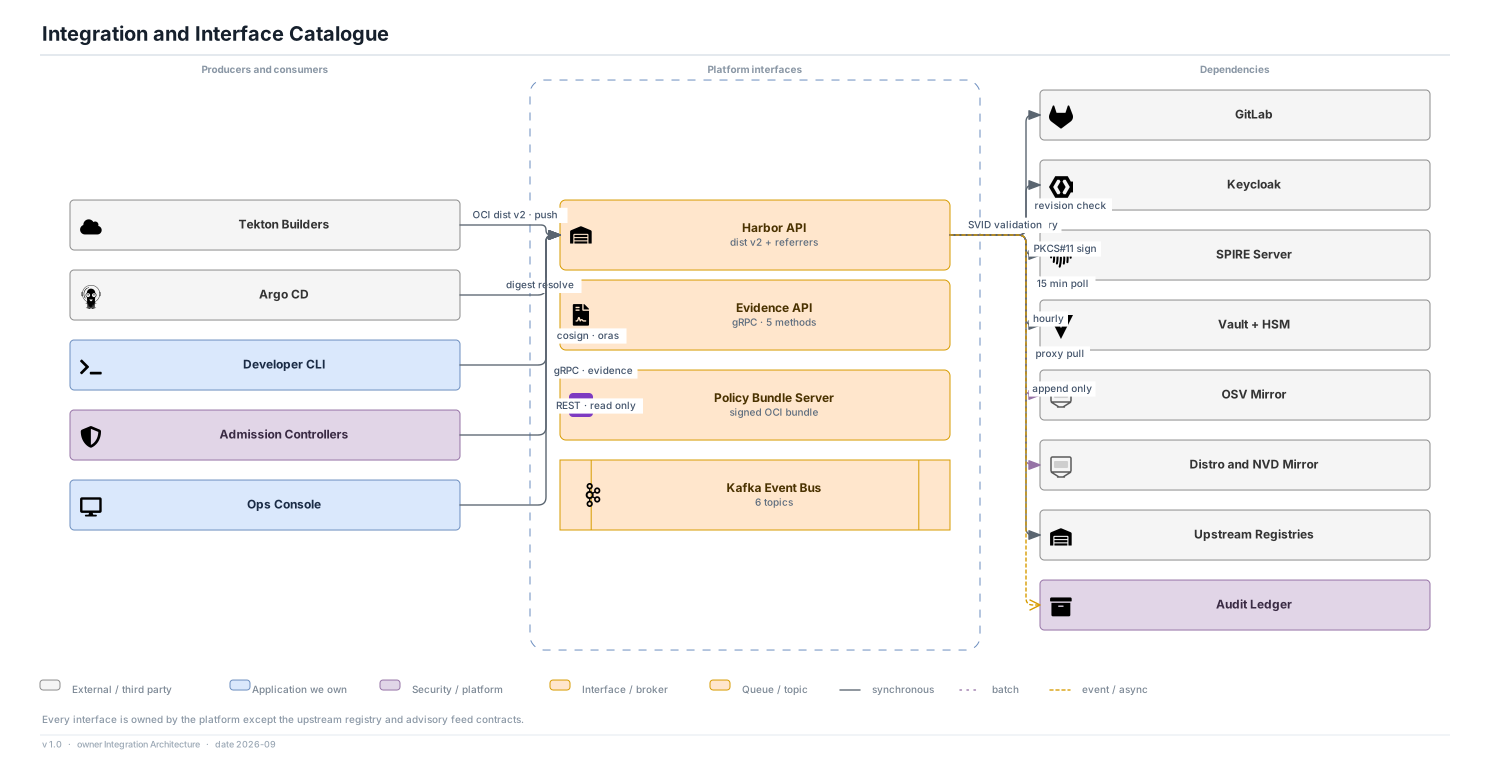
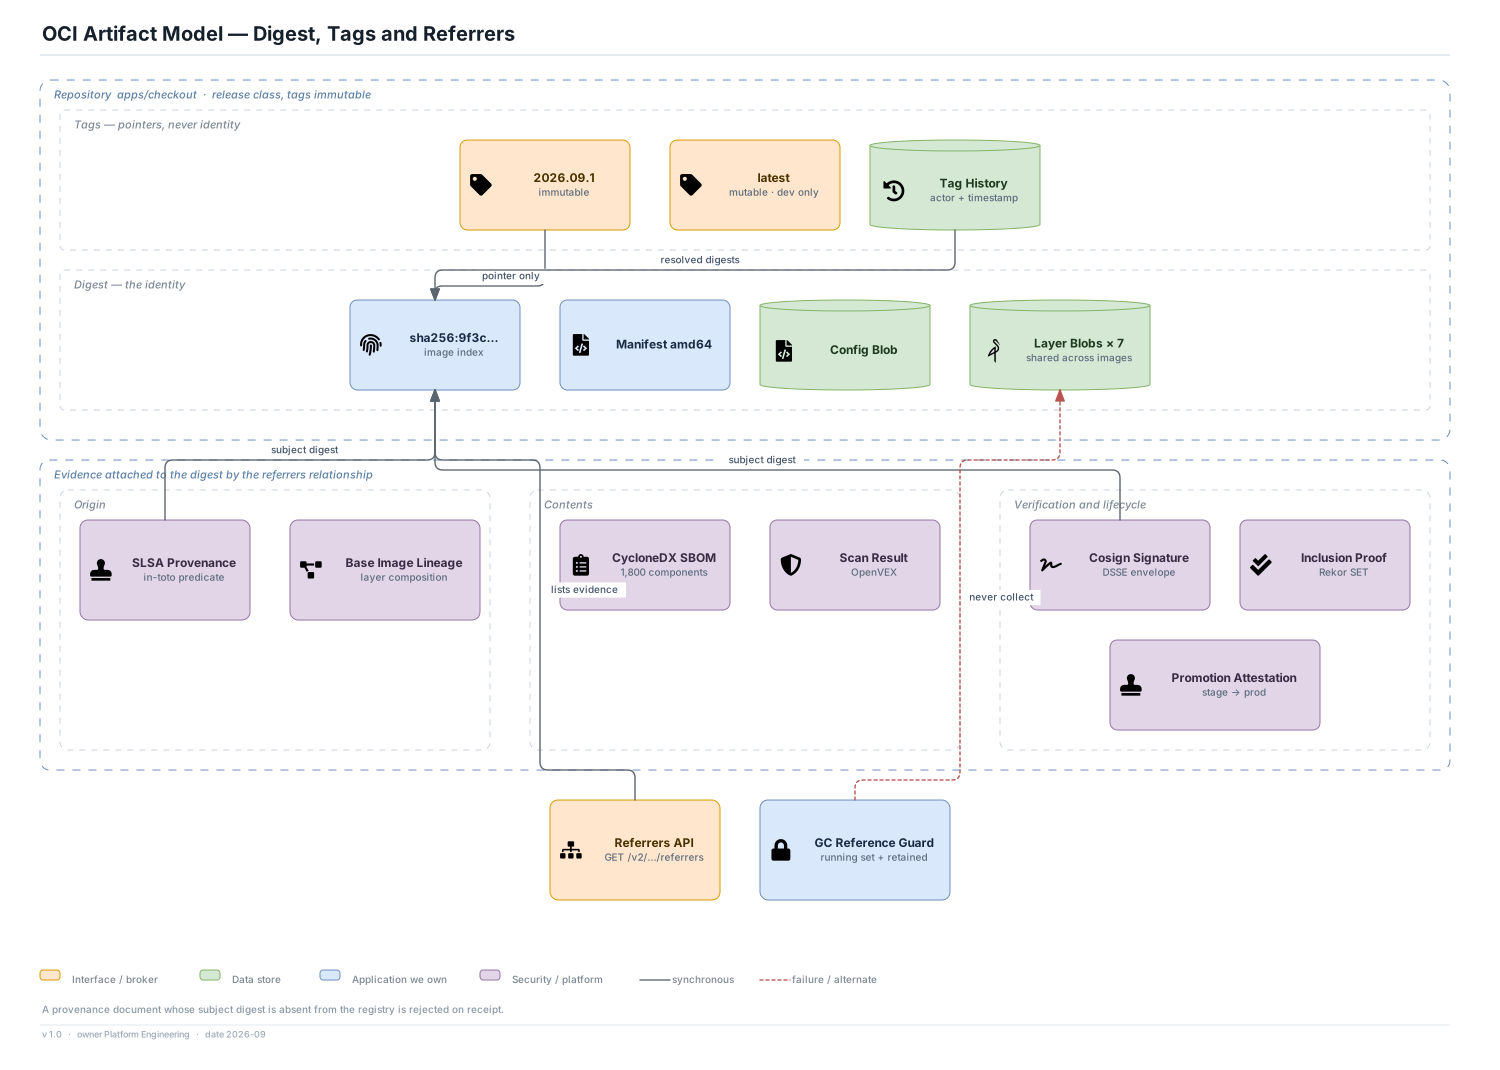
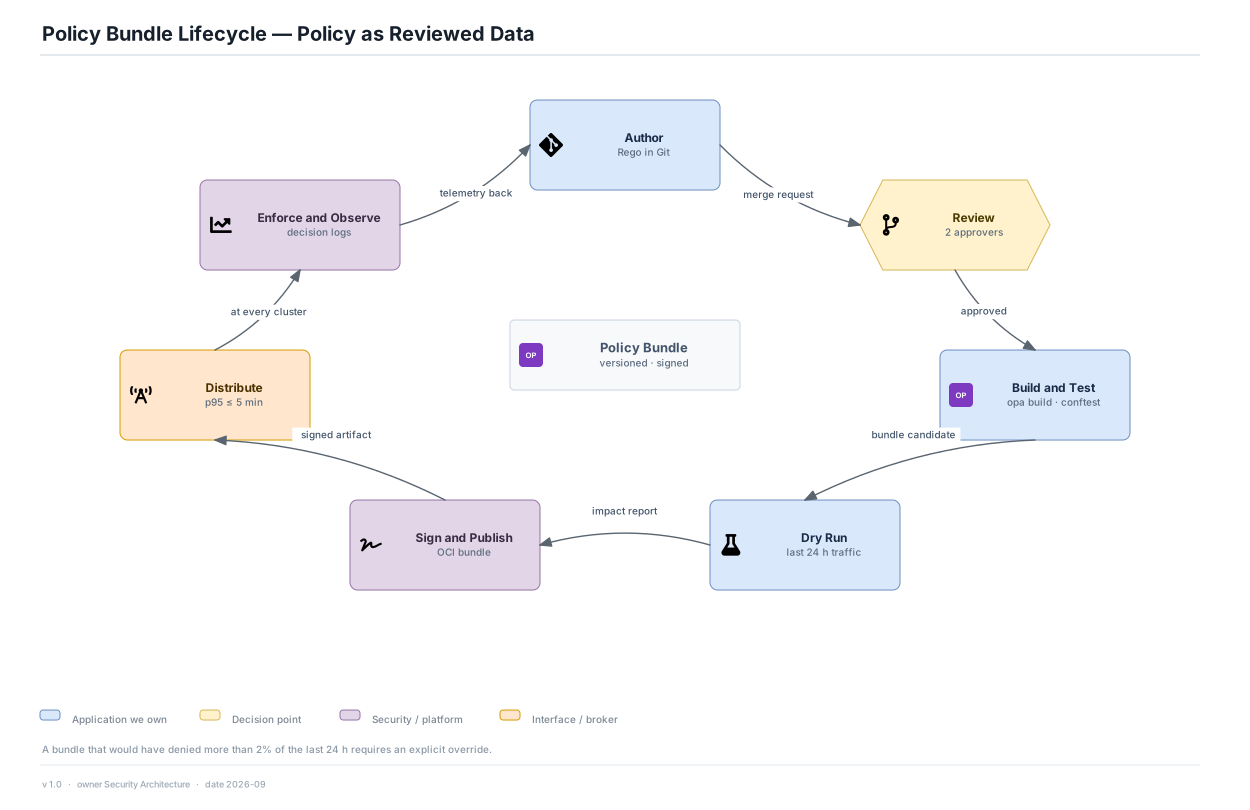
The layering rule, the deployable units, every interface, the OCI artifact model, and how policy becomes reviewed data.

3 · Data

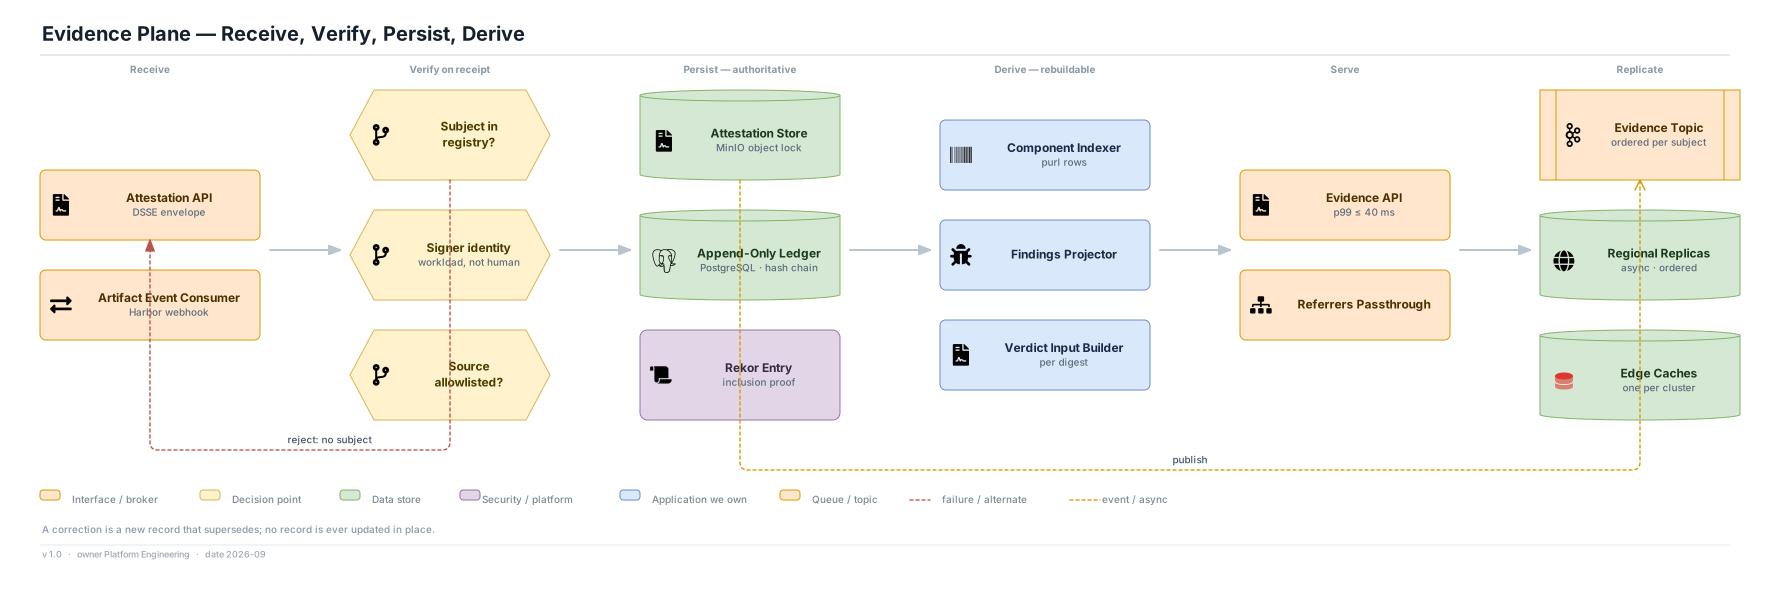
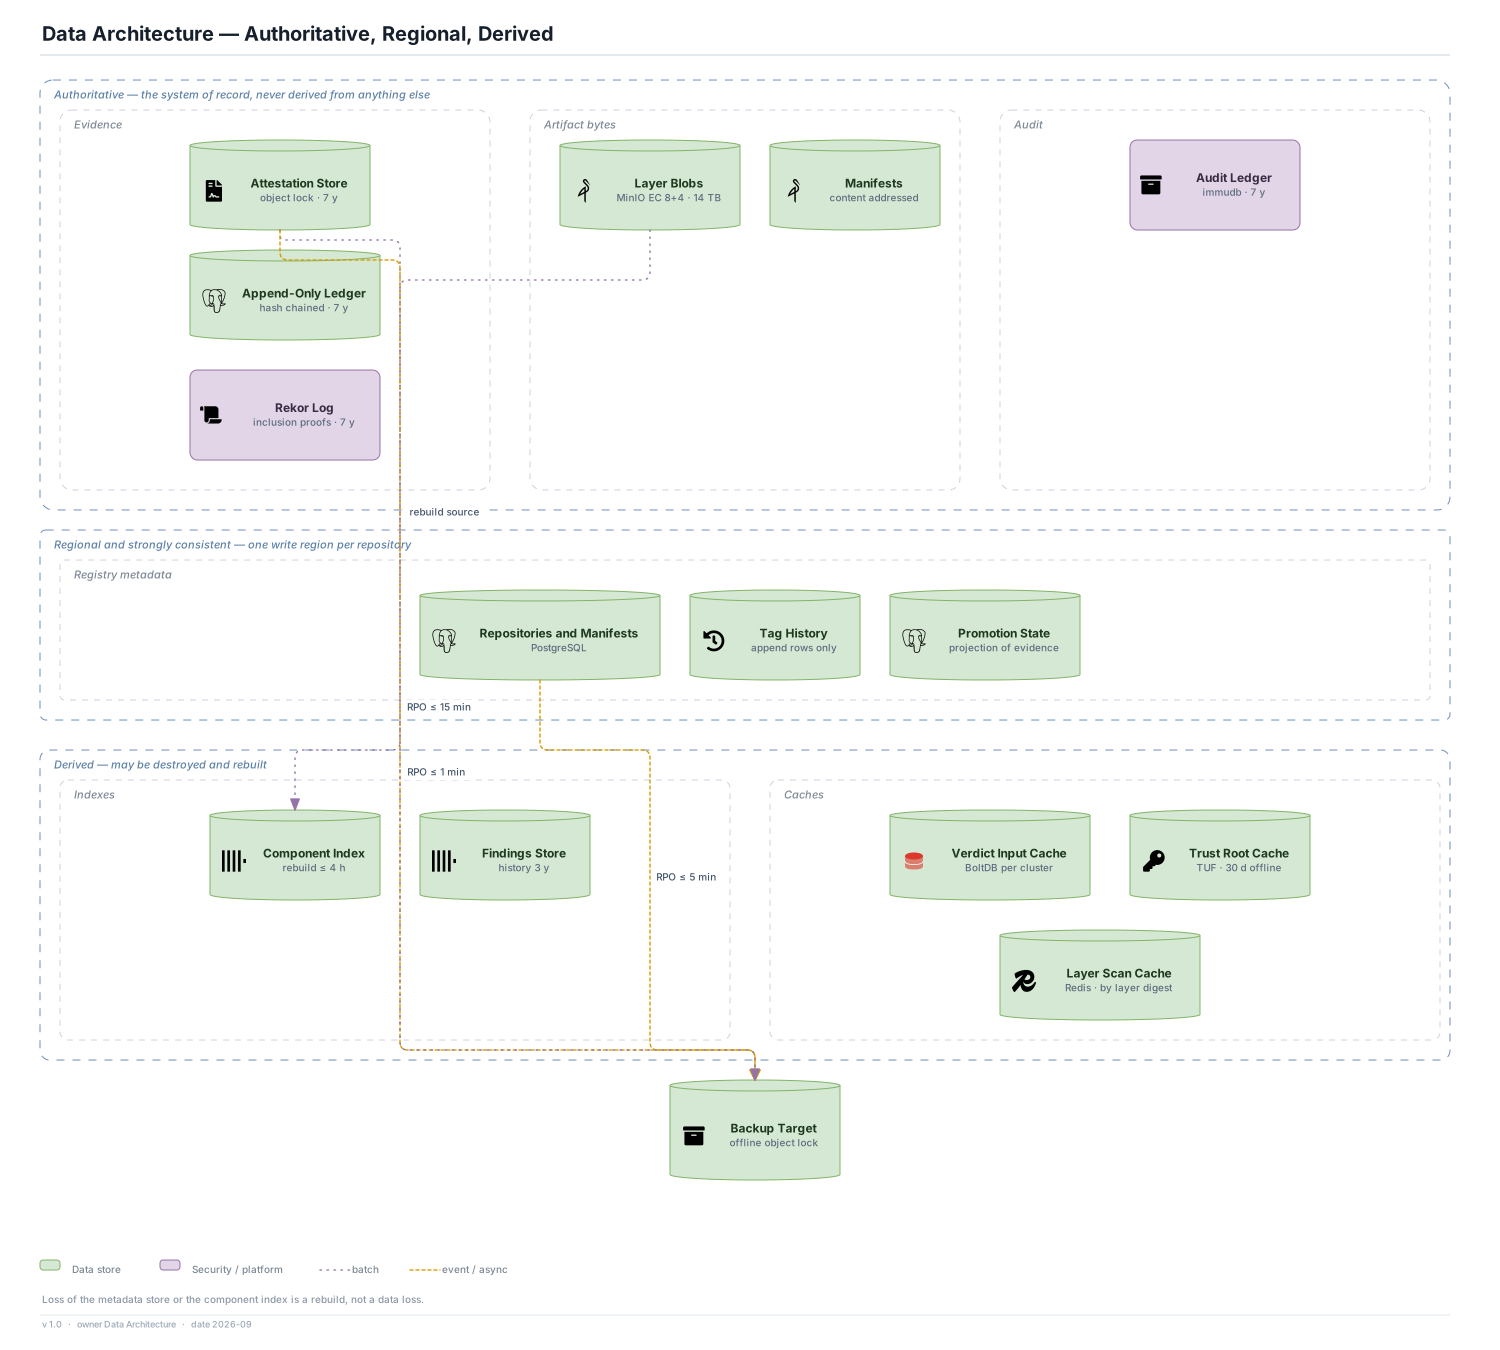
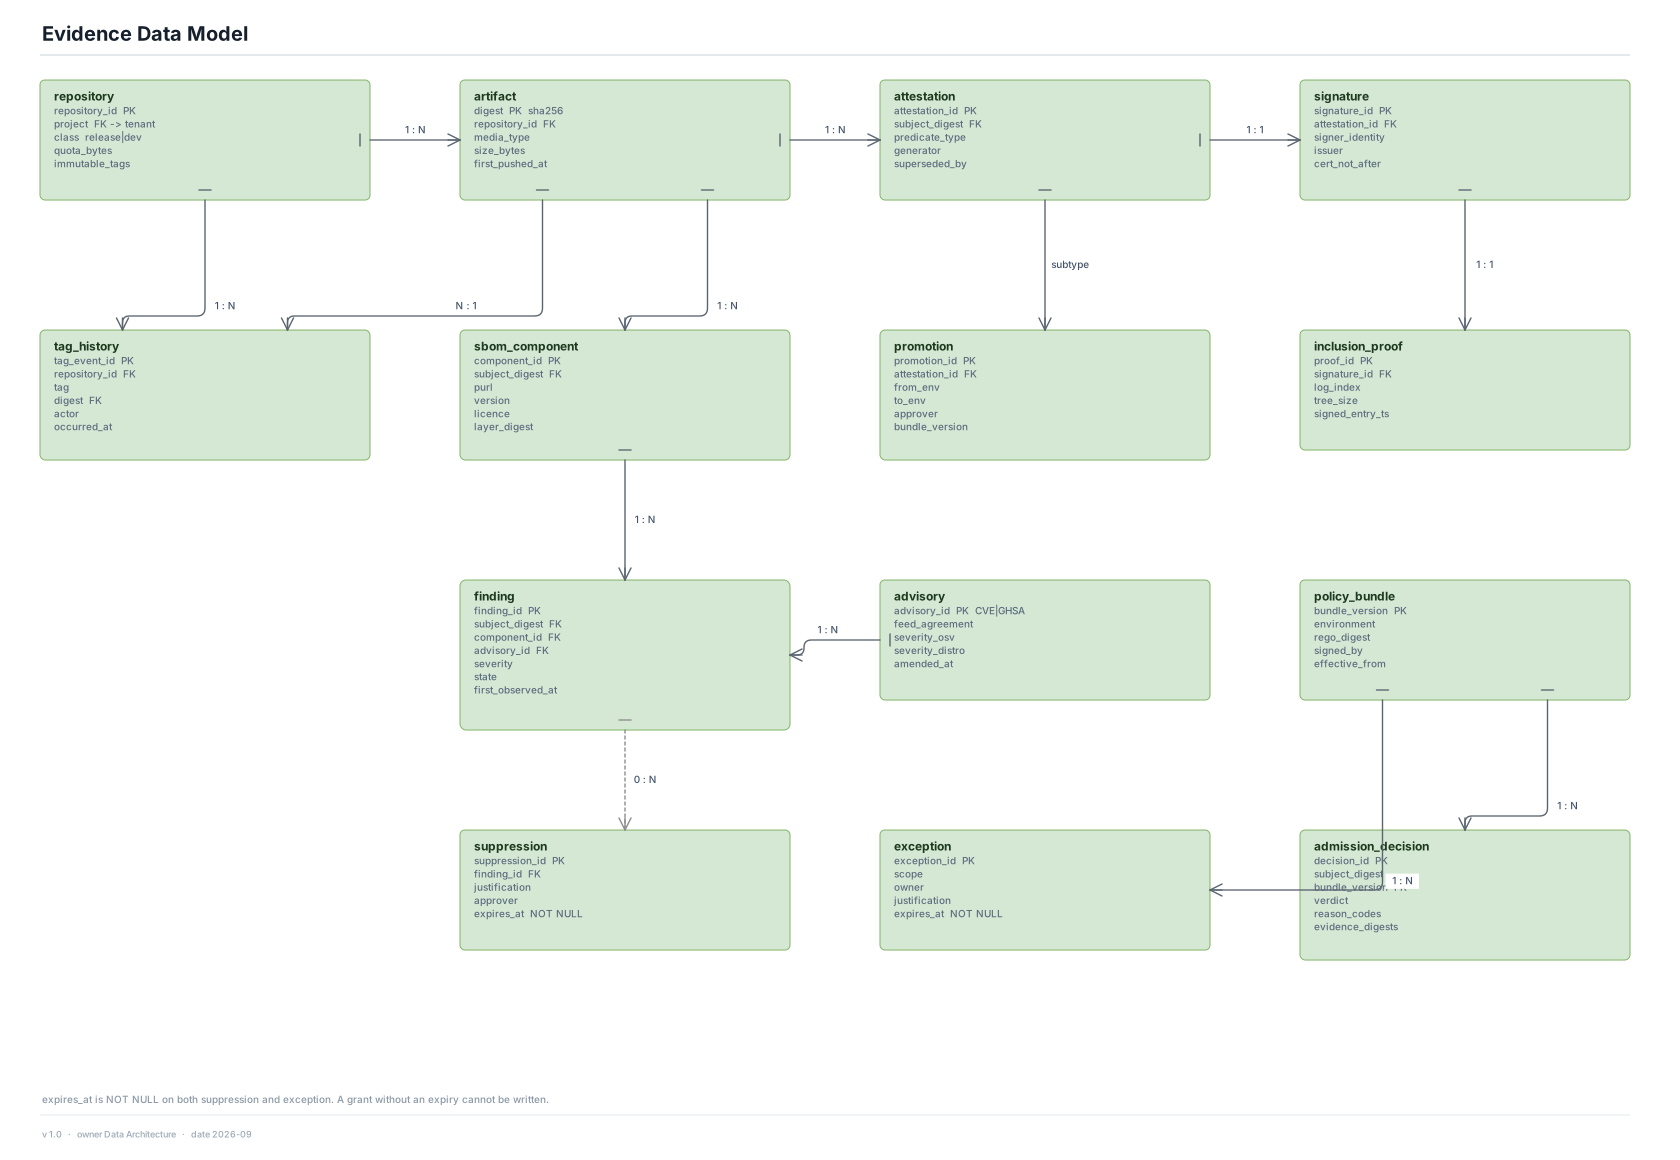
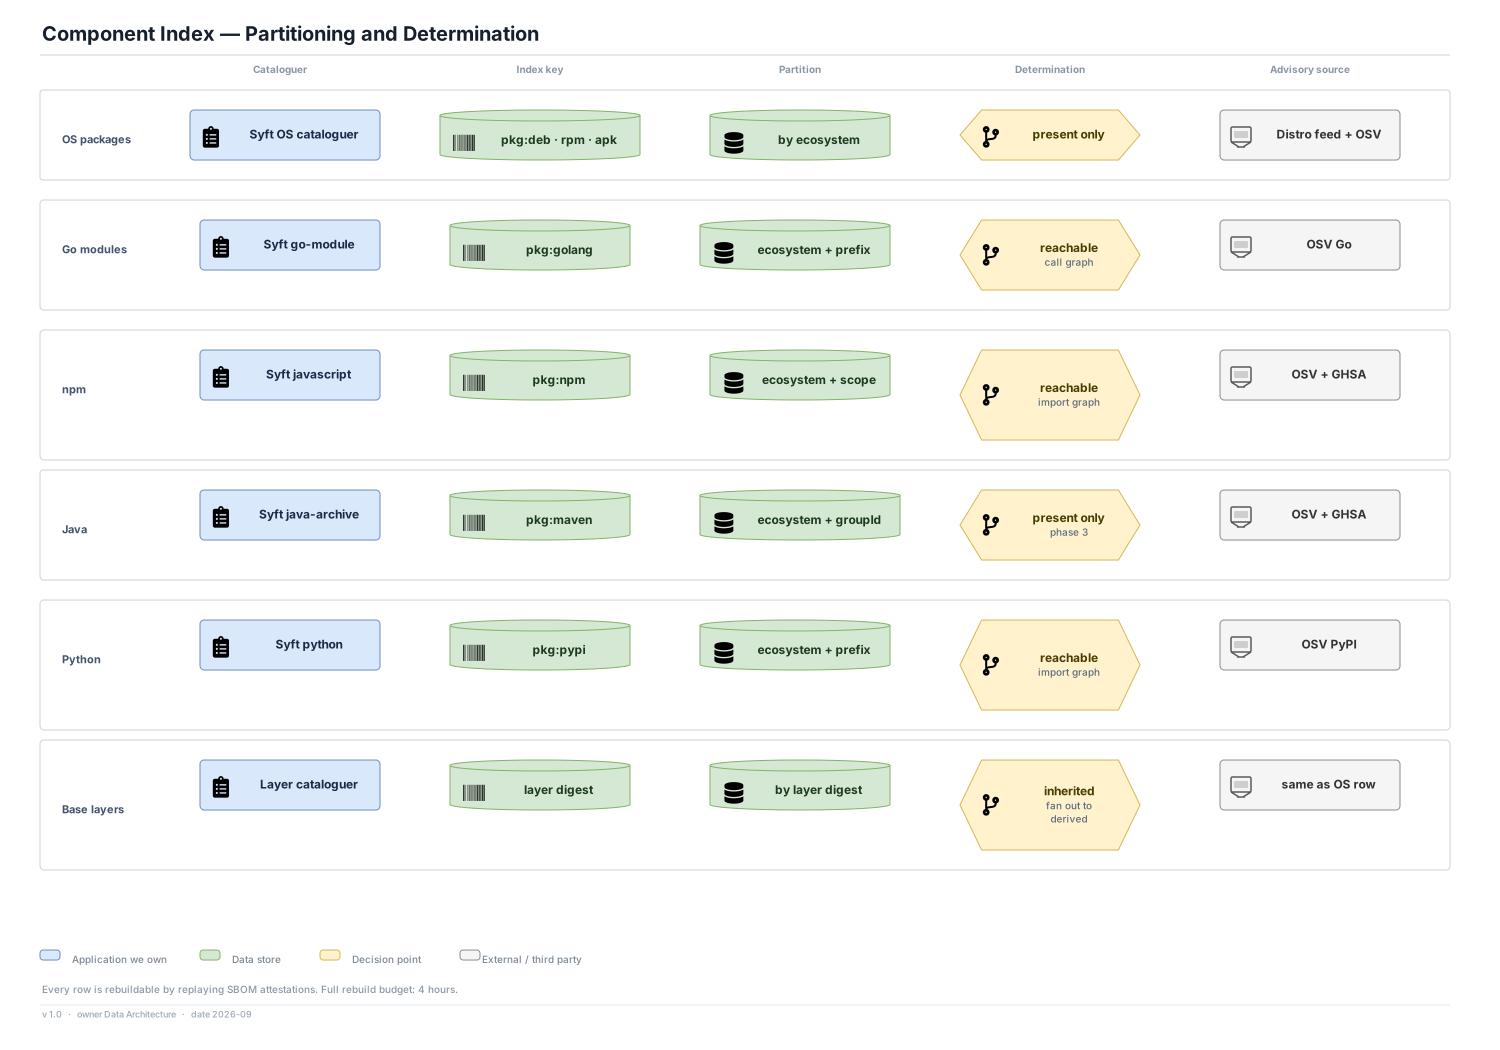
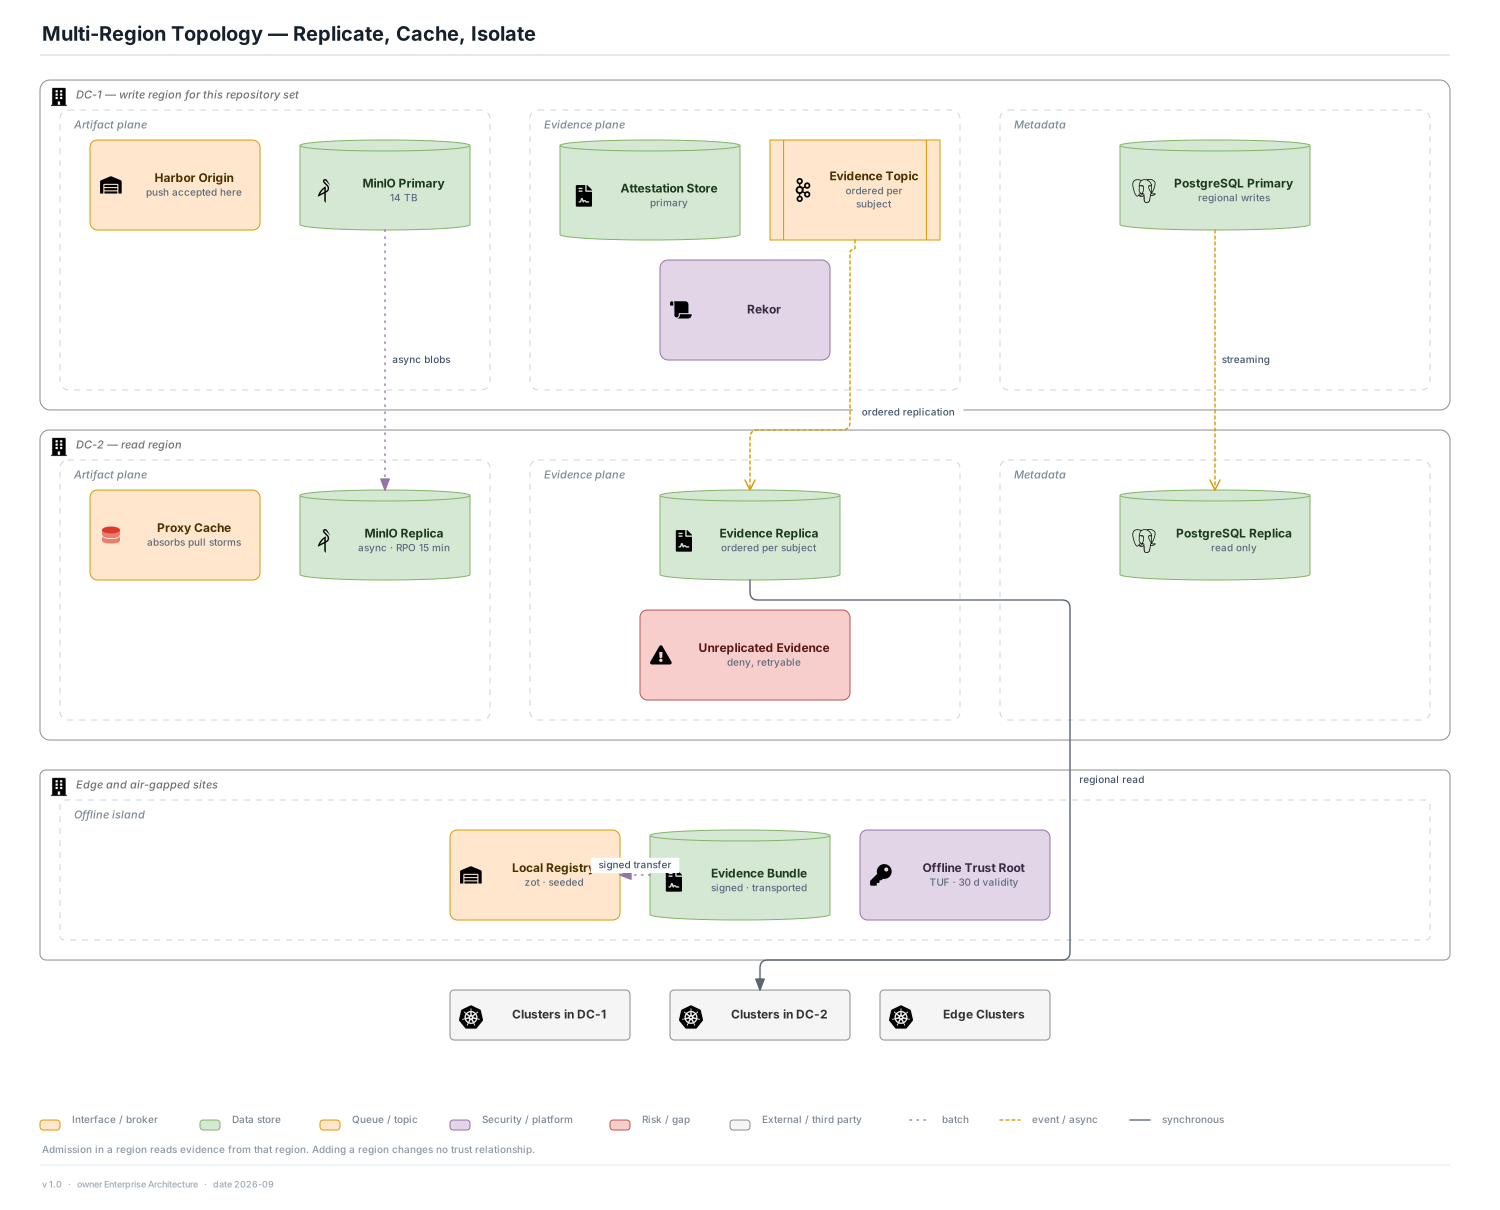
Which store is the system of record, what is derived, what the model looks like, and how it moves across regions.
11 repository repository_id PK project FK -> tenant class release|dev quota_bytes immutable_tags artifact digest PK sha256 repository_id FK media_type size_bytes first_pushed_at attestation attestation_id PK subject_digest FK predicate_type generator superseded_by signature signature_id PK attestation_id FK signer_identity issuer cert_not_after tag_history tag_event_id PK repository_id FK tag digest FK actor occurred_at sbom_component component_id PK subject_digest FK purl version licence layer_digest promotion promotion_id PK attestation_id FK from_env to_env approver bundle_version inclusion_proof proof_id PK signature_id FK log_index tree_size signed_entry_ts finding finding_id PK subject_digest FK component_id FK advisory_id FK severity state first_observed_at advisory advisory_id PK CVE|GHSA feed_agreement severity_osv severity_distro amended_at policy_bundle bundle_version PK environment rego_digest signed_by effective_from suppression suppression_id PK finding_id FK justification approver expires_at NOT NULL exception exception_id PK scope owner justification expires_at NOT NULL admission_decision decision_id PK subject_digest bundle_version FK verdict reason_codes evidence_digests 1 : N 1 : N N : 1 1 : N 1 : 1 1 : 1 subtype 1 : N 1 : N 1 : N 0 : N 1 : N 1 : N Evidence Data Model expires_at is NOT NULL on both suppression and exception. A grant without an expiry cannot be written. v 1.0 · owner Data Architecture · date 2026-09 Evidence Data Model The entities a decision reads, and the two columns that cannot be null. HTML page SVG draw.io

4 · Runtime

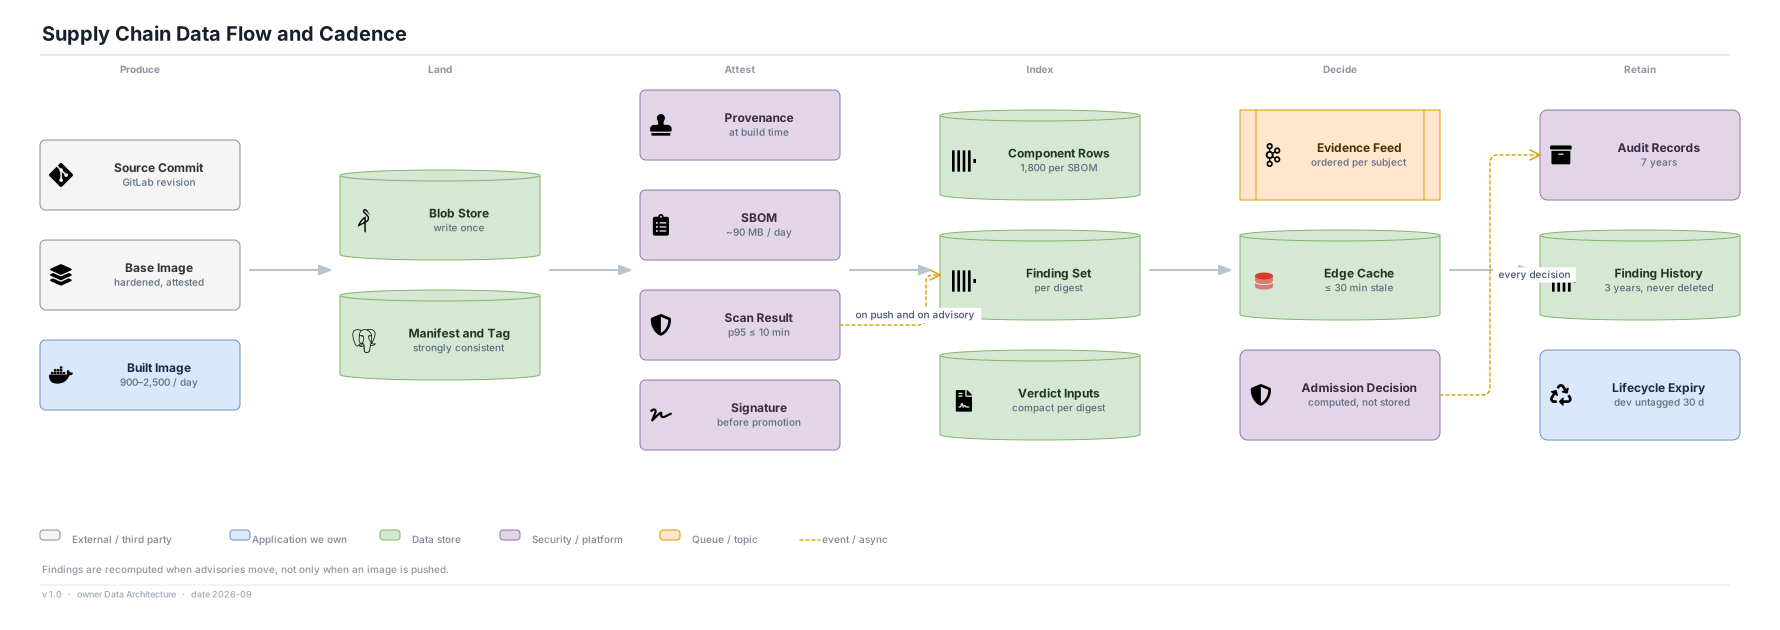
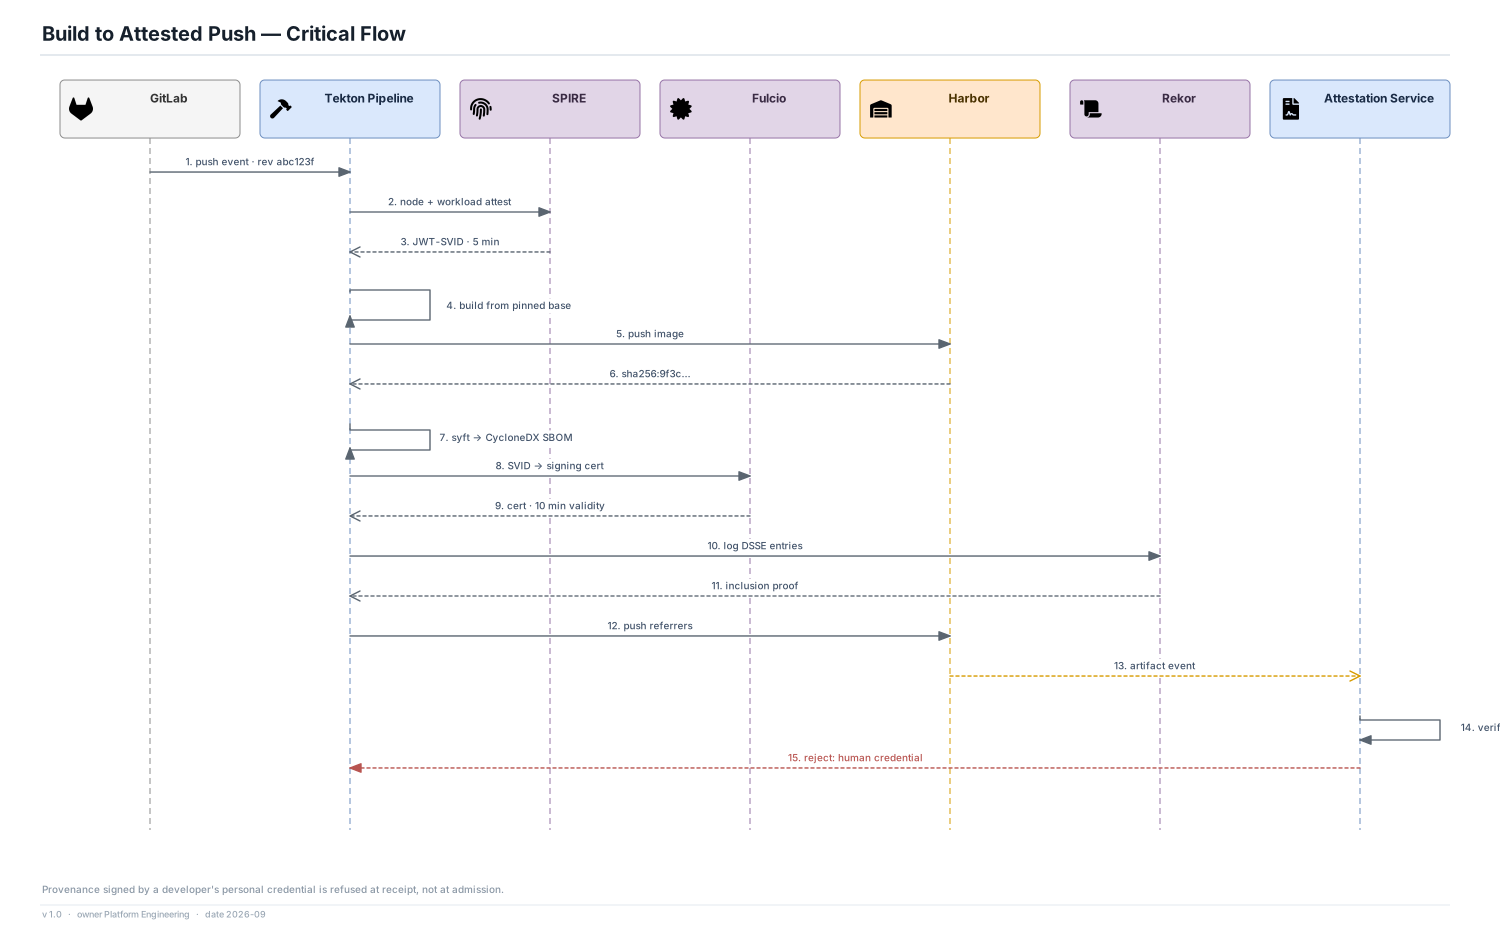
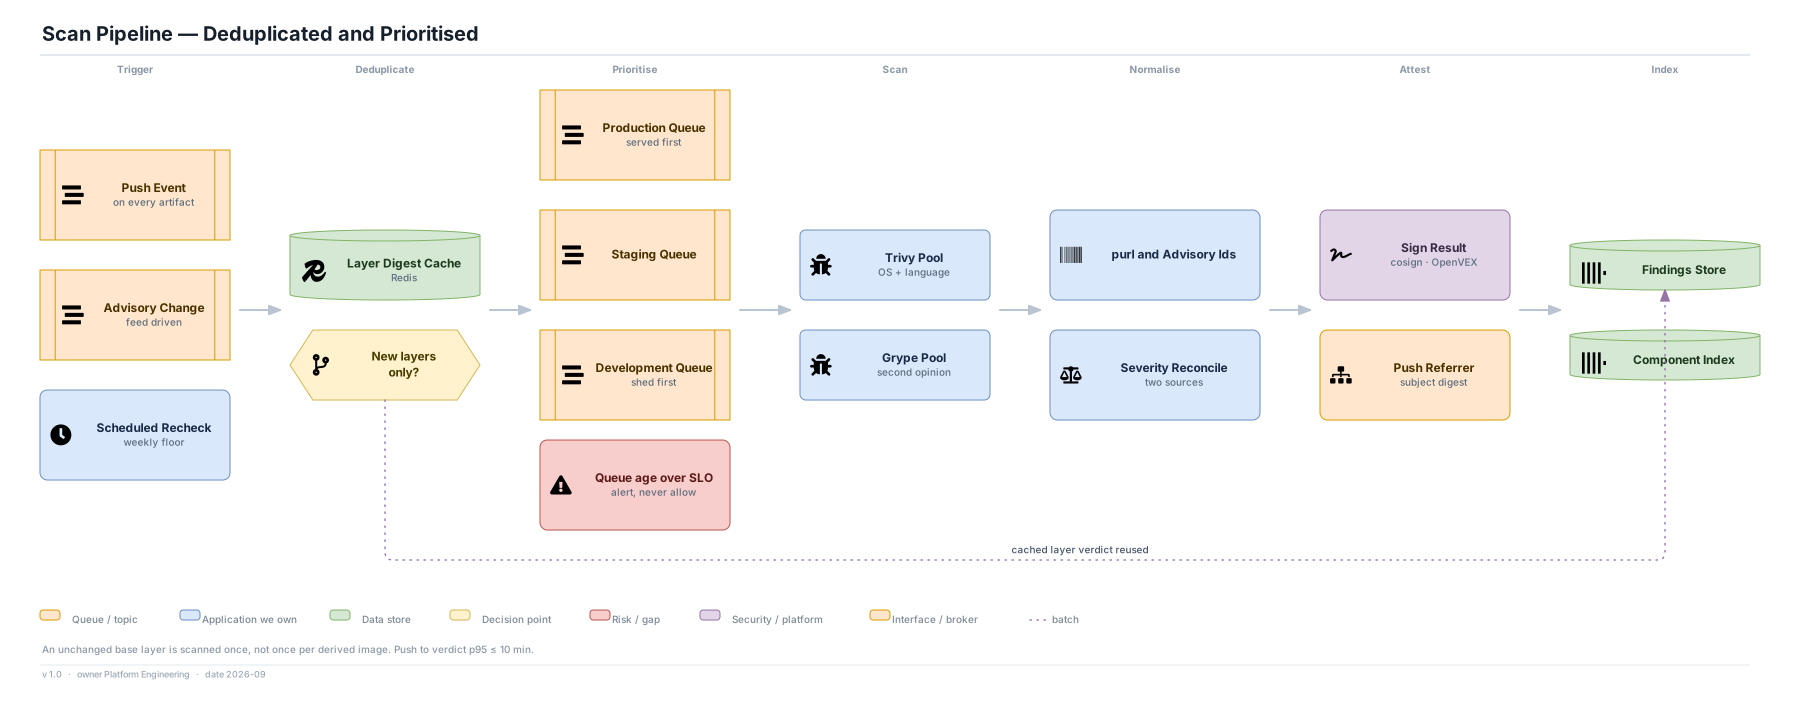
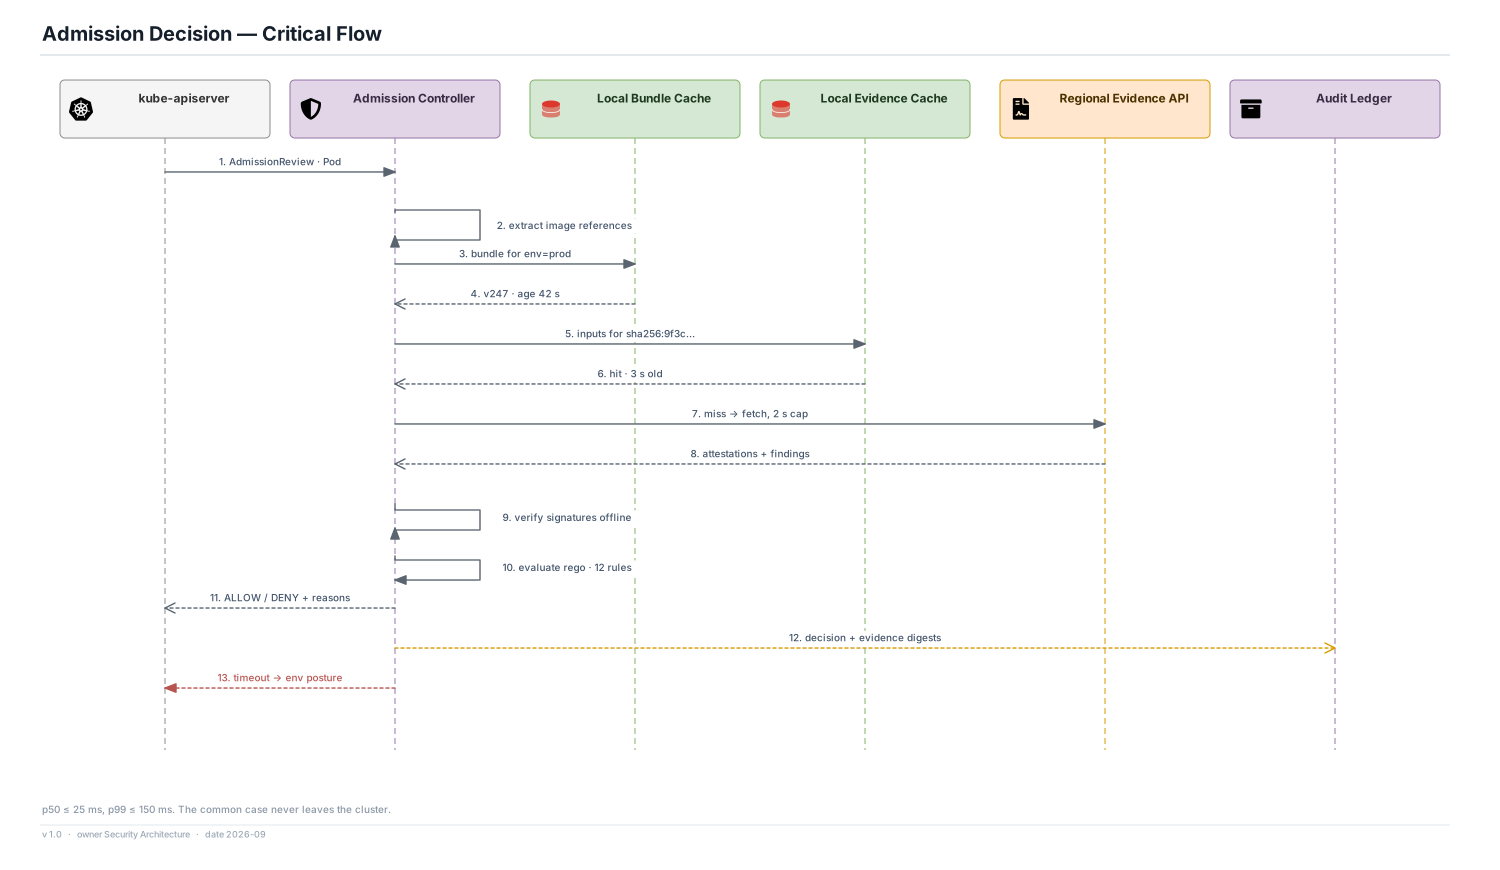
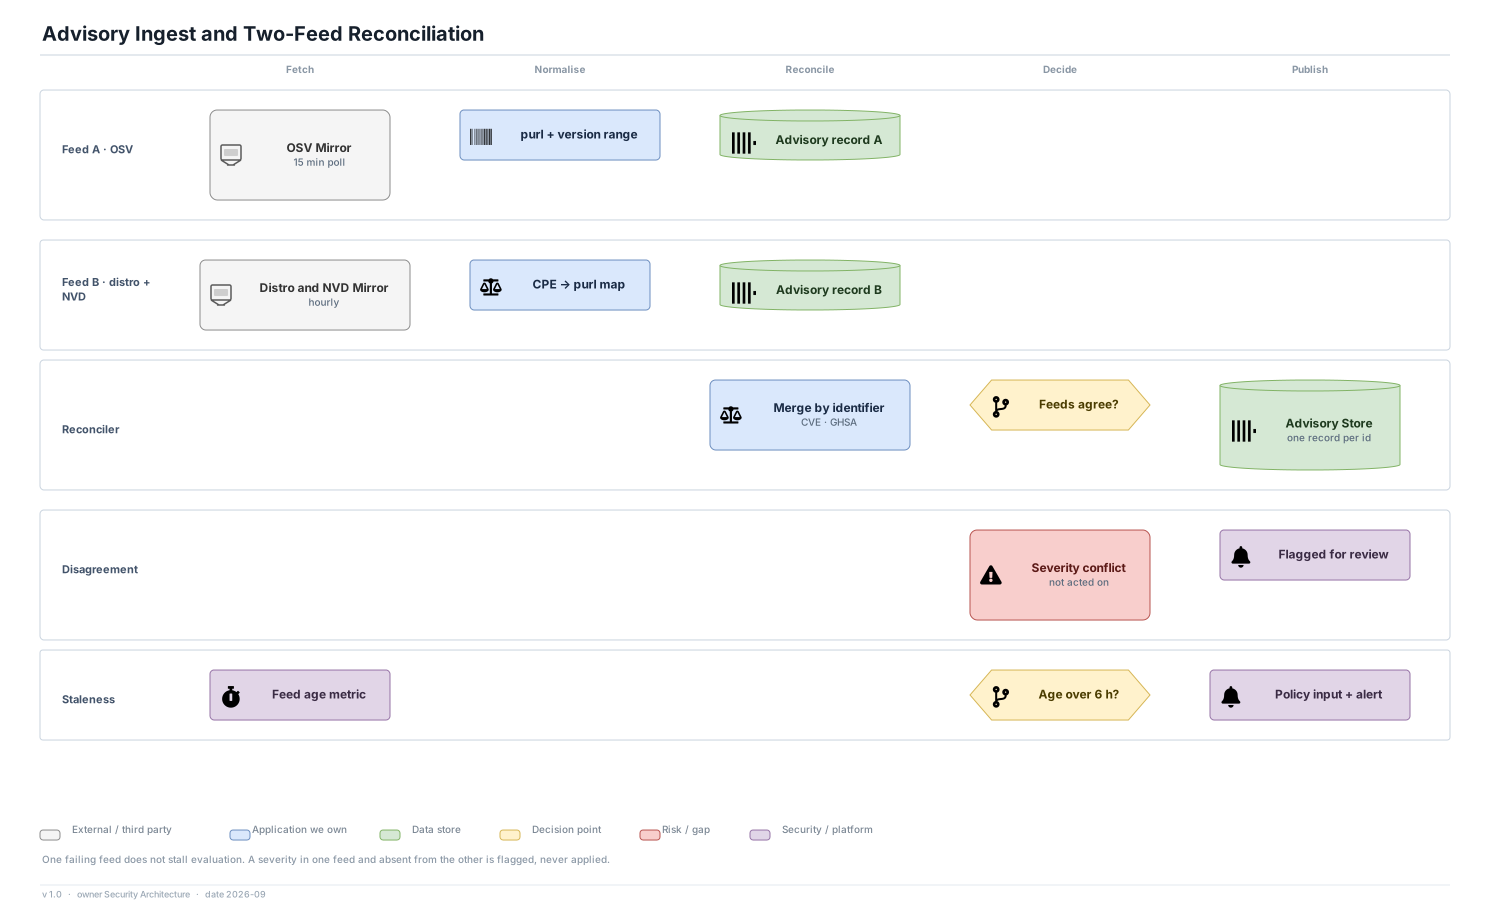
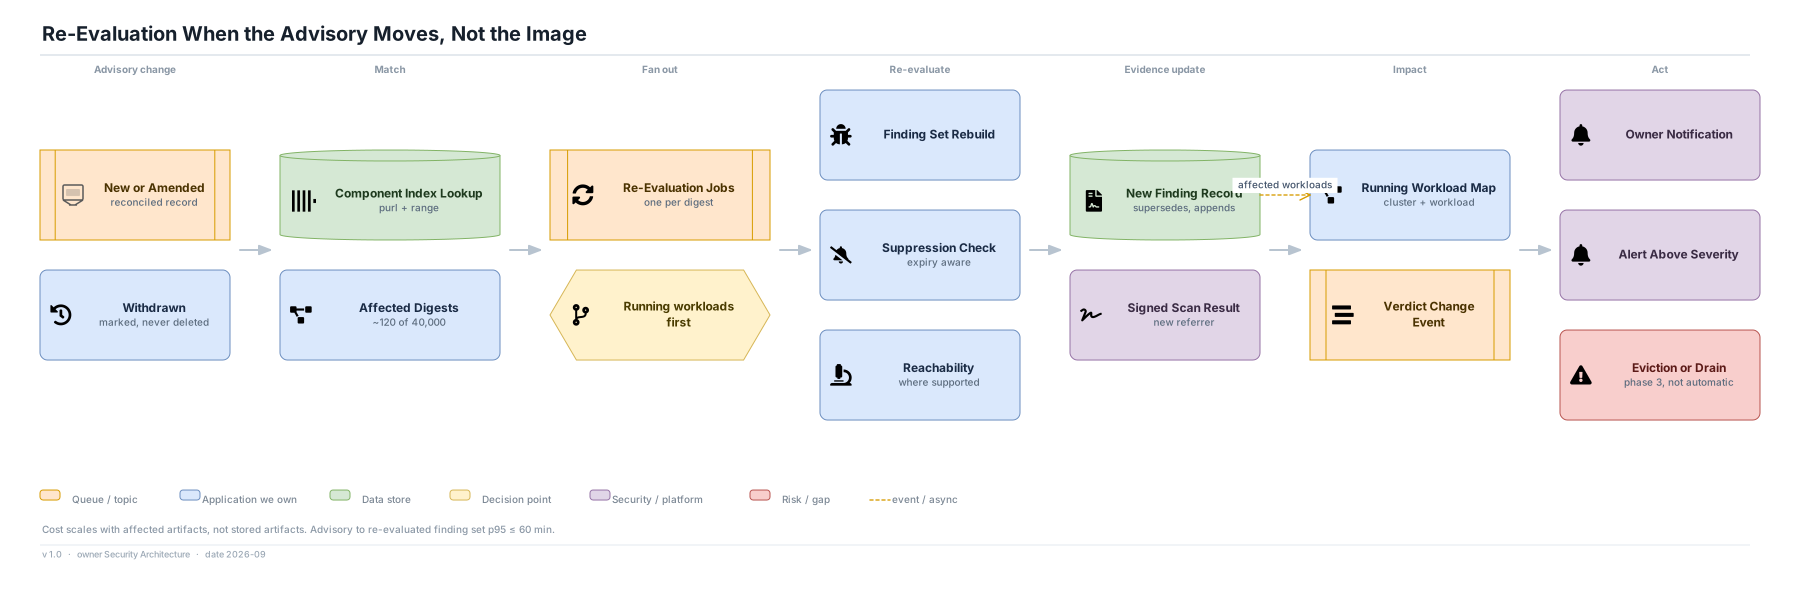
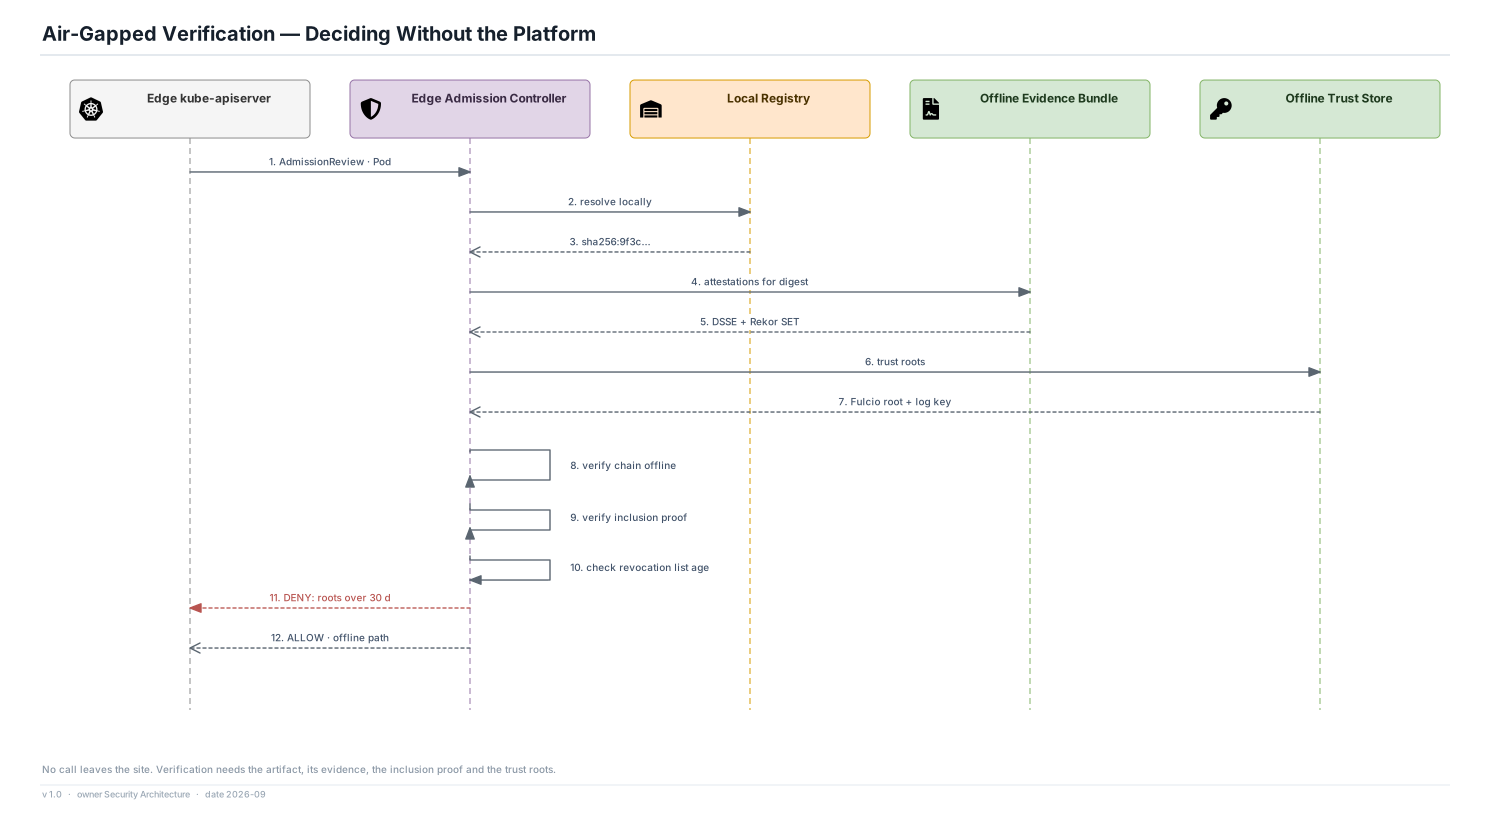
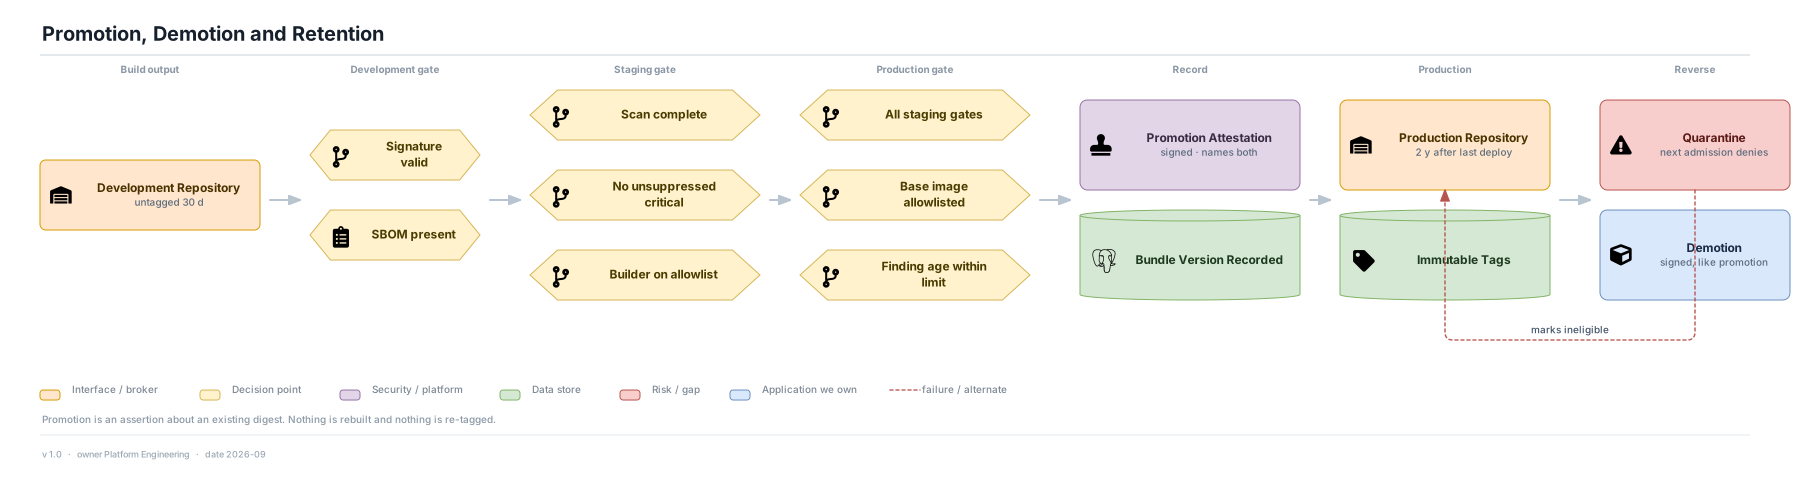
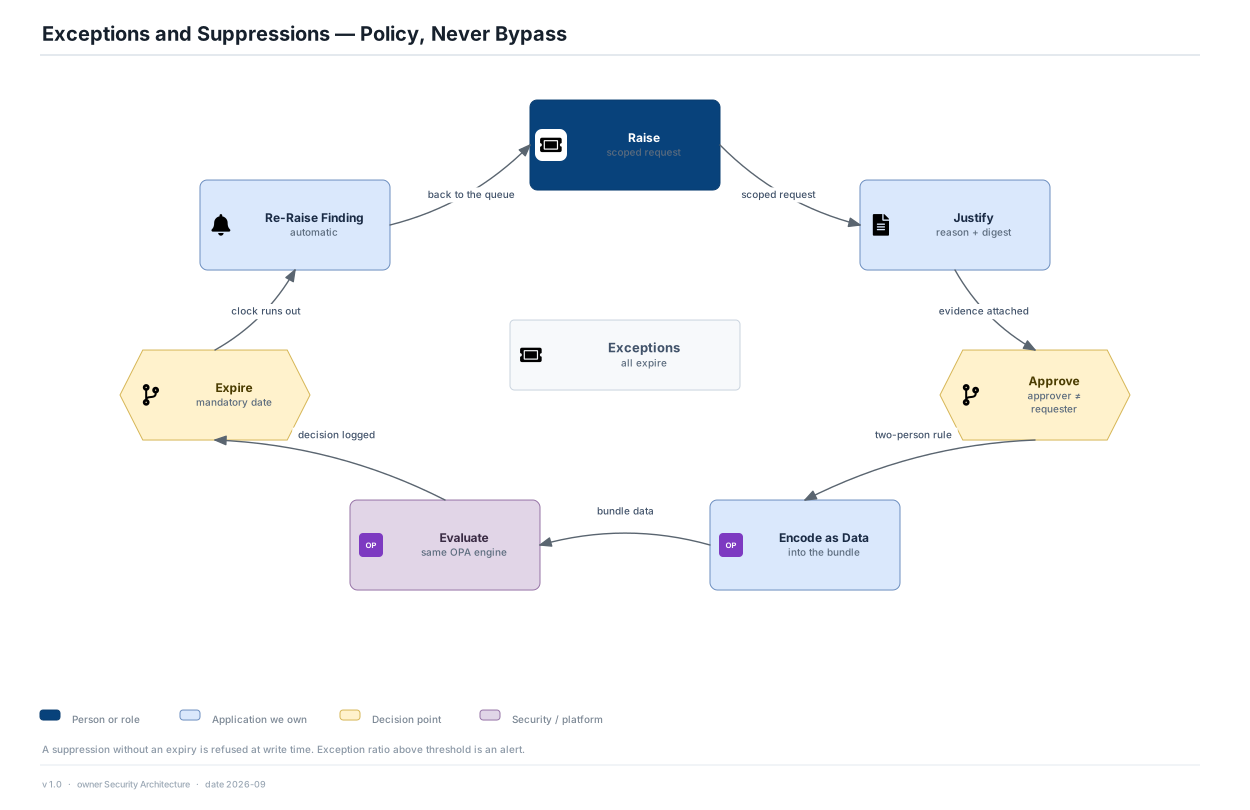
Build and attest, scan, admit, reconcile advisories, re-evaluate, verify offline, promote, and grant an exception that expires.

5 · Operations

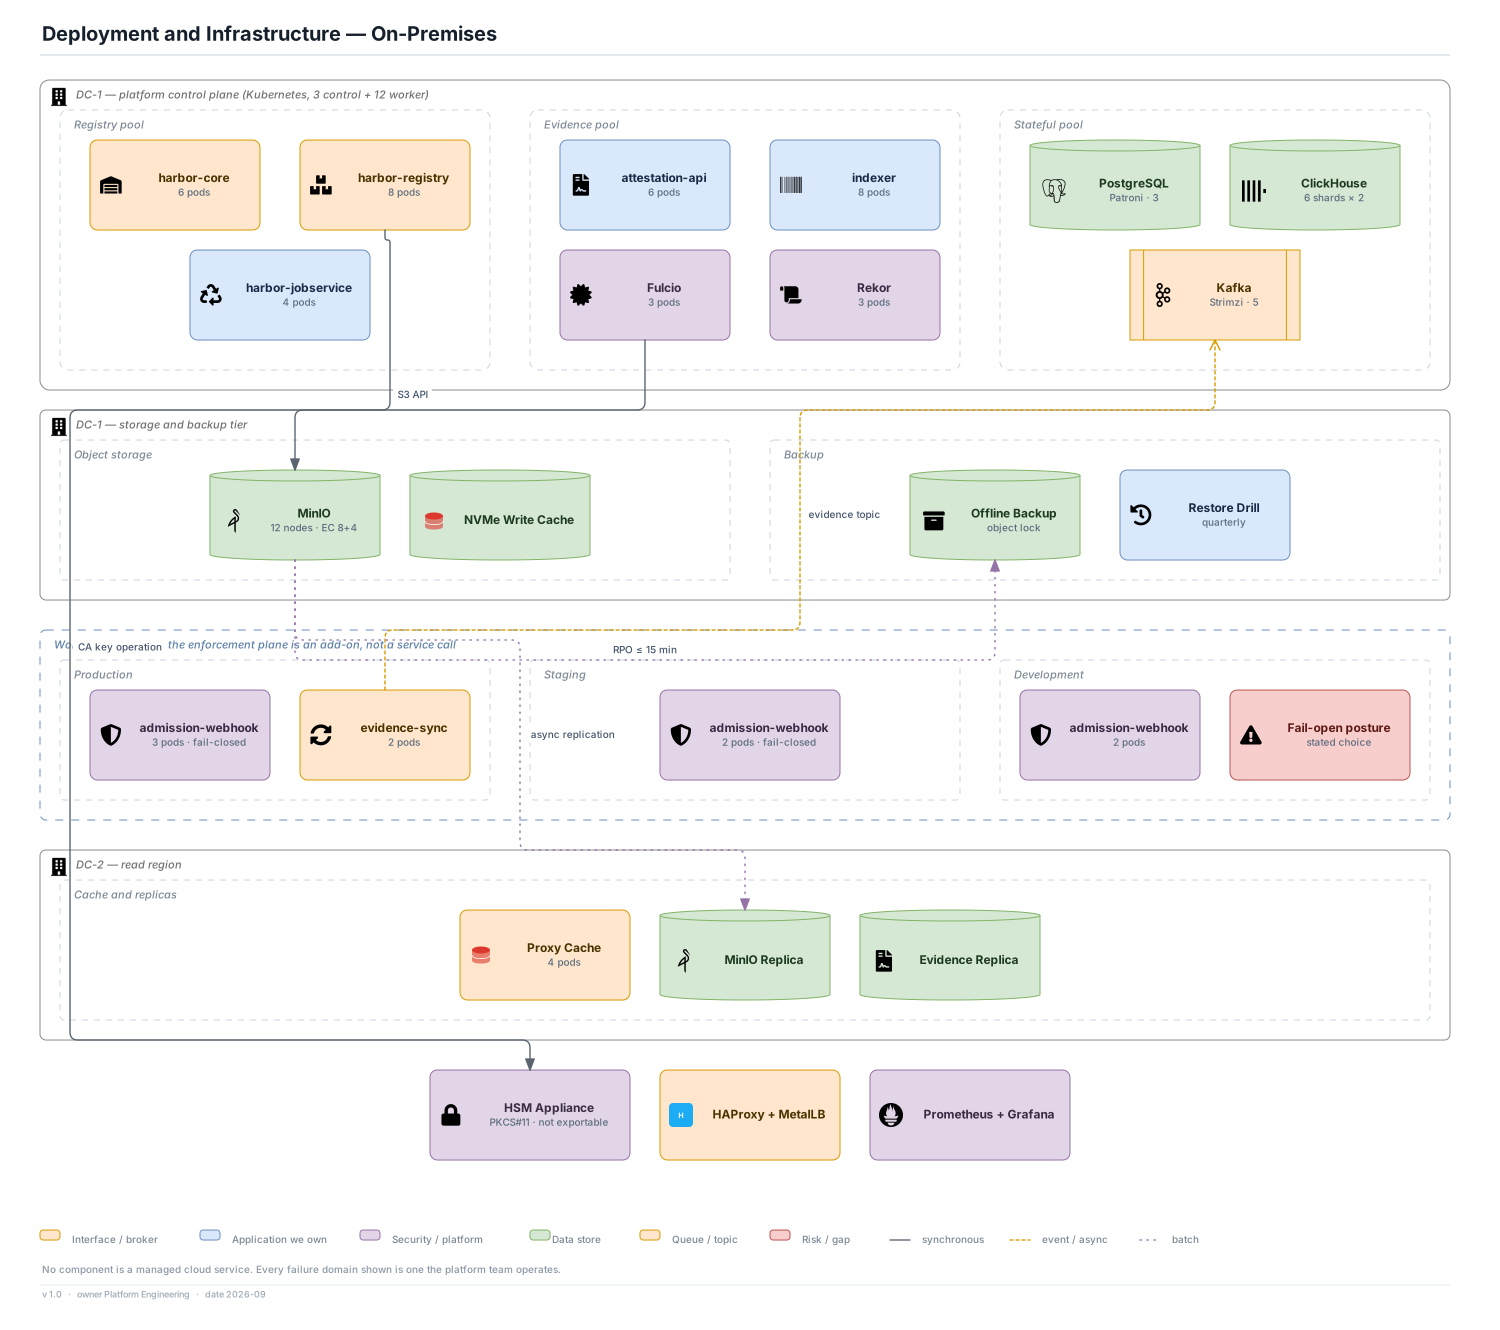
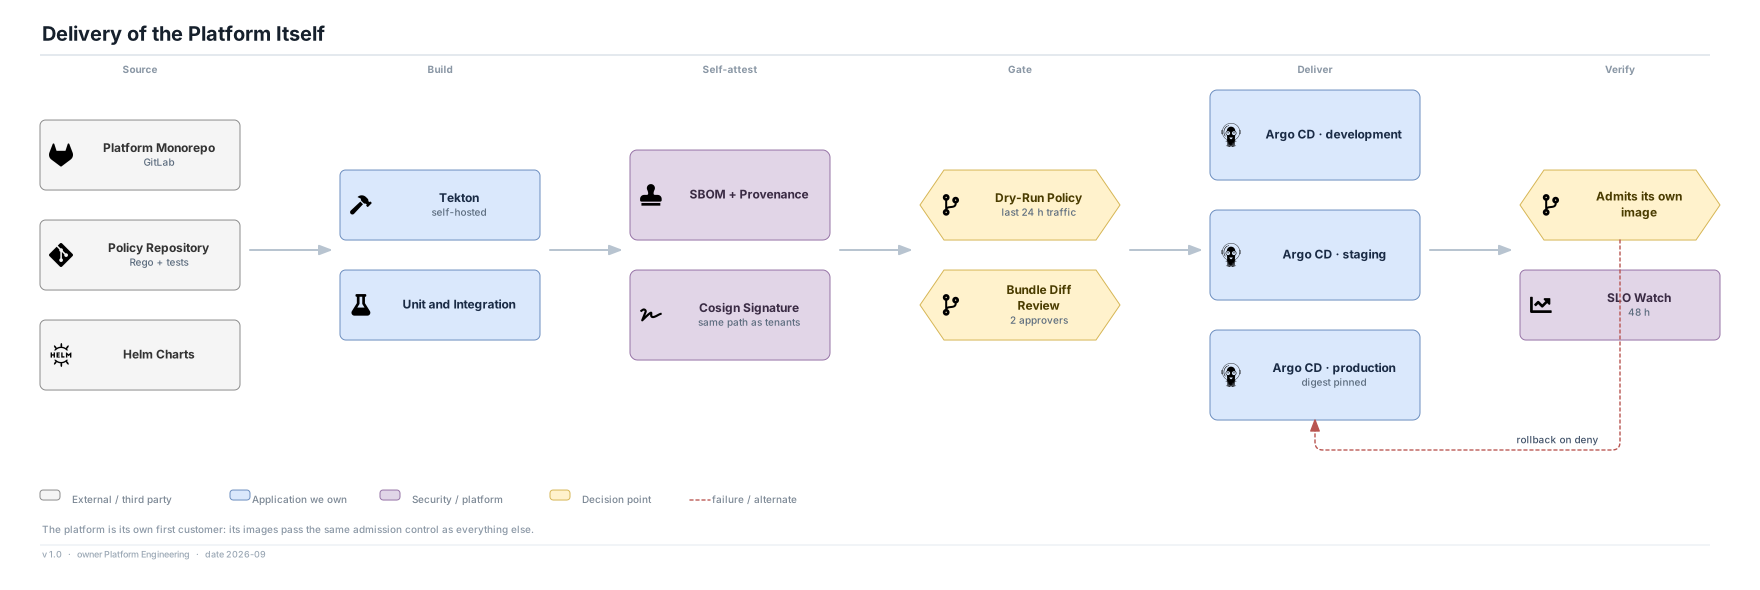
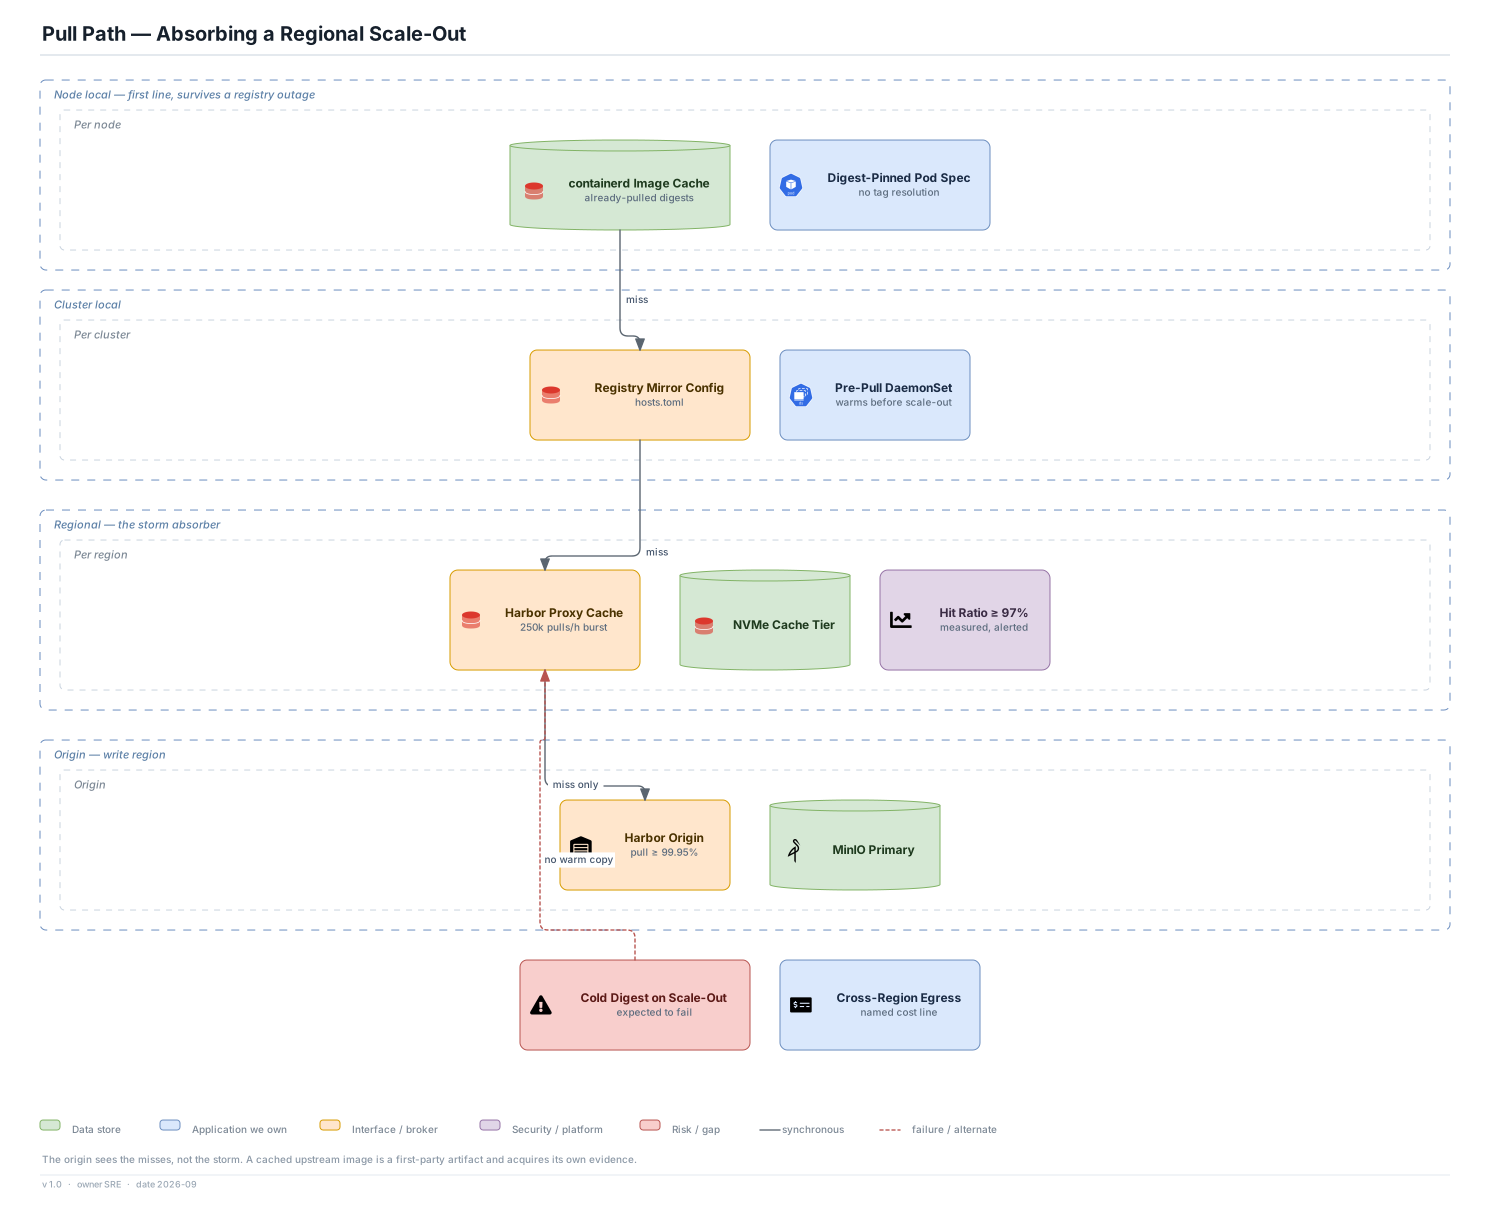
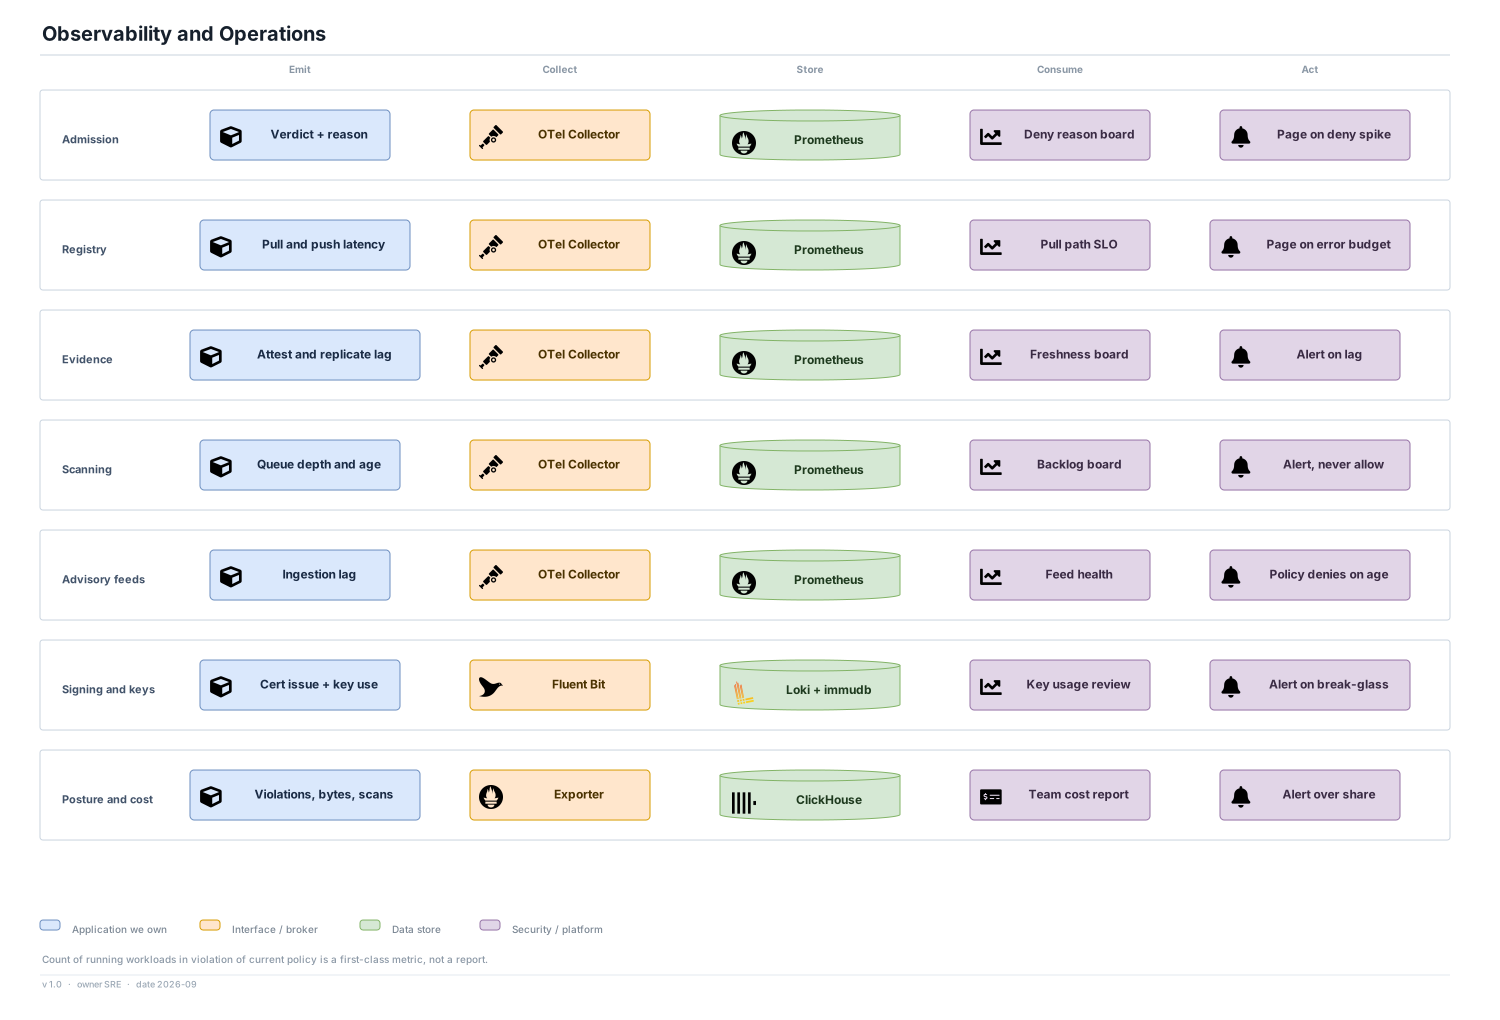
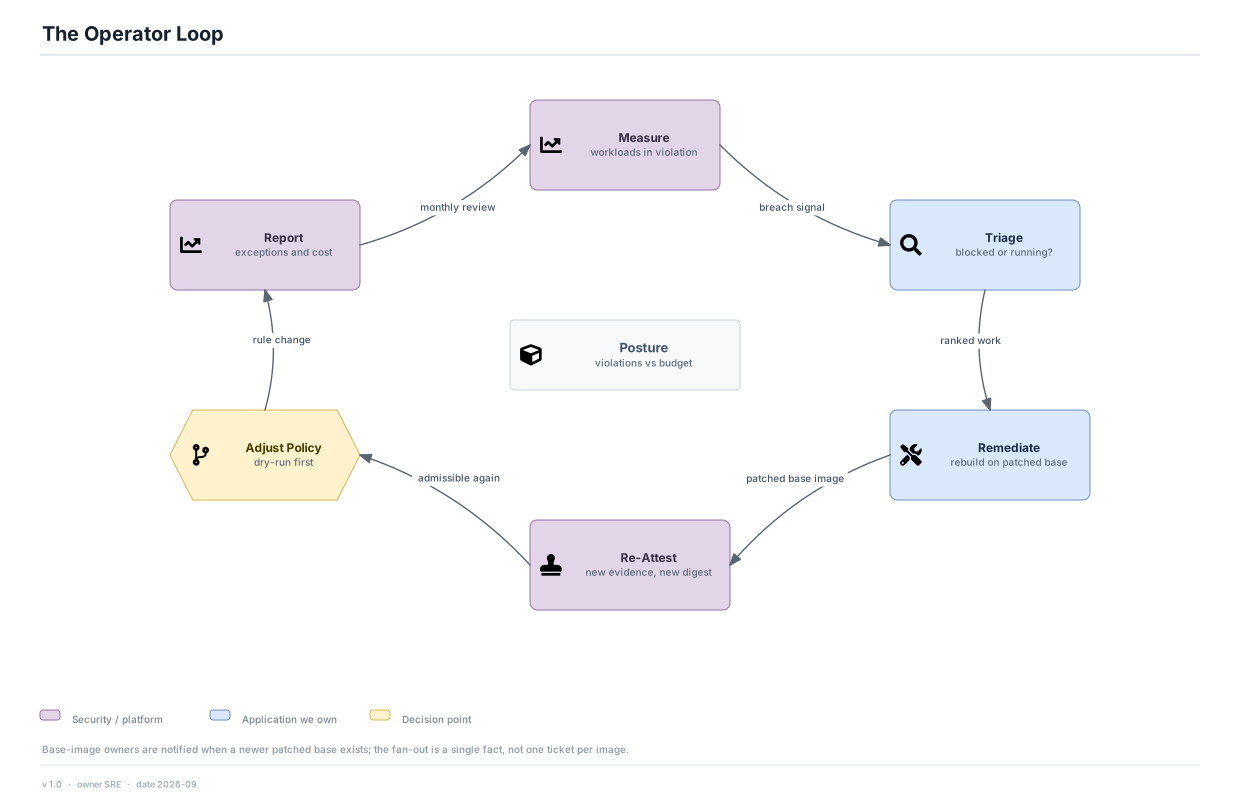
Where it runs, how it ships itself, how a pull storm is absorbed, what is watched, and the operator's loop.

6 · Assurance

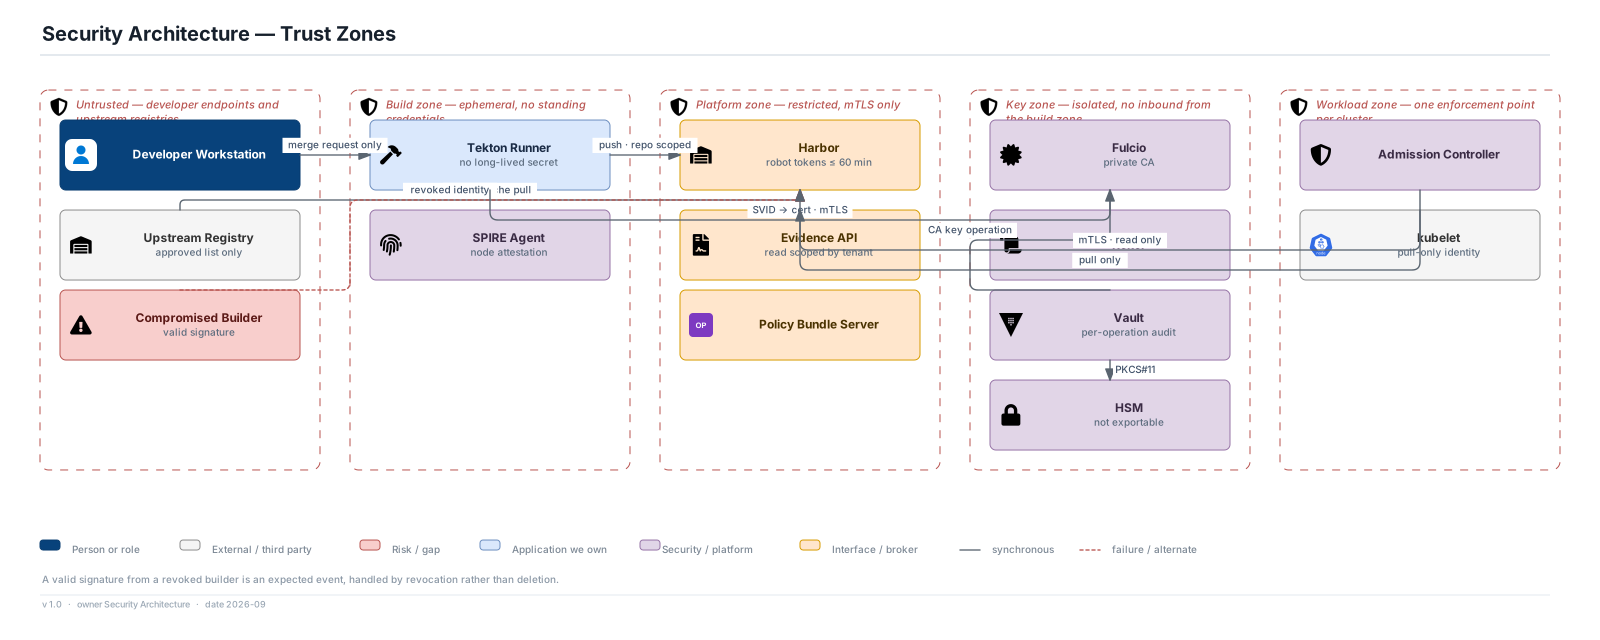
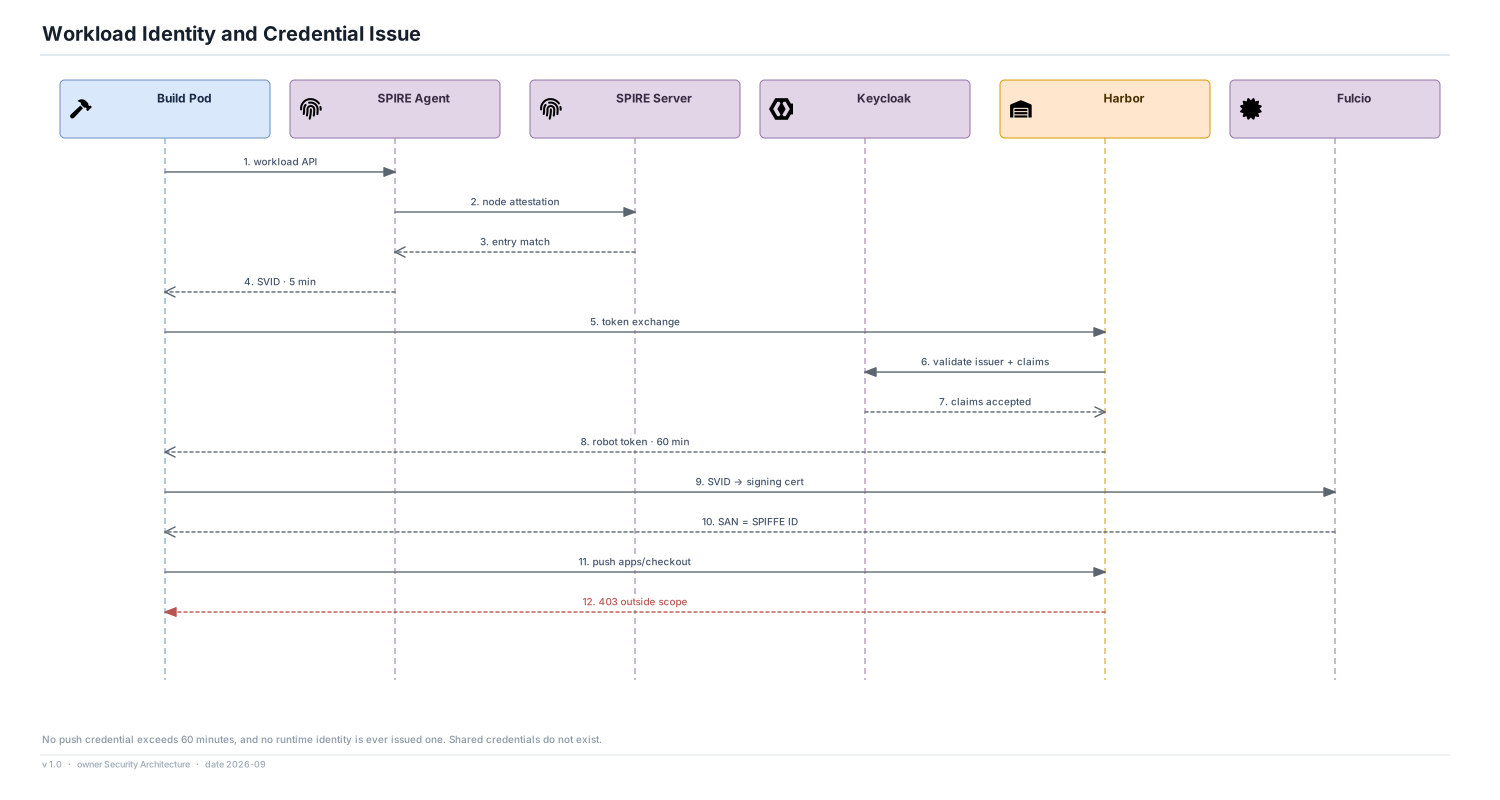
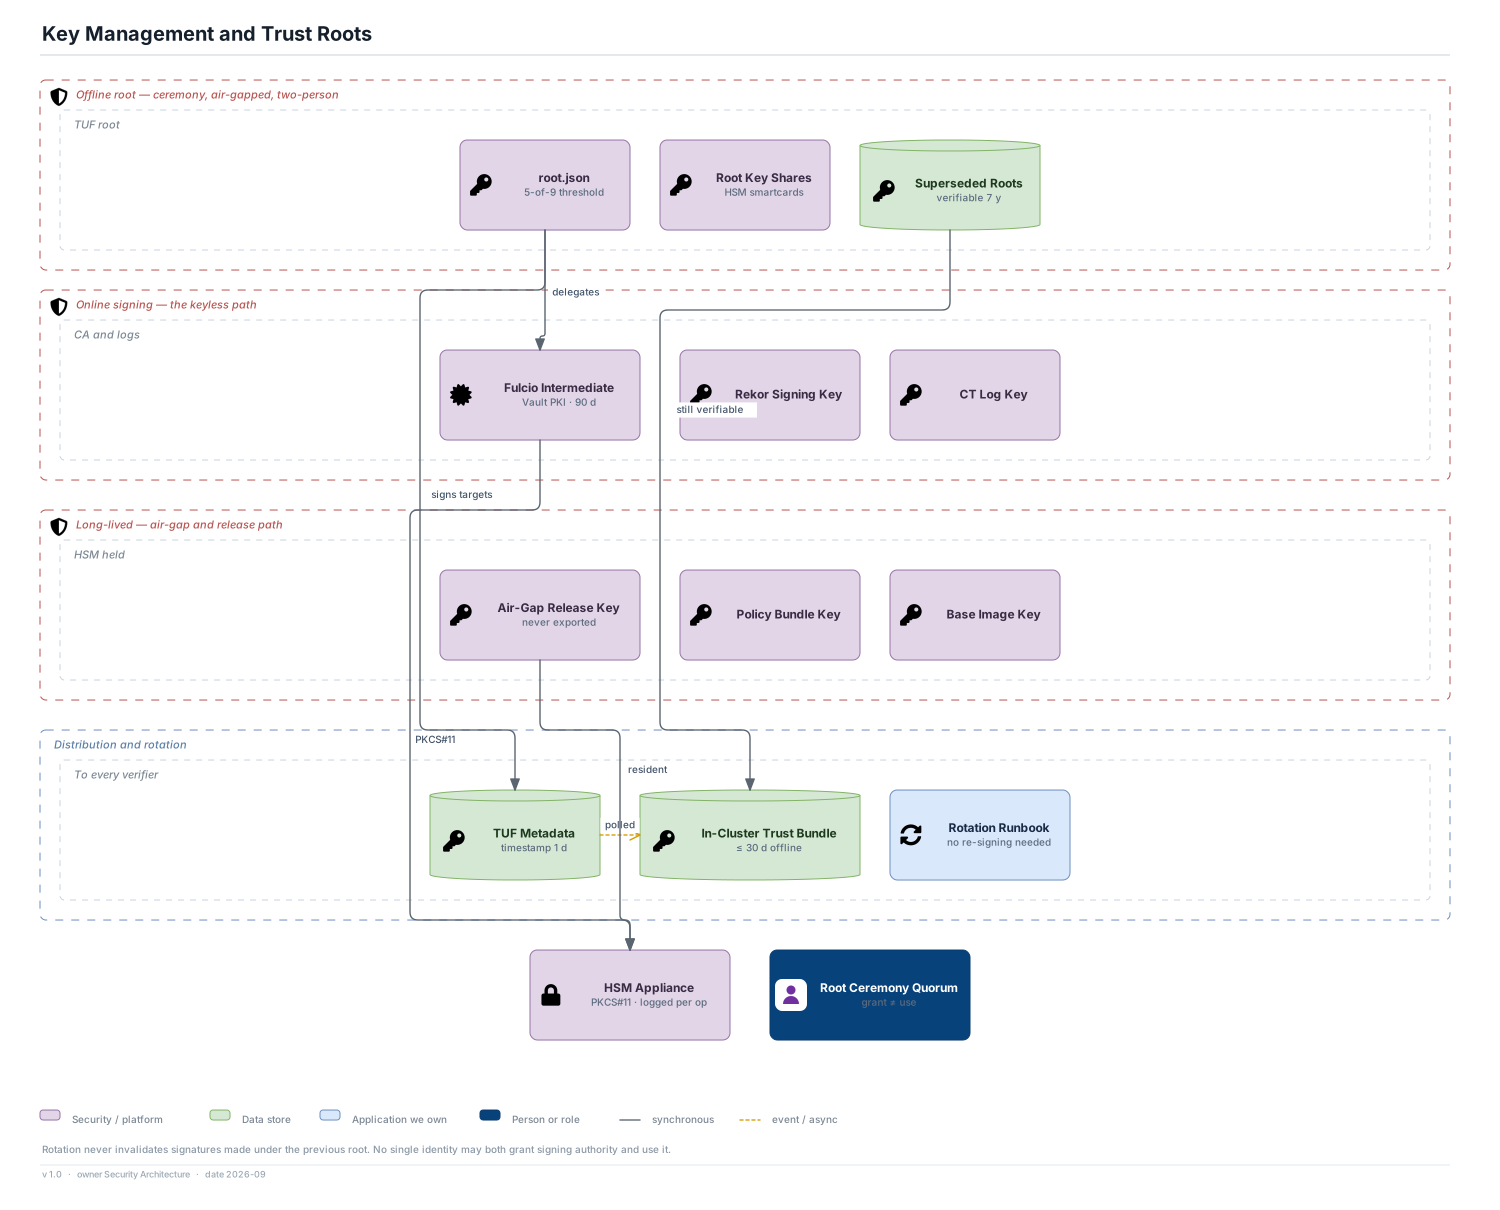
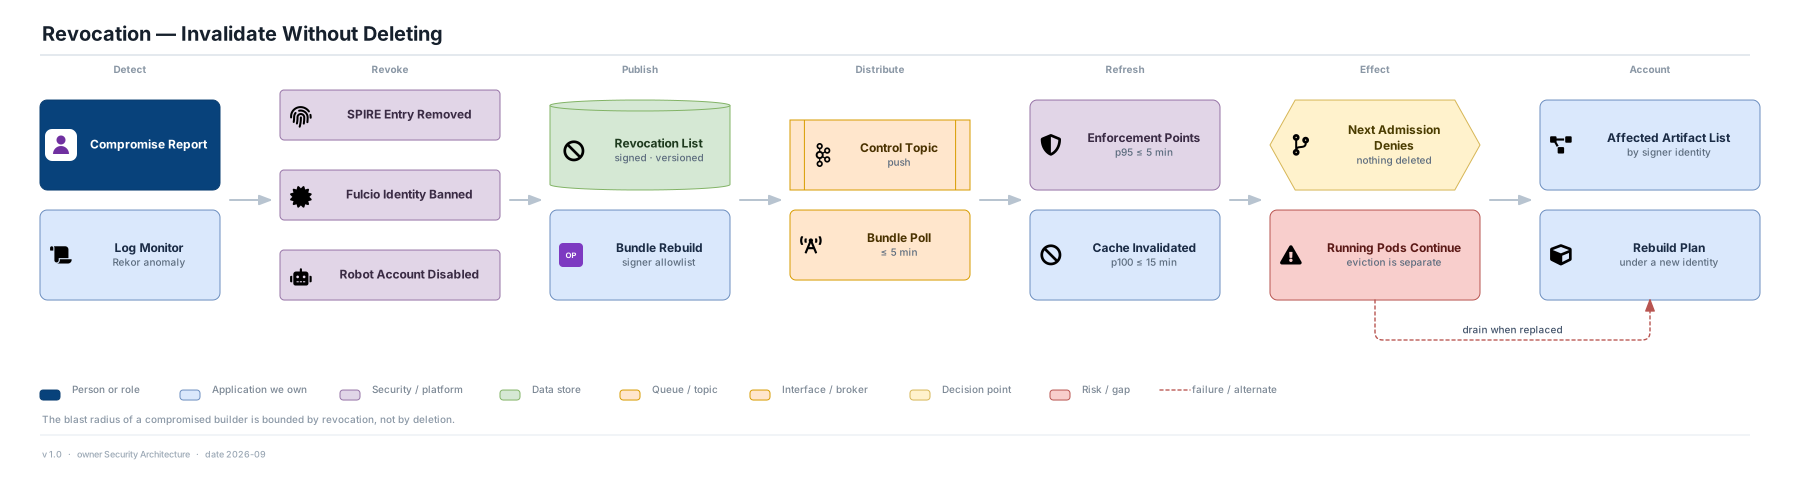
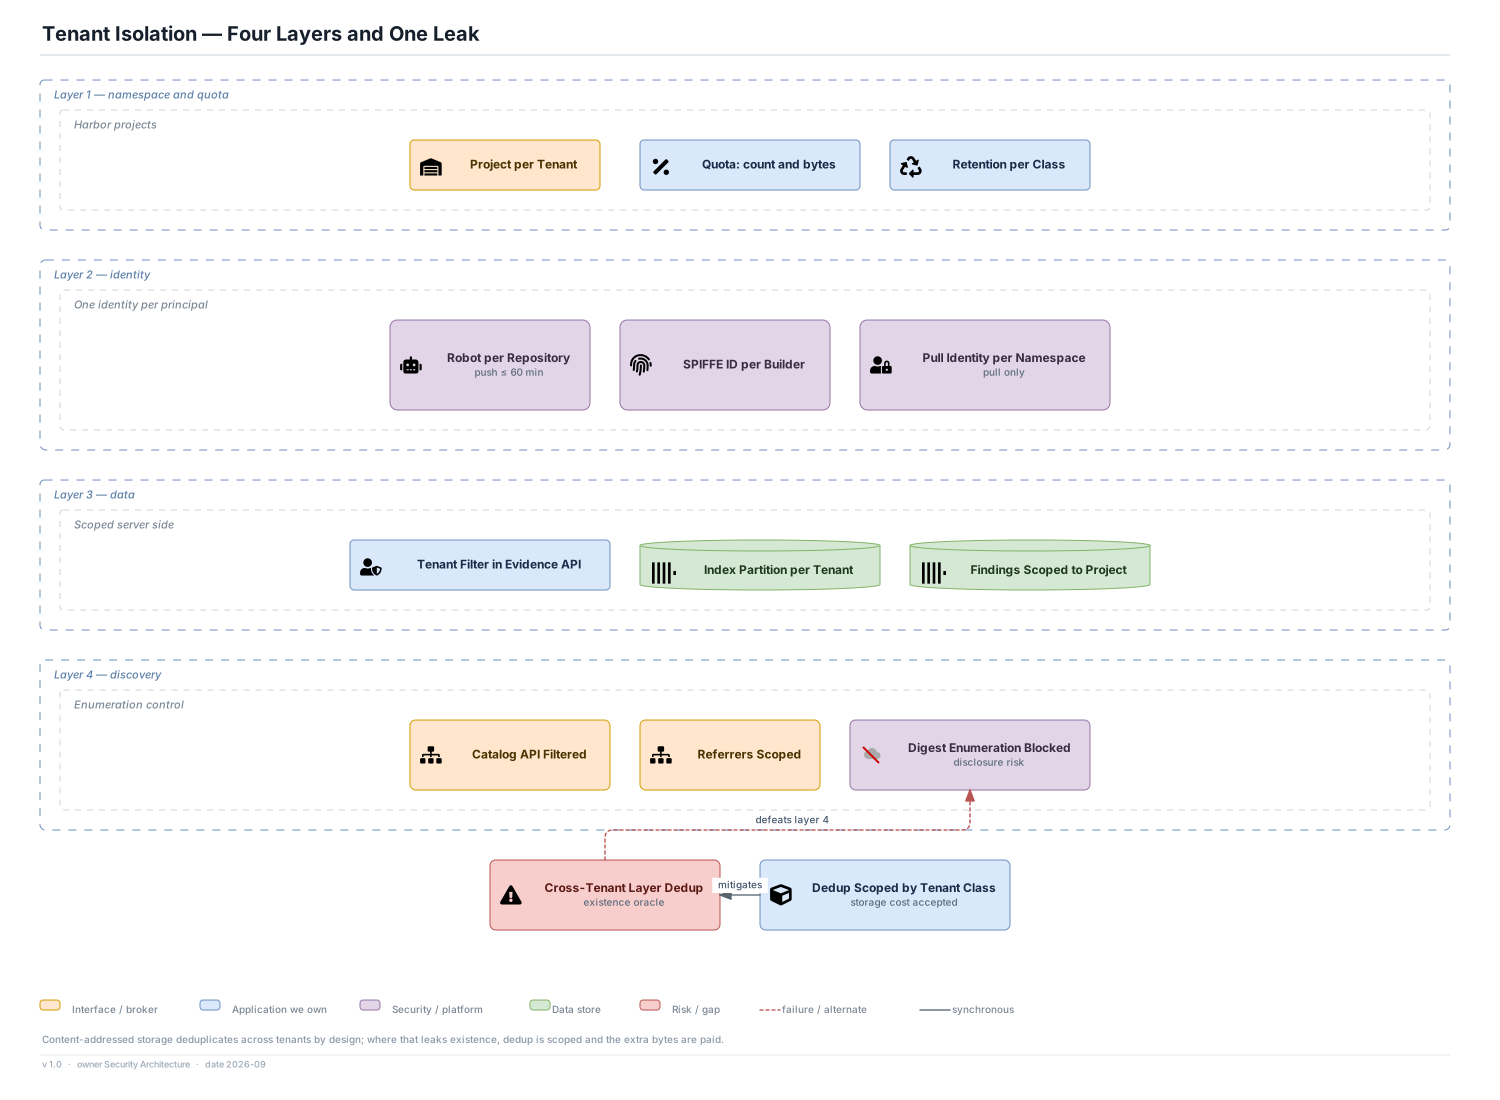
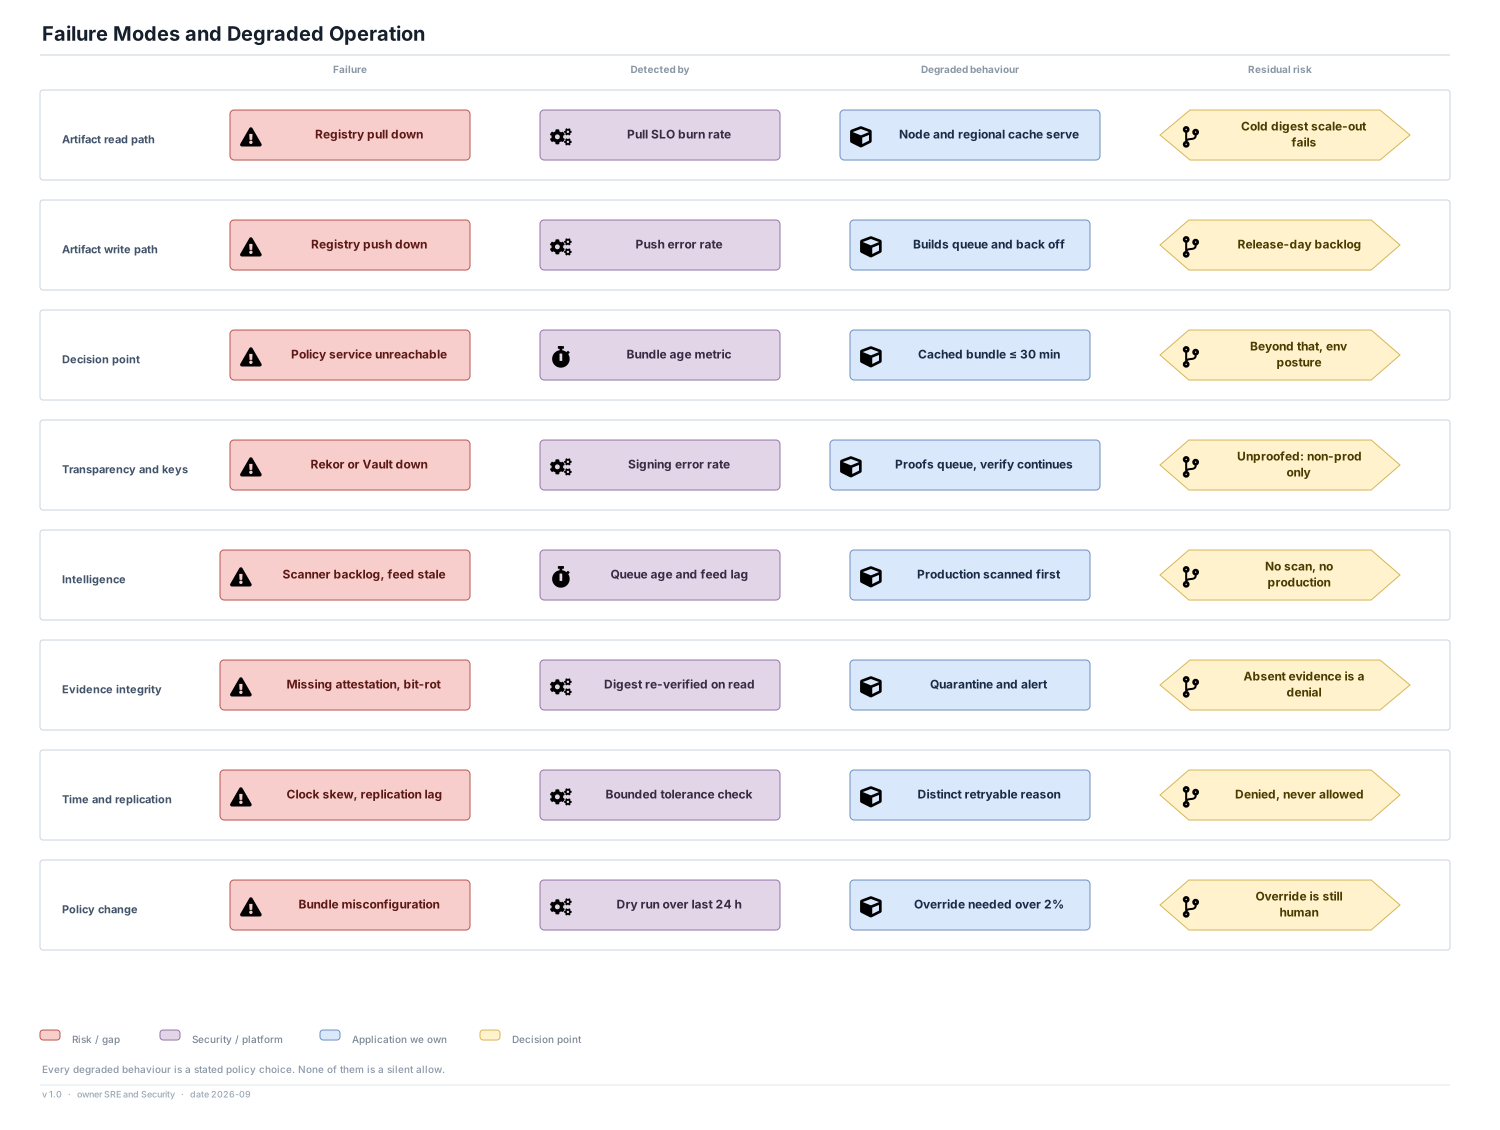
Trust zones, credential issue, key custody, revocation, tenant isolation, and every named failure mode.
Open svg/<view>.svg or drawio/<view>.drawio in draw.io Desktop or at app.diagrams.net to edit. The SVG carries the diagram inside it, so it is both the picture and the source. This folder is self-contained — copy it whole and every link still resolves.