Container Registry and Software Supply Chain Platform · View 29 of 33 · 6 · Assurance
Decisions
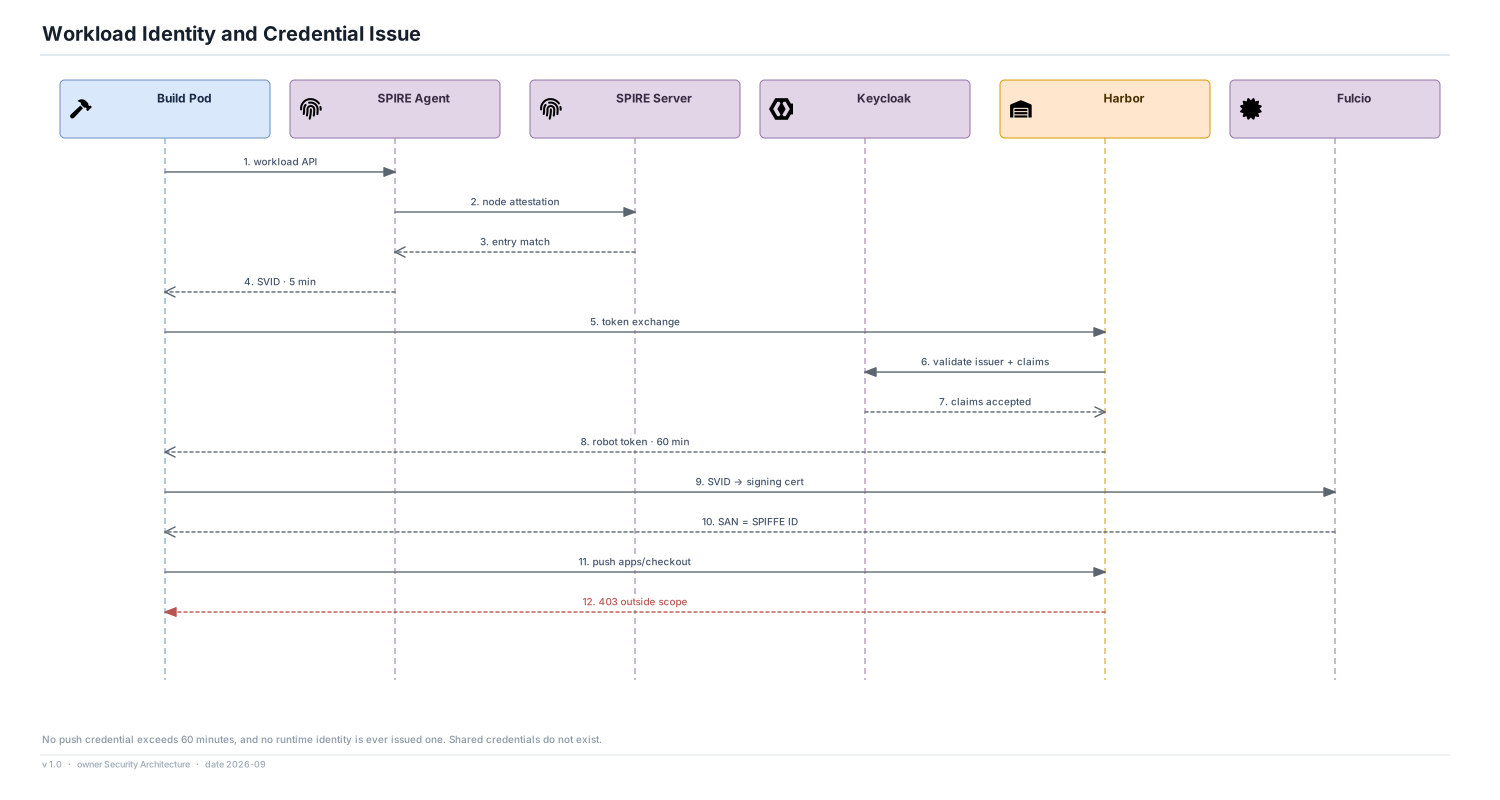
- SPIRE issues an SVID to the build pod after node and workload attestation; nothing is provisioned as a secret
- Harbor exchanges that SVID for a robot token scoped to the repositories that identity owns
- Runtime identities receive pull-only credentials scoped to a namespace and environment
Hard limits
- No credential with push scope has a lifetime exceeding 60 minutes
- Fulcio signing certificates are valid for 10 minutes
- A push outside the identity's scope is a 403 with a distinct reason code, logged
Separation of duty
- No single human identity can both grant signing authority and use it — enforced in Keycloak group membership, checked at review
- Root ceremony participation is a separate role again, with a two-person rule
- Every HSM operation is authorised and logged individually