Container Registry and Software Supply Chain Platform  ·  View 01 of 33  ·  1 · Context and scope

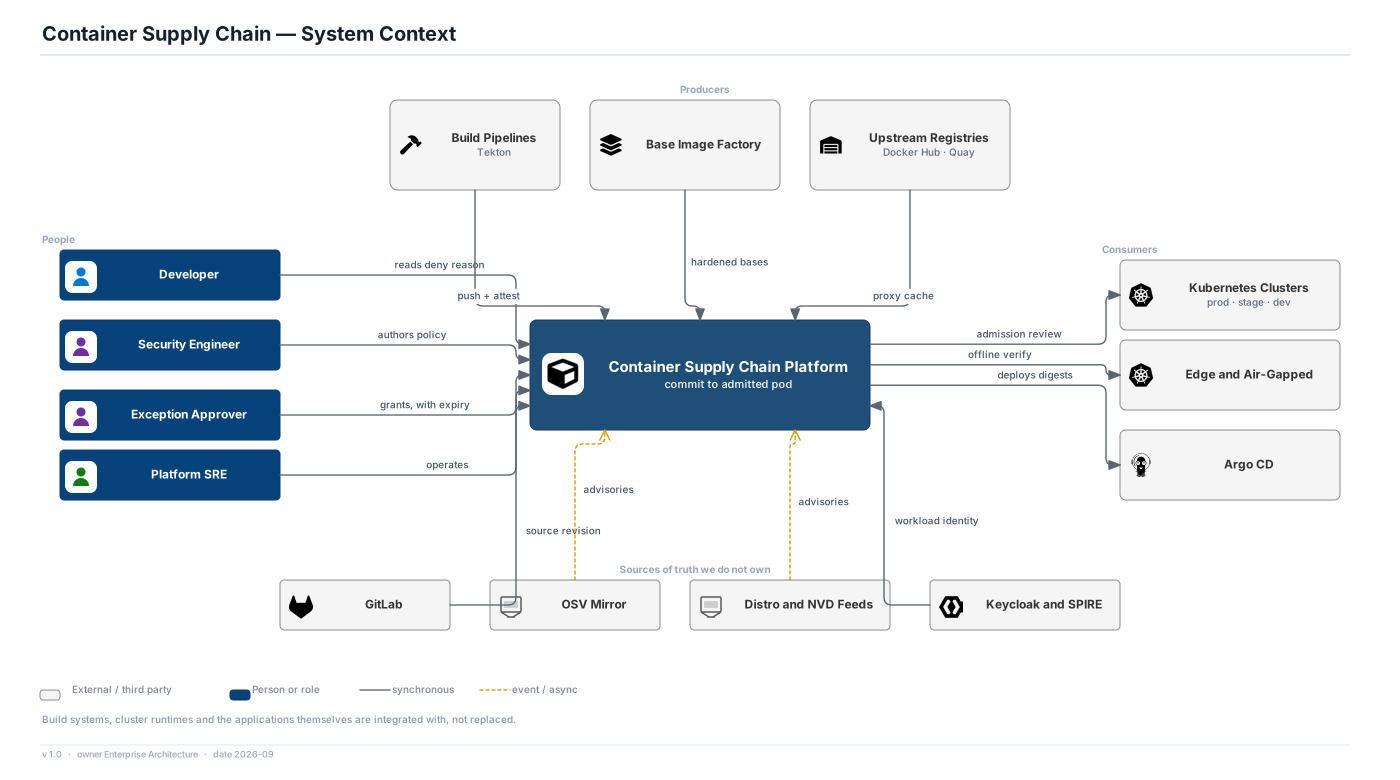
System Context

Who produces artifacts, who consumes them, and what the platform deliberately does not own.

Editable source SVG draw.io All views
Producers Build Pipelines Tekton Base Image Factory Upstream Registries Docker Hub · Quay People Developer Security Engineer Exception Approver Platform SRE Consumers Kubernetes Clusters prod · stage · dev Edge and Air-Gapped Argo CD Container Supply Chain Platform commit to admitted pod Sources of truth we do not own GitLab OSV Mirror Distro and NVD Feeds Keycloak and SPIRE reads deny reason authors policy grants, with expiry operates push + attest hardened bases proxy cache admission review offline verify deploys digests source revision advisories advisories workload identity Container Supply Chain — System Context External / third party Person or role synchronous event / async Build systems, cluster runtimes and the applications themselves are integrated with, not replaced. v 1.0 · owner Enterprise Architecture · date 2026-09

In scope

  • The OCI registry and its content-addressed artifact store
  • The evidence that travels with each artifact: signatures, provenance, SBOMs, findings
  • The enforcement point that refuses an artifact whose evidence does not satisfy policy
  • Re-evaluation of stored and running artifacts when advisories move

Out of scope

  • Build systems — Tekton is integrated with, not replaced
  • Cluster runtimes and the applications themselves
  • Source control, identity provider and advisory feeds remain external systems of record

Assumptions

  • Mid-size engineering organisation: 1,200 repositories, 40,000 retained artifacts, 14 TB
  • The whole stack is open source and runs on premises; the requirement named AWS, the deployment target here does not
  • GitLab, Keycloak and SPIRE already exist in the estate