Certificate Lifecycle Service  ·  View 11 of 21  ·  Data

Core Data Model

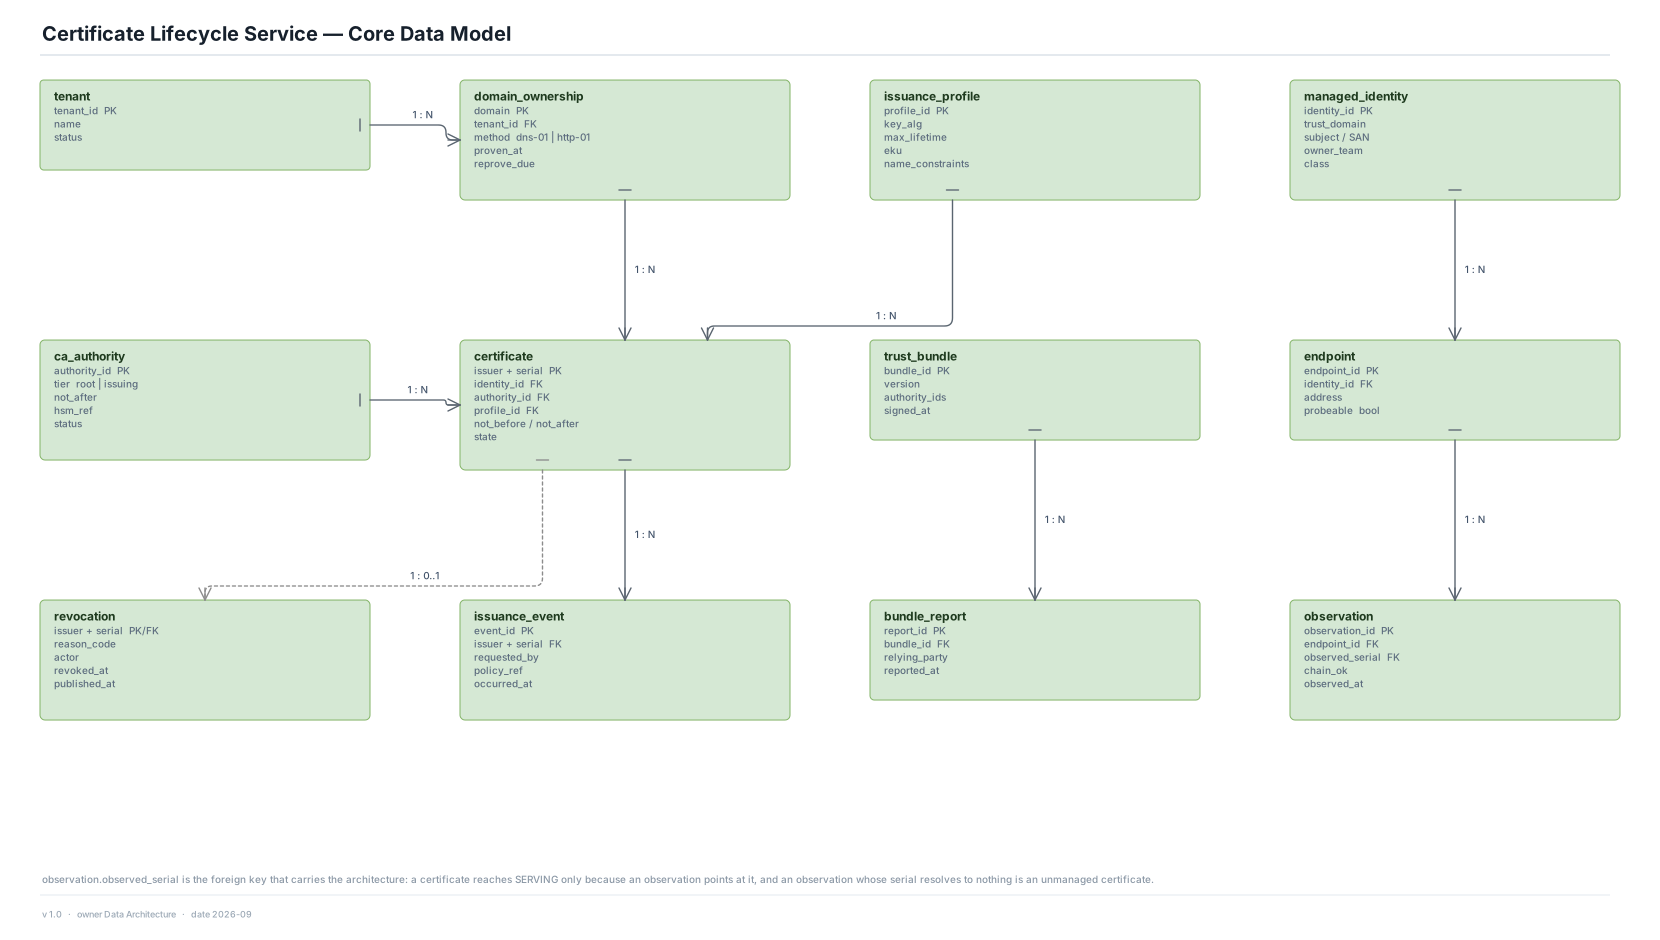
Twelve entities, and one foreign key that decides whether this is a certificate manager or a certificate inventory.

Editable source SVG draw.io All views
tenant tenant_id PK name status domain_ownership domain PK tenant_id FK method dns-01 | http-01 proven_at reprove_due issuance_profile profile_id PK key_alg max_lifetime eku name_constraints managed_identity identity_id PK trust_domain subject / SAN owner_team class ca_authority authority_id PK tier root | issuing not_after hsm_ref status certificate issuer + serial PK identity_id FK authority_id FK profile_id FK not_before / not_after state endpoint endpoint_id PK identity_id FK address probeable bool trust_bundle bundle_id PK version authority_ids signed_at revocation issuer + serial PK/FK reason_code actor revoked_at published_at issuance_event event_id PK issuer + serial FK requested_by policy_ref occurred_at bundle_report report_id PK bundle_id FK relying_party reported_at observation observation_id PK endpoint_id FK observed_serial FK chain_ok observed_at 1 : N 1 : N 1 : N 1 : N 1 : N 1 : N 1 : 0..1 1 : N 1 : N Certificate Lifecycle Service — Core Data Model observation.observed_serial is the foreign key that carries the architecture: a certificate reaches SERVING only because an observation points at it, and an observation whose serial resolves to nothing is an unmanaged certificate. v 1.0 · owner Data Architecture · date 2026-09

The key that carries the design

  • observation.observed_serial is a foreign key to certificate. A certificate reaches SERVING because an observation points at it — not because an issuance succeeded.
  • An observation whose serial resolves to nothing is, by definition, an unmanaged certificate, which is how discovery and the state machine become the same mechanism rather than two features.

Identity outlives certificates

  • managed_identity is the durable row: owner, trust domain, subject. Certificates are the perishable ones, and a compromise is recorded against the identity rather than only against the certificate it happened to hold.
  • ca_authority carries not_after like any other certificate, so a root or intermediate approaching expiry appears on the same clock as a leaf.

Omitted

  • The certificate-to-identity relation is carried as an attribute rather than drawn, to keep the relation lines readable; profile, authority and domain are the three drawn constraints on issuance.