Certificate Lifecycle Service  ·  View 10 of 21  ·  Data

Data Architecture and Ownership

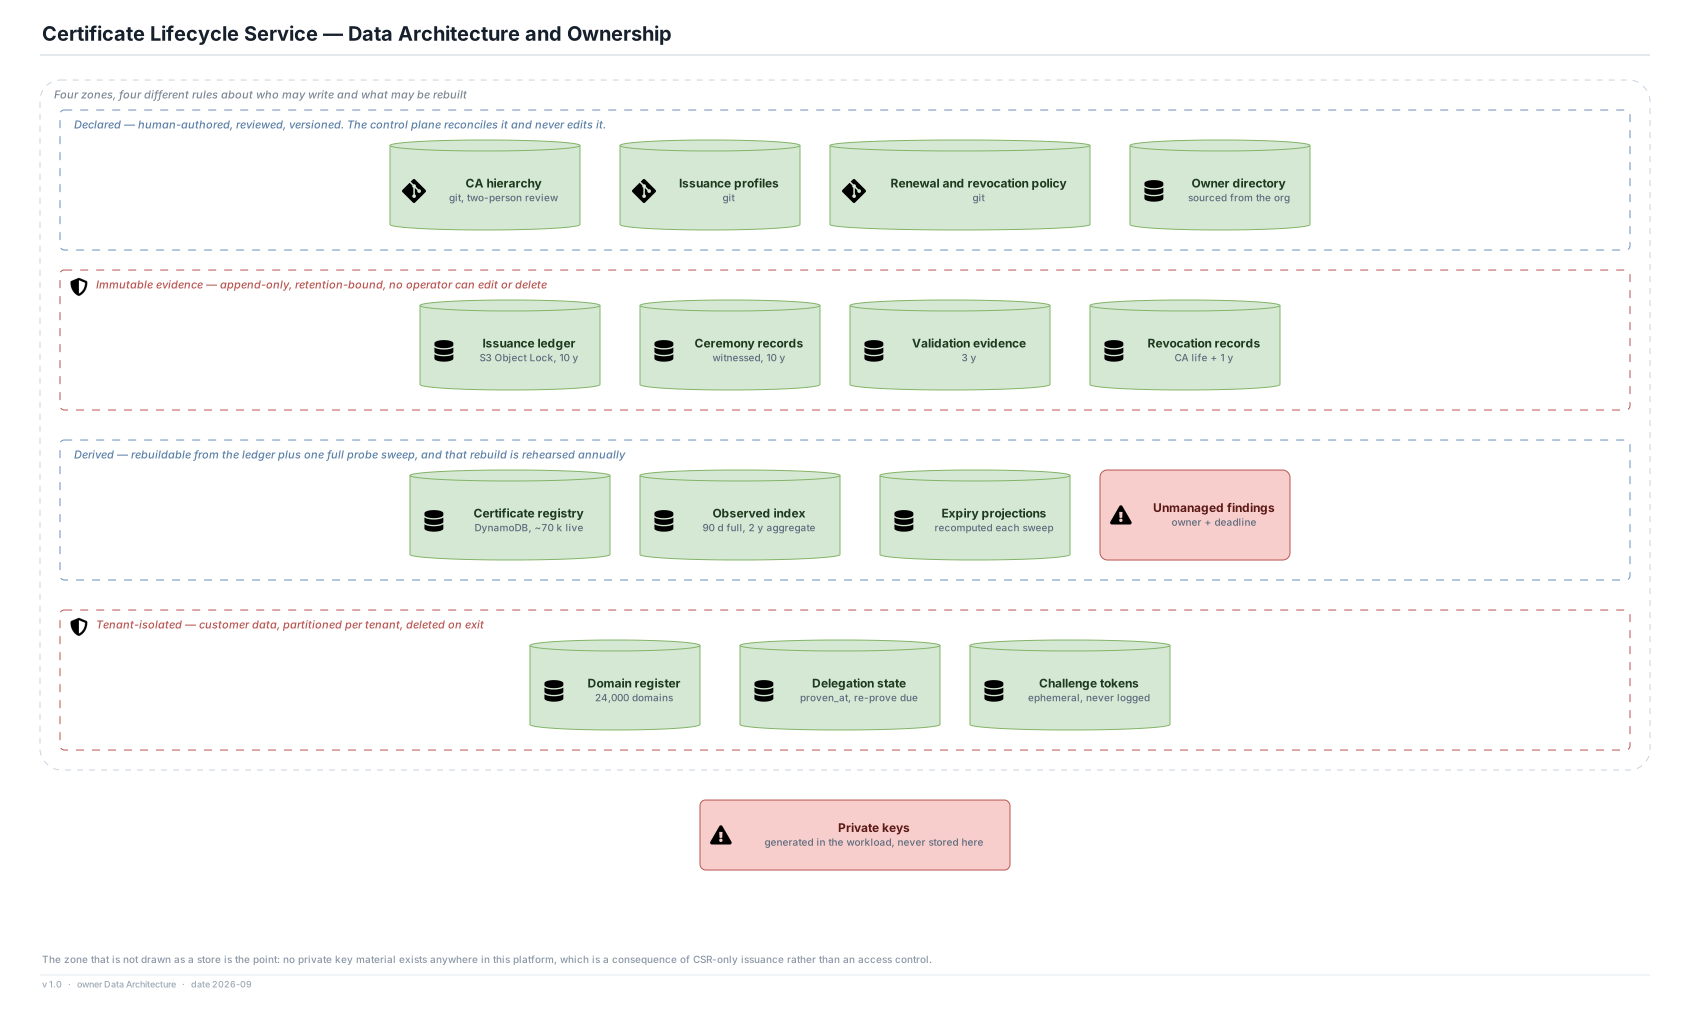
Four zones with four different rules about who may write, and one category of data that is deliberately absent.

Editable source SVG draw.io All views
Four zones, four different rules about who may write and what may be rebuilt Declared — human-authored, reviewed, versioned. The control plane reconciles it and never edits it. CA hierarchy git, two-person review Issuance profiles git Renewal and revocation policy git Owner directory sourced from the org Immutable evidence — append-only, retention-bound, no operator can edit or delete Issuance ledger S3 Object Lock, 10 y Ceremony records witnessed, 10 y Validation evidence 3 y Revocation records CA life + 1 y Derived — rebuildable from the ledger plus one full probe sweep, and that rebuild is rehearsed annually Certificate registry DynamoDB, ~70 k live Observed index 90 d full, 2 y aggregate Expiry projections recomputed each sweep Unmanaged findings owner + deadline Tenant-isolated — customer data, partitioned per tenant, deleted on exit Domain register 24,000 domains Delegation state proven_at, re-prove due Challenge tokens ephemeral, never logged Private keys generated in the workload, never stored here Certificate Lifecycle Service — Data Architecture and Ownership The zone that is not drawn as a store is the point: no private key material exists anywhere in this platform, which is a consequence of CSR-only issuance rather than an access control. v 1.0 · owner Data Architecture · date 2026-09

The rules per zone

  • Declared: human-authored, reviewed, versioned in git. The control plane reconciles it and never edits it, so a running system cannot quietly become its own policy authority.
  • Immutable evidence: append-only, retention-bound, no operator edit or delete. S3 Object Lock, not an IAM policy.
  • Derived: rebuildable from the ledger plus one full probe sweep — and that rebuild is rehearsed annually rather than assumed.
  • Tenant-isolated: partitioned per tenant, deleted on exit, challenge tokens never logged.

What is not here

  • No private key material exists anywhere in this platform. That is a consequence of CSR-only issuance, not an access control on a store — which means a full compromise of the platform's databases yields no key.
  • It also means a backup restore cannot revive a key that should be gone.

Assumption

  • Registry RPO 0, RTO ≤ 30 minutes; the ledger is the fallback source of truth for a rebuild.