Audit Log Service · View 39 of 40 · 7 · Assurance
Decisions
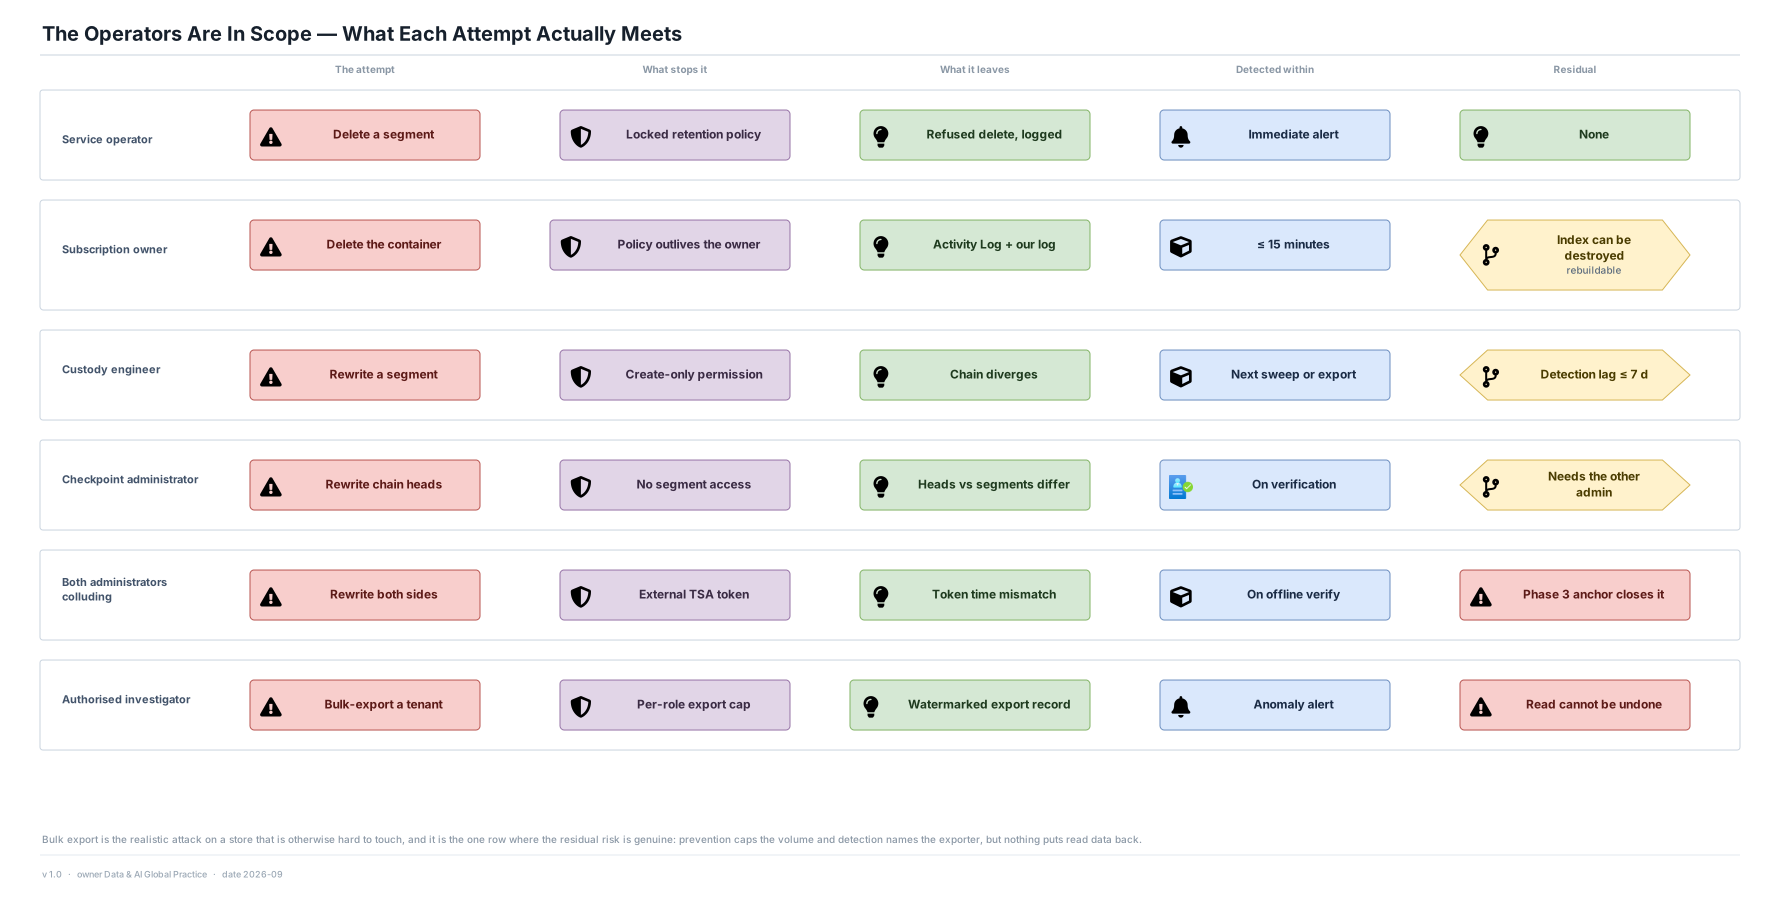
- The service's own operators are treated as an in-scope threat rather than an assumed-trusted party. This view is the test of whether the rest of the set was honest.
- Prevention is not enough — tampering must be provable. Access control can be misconfigured; the chain exists so an external party can detect what access control failed to prevent.
- The two administrator rows are separated deliberately: the segment administrator has no ledger access and the ledger administrator has no segment access, so the cheapest attack requires collusion.
Where it holds and where it does not
- Segment deletion by any principal, including the subscription owner: prevented outright by the locked retention policy, and the attempt is alerted.
- Two colluding administrators rewriting both segments and heads: caught by the external RFC 3161 token, whose time they cannot forge. Phase-3 witness anchoring closes this row properly.
- Bulk export by an authorised investigator: capped and detected, never undone. This is the one row with a genuine residual, and it is the reason export volume is capped per role rather than merely logged.
Risks
- Custody-plane segment rewriting is caught by chain divergence, but detection may lag by up to the seven-day sweep unless an export or on-demand verification touches the range sooner. A shorter sweep is a compute cost, and the number deserves review after the first year of real volume.