Spot Capacity Orchestrator · View 10 of 32 · 3 · Structure
Decisions
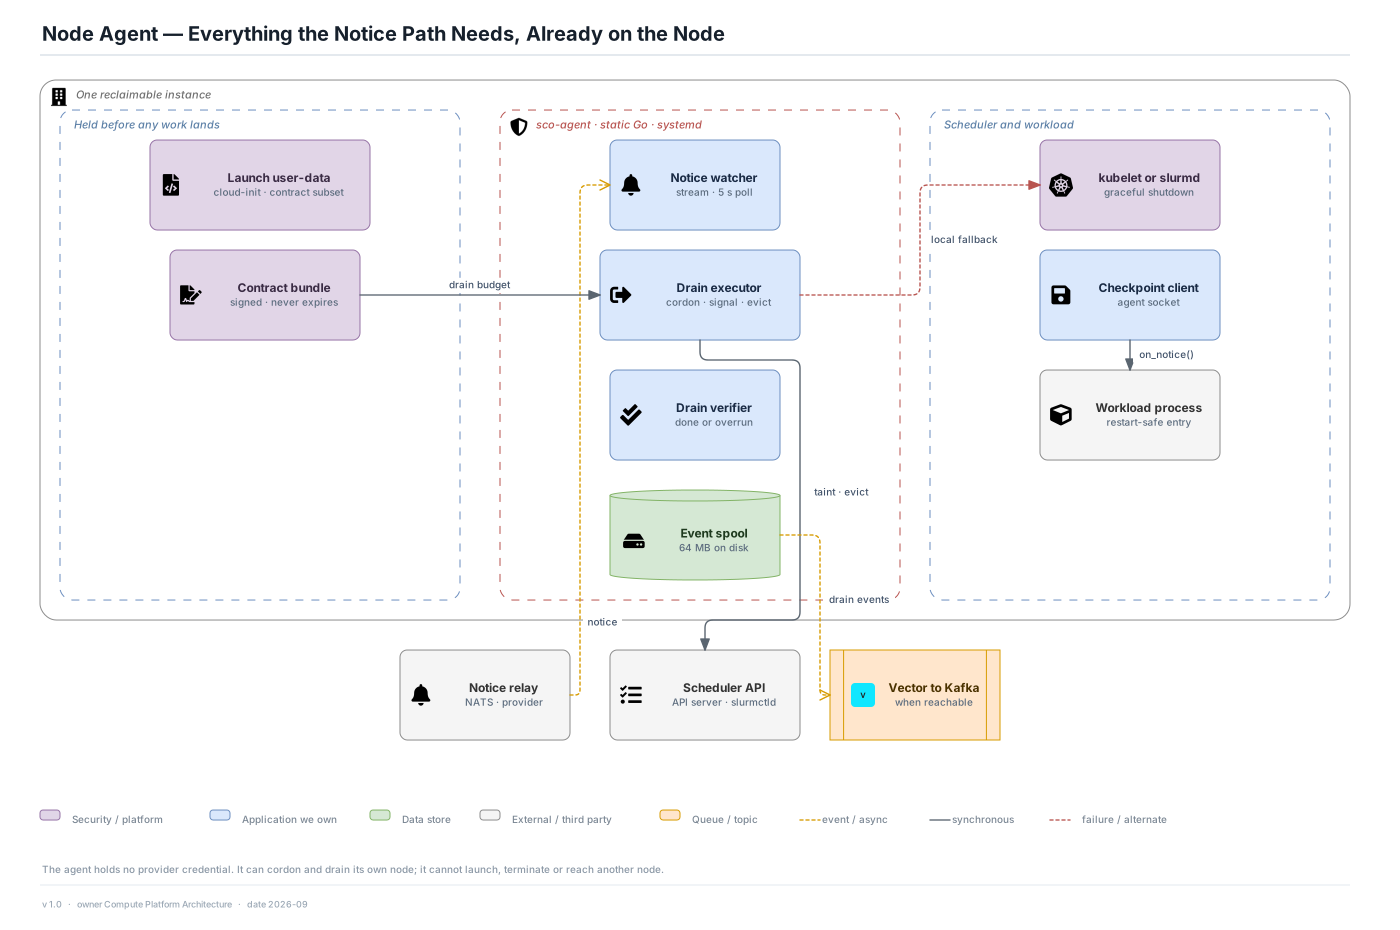
- A static Go binary under systemd, baked into every image, not a DaemonSet. It must run on Slurm nodes as well as Kubernetes nodes, and it must not depend on the scheduler it may have to work around.
- The contract subset arrives in cloud-init user-data at launch, and the signed bundle refreshes every 60 s afterwards. A node never has a window where work is running and the drain budget is unknown.
- Notice arrives on two channels: a subscription to the per-hall notice relay, and a 5-second poll of instance metadata in case the stream is down. A third channel is absence: the no-notice path is covered by leases and periodic checkpoints, not by the agent.
Scope of power
- The agent authenticates with a node-bound identity, and an admission policy lets it taint and evict on its own node only. It holds no provider credential: it cannot launch, terminate or touch another node, so a compromised agent is a compromised node and nothing more.
Footprint
- Budget of 20 millicores and 40 MiB per node. At 5,000 nodes that is 100 vCPU fleet-wide, and it counts against the orchestrator's 2% cost ceiling (view 28).