Passkey Authentication Service · View 15 of 21 · Runtime
Decisions
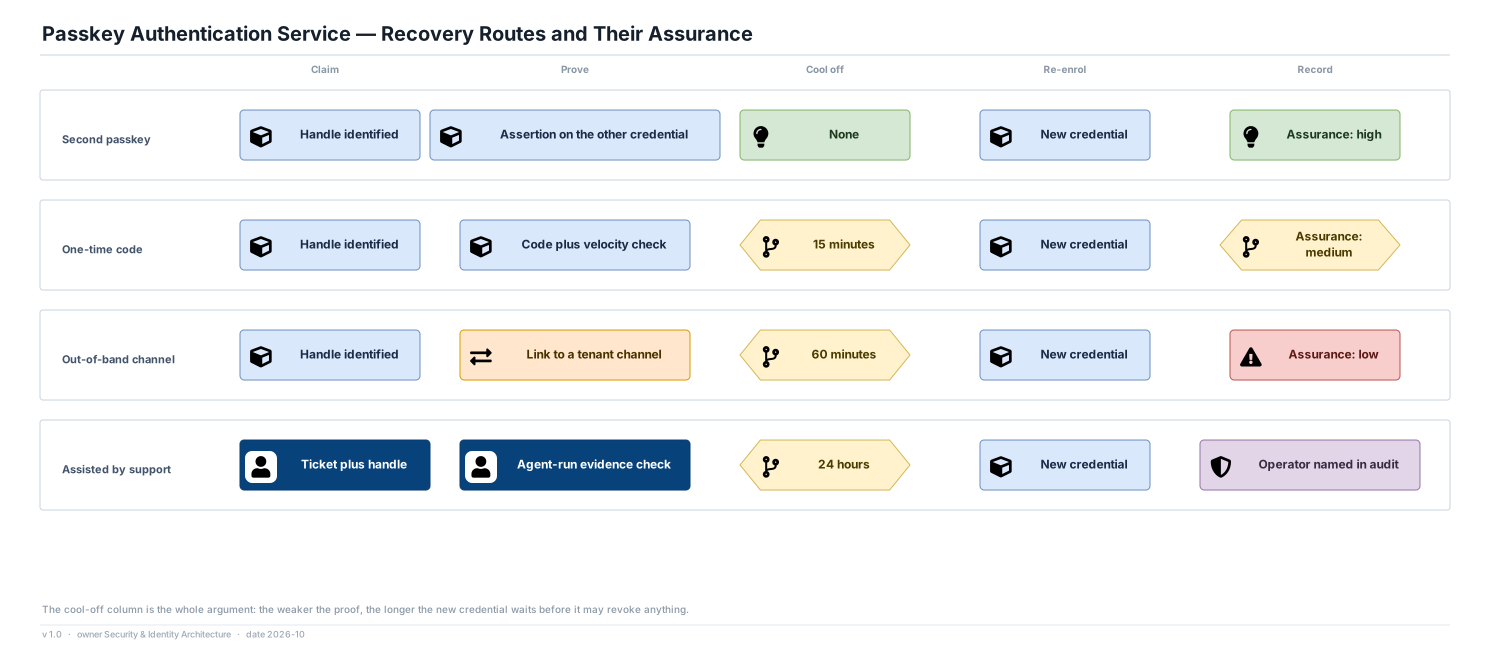
- Every route ends in a new credential. A route that returns a session without one is counted as an incomplete recovery, not a successful login.
- Assurance is a property of the route and is carried into the verdict, so a tenant can let a low-assurance recovery sign in but not authorise a payment.
- The cool-off window scales inversely with the proof: none for a second passkey, 24 hours for an assisted recovery. The window is what stops a successful takeover evicting the owner.
- An assisted recovery names the operator in the audit trail. There is no shared support account anywhere in the platform.
Assumptions
- Cool-off windows of 0, 15 minutes, 60 minutes and 24 hours; all four are tenant-configurable within a platform floor.
- Assisted recovery is a minority route by volume and the dominant one by cost per case.
- Recovery attempts are rate-limited per handle and per network, and a burst across many handles is an abuse signal rather than many independent events.
Risks
- The legitimate owner of a lost device waits out the same window as an attacker. For the user in view 05, that is the single worst moment in the product, and it is a deliberate trade.