Internal Developer Platform  ·  View 20 of 21  ·  Assurance

Trust Zones

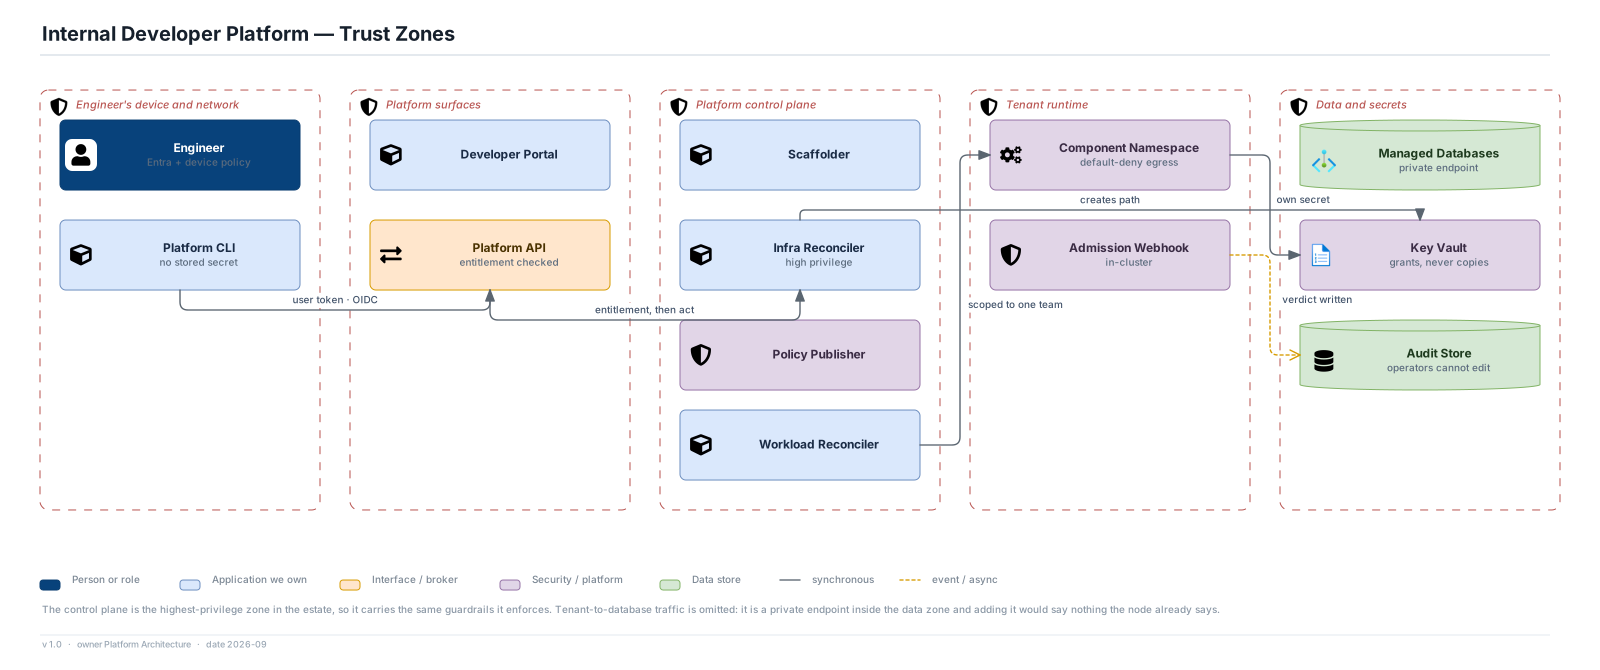
Five zones, and the fact that the highest-privilege one is the platform's own.

Editable source SVG draw.io All views
Engineer's device and network Engineer Entra + device policy Platform CLI no stored secret Platform surfaces Developer Portal Platform API entitlement checked Platform control plane Scaffolder Infra Reconciler high privilege Policy Publisher Workload Reconciler Tenant runtime Component Namespace default-deny egress Admission Webhook in-cluster Data and secrets Managed Databases private endpoint Key Vault grants, never copies Audit Store operators cannot edit user token · OIDC entitlement, then act creates path scoped to one team own secret verdict written Internal Developer Platform — Trust Zones Person or role Application we own Interface / broker Security / platform Data store synchronous event / async The control plane is the highest-privilege zone in the estate, so it carries the same guardrails it enforces. Tenant-to-database traffic is omitted: it is a private endpoint inside the data zone and adding it would say nothing the node already says. v 1.0 · owner Platform Architecture · date 2026-09

Decisions

  • The control plane holds the estate's highest privilege — it can provision, deploy and grant — so it carries the same guardrails, review and audit it enforces on tenants (ADR-15).
  • Key Vault is granted, never read: the platform creates a path and binds an identity to it, and no plaintext secret passes through the portal, the catalog or a pipeline log.
  • The audit store is the one place the platform's own operators cannot write (ADR-16).

Assumptions

  • Default-deny egress from tenant namespaces; private endpoints for managed data services (stated assumptions).
  • Device policy enforced at sign-in by Entra Conditional Access.

Separation of duty

  • Authoring a policy, granting an exception to it, and deploying are three distinct entitlements, so no single actor can lower a control and then exploit it (ADR-08, ADR-15).
  • Tenant-to-database traffic is omitted from the drawing: it is a private endpoint inside the data zone and the edge would say nothing the node does not.