Certificate Lifecycle Service  ·  View 07 of 21  ·  Structure

Container View

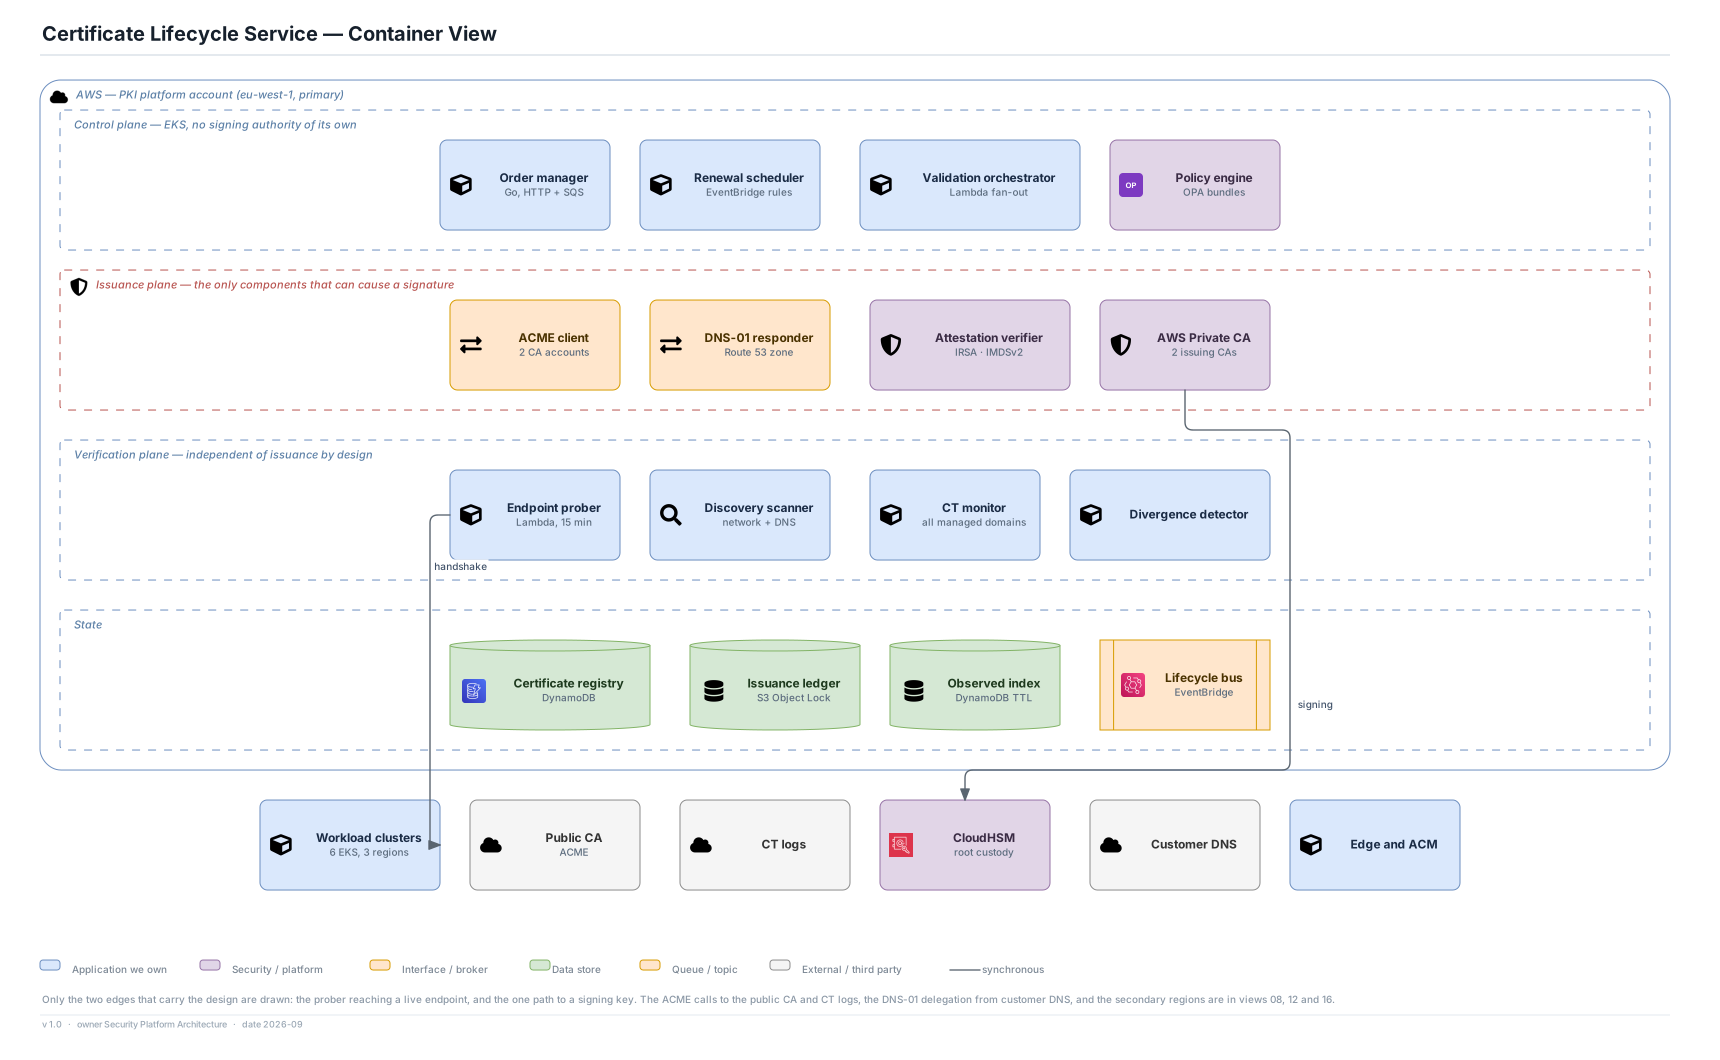
The deployable units, split across three planes that are deliberately not allowed to be each other.

Editable source SVG draw.io All views
AWS — PKI platform account (eu-west-1, primary) Control plane — EKS, no signing authority of its own Order manager Go, HTTP + SQS Renewal scheduler EventBridge rules Validation orchestrator Lambda fan-out Policy engine OPA bundles Issuance plane — the only components that can cause a signature ACME client 2 CA accounts DNS-01 responder Route 53 zone Attestation verifier IRSA · IMDSv2 AWS Private CA 2 issuing CAs Verification plane — independent of issuance by design Endpoint prober Lambda, 15 min Discovery scanner network + DNS CT monitor all managed domains Divergence detector State Certificate registry DynamoDB Issuance ledger S3 Object Lock Observed index DynamoDB TTL Lifecycle bus EventBridge Workload clusters 6 EKS, 3 regions Public CA ACME CT logs CloudHSM root custody Customer DNS Edge and ACM handshake signing Certificate Lifecycle Service — Container View Application we own Security / platform Interface / broker Data store Queue / topic External / third party synchronous Only the two edges that carry the design are drawn: the prober reaching a live endpoint, and the one path to a signing key. The ACME calls to the public CA and CT logs, the DNS-01 delegation from customer DNS, and the secondary regions are in views 08, 12 and 16. v 1.0 · owner Security Platform Architecture · date 2026-09
Decisions

  • The control plane holds no signing authority of its own: it can request a signature and never produce one.
  • The verification plane is a separate set of components with its own schedule and its own network path, so that an outage of issuance does not also blind observation.
  • State is split four ways — registry (derived), ledger (immutable), observed index (high-volume, expendable) and the lifecycle bus — because they have four different retention and recovery rules.

Realisation on AWS

  • Control plane on EKS; validation fan-out and probing on Lambda; registry in DynamoDB as a global table; ledger in S3 with Object Lock; EventBridge as the lifecycle spine.
  • AWS Private CA holds the two issuing authorities; CloudHSM holds root custody outside the account's normal access path.

Omitted

  • Only two external edges are drawn — the prober reaching a live endpoint, and the one path to a signing key. The ACME and CT calls, the DNS-01 delegation and the secondary regions are in views 08, 12 and 16.