Audit Log Service · View 21 of 40 · 5 · Runtime
Decisions
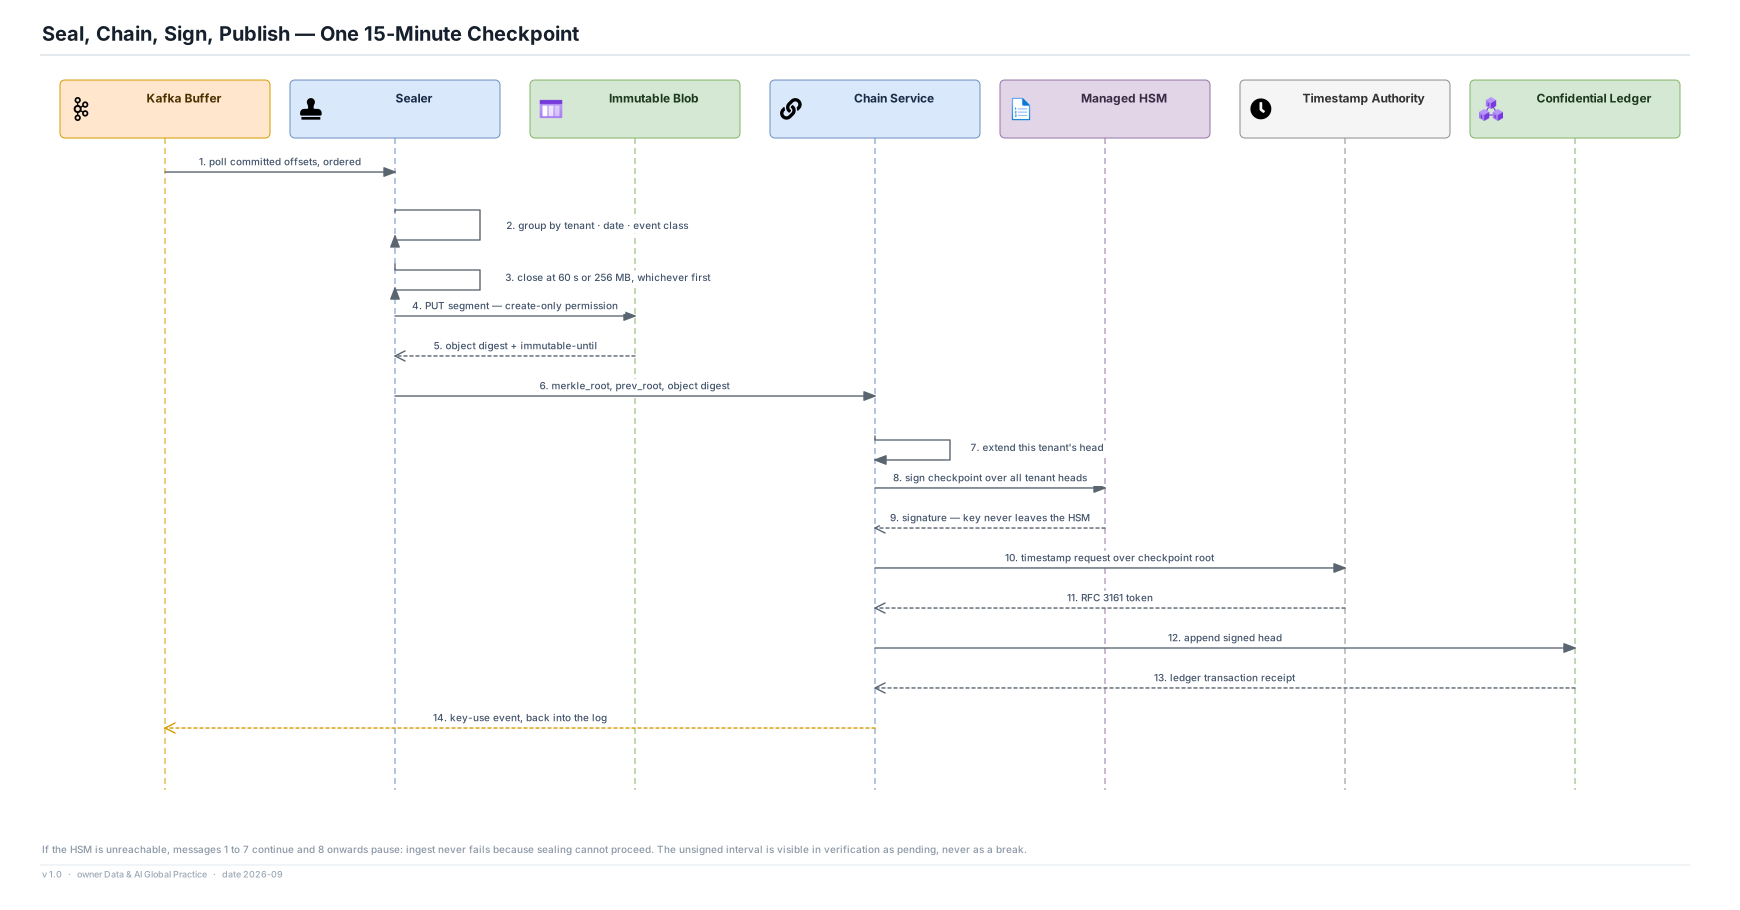
- The sealer holds create-only permission on the segment container. There is no code path in the custody plane that can overwrite an object it has just written, and no role that would let it.
- The checkpoint is signed over every tenant head at once, so one HSM operation every fifteen minutes covers 500 chains. That is what keeps HSM cost fixed rather than proportional to tenants.
- The RFC 3161 countersignature comes from a TSA outside this estate. A timestamp authority we operated would be a clock we could move, which is the same as having none.
Degradation
- If the HSM is unreachable, messages 1 to 7 continue and 8 onwards pause. Ingest never fails because sealing cannot proceed — durability outranks freshness, and this is where that principle is actually enforced.
- The unsigned interval is visible in verification as pending rather than broken, and is alerted at 30 minutes.
- If the sealer dies mid-segment it resumes from the last checkpoint and re-seals the incomplete segment. It is never discarded, and the gap is visible in verification.
Numbers
- Segment seals ≤ 60 s. Checkpoints every 15 min. One HSM sign operation per checkpoint per region.
- Every use of the signing key emits a key-use record into this log, which means the log records the operations that make the log believable.