Secrets Distribution Service · View 02 of 34 · 1 · Context and scope
Decisions
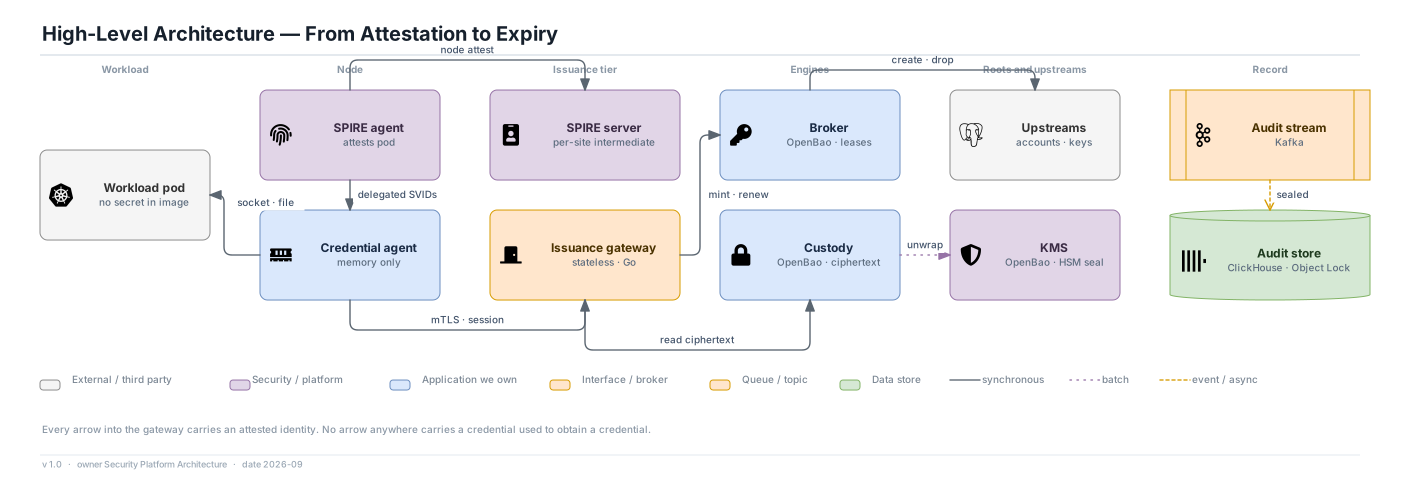
- Attestation comes first and is a separate product. SPIRE turns what the infrastructure knows about a pod into a short-lived identity; nothing downstream accepts anything else.
- Brokerage and custody are separate engines. A minted database account and a partner's API key have different lifecycles, different failure modes and different guarantees, so they do not share a cluster, a key or a promise.
- The gateway is the only door. It is stateless and small, and it holds the checks that must precede any policy: environment, key binding, restore generation, admission and audit posture.
Why this shape lasts
- Each stage speaks a standard: SPIFFE for identity, the OpenBao API for engines, SQL and admin APIs for upstreams, Kafka for the record. Any one can be replaced without renegotiating the others.
Read next
- The chain of trust is view 10. The checks inside the gateway are view 12. How the audit record is kept is view 15.