Passkey Authentication Service · View 13 of 21 · Runtime
Decisions
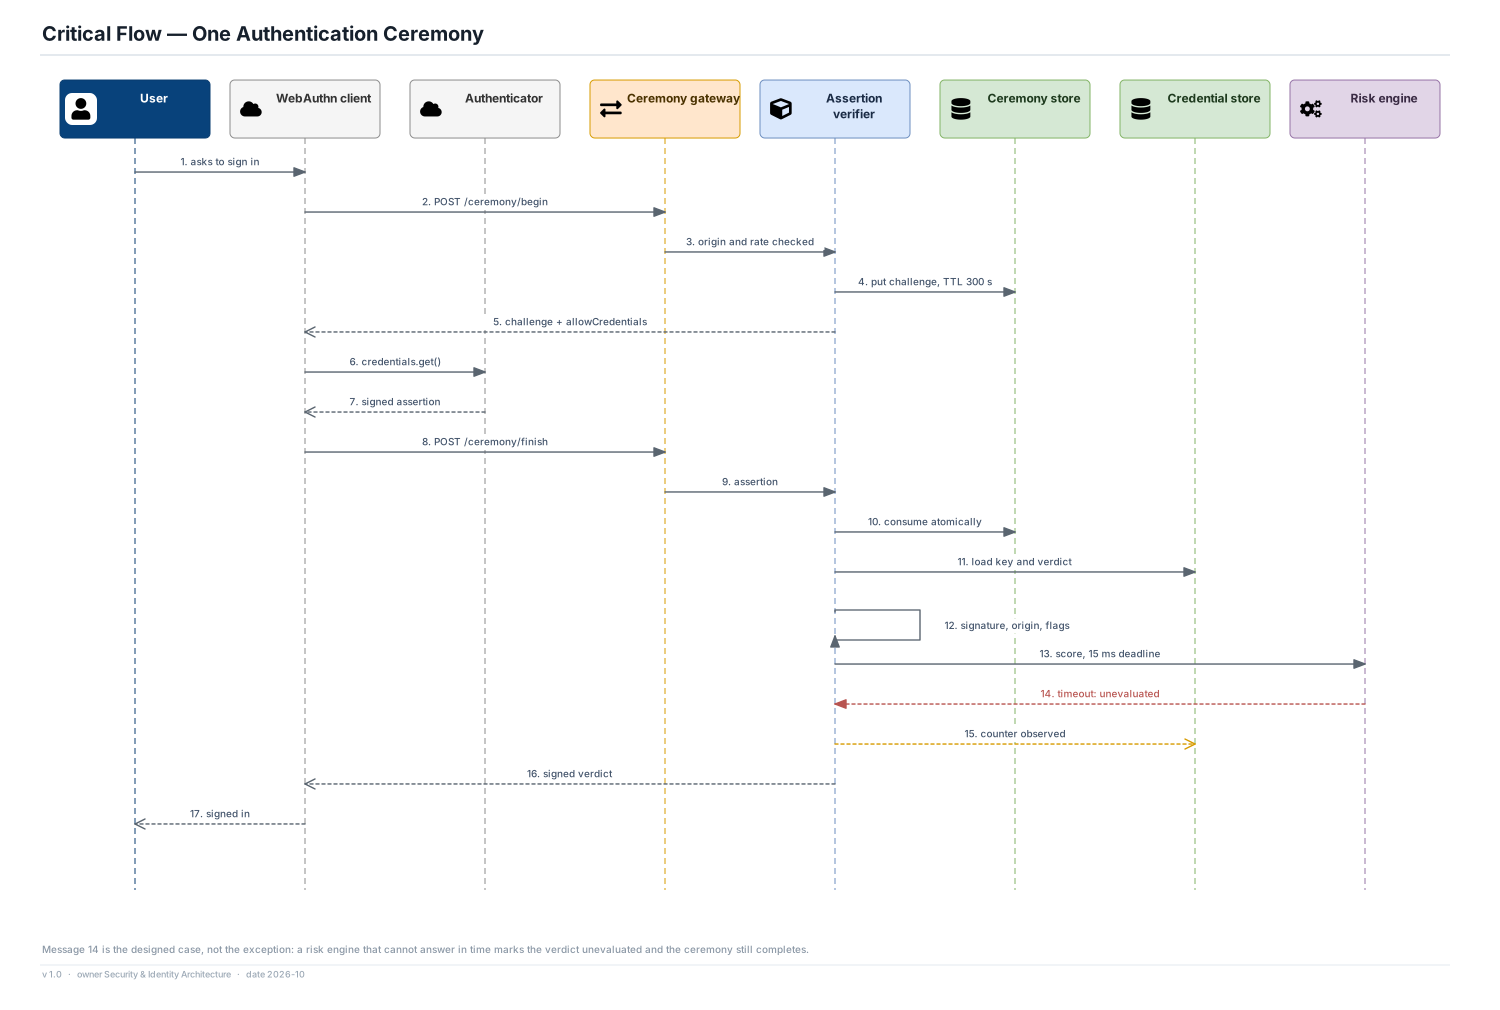
- The challenge is consumed atomically before the signature is verified, so a replay cannot win a race against a valid assertion.
- The credential and its admission verdict are loaded together, which is what lets verification be pure cryptography against a stored decision instead of a policy evaluation.
- The risk engine is called with a 15 ms deadline and its timeout is drawn as the normal case: the ceremony completes and the verdict says "unevaluated" so the relying party can choose to step up.
- The sign-counter observation is asynchronous. It is evidence, not a gate, except where tenant policy makes it one.
Assumptions
- Two round trips to the platform per ceremony, which is why challenge issuance is the cheaper call and the one shed first.
- Risk deadline 15 ms inside a 60 ms p99 budget.
- Ceremony TTL 300 seconds, matching common WebAuthn client timeouts.
Risks
- A ceremony store outage fails this flow closed at message 10, which is correct and still looks to the user like a broken login. The error taxonomy has to distinguish "restart the ceremony" from "stop trying" or the support desk cannot.