Passkey Authentication Service  ·  View 07 of 21  ·  Structure

Layered Architecture

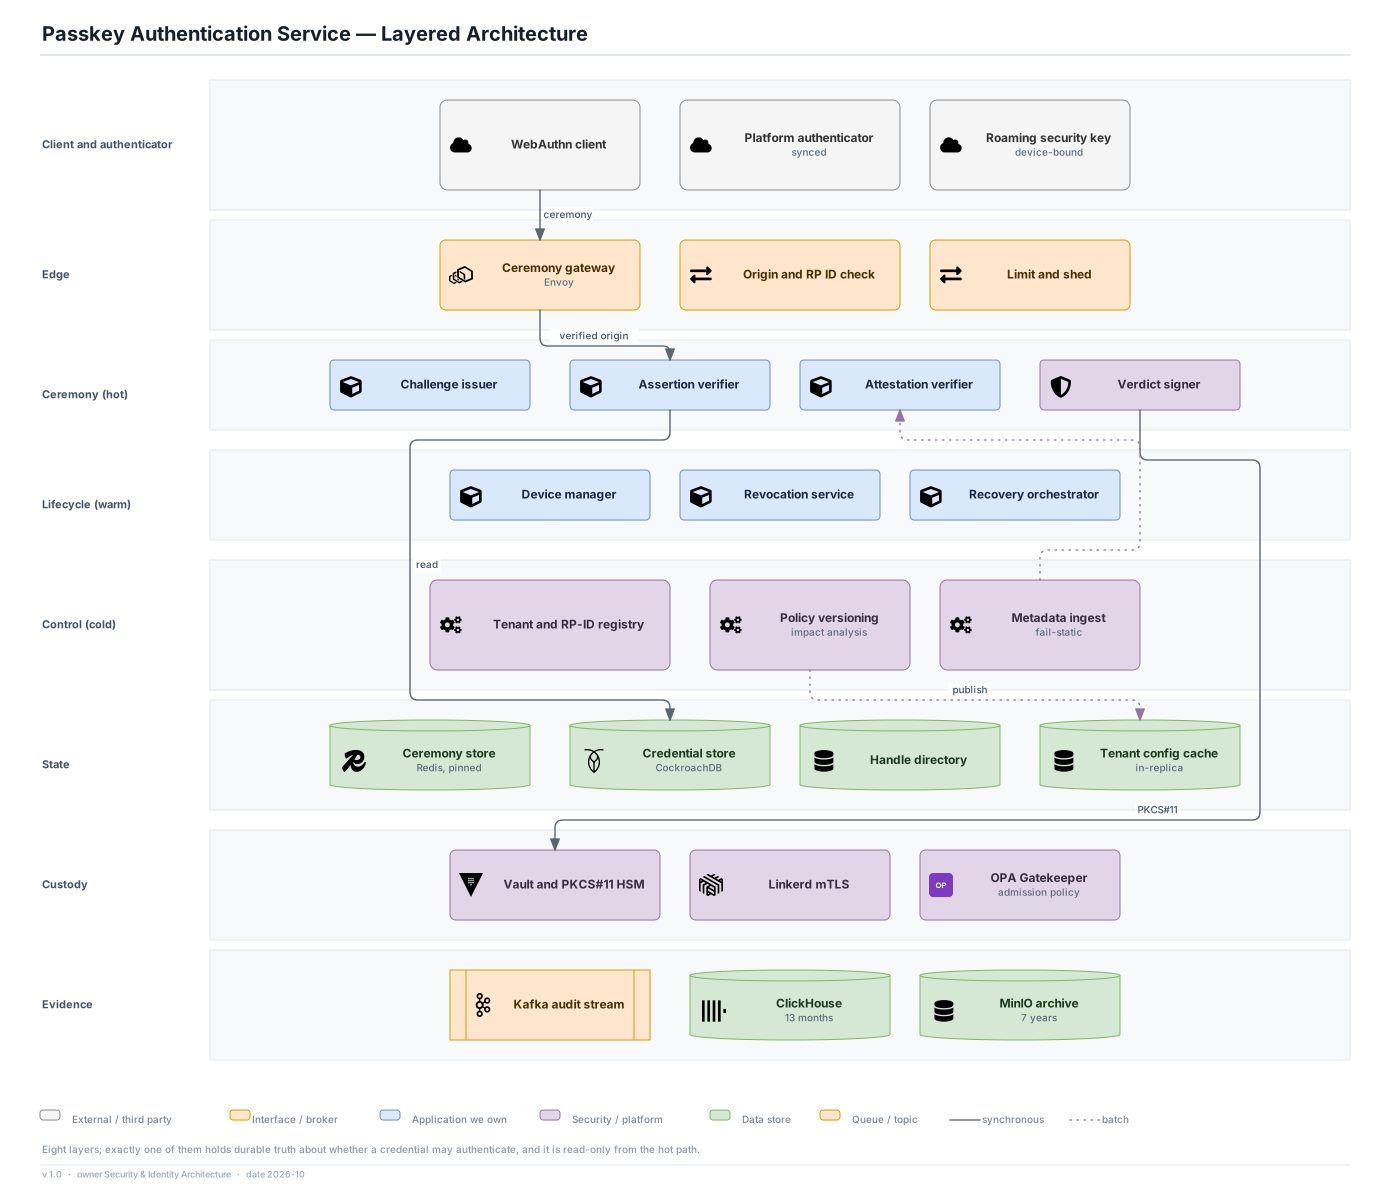
Eight layers, of which exactly one holds durable truth about whether a credential may authenticate.

Editable source SVG draw.io All views
Client and authenticator WebAuthn client Platform authenticator synced Roaming security key device-bound Edge Ceremony gateway Envoy Origin and RP ID check Limit and shed Ceremony (hot) Challenge issuer Assertion verifier Attestation verifier Verdict signer Lifecycle (warm) Device manager Revocation service Recovery orchestrator Control (cold) Tenant and RP-ID registry Policy versioning impact analysis Metadata ingest fail-static State Ceremony store Redis, pinned Credential store CockroachDB Handle directory Tenant config cache in-replica Custody Vault and PKCS#11 HSM Linkerd mTLS OPA Gatekeeper admission policy Evidence Kafka audit stream ClickHouse 13 months MinIO archive 7 years ceremony verified origin read PKCS#11 publish Passkey Authentication Service — Layered Architecture External / third party Interface / broker Application we own Security / platform Data store Queue / topic synchronous batch Eight layers; exactly one of them holds durable truth about whether a credential may authenticate, and it is read-only from the hot path. v 1.0 · owner Security & Identity Architecture · date 2026-10

Decisions

  • Ceremony, lifecycle and control are three layers rather than one service, because they have three different availability targets and three different failure behaviours.
  • The state layer is split by lifetime, not by technology: a 300-second ceremony record and a permanent credential record have nothing in common but the word "store".
  • Custody is its own layer so that the set of things able to sign on behalf of the platform is small enough to enumerate.
  • Evidence is the bottom layer and depends on everything above it, never the reverse.

What this view omits

  • Audit emission from every layer, and the config-cache read from every service: both would be an arrow from every box to one box.
  • The warm plane's write to the credential store, which view 08 draws.

Risks

  • A layered picture invites a layered deployment. These eight layers are three deployable planes, and conflating the two produces a control plane on the login path.