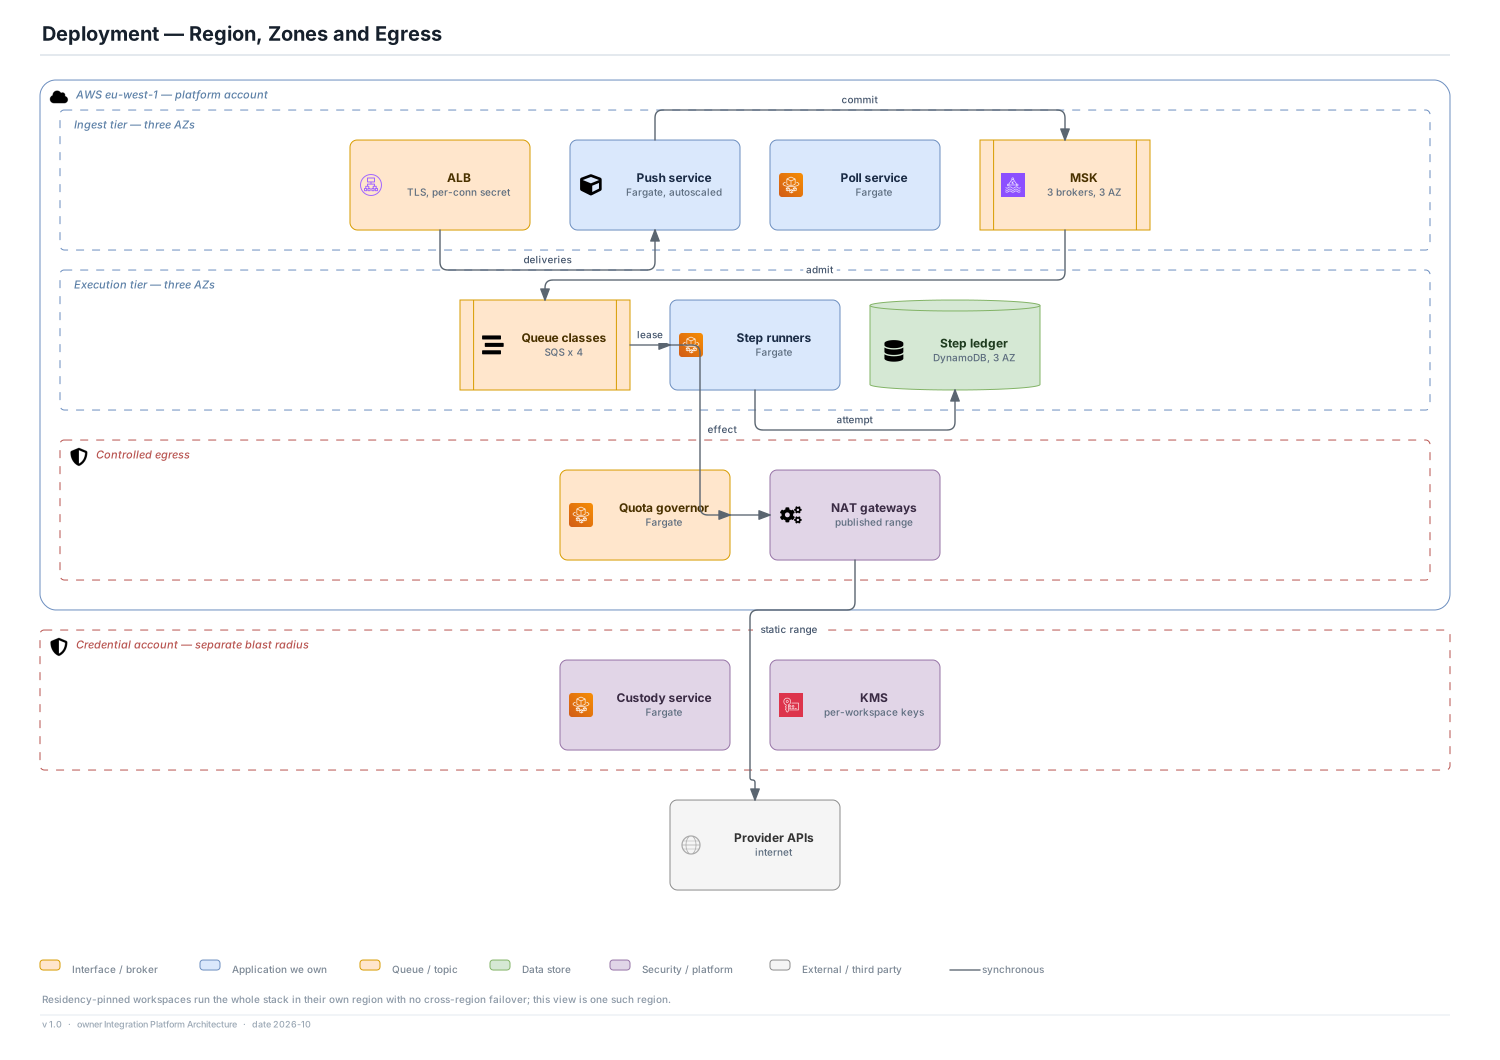
No-Code SaaS Automation Platform · View 15 of 21 · Operations
Decisions
- A published, stable NAT egress range is a product feature, not an implementation detail: customers and providers allowlist it, which means it cannot change without notice.
- The credential account is a separate account in the same region — the blast-radius boundary is an account boundary, so a compromised task role in the platform account cannot reach the key material.
- Three AZs for MSK and DynamoDB, because the two authoritative stores carry RPO 0 and an AZ loss must not cost a committed trigger.
Assumptions
- RTO 5 min for the execution plane in-region; RTO 20 min to serve ingest and execution from a second region for non-resident workspaces.
- Residency-pinned workspaces run this whole stack in their own region with no cross-region failover — the availability cost of a residency promise, taken deliberately.
Risks
- The NAT range is a shared identity: one workspace's abusive automation can get the range rate-limited or blocked by a provider for every other workspace behind it.