Model Evaluation Service  ·  View 21 of 21  ·  Assurance

Identity and Access

Who may change a gate, and the one request the platform is required to refuse.

Editable source SVG draw.io All views
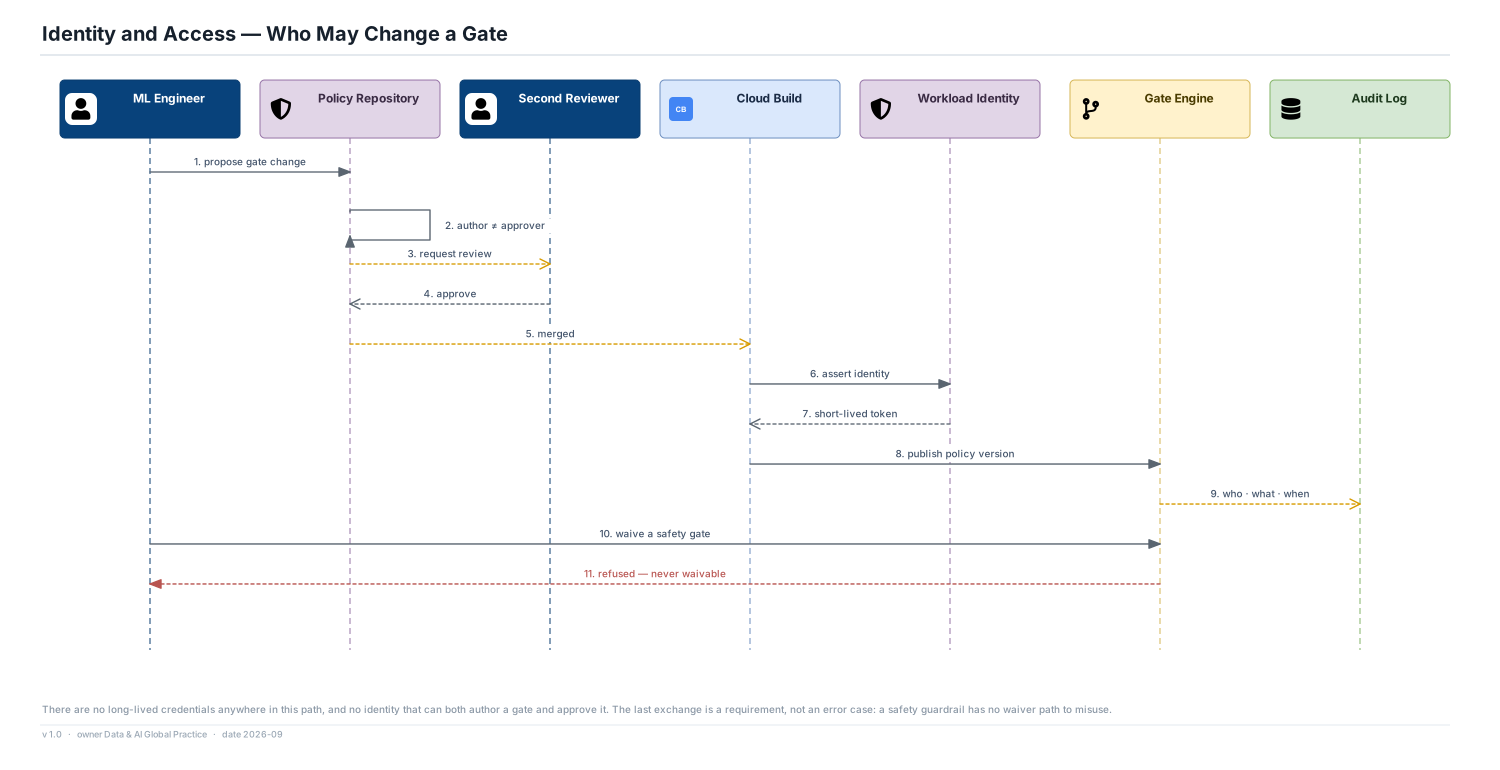
ML Engineer Policy Repository Second Reviewer Cloud Build Workload Identity Gate Engine Audit Log 1. propose gate change 2. author ≠ approver 3. request review 4. approve 5. merged 6. assert identity 7. short-lived token 8. publish policy version 9. who · what · when 10. waive a safety gate 11. refused — never waivable Identity and Access — Who May Change a Gate There are no long-lived credentials anywhere in this path, and no identity that can both author a gate and approve it. The last exchange is a requirement, not an error case: a safety guardrail has no waiver path to misuse. v 1.0 · owner Data & AI Global Practice · date 2026-09

Decisions

  • The gate is a production control: author and approver must be different people, and a candidate's own author cannot approve the gate it will face.
  • Workload Identity Federation throughout — no long-lived credentials anywhere in the policy path.
  • Every waiver carries a named approver, a reason and an expiry, and sits on a standing register.

The refusal

  • A safety guardrail gate has no waiver path at all. The last exchange in this view is a requirement, not an error case — there is nothing to misuse.

Audit

  • Gate changes, waivers and raw-trace access are written immutably. A release decision must stay defensible for 7 years (stated assumption).