Model Evaluation Service  ·  View 20 of 21  ·  Assurance

Security Trust Zones

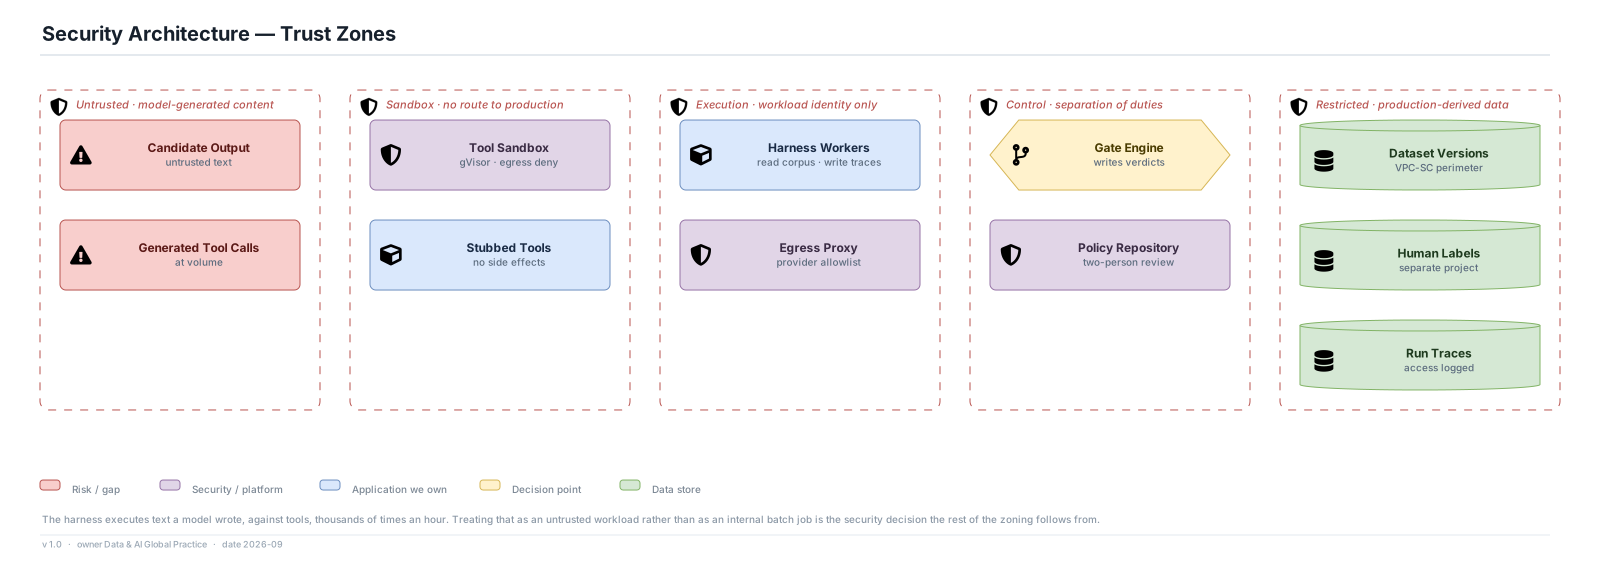
Five zones, drawn around the fact that this platform executes text a model wrote, thousands of times an hour.

Editable source SVG draw.io All views
Untrusted · model-generated content Candidate Output untrusted text Generated Tool Calls at volume Sandbox · no route to production Tool Sandbox gVisor · egress deny Stubbed Tools no side effects Execution · workload identity only Harness Workers read corpus · write traces Egress Proxy provider allowlist Control · separation of duties Gate Engine writes verdicts Policy Repository two-person review Restricted · production-derived data Dataset Versions VPC-SC perimeter Human Labels separate project Run Traces access logged Security Architecture — Trust Zones Risk / gap Security / platform Application we own Decision point Data store The harness executes text a model wrote, against tools, thousands of times an hour. Treating that as an untrusted workload rather than as an internal batch job is the security decision the rest of the zoning follows from. v 1.0 · owner Data & AI Global Practice · date 2026-09

Decisions

  • Model output and its tool calls are untrusted content. Treating the harness as an untrusted workload rather than an internal batch job is the decision the rest of the zoning follows from.
  • The sandbox has no network route to production and no side-effecting tools — only stubs.
  • All outbound inference leaves through an allowlisting egress proxy, so a prompt-injected tool call cannot reach an arbitrary host.

Data protection

  • Production-derived content sits inside a VPC Service Controls perimeter; every raw trace access is logged and attributable.

Separation of duties

  • The harness reads the corpus and writes traces. It cannot read a human label, write a verdict, or alter a gate policy.