Edge Cache and CDN Platform · View 01 of 29 · 1 · Context and scope
Decisions
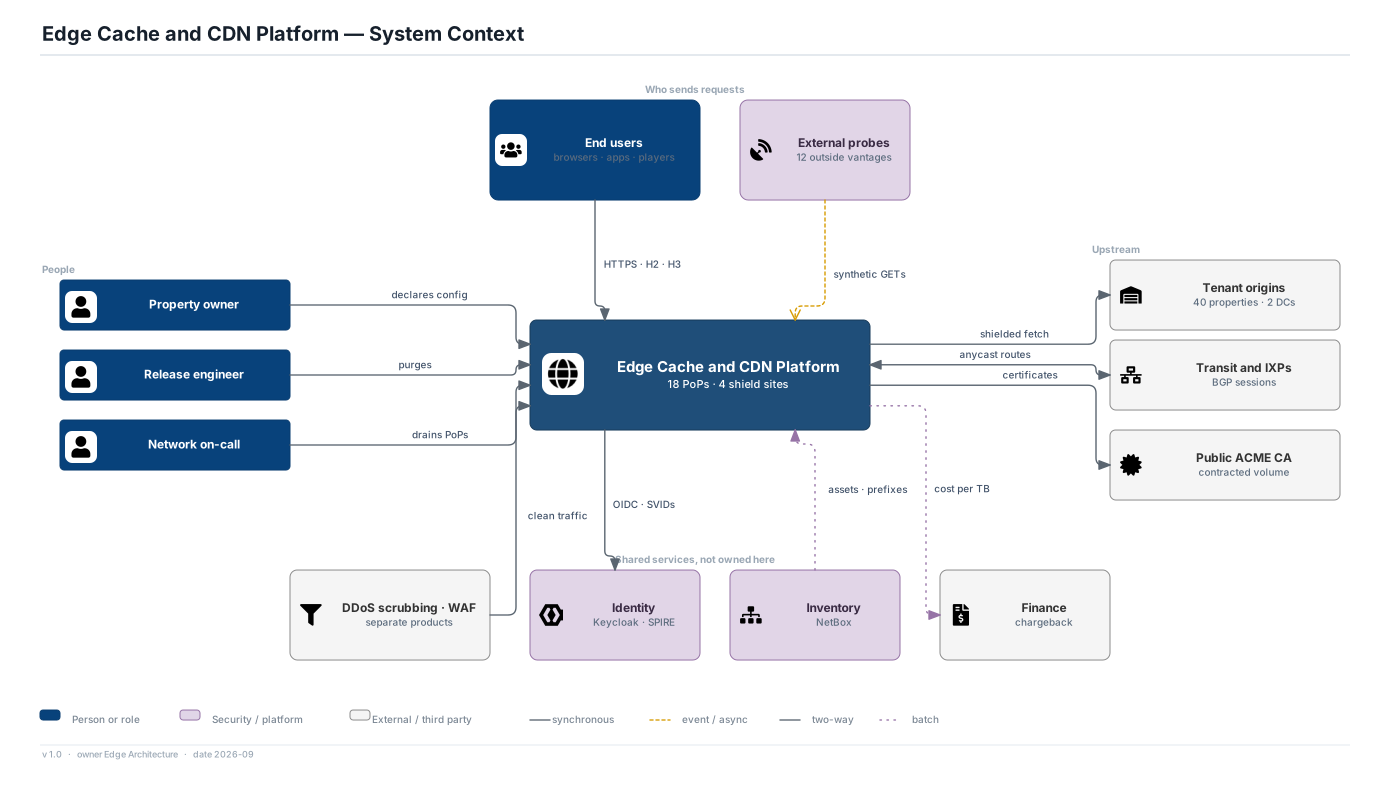
- Origins are drawn outside the boundary. The platform consumes them and protects them; it never designs them, and a property whose origin cannot answer a conditional request is still onboarded, just with a lower offload.
- DDoS scrubbing and WAF are separate products that hand clean traffic back. The edge enforces its own per-property ceilings so an attack that passes scrubbing still meets a limit.
- External probes sit outside the boundary on purpose. A platform that only measures itself cannot see the request that never reached it.
Assumptions
- 40 properties owned by business units of one organisation, 250,000 requests per second and 400 Gbps at peak, 900 million cacheable objects with a 40 KB median.
- Origins live in two organisation-owned data centres, one in the eastern US and one in Frankfurt. The requirement placed them in a public cloud; here they are on-premises like everything else.
- Keycloak, SPIRE, NetBox and the paging stack already exist and are operated by other teams.
Out of scope
- Edge compute and personalisation, video packaging and DRM, and peering commercials. Each is named in the roadmap or left to its owner.