Cloud Development Environment Platform · View 10 of 21 · Data
Decisions
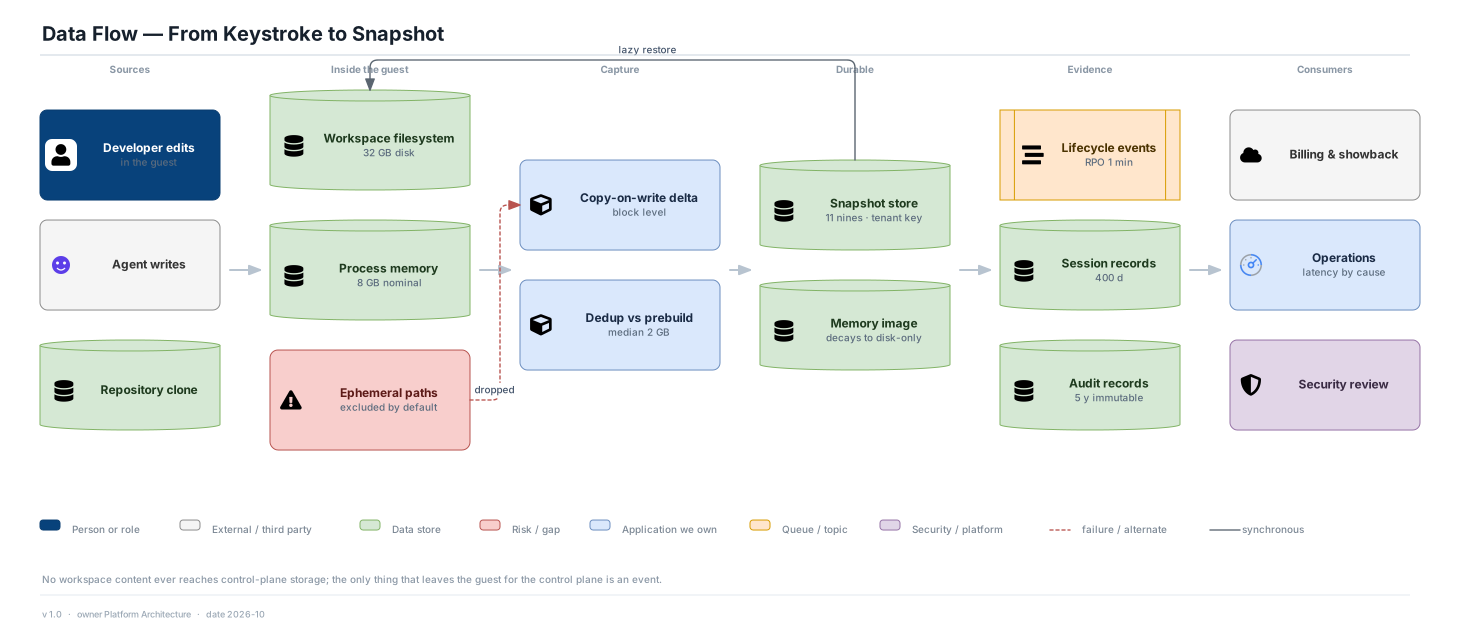
- Declared ephemeral paths — /tmp, package and build caches — are excluded from the persisted delta by default, because paying to store a rebuildable cache twice a day is the easiest money the platform can waste.
- The snapshot delta is deduplicated against the prebuild it derives from, so the stored bytes approximate the developer's work rather than the image.
- The only thing that leaves the guest for the control plane is an event. Content goes to the snapshot store, under a tenant-scoped key.
Assumptions
- Median persisted delta ≤ 2 GB compressed, p95 ≤ 9 GB, 180 TB of new snapshot data per day.
- Session, command and egress records 400 days; audit 5 years, immutable; raw telemetry 14 days.
Risks
- A tenant whose build writes into a persisted path can quietly multiply storage cost; the exclusion list is overridable, which makes it a support burden as well as a feature.
- Command and egress records are close to a developer's keystrokes. The retention is defensible only while the purpose is stated and the access is audited.