Audit Log Service · View 36 of 40 · 7 · Assurance
Decisions
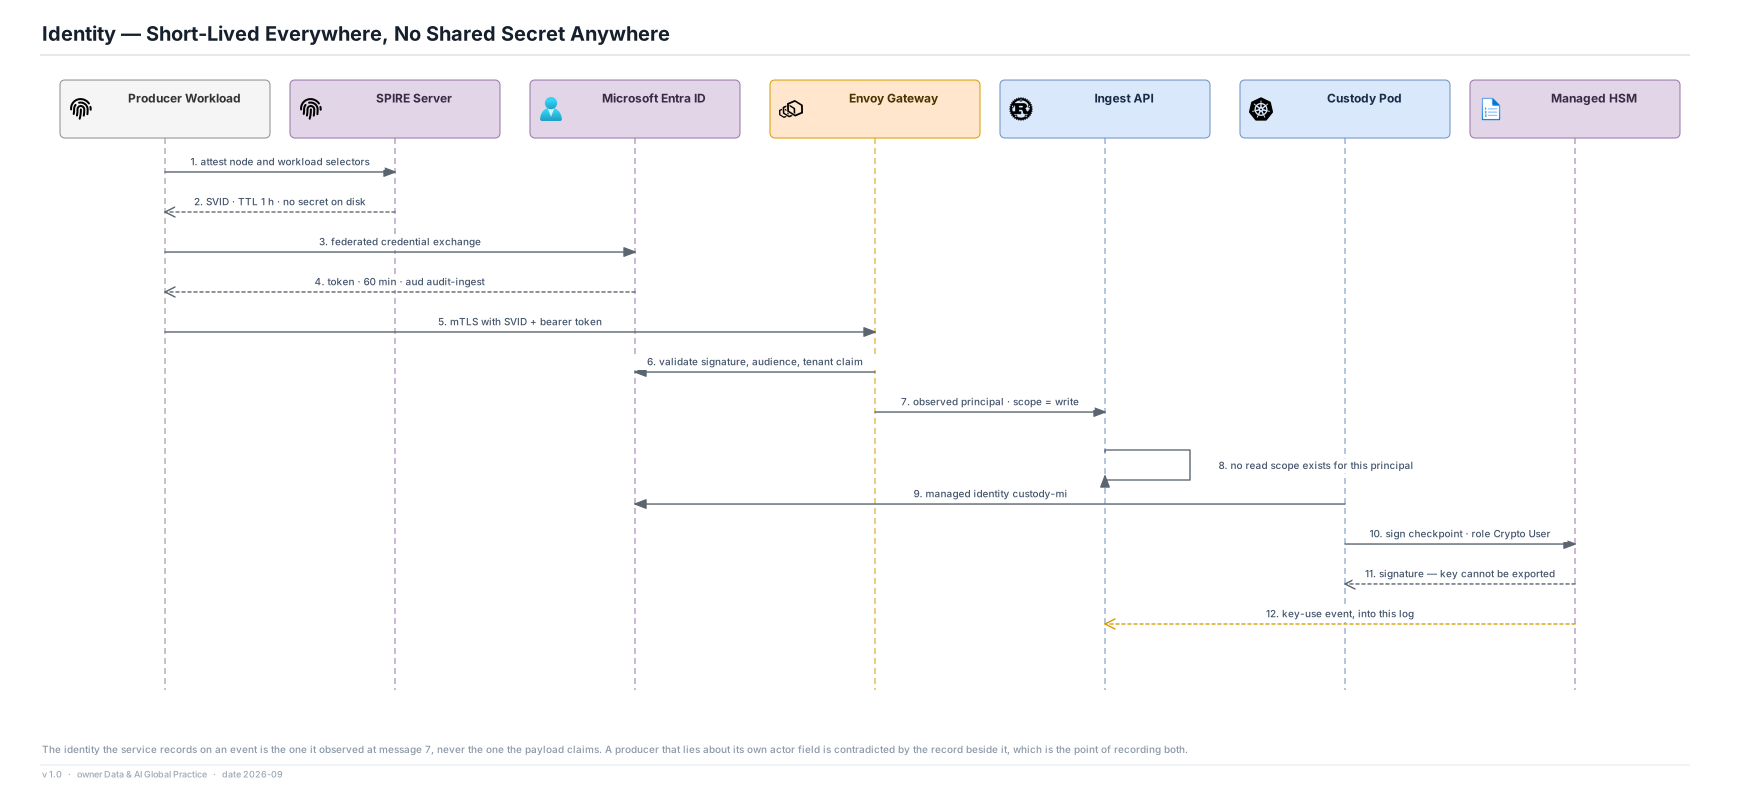
- No long-lived shared secret exists anywhere on the ingest path. Azure workloads use workload identity federation; non-Azure producers get a SPIFFE SVID from SPIRE with a one-hour TTL.
- The identity written on an event is the one observed at the gateway, not the one asserted in the payload. Both are kept — a producer lying about its own actor field is precisely the event worth having.
- Producer credentials carry a write scope and no read scope. There is no read scope that can be granted to a producer principal, so the misconfiguration is unavailable rather than merely forbidden.
Separation in practice
- Five workload identities, one per plane, each with the narrowest Azure RBAC role that lets it do its job: create-only on the segment container for the sealer, read-only for the verifier, Crypto User on one key for the signer.
- Human access is through Entra PIM with time-boxed elevation and approval; standing membership of the custody groups is empty.
- Every HSM key use emits an event into this log, including the ones performed under break-glass.
Risks
- SPIRE is another trust root to run, and its node attestation is the weakest link for off-Azure producers. Where possible, producers are onboarded through Entra federation instead and SPIRE is reserved for the on-premises estate.