Audit Log Service · View 06 of 40 · 2 · People and journeys
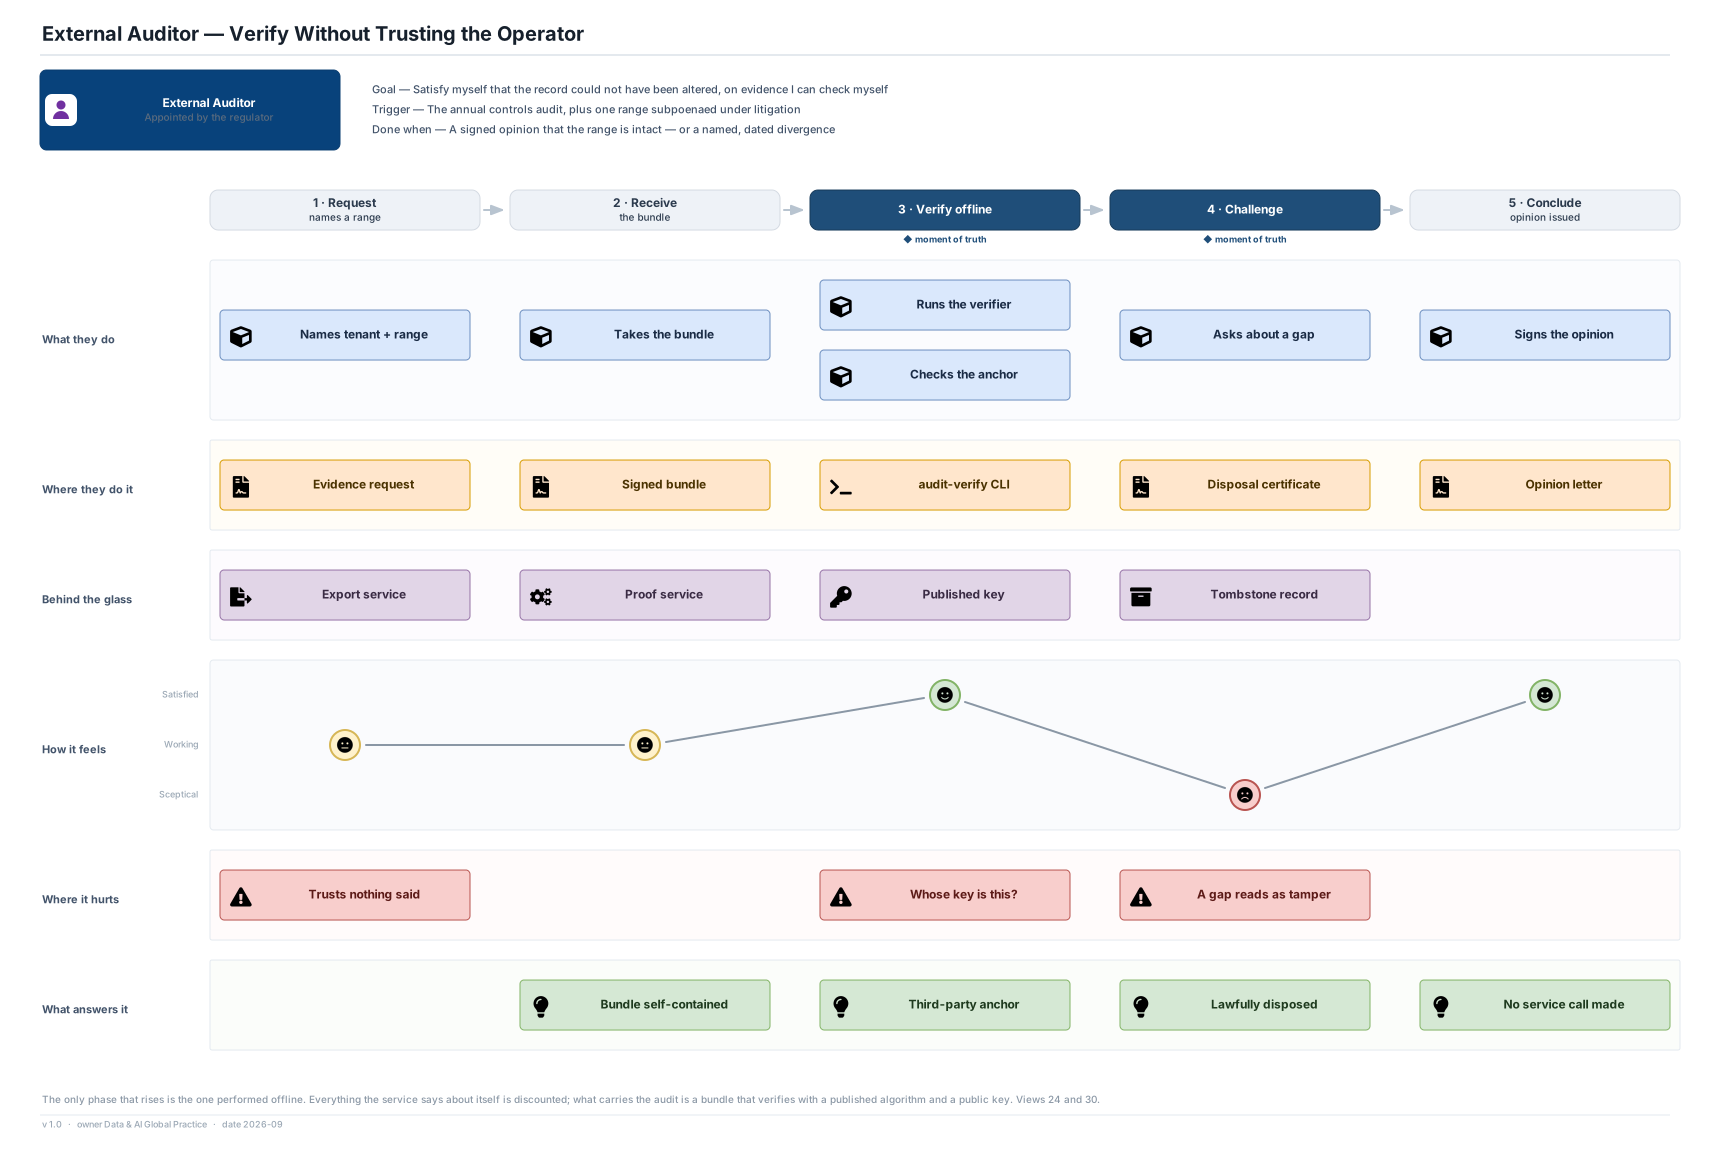
The trough, and its answer
- The low point is Challenge: the auditor hits a range where records have been disposed of, and a gap in a hash chain is indistinguishable from a deletion unless the design anticipated it.
- Answered by the tombstone: the segment bytes go, the Merkle root and the signed disposal certificate stay in the chain, and verification reports 'lawfully disposed under certificate X' rather than 'broken here'. Views 16 and 25.
- The rising phase is Verify offline, because it is the only one that does not depend on this organisation being honest.
What makes the bundle stand alone
- Records, covering checkpoints, inclusion proofs, segment hashes and the export's own manifest, signed by a key whose public half is published and anchored.
- A published algorithm and a single-binary verifier, so the auditor runs it on an air-gapped laptop and contacts nothing.
- Phase 3 adds a third-party witness anchor, which removes the last dependency on this organisation entirely.
Risks
- Until the witness anchor ships, 'whose key is this?' is answered by our own key transparency record and the external TSA countersignature. That is strong, and it is not the same as an independent witness.