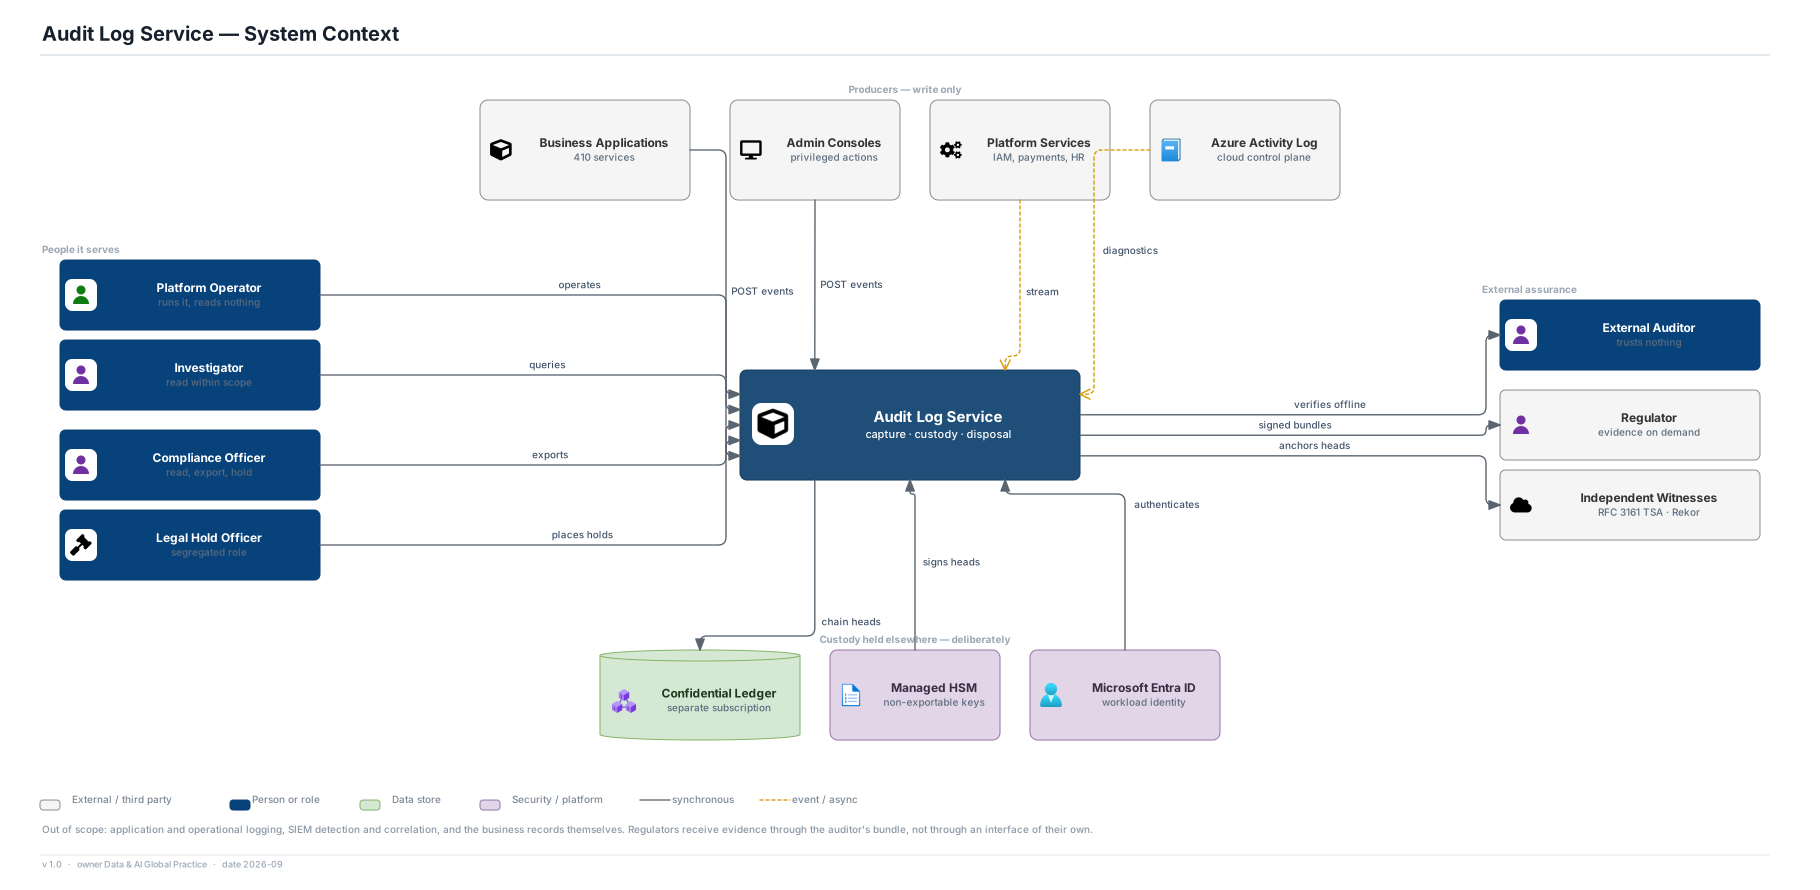
Audit Log Service · View 01 of 40 · 1 · Context and scope
Decisions
- This is not application logging. Operational logs may be sampled, rewritten and dropped; nothing here may be, and conflating the two is the failure this service exists to prevent.
- The checkpoint ledger and the signing key sit outside the service's own subscription and under different administrators. That is not defence in depth, it is the mechanism: no single compromised administrator can rewrite both the records and the evidence about the records.
- Producers are write-only at the interface level. There is no read scope a producer credential can be granted.
Stack — retargeted
- The requirement names Amazon Web Services; this architecture is built on Microsoft Azure and open source at the sponsor's direction.
- Substitutions: S3 Object Lock → Blob immutable containers with a locked time-based retention policy; Kinesis → Apache Kafka (Strimzi on AKS); KMS/CloudHSM → Key Vault Managed HSM; Athena → Trino; OpenSearch → ClickHouse; QLDB → Azure Confidential Ledger.
- The requirement was written to survive a change of cloud, and it did: only technology names moved, no property did.
Assumptions
- 500 tenants, 410 producing services, ~2.2 billion events/day, 25 k/s steady and 100 k/s burst — all as stated in the requirement.
- The timestamp authority is an external commercial TSA, not one this organisation runs; a TSA we operate would defeat the point of having one.
- Regulators receive evidence through the auditor's bundle rather than through an interface of their own.