URL Shortener & Link Management Service  ·  View 22 of 23  ·  Assurance

Security Trust Zones

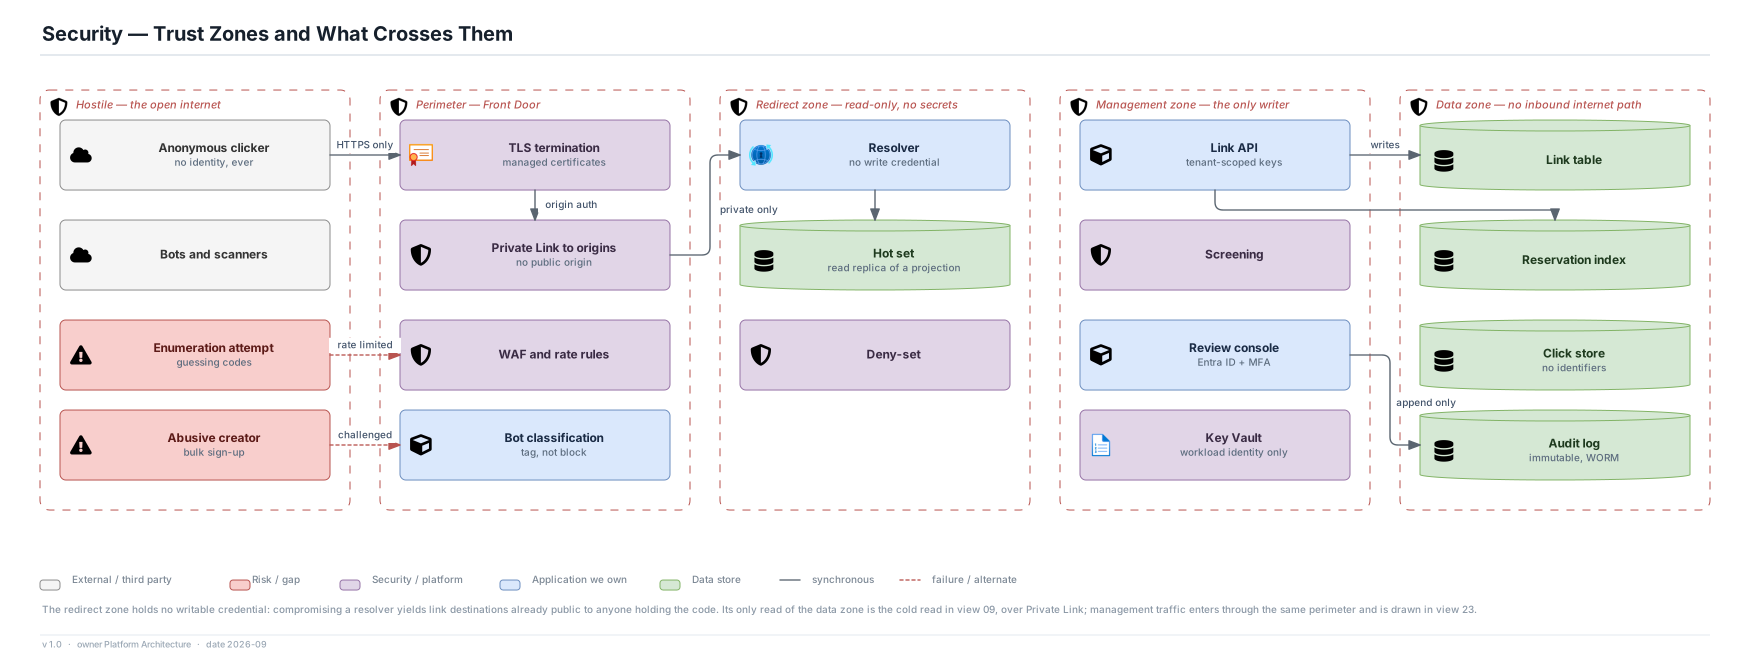
Five zones, and a redirect plane that holds no writable credential of any kind.

Editable source SVG draw.io All views
Hostile — the open internet Anonymous clicker no identity, ever Bots and scanners Enumeration attempt guessing codes Abusive creator bulk sign-up Perimeter — Front Door TLS termination managed certificates Private Link to origins no public origin WAF and rate rules Bot classification tag, not block Redirect zone — read-only, no secrets Resolver no write credential Hot set read replica of a projection Deny-set Management zone — the only writer Link API tenant-scoped keys Screening Review console Entra ID + MFA Key Vault workload identity only Data zone — no inbound internet path Link table Reservation index Click store no identifiers Audit log immutable, WORM HTTPS only rate limited challenged origin auth private only writes append only Security — Trust Zones and What Crosses Them External / third party Risk / gap Security / platform Application we own Data store synchronous failure / alternate The redirect zone holds no writable credential: compromising a resolver yields link destinations already public to anyone holding the code. Its only read of the data zone is the cold read in view 09, over Private Link; management traffic enters through the same perimeter and is drawn in view 23. v 1.0 · owner Platform Architecture · date 2026-09

The containment argument

  • Compromising a resolver yields the ability to read link destinations, which are already available to anyone who holds the code. It yields no write path and no secret.
  • Origins are reachable only over Private Link from Front Door; there is no public origin address to find.
  • The data zone has no inbound internet path at all, and the audit store is write-once.

Threats this design names

  • Code enumeration: answered by unguessable 7-character codes on shared domains plus perimeter rate limiting, and by the negative cache so enumeration is cheap to serve.
  • Abusive creation at volume: answered by challenges and quotas on new or unverified accounts, which is where abusive links come from.
  • The platform as an open redirect: destinations only ever come from a stored record, never from a query parameter (ADR-14 and the requirement's §9).

Omitted

  • Key rotation schedules, WAF rule inventory and the DDoS posture are operational documents; this view is about which boundary holds when a control fails.