Secrets Distribution Service  ·  View 04 of 34  ·  2 · People and journeys

Journey — Ship With No Stored Password

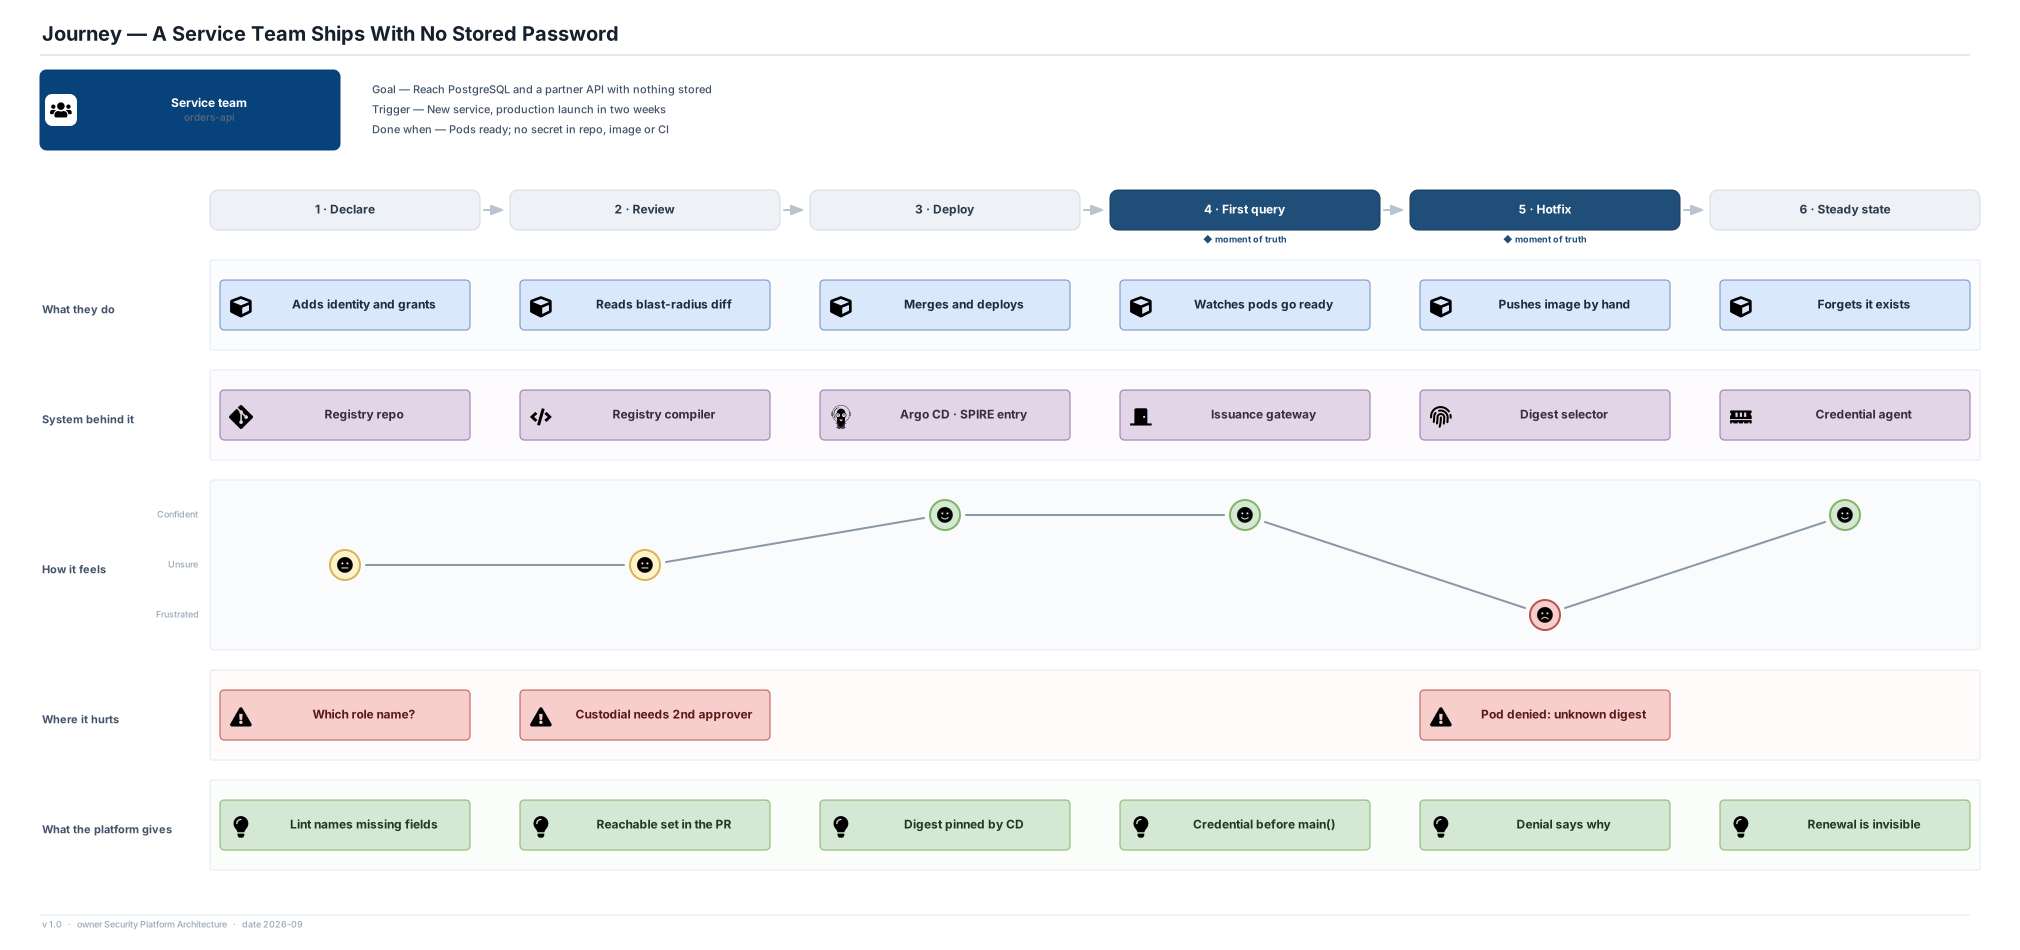
A service team takes orders-api to production with a PostgreSQL role and a partner key, and nothing written anywhere a human or a build can read.

Editable source SVG draw.io All views
Service team orders-api Goal — Reach PostgreSQL and a partner API with nothing stored Trigger — New service, production launch in two weeks Done when — Pods ready; no secret in repo, image or CI 1 · Declare 2 · Review 3 · Deploy 4 · First query ◆ moment of truth 5 · Hotfix ◆ moment of truth 6 · Steady state What they do Adds identity and grants Reads blast-radius diff Merges and deploys Watches pods go ready Pushes image by hand Forgets it exists System behind it Registry repo Registry compiler Argo CD · SPIRE entry Issuance gateway Digest selector Credential agent How it feels Confident Unsure Frustrated Where it hurts Which role name? Custodial needs 2nd approver Pod denied: unknown digest What the platform gives Lint names missing fields Reachable set in the PR Digest pinned by CD Credential before main() Denial says why Renewal is invisible Journey — A Service Team Ships With No Stored Password v 1.0 · owner Security Platform Architecture · date 2026-09

The trough

  • A hotfix image pushed outside the delivery pipeline has a digest the identity entry does not know, so the pod is refused a credential. This is the design working, and it will not feel like it at 02:00.
  • Answer: the refusal names the missing selector and the pipeline that would have registered it (view 16). The break-glass path for a digest is the pipeline itself, run with approval waived for a declared incident, never an identity created by hand.

What makes the rest quiet

  • The registry lint rejects a grant with no owner, a wildcard or a mismatched environment before review. The pull request shows the identity's complete reachable set, so the reviewer approves a list, not a policy language.
  • Renewal is the agent's problem. The team's code reads a local socket and never sees an address, a token or a schedule.

Targets

  • Credential available before main() runs: attestation p99 ≤ 400 ms, mint p99 ≤ 500 ms. Second approval for production custodial grants within four working hours.