Passkey Authentication Service · View 20 of 21 · Assurance
Decisions
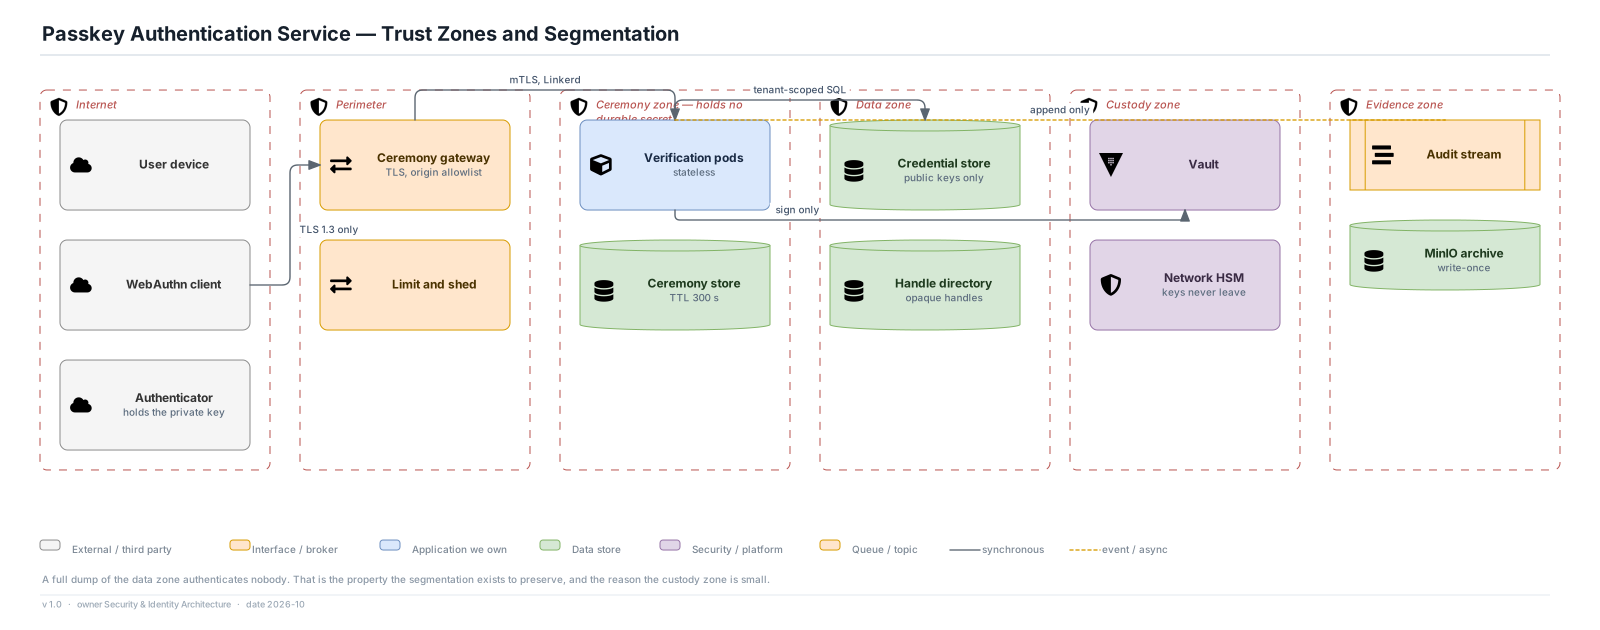
- A full dump of the data zone authenticates nobody. The platform holds public keys and verification material only, which is the single strongest security property in the design and the reason the custody zone can stay small.
- The ceremony zone holds no durable secret, so its blast radius is one five-minute window of in-flight logins.
- The custody zone signs and never exports. There is no key backup, because a key that can be restored is a key that can be stolen from a restore.
- Origin and RP ID are checked at the perimeter and re-checked against the tenant allowlist server-side, regardless of what the request's own headers claim.
Failure handling
- Credential store unreachable: fail closed. The platform does not authenticate from cache.
- Metadata service unreachable: fail static on the last signed snapshot, with the staleness recorded on any verdict it admits.
- Risk engine unreachable: fail open, verdict marked unevaluated.
- Ceremony store partition: in-flight ceremonies fail closed with a distinct restart-the-ceremony error rather than a generic failure.
Accepted residual risk
- A compromised verification replica can issue challenges and read credential public keys for its tenant's traffic; it cannot forge an assertion or sign a verdict without the HSM.
- A tenant whose only recovery route is an out-of-band channel has an account assurance ceiling set by that channel, and no zone boundary changes that.