No-Code SaaS Automation Platform · View 01 of 21 · Context and scope
Decisions
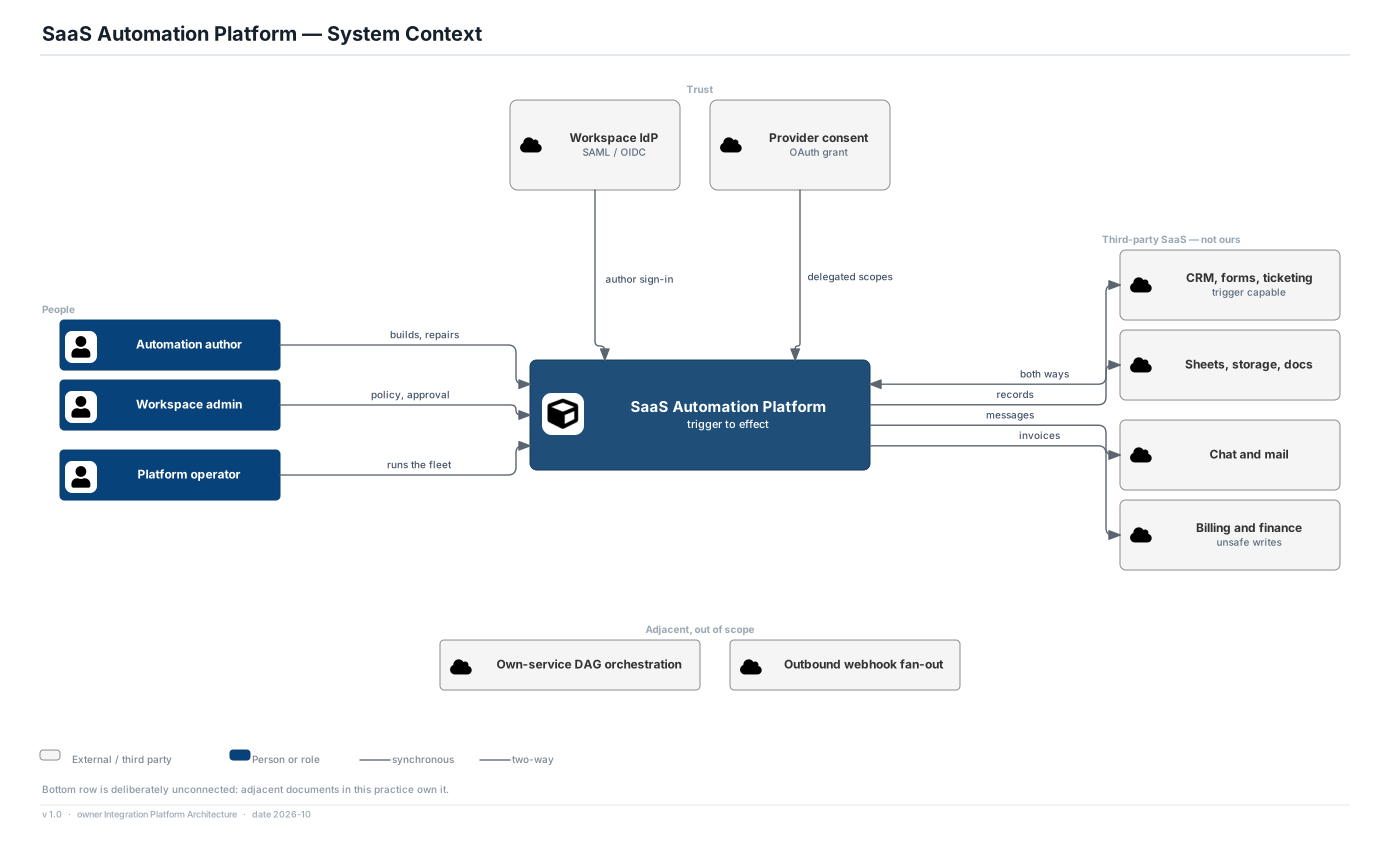
- Providers are drawn as classes, not brands: the architecture turns on a provider's capabilities — can it push, does it honour an idempotency key — not on its logo.
- Billing and finance is called out as an unsafe-write class because that single property changes the execution guarantee the platform can offer.
- The workspace identity provider and the provider OAuth consent screen are both external: the platform authenticates authors and acts for them, but owns neither trust root.
Scope boundary
- In: trigger ingestion, the automation definition, durable step execution, credential custody, quota governance, and failure legibility.
- Out, and unconnected on purpose: DAG orchestration of our own services, outbound webhook fan-out to subscribers, and standalone request dedup — each an adjacent document in this practice.
Risks
- The platform's reputation is made of other people's uptime; an author attributes a provider outage to us.
- Holding delegated credentials for 2.5 M workspaces makes this platform a high-value target for reasons unrelated to its own data.