File Upload & Scanning Pipeline  ·  View 21 of 21  ·  Assurance

Identity & Credential Flow

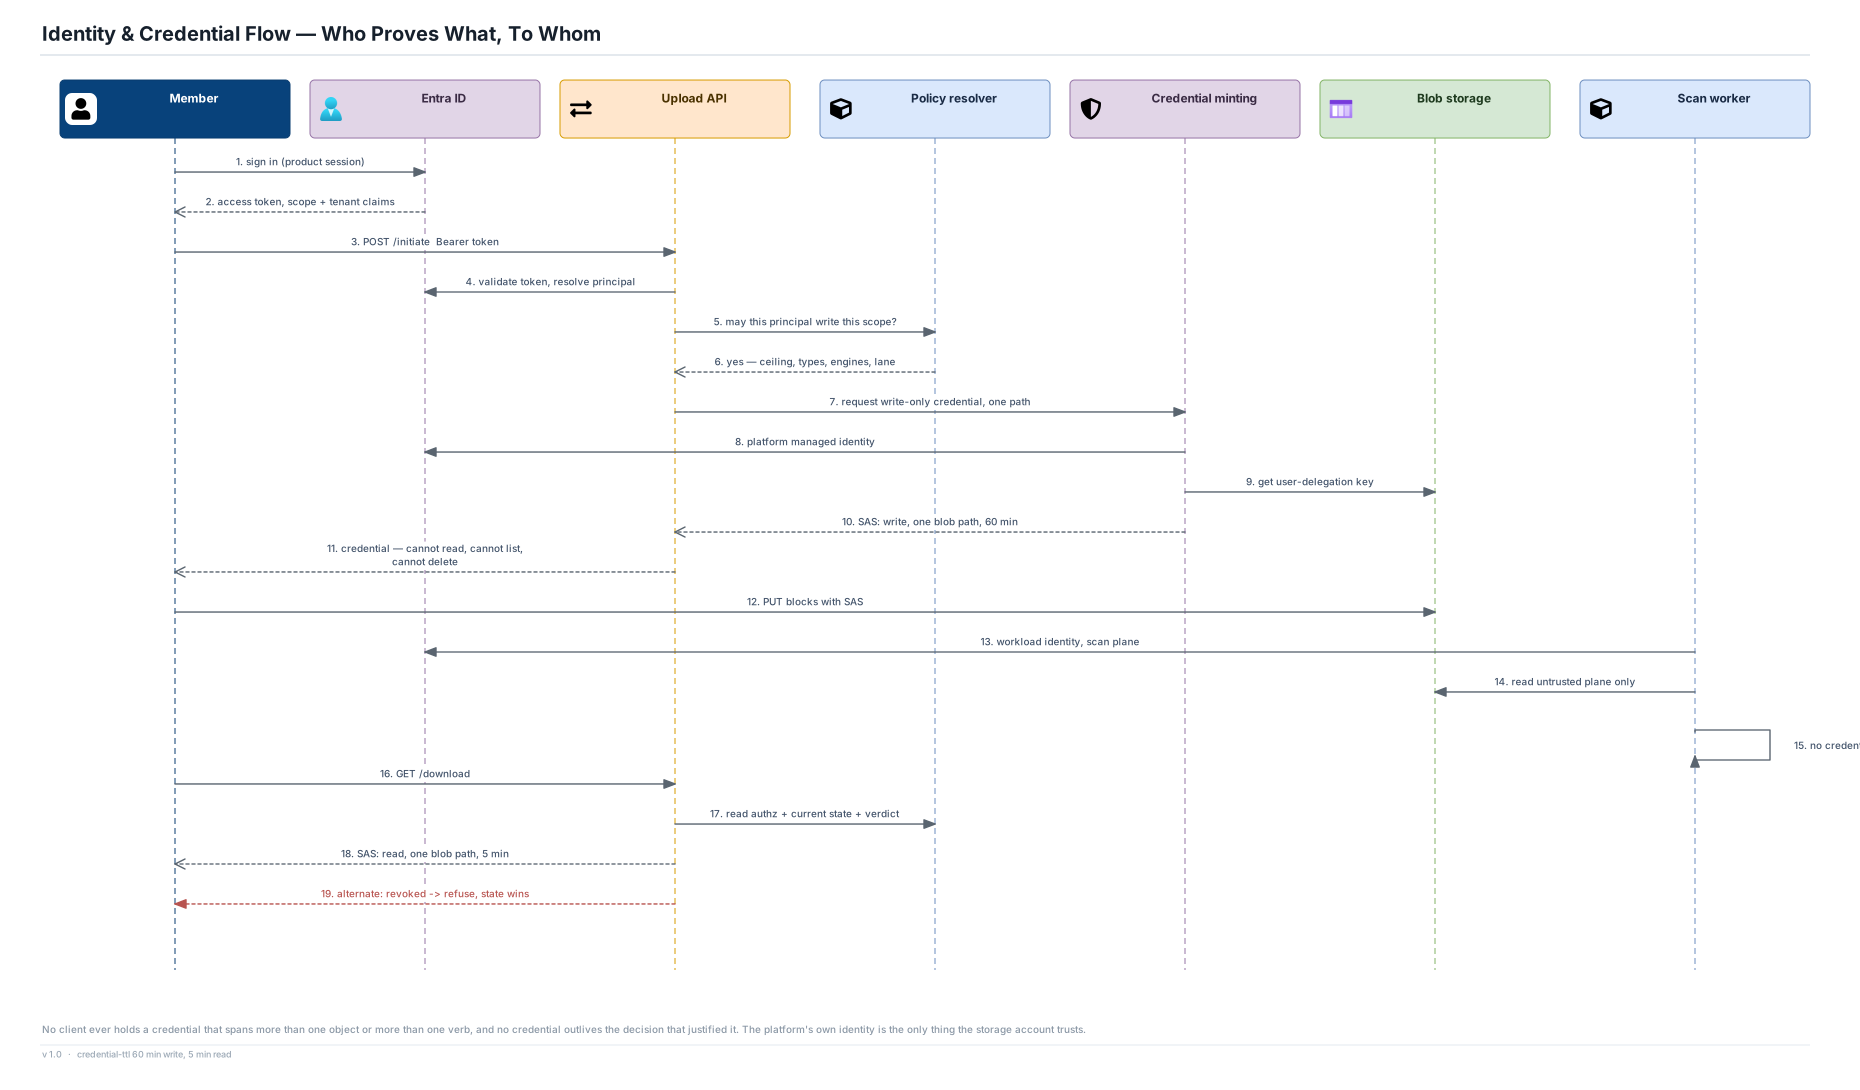
Nineteen messages establishing that no credential outlives the decision that justified it.

Editable source SVG draw.io All views
Member Entra ID Upload API Policy resolver Credential minting Blob storage Scan worker 1. sign in (product session) 2. access token, scope + tenant claims 3. POST /initiate Bearer token 4. validate token, resolve principal 5. may this principal write this scope? 6. yes — ceiling, types, engines, lane 7. request write-only credential, one path 8. platform managed identity 9. get user-delegation key 10. SAS: write, one blob path, 60 min 11. credential — cannot read, cannot list, cannot delete 12. PUT blocks with SAS 13. workload identity, scan plane 14. read untrusted plane only 15. no credential able to change state 16. GET /download 17. read authz + current state + verdict 18. SAS: read, one blob path, 5 min 19. alternate: revoked -> refuse, state wins Identity & Credential Flow — Who Proves What, To Whom No client ever holds a credential that spans more than one object or more than one verb, and no credential outlives the decision that justified it. The platform's own identity is the only thing the storage account trusts. v 1.0 · credential-ttl 60 min write, 5 min read

Decisions

  • The storage account trusts only the platform's own identity; every client credential is derived from it, scoped to one object path and one verb
  • No long-lived or account-wide storage key is ever handed to a client, and no credential spans two objects
  • The scan plane holds a workload identity that can read the untrusted plane and write verdicts — and nothing that can change a lifecycle state

What this makes impossible

  • Enumerating another tenant's objects with a leaked upload credential, because the credential names one path and grants no list
  • Reading an object you uploaded but were never authorised to read, because read authorisation is evaluated at download time against current state
  • Keeping access after a revocation for longer than the credential's 5 minutes

Stated assumptions

  • Entra ID is the identity provider for both workforce and customer identities
  • User-delegation SAS, derived from the platform's managed identity, is the credential mechanism
  • Customer-managed keys available to tenants that require them