File Upload & Scanning Pipeline · View 09 of 21 · Structure
Decisions
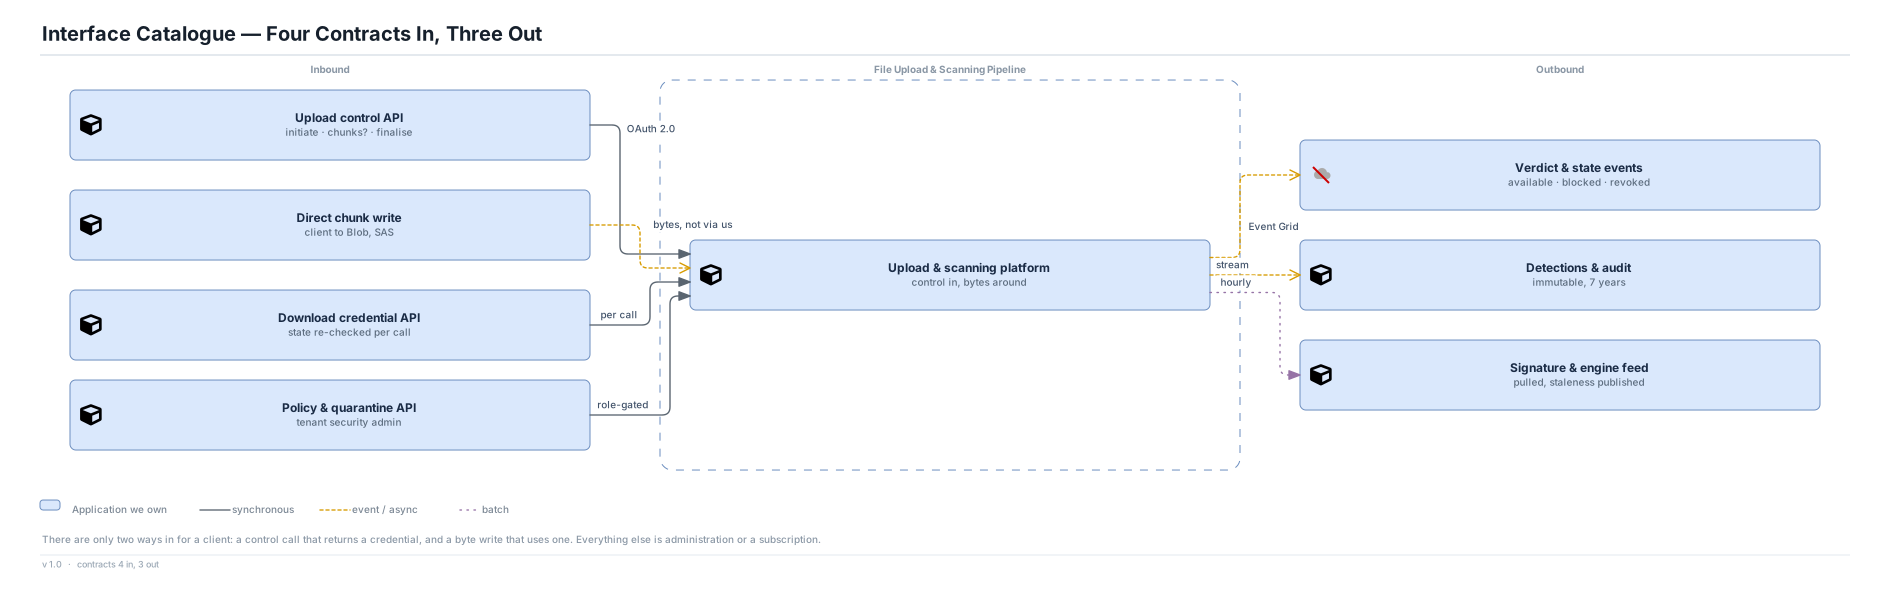
- There are exactly two ways in for a client: a control call that returns a credential, and a byte write that uses one — everything else is administration or a subscription
- The byte-write contract is with the object store, not with this platform: the platform's obligation is the credential's scope and lifetime, and nothing about the transfer itself
- Verdict events are the integration surface for every downstream consumer, so a product surface learns an attachment became available without polling
Interface rules
- Every inbound call is authenticated as a workload or end-user identity and authorised against the destination scope; there is no unauthenticated path that yields a credential
- The signature feed is pulled, never pushed, and its staleness is published — an object scanned under a set older than the declared age is marked for re-scan rather than trusted
- Audit and detections leave as an append-only stream, retained 7 years, and never as a mutable report
Deliberately omitted
- A streaming upload gateway — the alternative in Question 1, kept off this catalogue as a consequence of the direct-to-store decision
- Key operations and identity, which are dependencies rather than contracts this platform publishes