Feature Store · View 20 of 21 · Assurance
Decisions
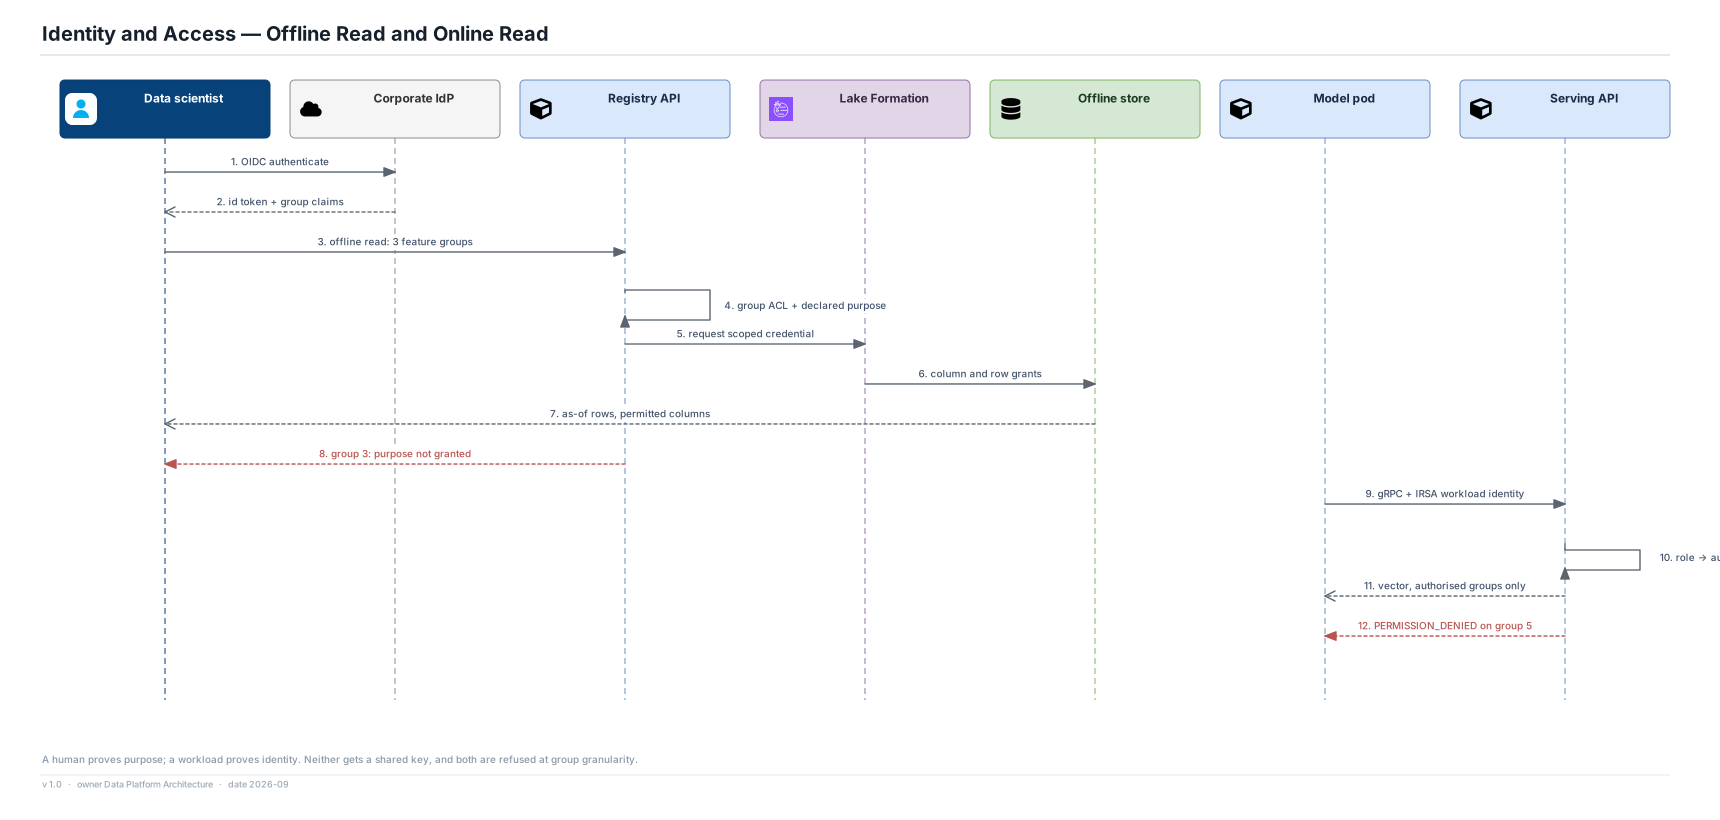
- No shared API keys for service-to-service reads. Every caller is a workload identity, and authorisation is evaluated per feature group.
- A human's offline read is authorised on group ACL plus declared purpose, and the credential Lake Formation issues is scoped to the columns that survive both checks.
- A denied group is refused explicitly and by name, not silently dropped from the vector — a silently narrower vector is a silent accuracy change.
Assumptions
- IRSA for workload identity on EKS; corporate OIDC for people; grants expire and must be renewed.
Risks
- Group-granularity authorisation means a consumer authorised for a group is authorised for every feature in it. Splitting a group is the only way to narrow that, which pushes access control into the data model.