Cloud Development Environment Platform  ·  View 08 of 21  ·  Structure

Platform Components

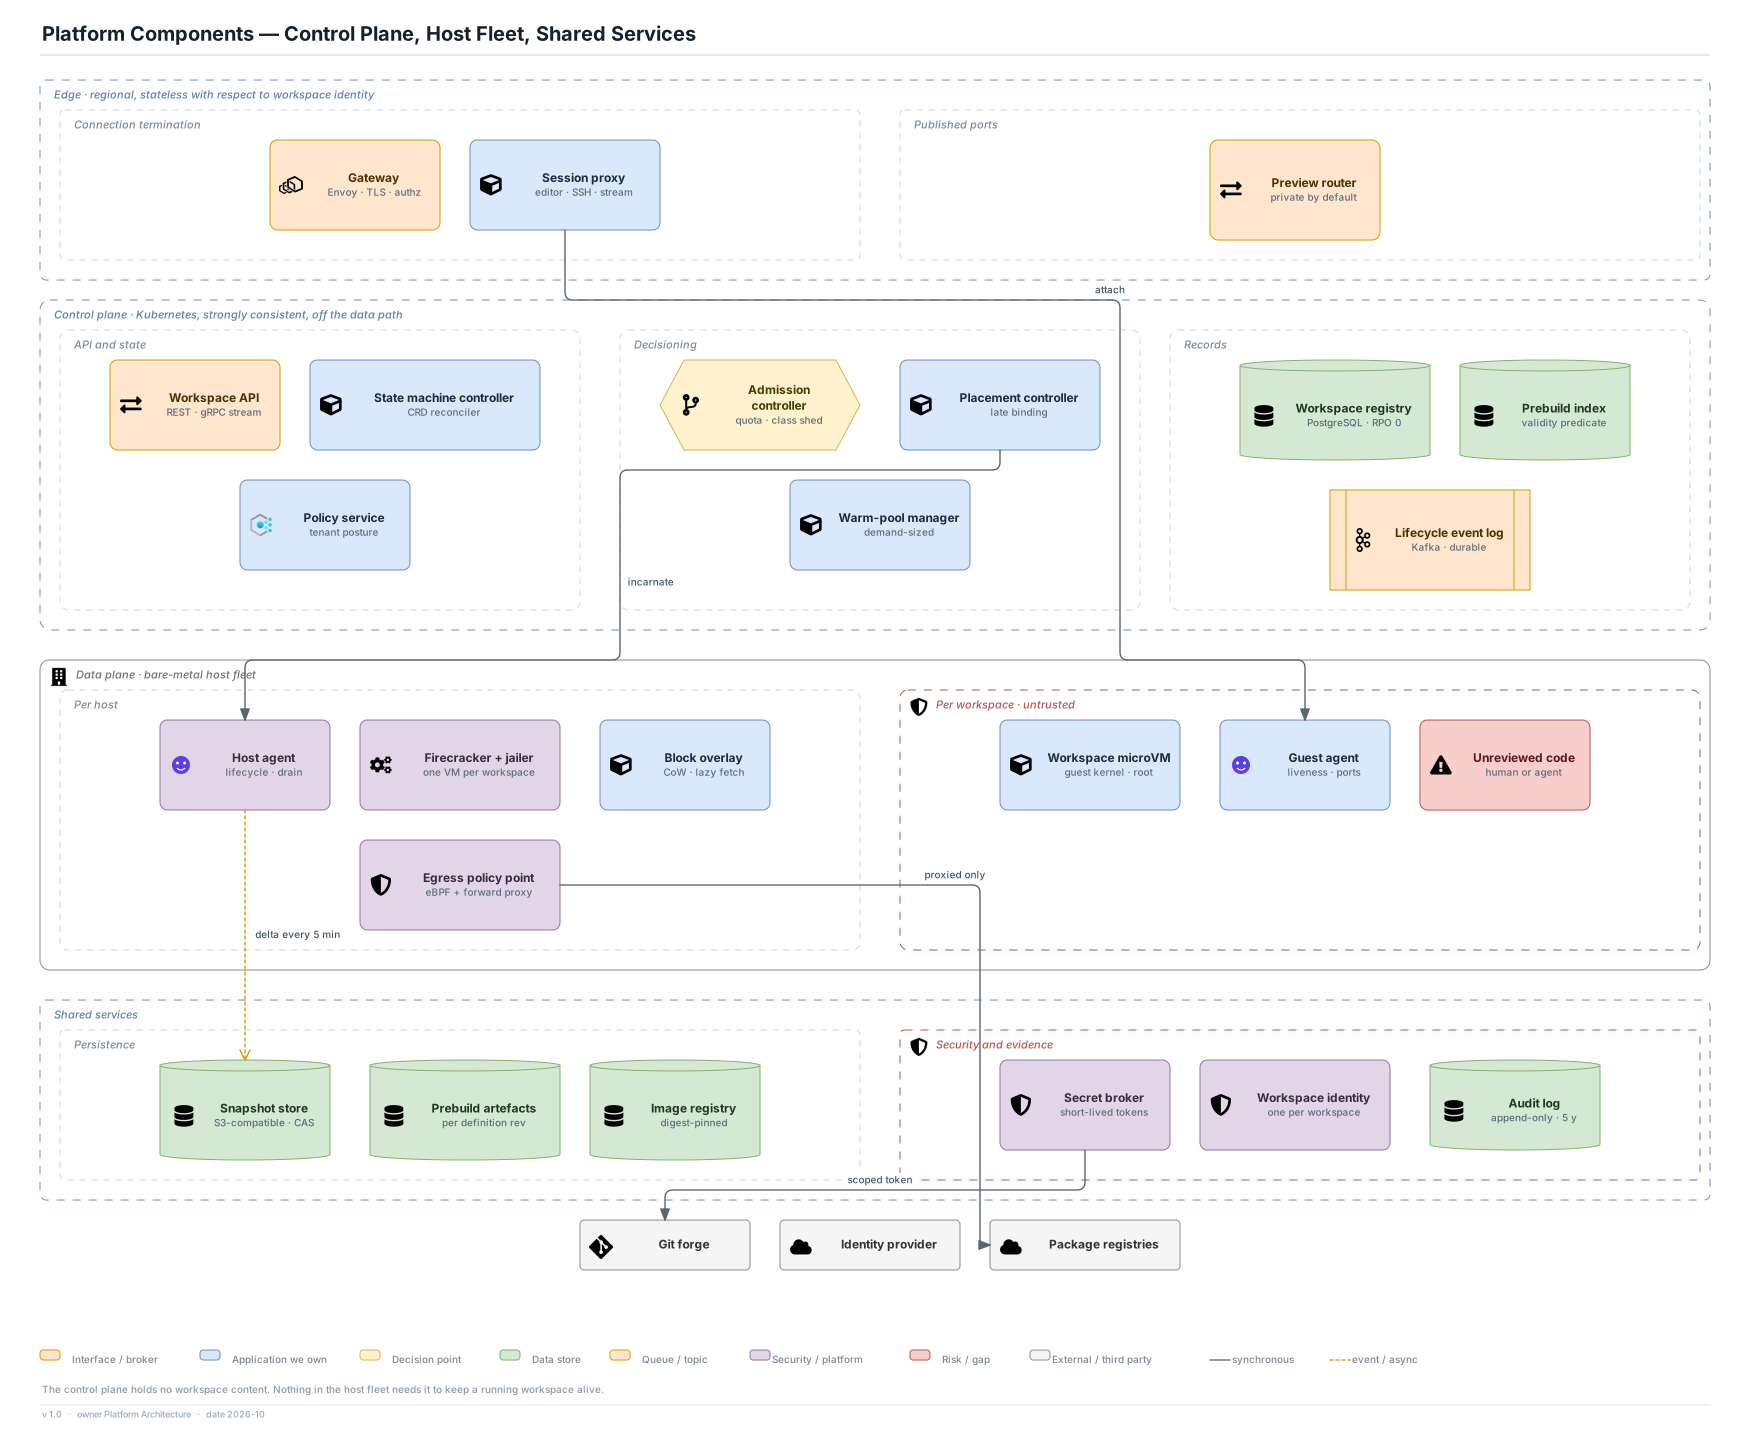
What is stateless, what is region-pinned, what is untrusted, and what holds a key.

Editable source SVG draw.io All views
Edge · regional, stateless with respect to workspace identity Connection termination Gateway Envoy · TLS · authz Session proxy editor · SSH · stream Published ports Preview router private by default Control plane · Kubernetes, strongly consistent, off the data path API and state Workspace API REST · gRPC stream State machine controller CRD reconciler Policy service tenant posture Decisioning Admission controller quota · class shed Placement controller late binding Warm-pool manager demand-sized Records Workspace registry PostgreSQL · RPO 0 Prebuild index validity predicate Lifecycle event log Kafka · durable Data plane · bare-metal host fleet Per host Host agent lifecycle · drain Firecracker + jailer one VM per workspace Block overlay CoW · lazy fetch Egress policy point eBPF + forward proxy Per workspace · untrusted Workspace microVM guest kernel · root Guest agent liveness · ports Unreviewed code human or agent Shared services Persistence Snapshot store S3-compatible · CAS Prebuild artefacts per definition rev Image registry digest-pinned Security and evidence Secret broker short-lived tokens Workspace identity one per workspace Audit log append-only · 5 y Git forge Identity provider Package registries attach incarnate delta every 5 min proxied only scoped token Platform Components — Control Plane, Host Fleet, Shared Services Interface / broker Application we own Decision point Data store Queue / topic Security / platform Risk / gap External / third party synchronous event / async The control plane holds no workspace content. Nothing in the host fleet needs it to keep a running workspace alive. v 1.0 · owner Platform Architecture · date 2026-10

Decisions

  • The control plane holds records, not content: a workspace registry, a prebuild index and an event log. No filesystem data, memory image or log transits control-plane storage (ADR-12).
  • The host agent owns the microVM, the block overlay and the egress policy point, so the enforcement point is on the host rather than in the guest — the guest agent is advisory only.
  • The secret broker and the workspace identity authority are separate from the control plane, so a management-plane outage cannot mint credentials and a broker compromise cannot change policy (ADR-05).

Assumptions

  • PostgreSQL for the registry with synchronous replicas (RPO 0); Kafka for the lifecycle stream (RPO 1 min).
  • One Firecracker microVM per workspace, 4 vCPU / 8 GB / 32 GB disk nominal, 40 per 128-core / 1 TB host at 4:1 memory oversubscription.

Risks

  • The host agent is the most privileged component in the system and it is adjacent to untrusted code; its attack surface toward the guest is the vsock channel and nothing else.
  • Oversubscription at 4:1 only holds while hibernation keeps working; a bug in idleness detection turns a cost assumption into a reliability incident.