CI/CD Platform · View 20 of 22 · Assurance
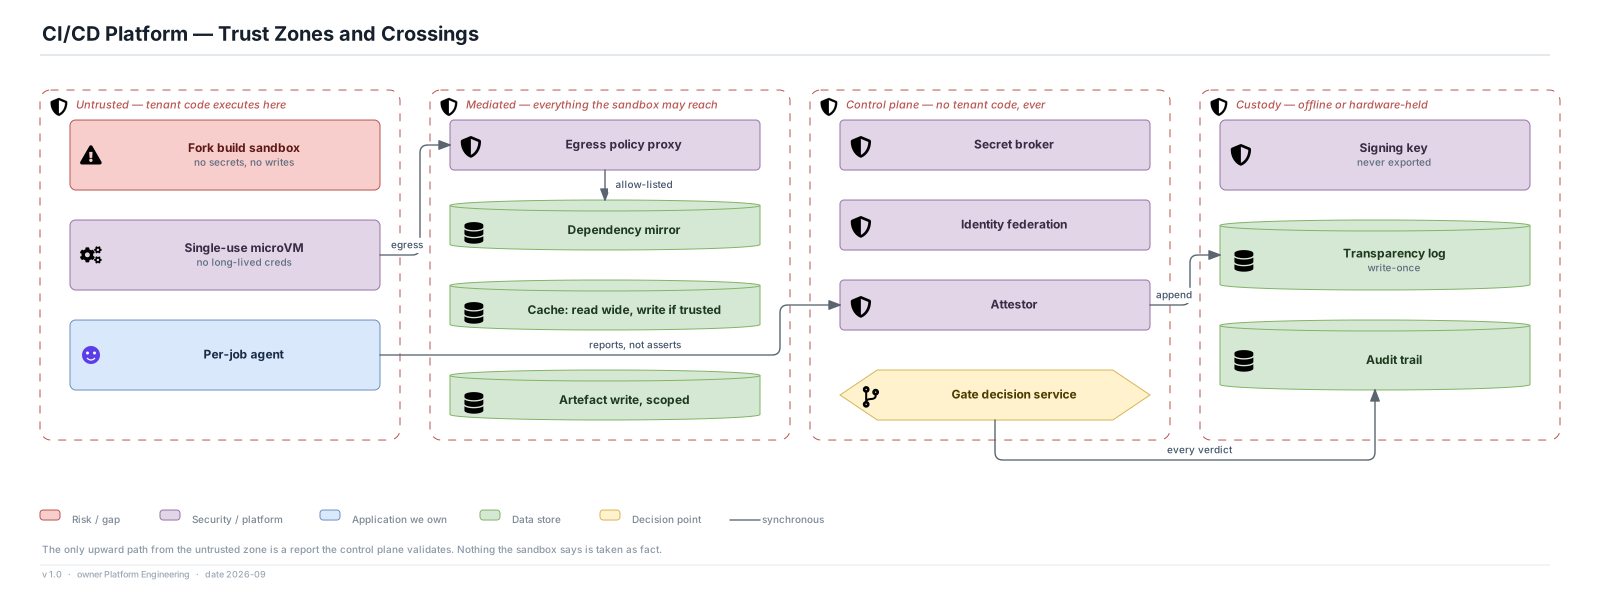
The boundary this set is built around
- Tenant code executes only in the untrusted zone, in a single-use sandbox holding no long-lived credential and no cross-tenant write authority.
- Everything that must be trusted — brokering a secret, signing provenance, deciding a gate, recording an outcome — happens in the control-plane zone, which never executes tenant code.
- The custody zone holds the signing key, the transparency log and the audit trail. Nothing in it is reachable from the execution plane by any path.
Realisation
- All sandbox egress is mediated by a policy proxy with a tenant allow-list, and every allowed and denied destination is logged against the run.
- The cache is read-wide and write-privileged: a fork build reads it and can never write it.
- Tenant storage isolation is by key prefix and credential, proved by continuous automated test rather than by review.
Risks
- A confused-deputy bug in the attestor would let one job's report be attributed to another's inputs. The attestor's input validation is the highest-value code in the platform and deserves the most review.