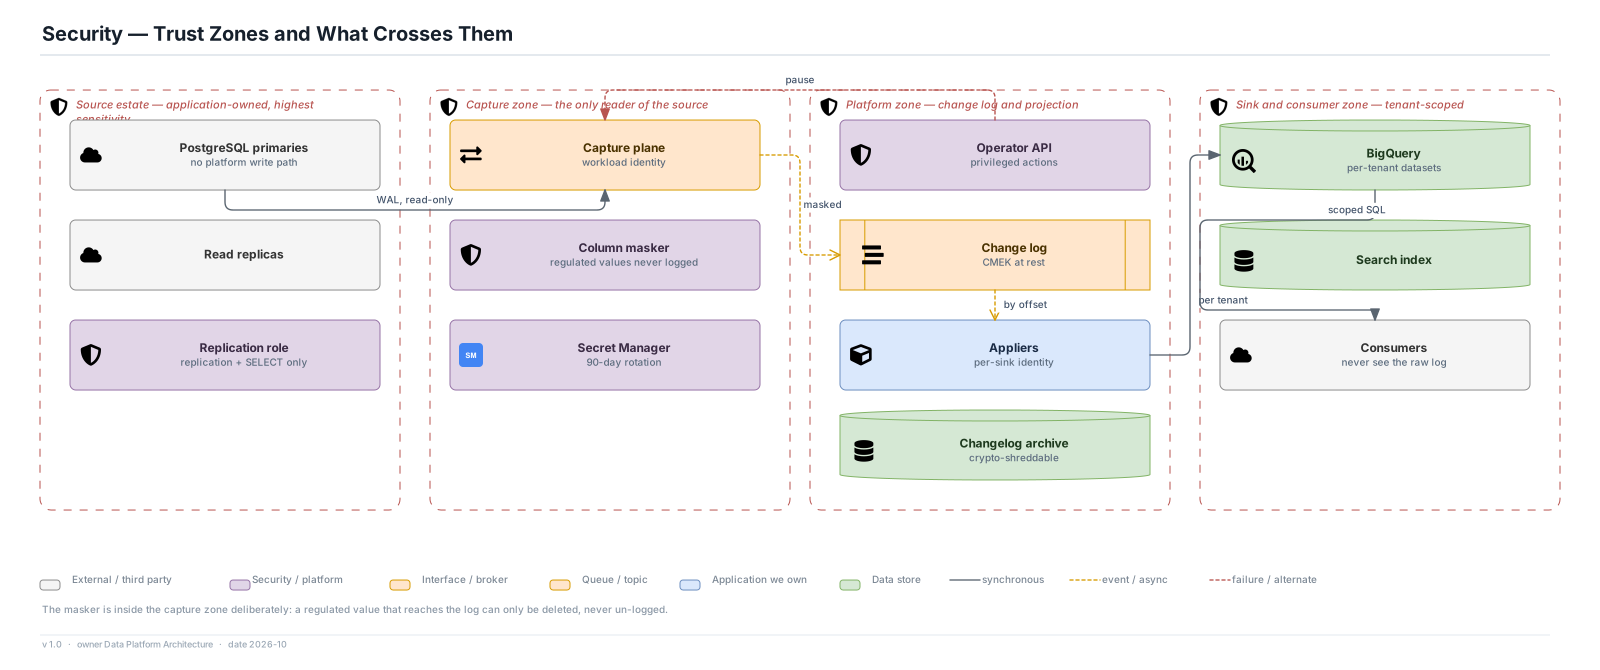
Change Data Capture Pipeline · View 19 of 21 · Assurance
Decisions
- Column masking happens at capture, before the log. A regulated value that reaches the log can only be deleted afterwards, never un-logged (ADR-07).
- The capture identity holds replication and SELECT only: this platform structurally cannot write to a source.
- Tenant isolation is enforced at the sink by per-tenant datasets, never by trusting a consumer's WHERE clause.
Assumptions
- Source credentials rotate at most every 90 days; the change log and archive are encrypted with customer-managed keys.
- Erasure in the archive is by crypto-shredding, which requires a per-subject key boundary decided in Phase 3.
Risks
- The archive is the longest-lived copy of personal data in the estate at 13 months; its erasure story is the weakest part of this design and is named as such.
- A masking rule added after a table is live does not retrospectively clean the log — it needs a re-snapshot and an archive rewrite.