API Key and Token Service  ·  View 09 of 22  ·  Act 3 · Structure

Integration Surface

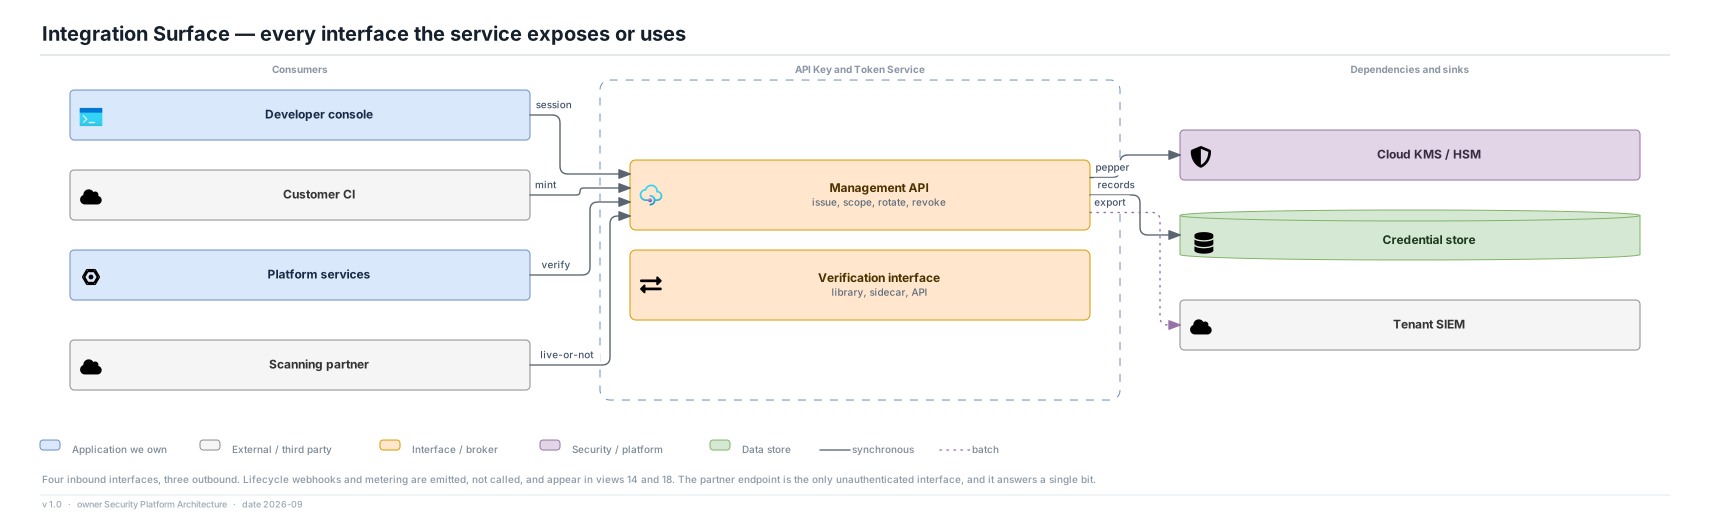
Four inbound interfaces, three outbound dependencies, and the one that is unauthenticated on purpose.

Editable source SVG draw.io All views
Consumers Developer console Customer CI Platform services Scanning partner API Key and Token Service Management API issue, scope, rotate, revoke Verification interface library, sidecar, API Dependencies and sinks Cloud KMS / HSM Credential store Tenant SIEM session mint verify live-or-not pepper records export Integration Surface — every interface the service exposes or uses Application we own External / third party Interface / broker Security / platform Data store synchronous batch Four inbound interfaces, three outbound. Lifecycle webhooks and metering are emitted, not called, and appear in views 14 and 18. The partner endpoint is the only unauthenticated interface, and it answers a single bit. v 1.0 · owner Security Platform Architecture · date 2026-09

Decisions

  • The partner check endpoint is treated as hostile: unauthenticated, hard-quota'd, and structurally incapable of returning anything but live-or-not. It cannot leak a tenant name, a scope or an owner because it never has them in scope.
  • Lifecycle webhooks are emitted rather than polled, so a customer's own credential inventory can stay in step without a scheduled job.

Assumptions

  • Partner endpoint quota: 20 requests per second per partner, invented, and deliberately far below what a brute-force search would need.