AI Code Completion Service · View 21 of 21 · Assurance
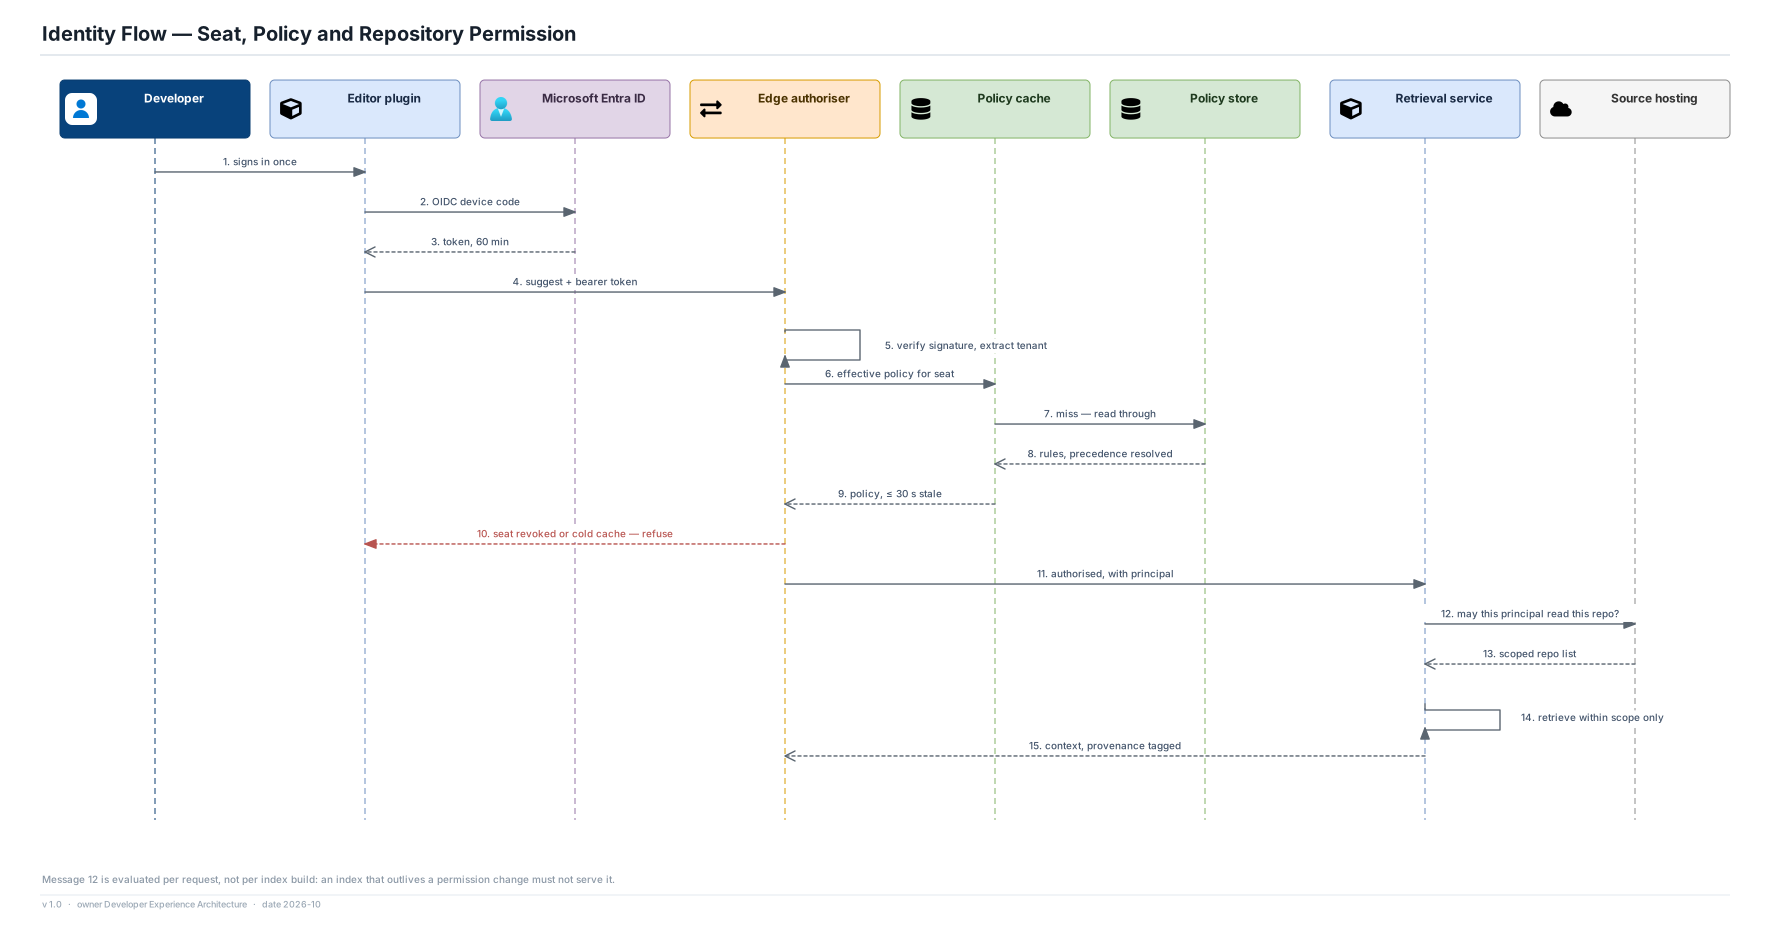
Read message 12 first
- Repository permission is resolved against the requesting principal at request time, not cached from index build. An index that outlives a permission change must not serve it.
- Message 10 is the refusal path: a revoked seat or a cold policy cache both fail to the restrictive answer, so an availability problem can never become a disclosure.
Assumptions
- Entra token lifetime 60 minutes, refreshed by the plugin; policy cache read-through with ≤ 30 s staleness.
- Source hosting answers the per-principal scope question inside the context-assembly budget.
Risks
- A synchronous permission check on the critical path is a dependency on a system this platform does not own, inside a 300 ms budget. Caching it is the obvious optimisation and the obvious way to leak a repository.